Qualys Enterprise TruRisk Management (ETM) is the AI-native platform at the heart of the Risk Operations Center (ROC), built to help organizations operationalize CTEM while reducing risk, sustaining compliance, and staying audit-ready. By unifying asset and identity inventories with risk signals from Qualys and 100+ third-party connectors, ETM moves teams beyond periodic assessments to continuous visibility.
| Capability | What it does | Key outcome |
|---|---|---|
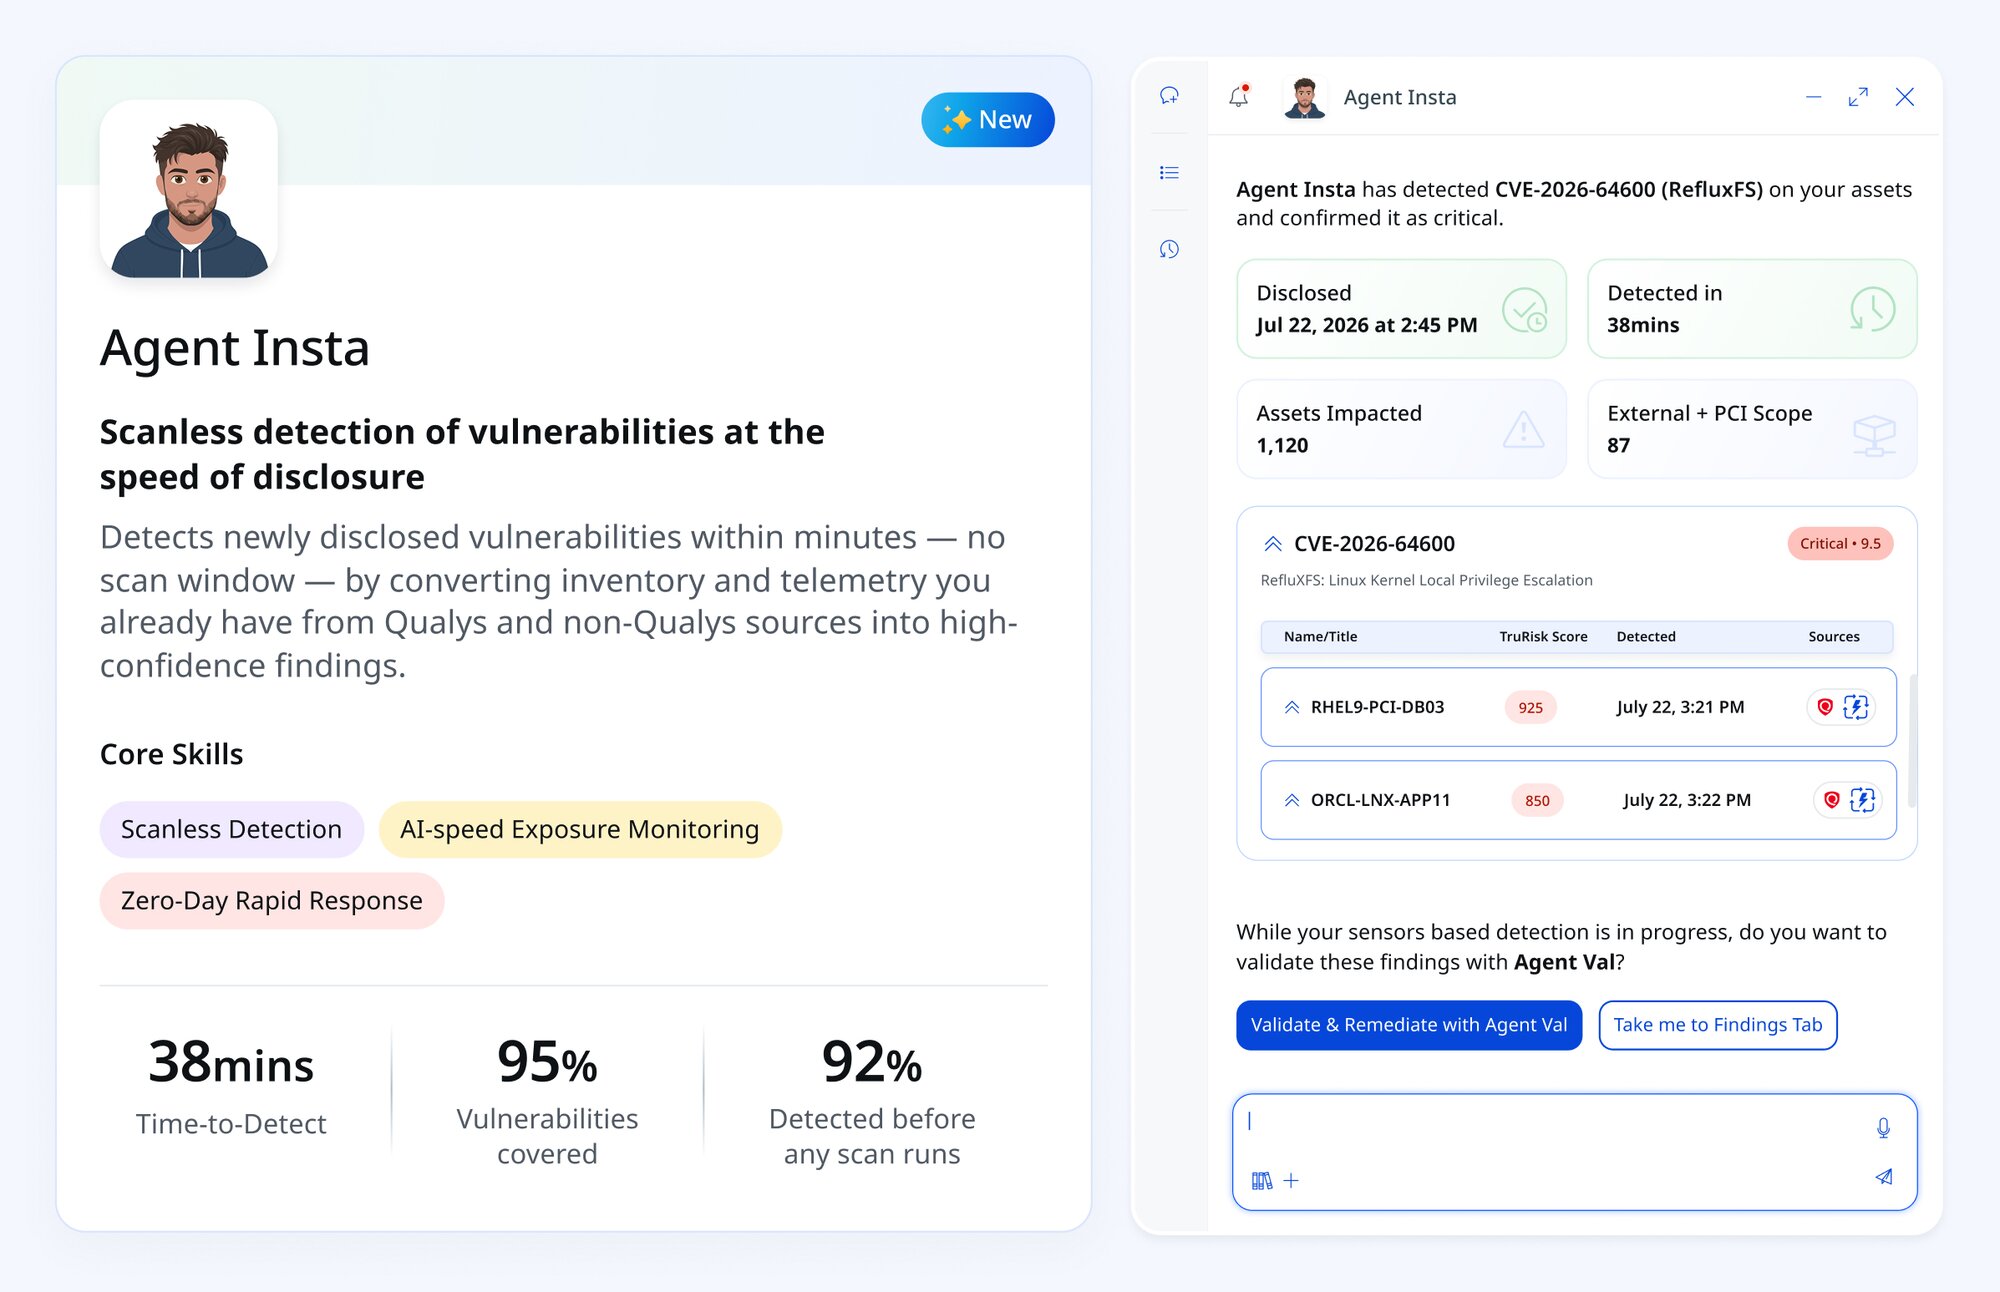
InstaScan (powered by Agent Insta) | ETM's built-in scanless scanning capability. Evaluates existing asset inventory and telemetry against new advisories, surfacing affected assets within minutes of disclosure, with no added scan load. | Assets surfaced within minutes of disclosure, no added scan load |
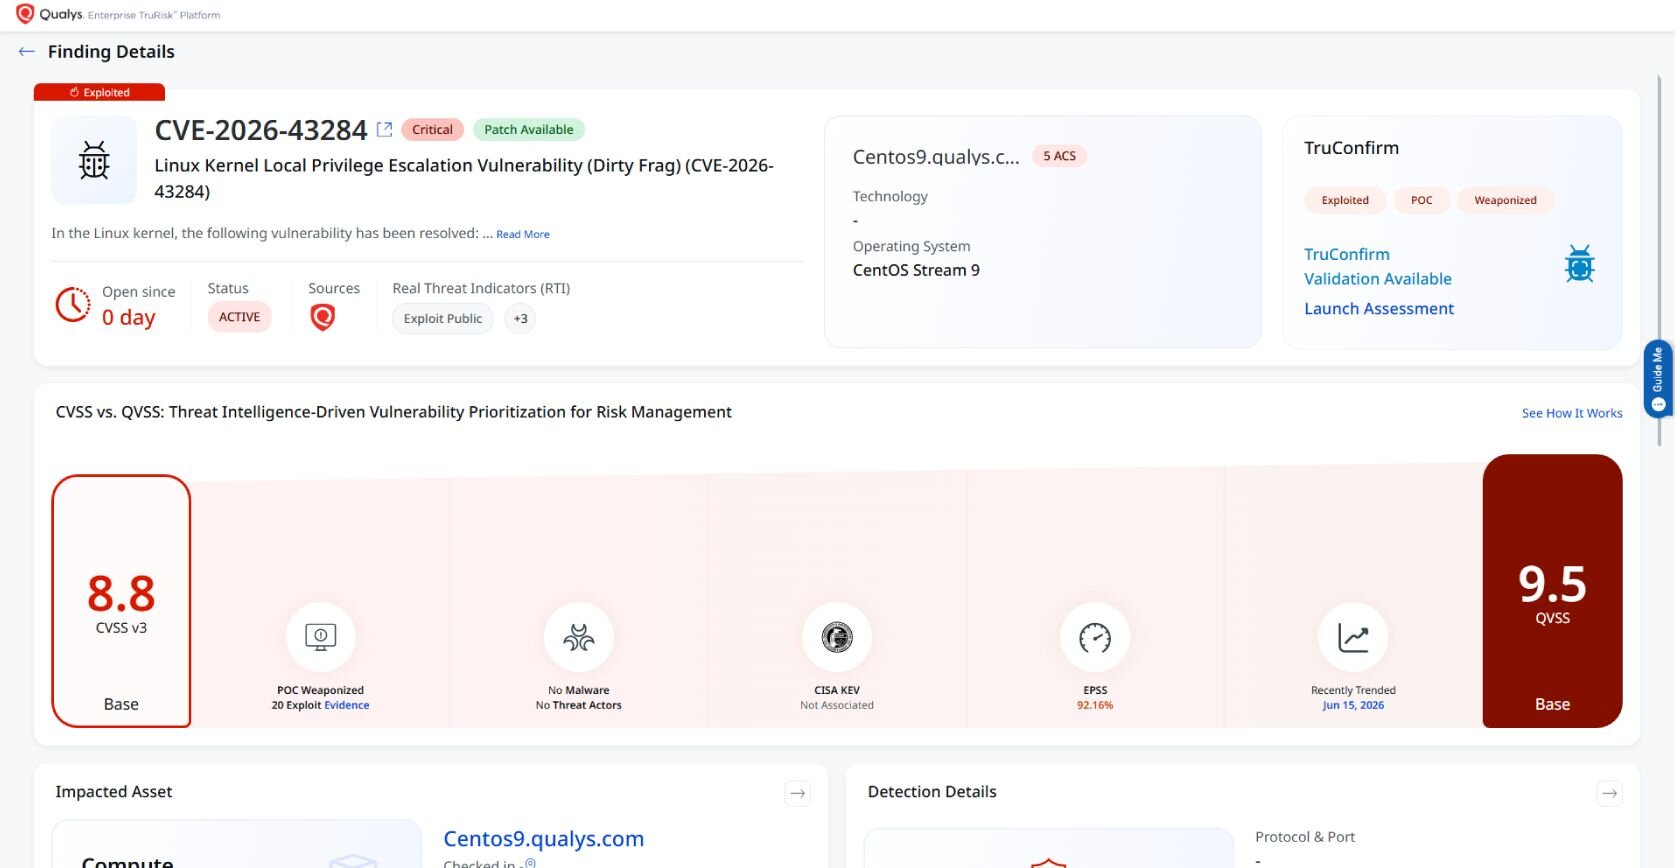
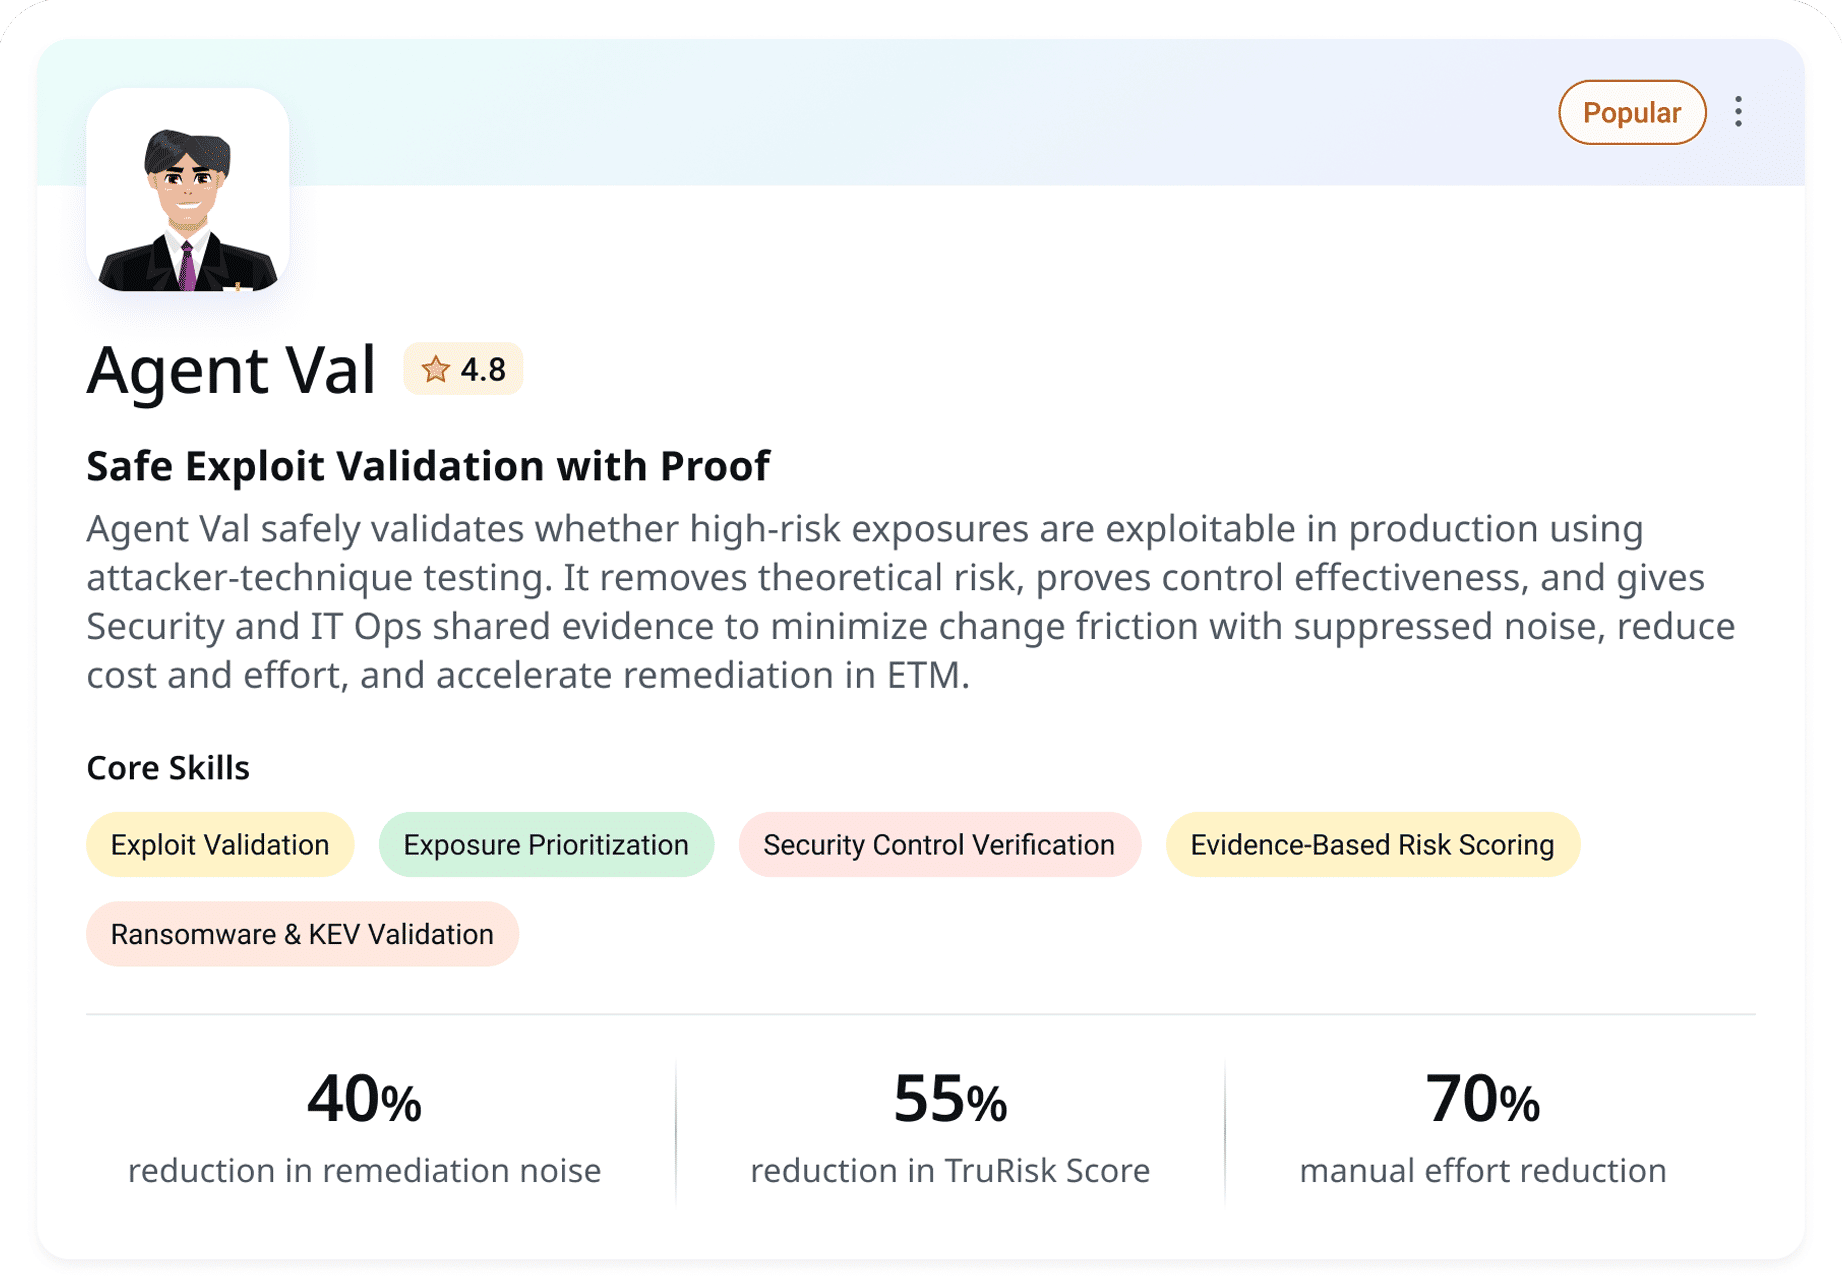
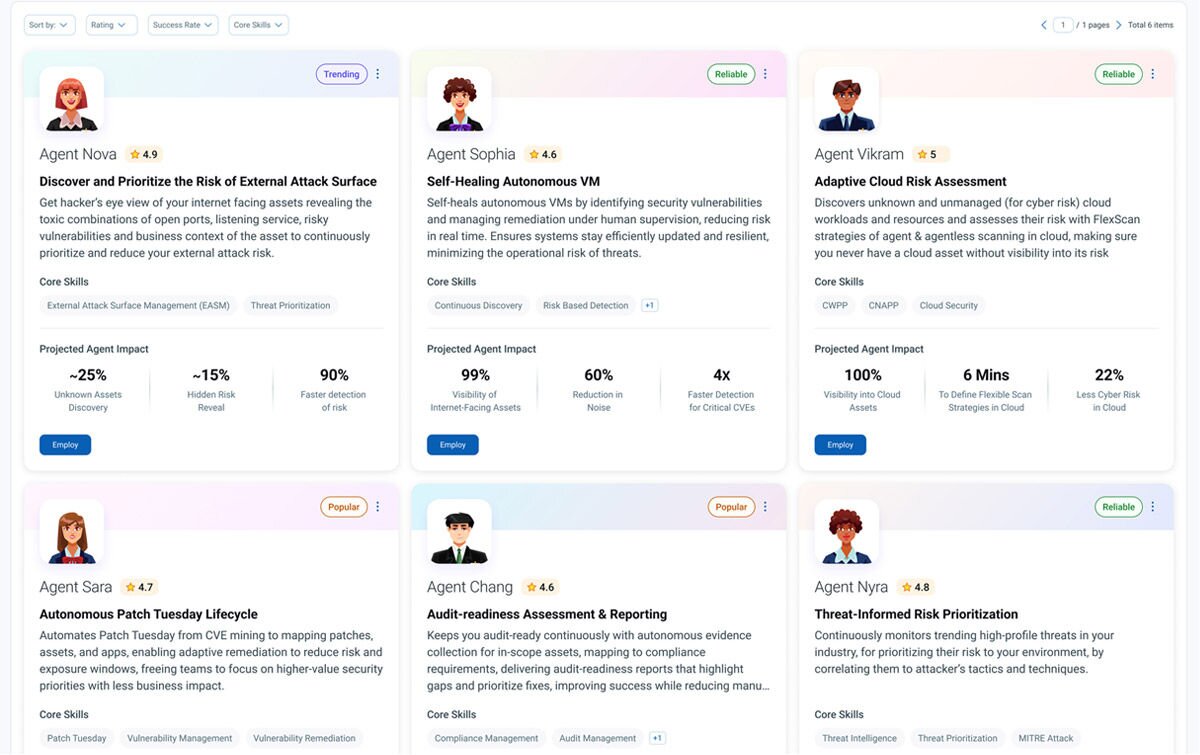
Agent Val | Performs autonomous exploit validation and builds the remediation plan for confirmed exposures, shifting teams from assumption-driven response to evidence-based, autonomous action. | Evidence-based, not assumption-driven |
Agent Sara | Takes Agent Val's plan and executes it autonomously in waves matched to each asset's operational risk, patching what she can and mitigating, customizing, or removing what she cannot. | Rollback below 0.1%, up to 70% faster MTTR |
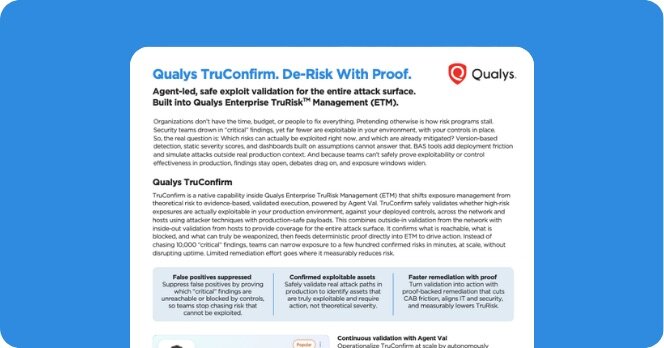
TruConfirm | Delivers the production-safe evidence behind autonomous validation, covering 1,800+ CVEs today and extending beyond network-reachable exposures to host-resident CVE classes, including privilege escalation, browser engine, kernel, insider-threat, and blind local RCE vulnerabilities. | Validated evidence that directs remediation effort to real threats wherever they live |
Agent Nyra | Correlates real-time adversary activity with your exposure profile to identify weaponized CVEs, impacted assets, and active campaigns, dynamically prioritizing risk based on what attackers are exploiting today | A stack-ranked list of assets matching active threat actor playbooks |
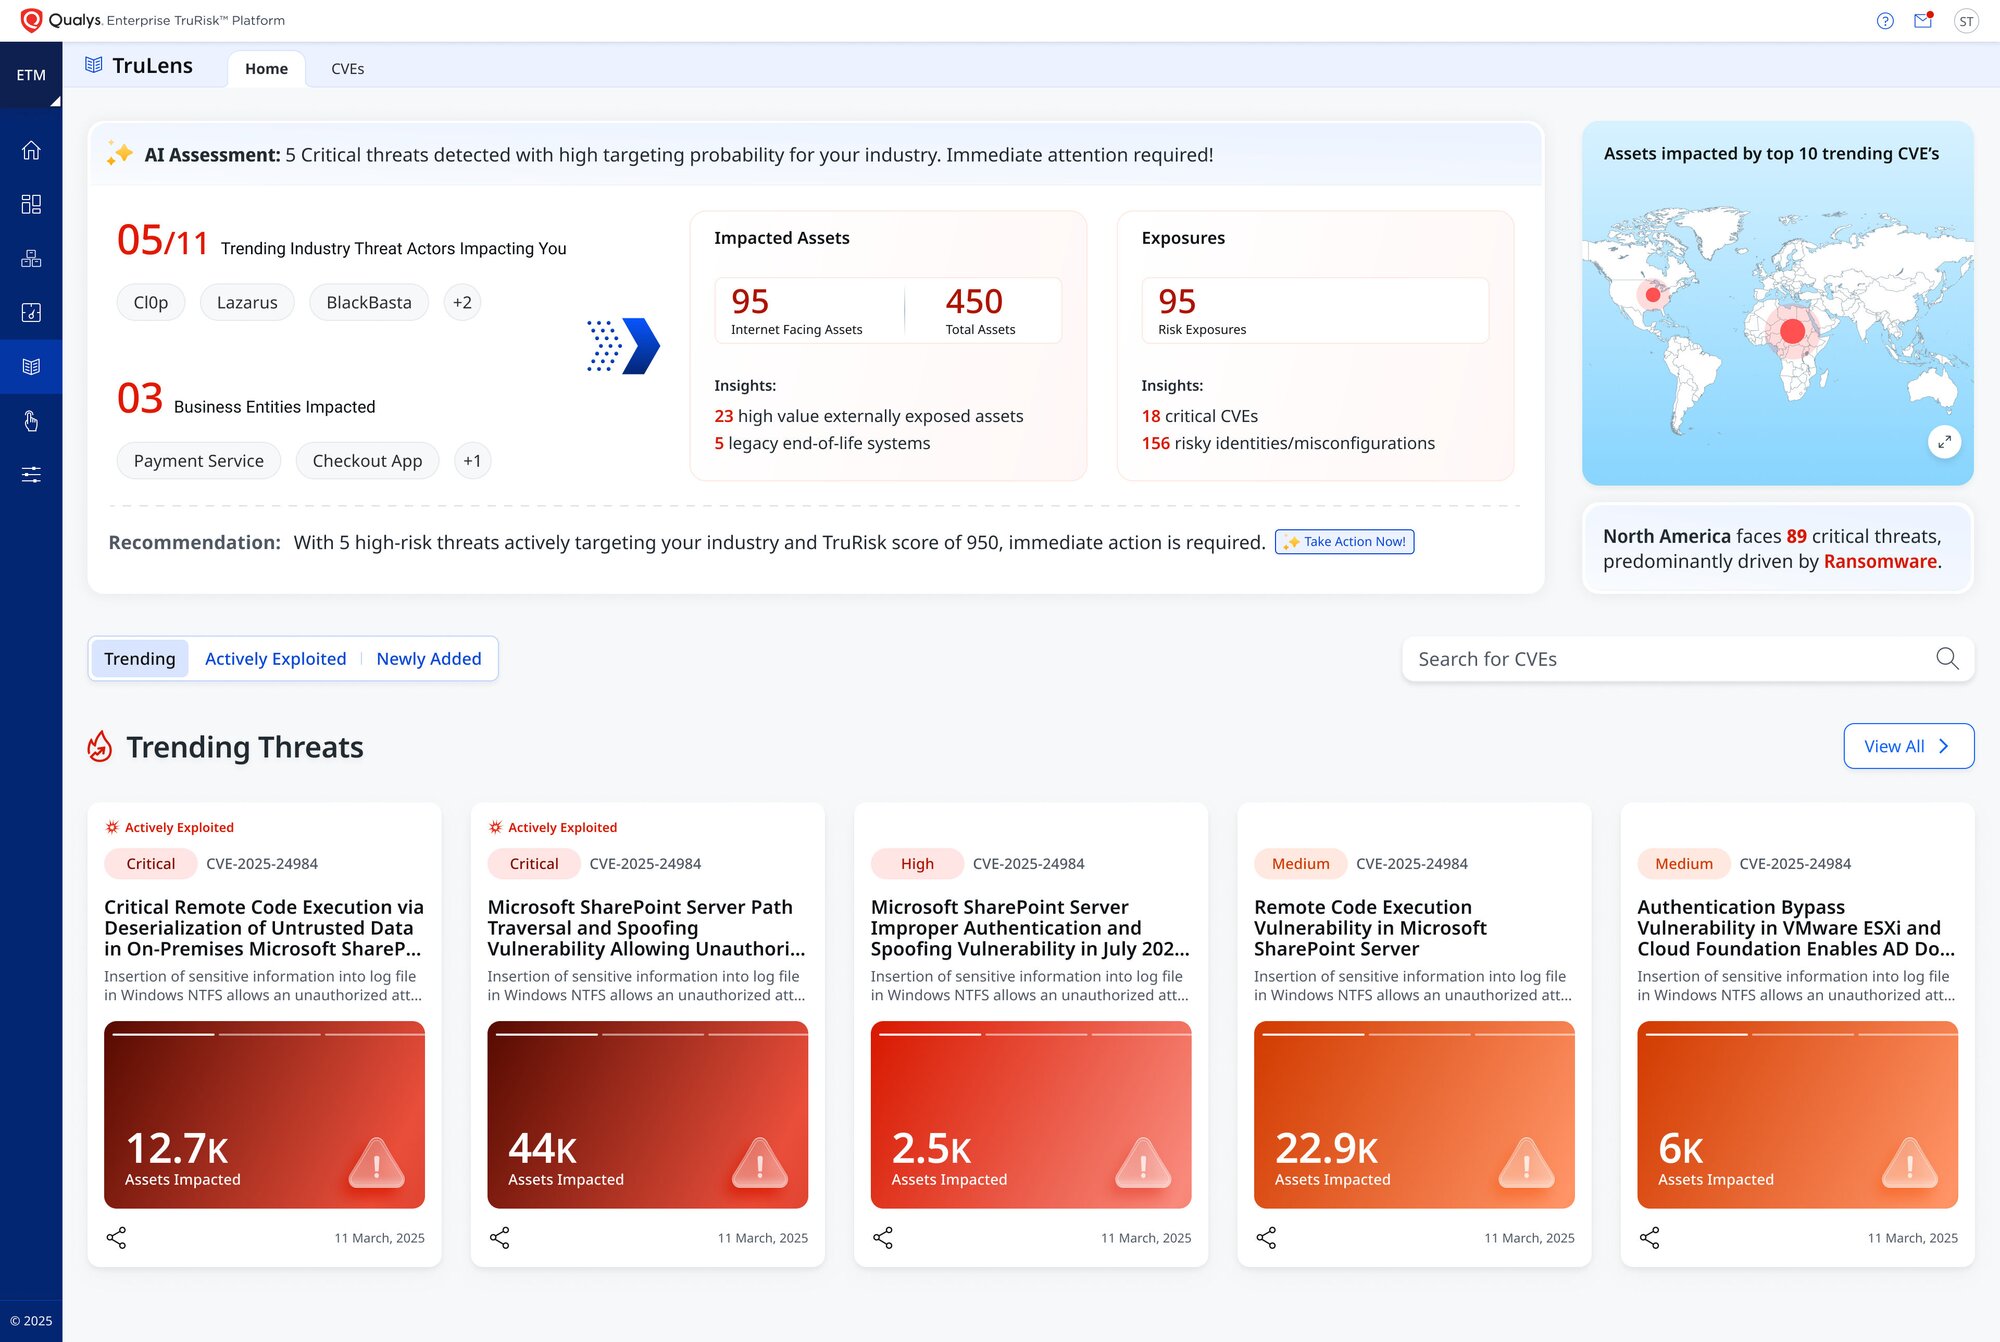
TruLens | Layers in real-time threat intelligence and peer benchmarking by geography, industry, and size, revealing how threat actors are targeting your critical assets. | Visibility into how threat actors target your assets |
Agent Sid | Focuses on the how and where of exposure by evaluating asset criticality and technical context to understand blast radius, automate remediation workflows, and prioritize actions that reduce organizational risk. | Blast-radius context turned into an executable technical plan |
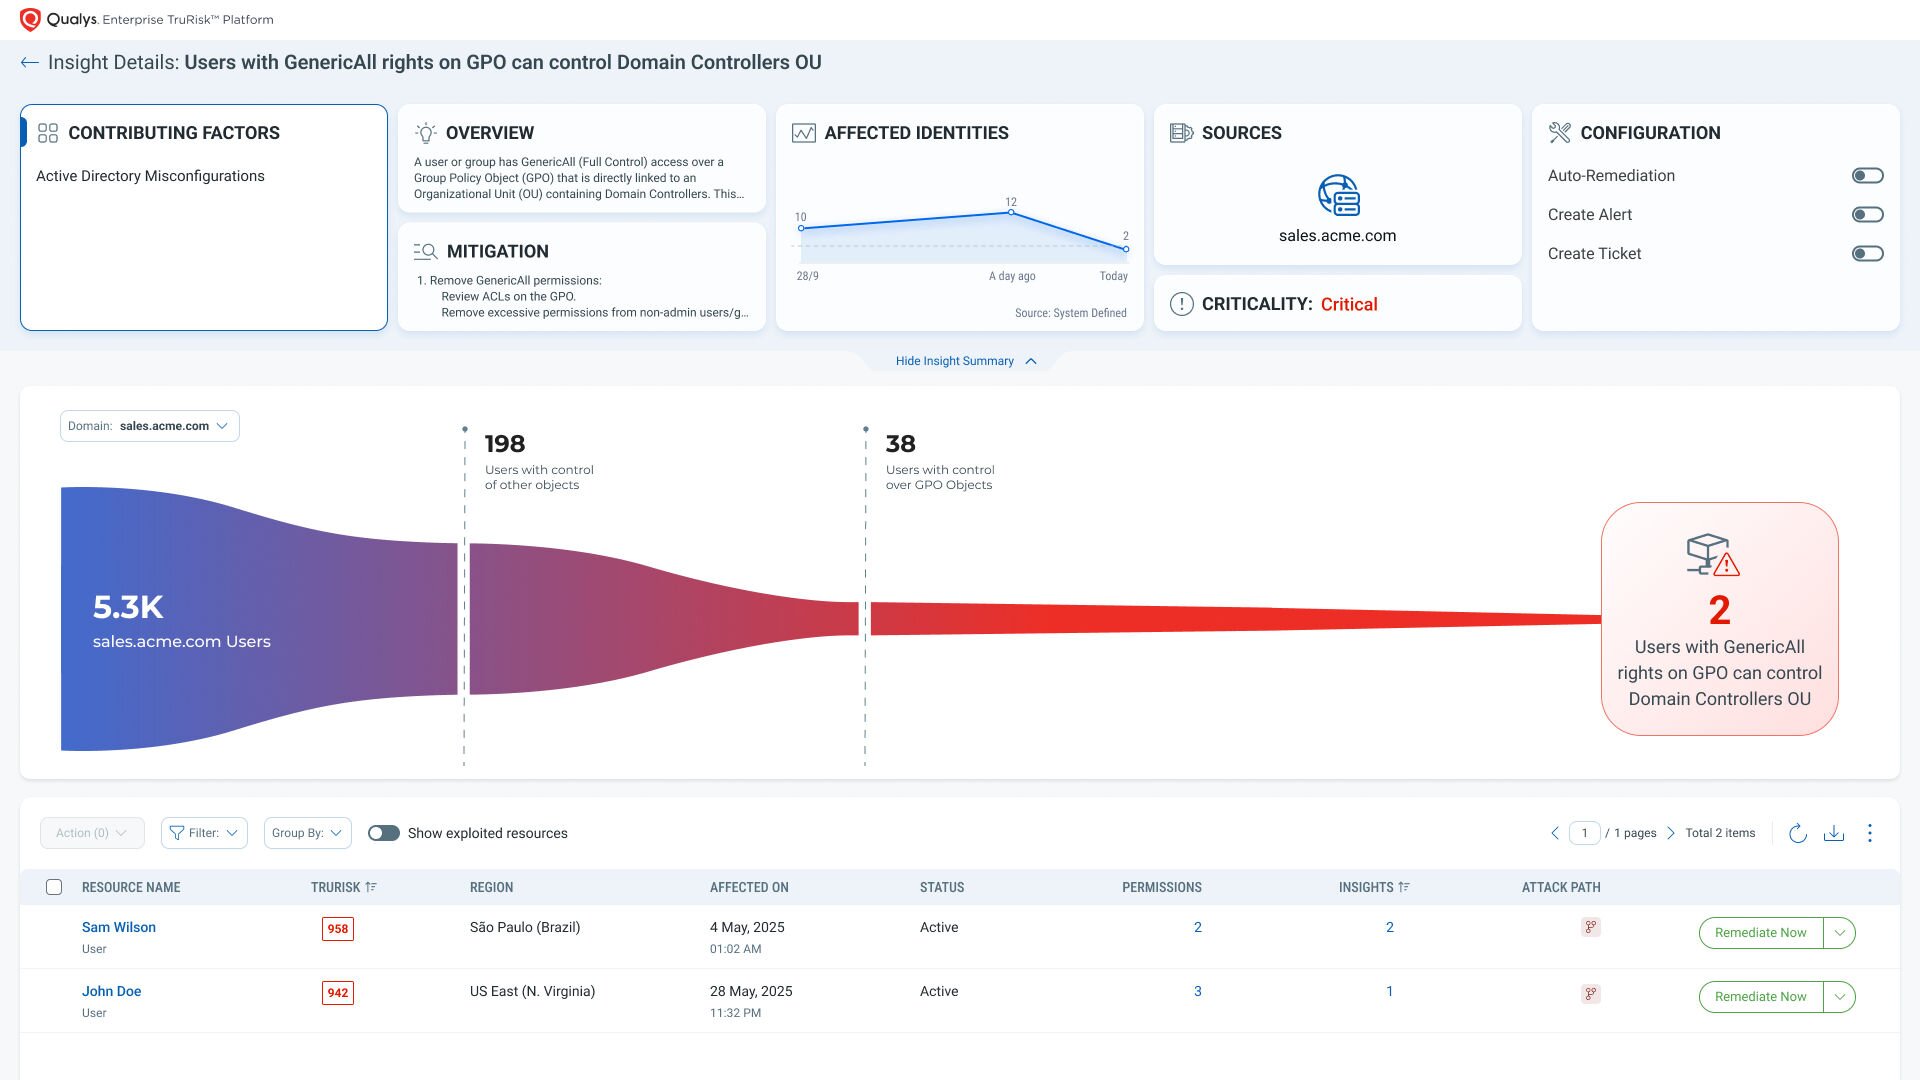
ETM Identity | Extends that same visibility and control to human and non-human identity risk, narrowing the attack surface through automated, context-driven prioritization and remediation. | Narrower attack surface via automated prioritization |
ROCky | A conversational AI interface embedded in the Risk Operations Center that augments analyst judgment with natural-language access to prioritized insights, remediation workflows, executive reporting, and actionable guidance. | Plain-language access to exposure data, executive reporting, and next-best-action guidance |

ETM precisely scopes your organization's attack surface by consolidating data from all sources, including on-premises, cloud, containers, identities, and applications, to provide complete visibility into known and unknown assets. InstaScan, powered by Agent Insta surfaces affected assets within minutes of new advisories. By integrating data from CMDBs, third-party tools, and Qualys agents with business context, ETM focuses your CTEM program on the most critical risk.
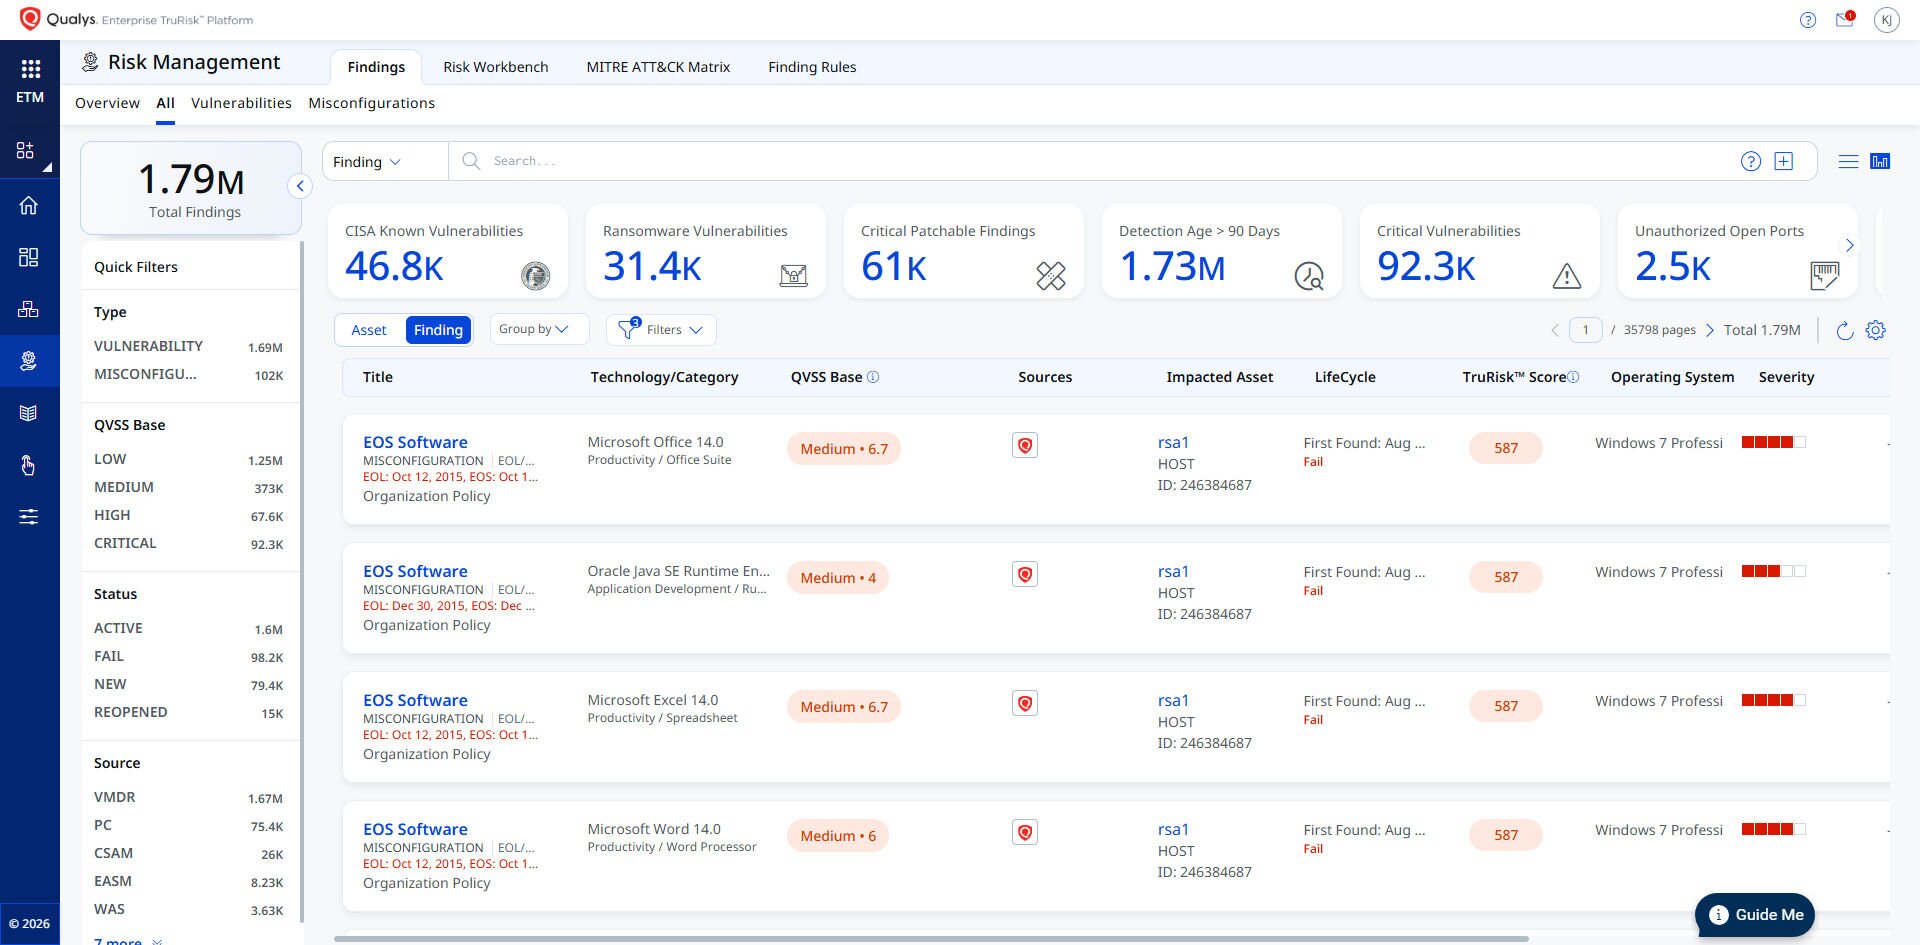
risk identification across your siloed security tools
using TruRisk™ score and business context for financial impact
with automated patching, IT tickets, & real-times alerts.
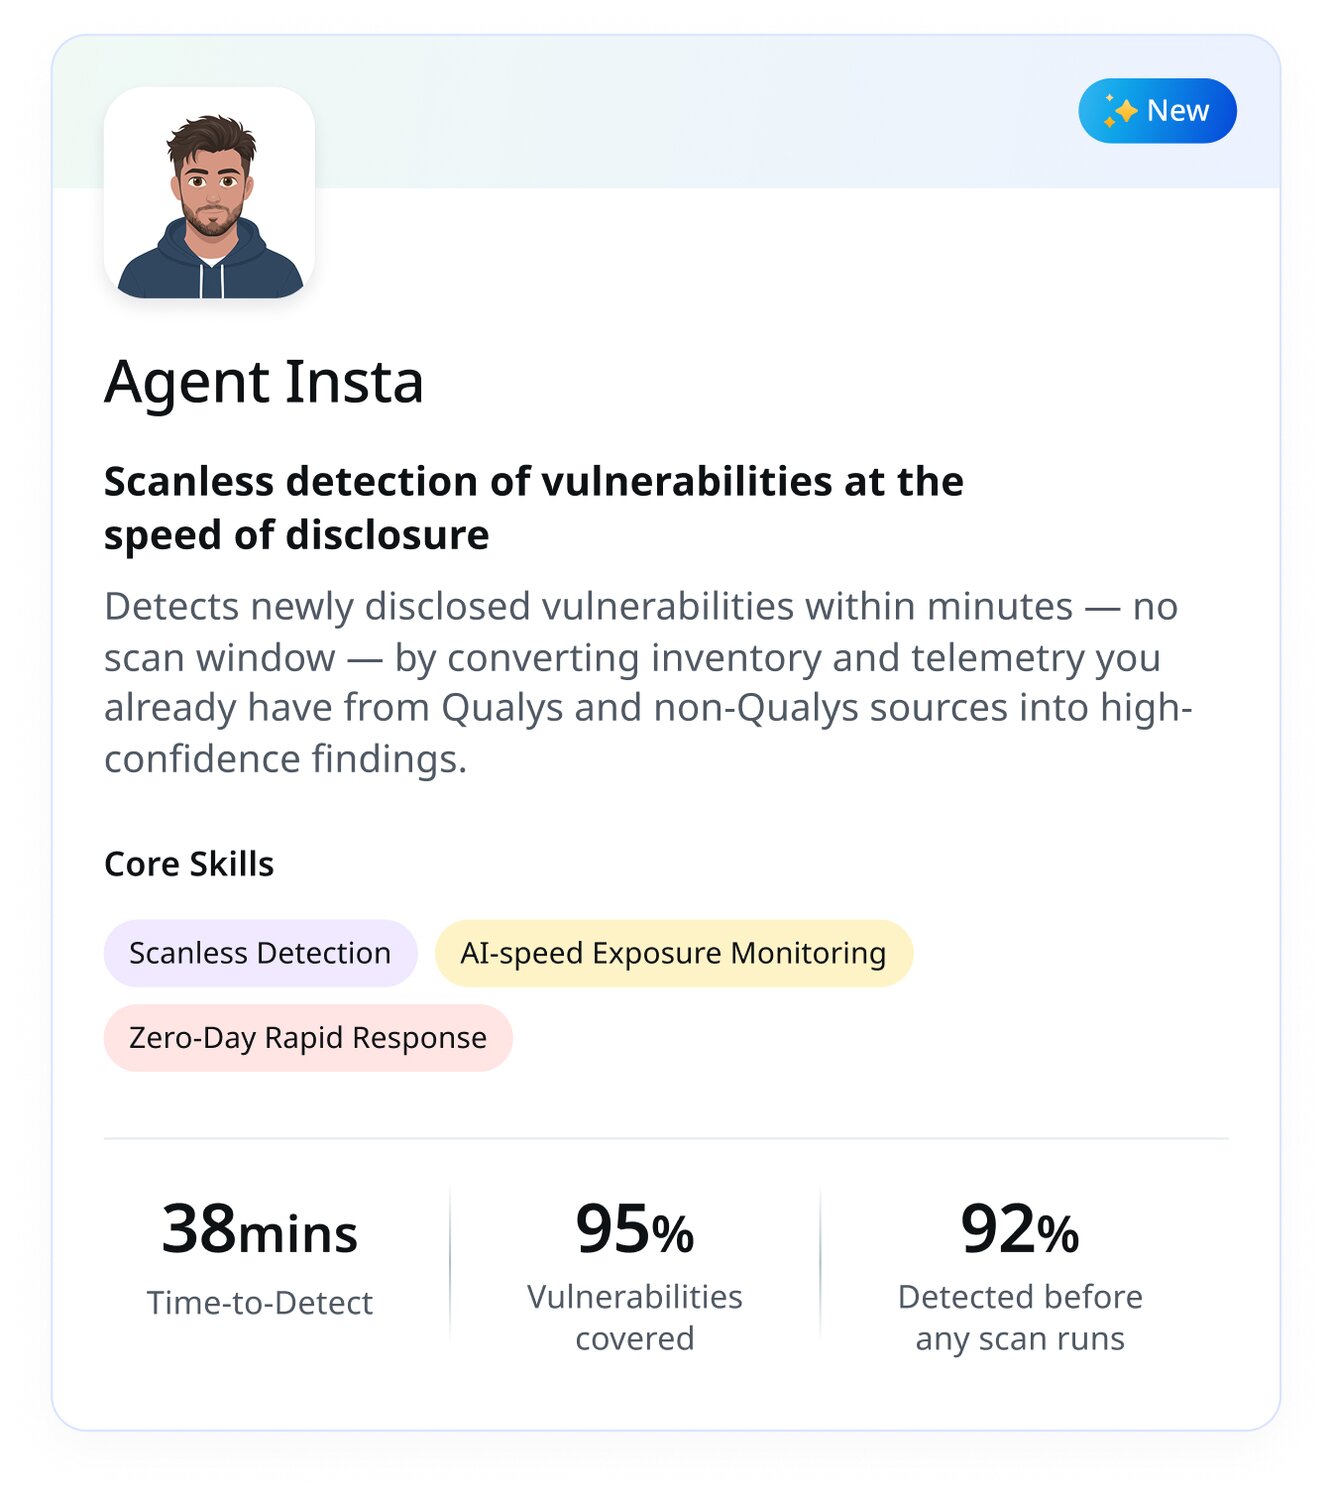
Scanless Scanning
InstaScan, powered by Agent Insta, leverages AI models to correlate the advisory against your live asset inventory in minutes. Every affected asset is surfaced without waiting for next scan which could be days later.
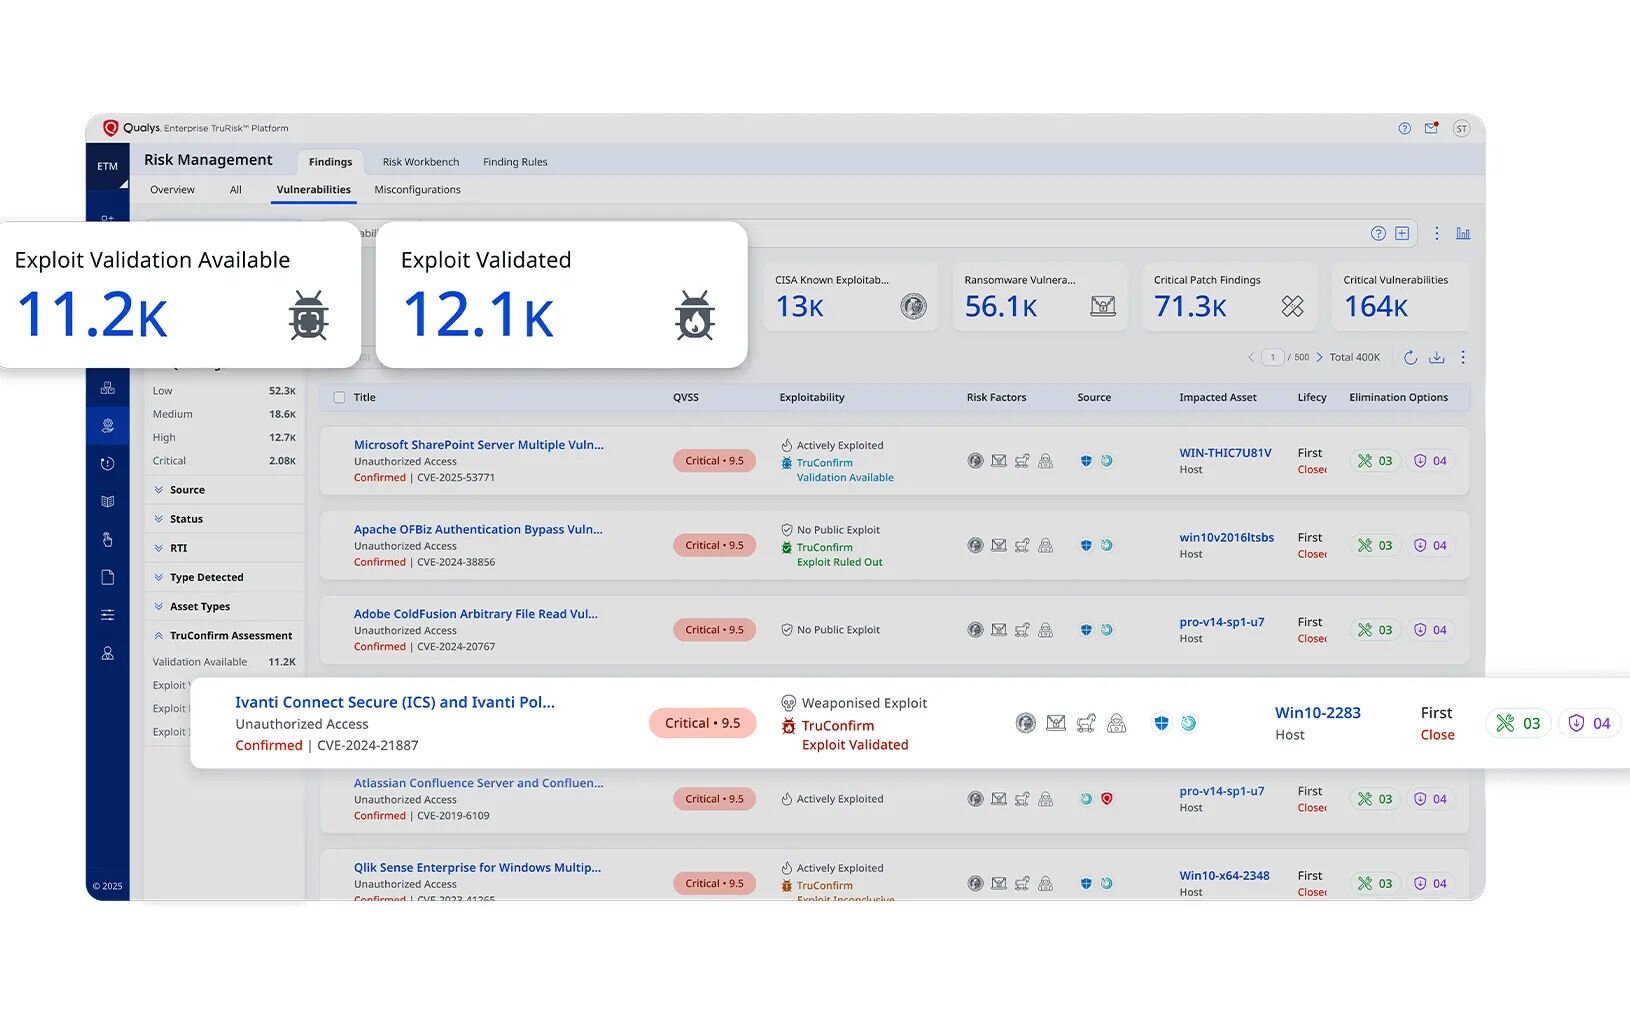
Agent-led safe exploit validation with proof
Powered by Agent Val, TruConfirm validates external assets via scanners and internal exploit paths via cloud agents, covering your entire organizational attack surface.
Identity Risk Operations.
Unify identity exposures across AD, Entra ID, IDaaS, cloud IdPs, IGA, PAM & more into one prioritized view. Correlate identity risks with asset risks for business impact to eliminate the most exploitable attack paths.
Benchmarking Power.
Correlating 25+ threat feeds, including MITRE ATT&CK, with peer benchmarking by geography, industry, and size, turning fragmented intelligence into defensible, business-aligned risk context.
Autonomous Cyber Risk Management.
Enabling an AI fabric for your enterprise to drive real-time, autonomous prioritization and response to exposures and deliver board-ready insights. This evolution shifts security teams from tactical responders to strategic orchestrators.
Integrated CSAM/EASM for complete asset visibility across all environments.
Communicate cyber risk in terms of business impact and financial exposure.
Manage risk to your environment and business from industry-specific threats with TruLens intelligence.
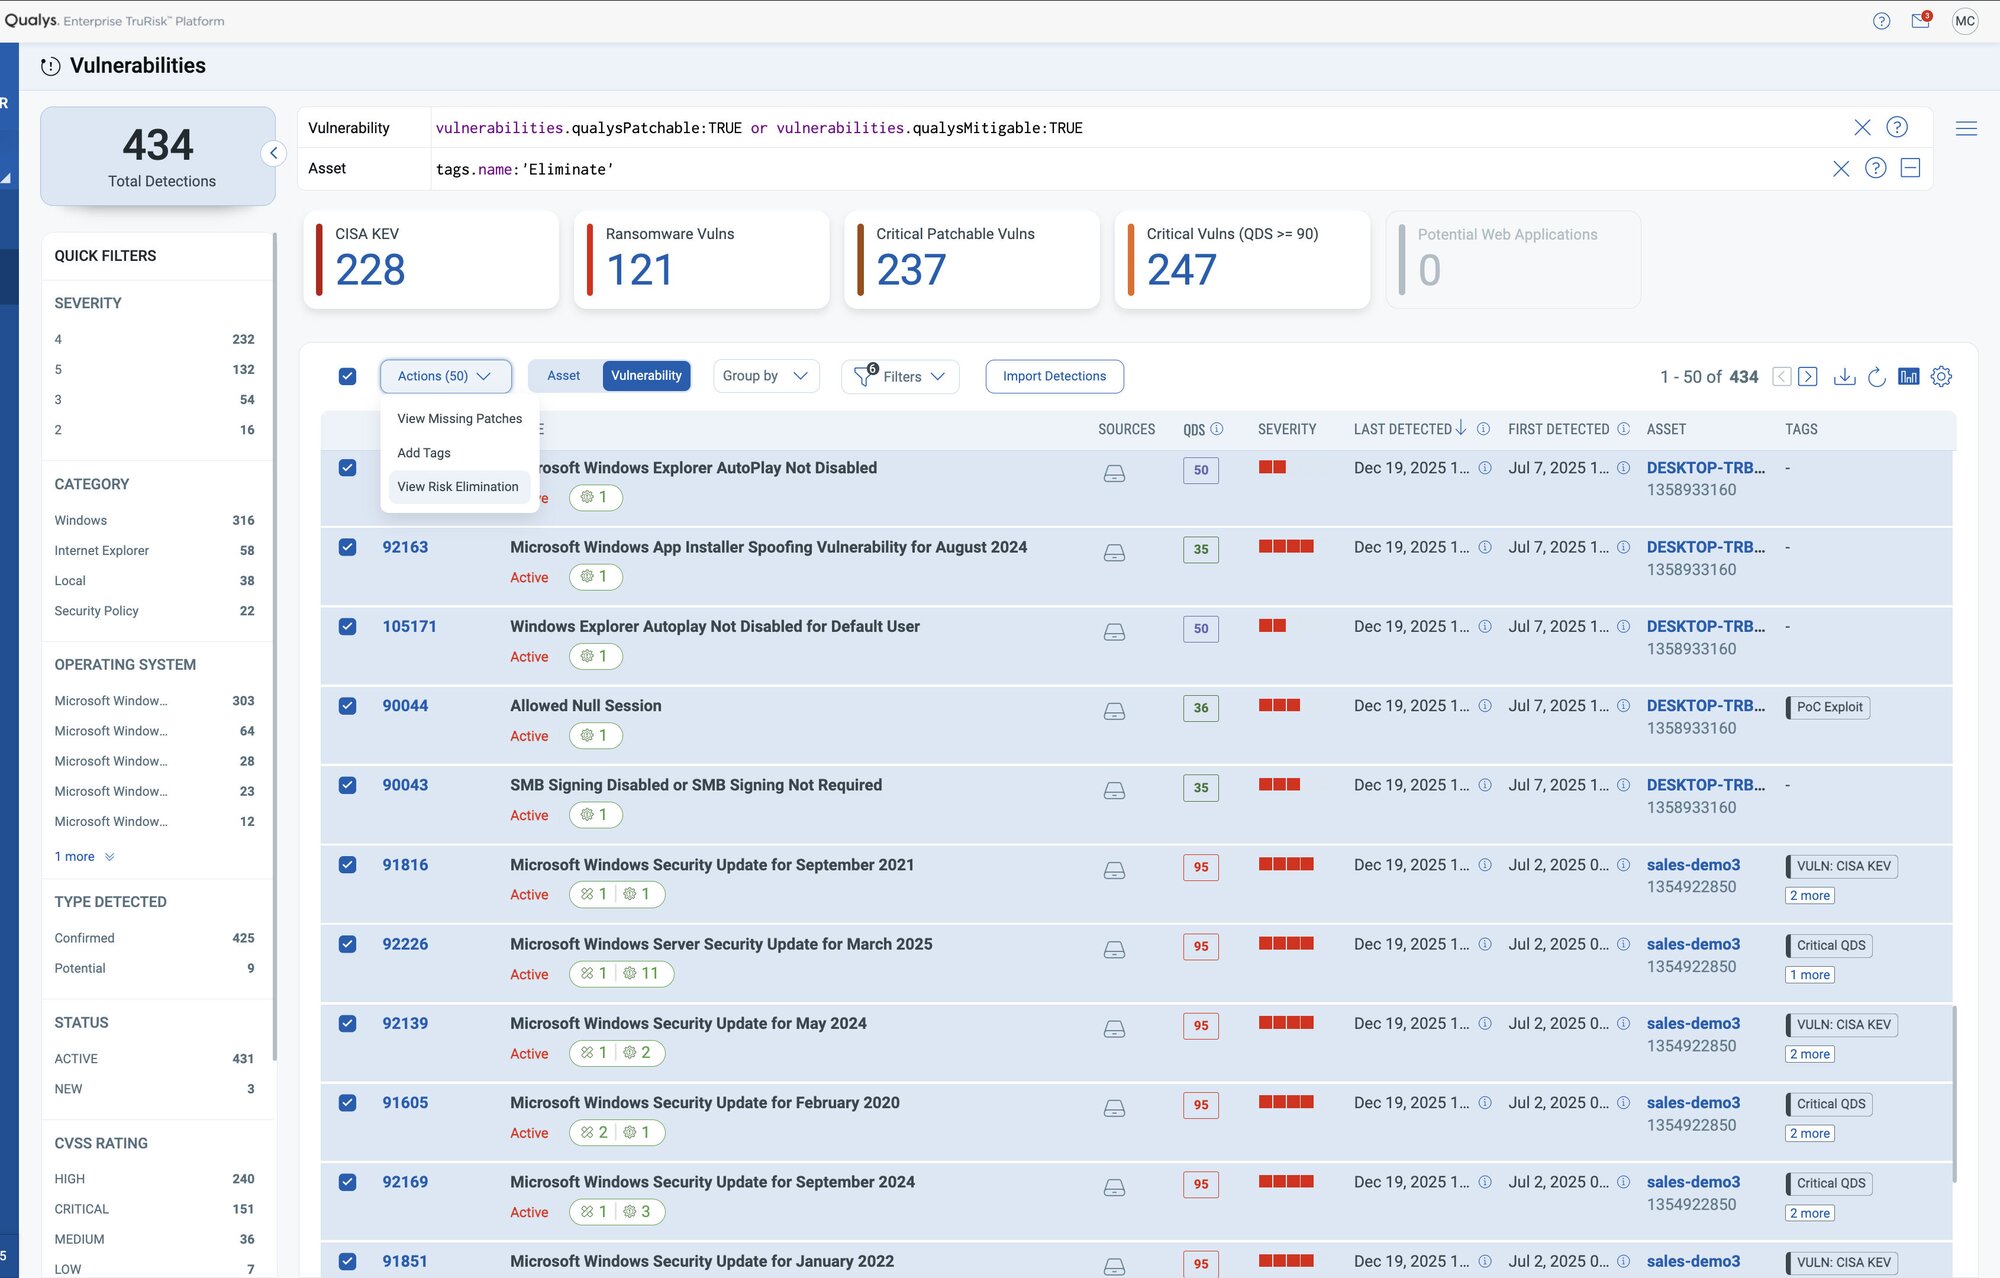
Aggregate Vulnerabilities, misconfigurations, and web app risksfrom Qualys and non Qualys sources for their risk-based prioritization with threat and business context.
Validate security controls with TruConfirm to confirm real exploitability of exposure in production environment using attacker's technique.
AI-driven cyber risk management across all CTEM/cyber risk management operational steps.
Mythos Gives Attackers Hours. Don't Give Them Days to Exploit.
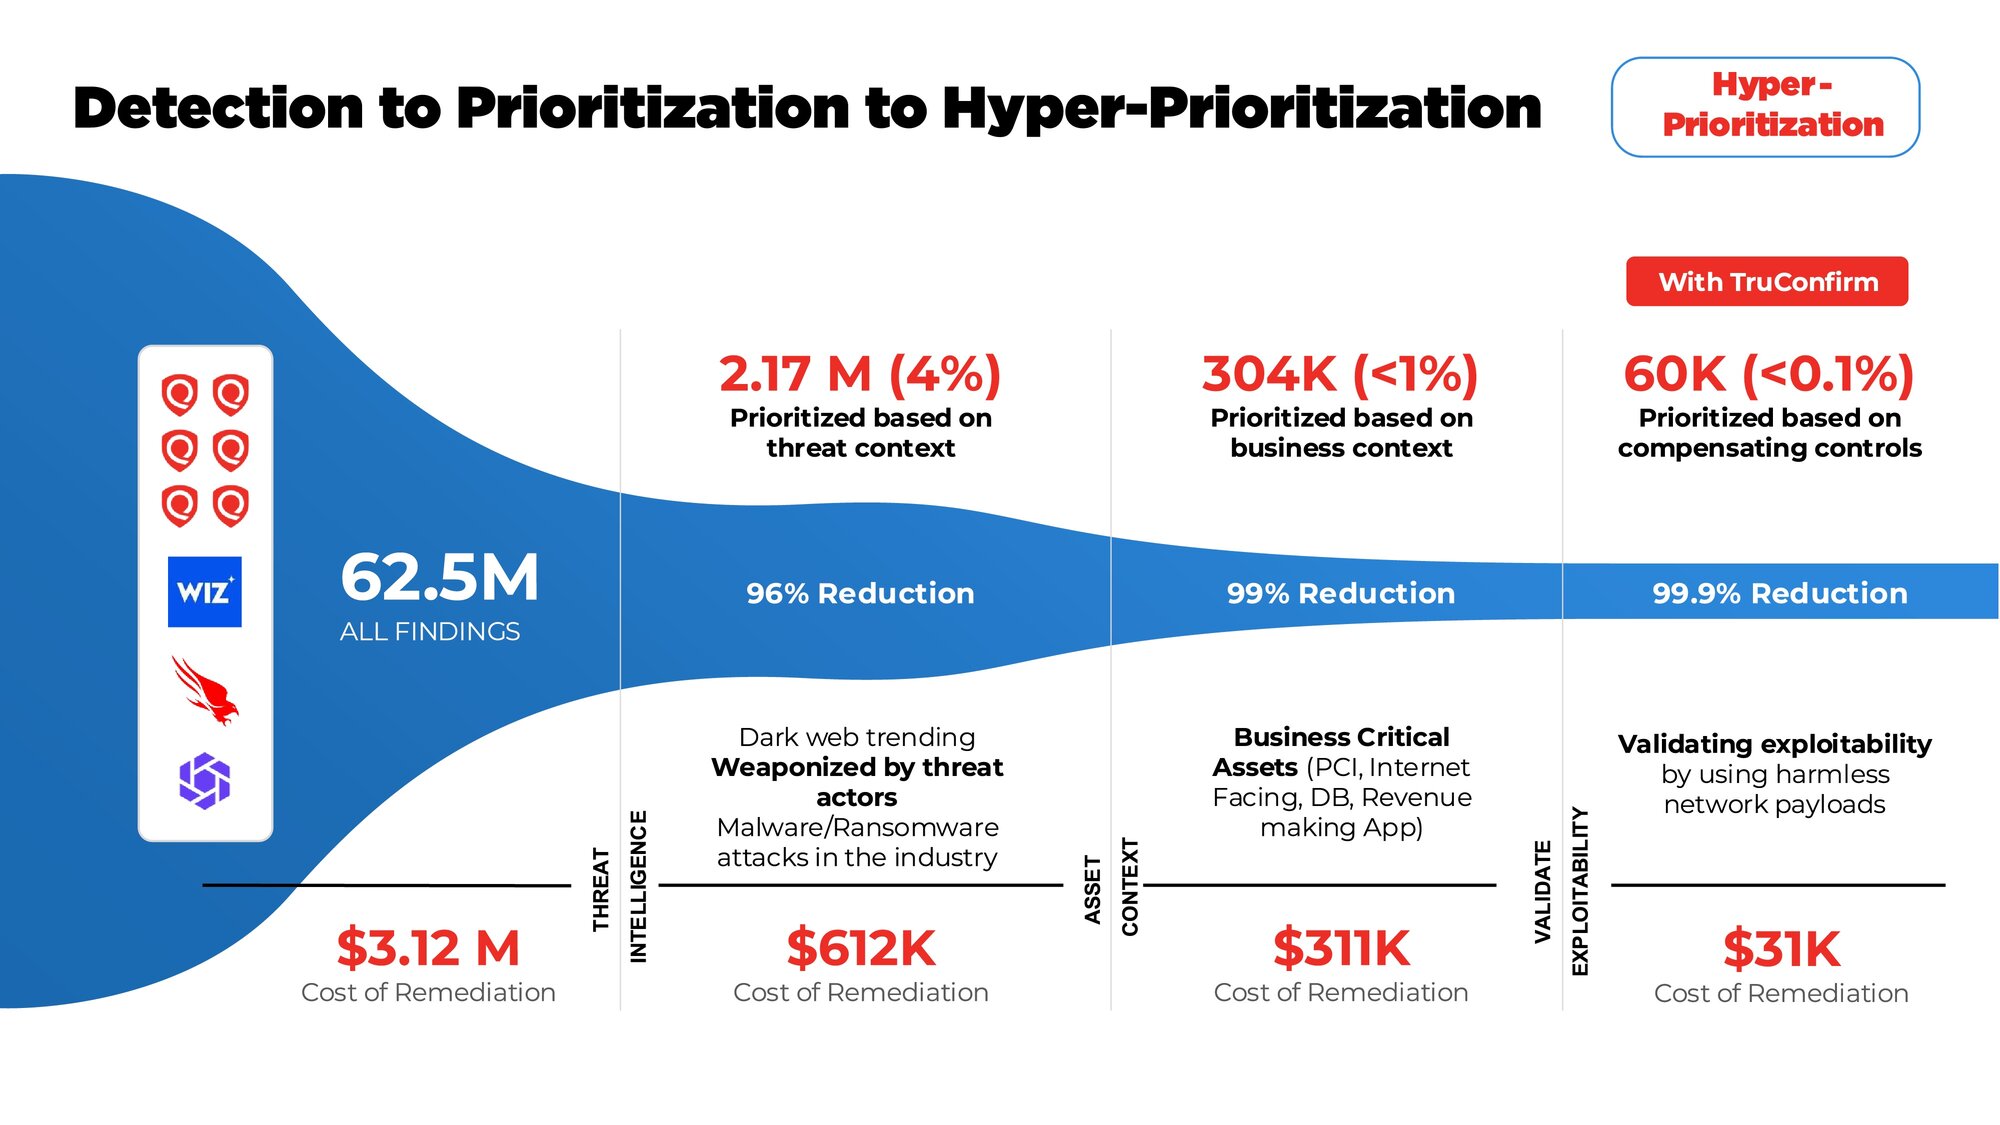
Frontier AI weaponizes vulnerabilities in hours. Patch cycles run in weeks. Close the gap with a new operating model: AI-Speed Detection, Hyper-Prioritization, and Zero-Day Remediation.
99%+
of Mythos-discovered vulnerabilities remain unpatched
43 days
median time to remediation (DBIR 2026)

Qualys’ approach with the Risk Operations Center delivers this ideal in a cohesive way. With the ability to analyze all risk factors at a glance – such as exploitability, unique organizational context, threat intelligence, and financial impact – Qualys Enterprise TruRisk™ Management empowers CISOs and business leaders to create actionable, enterprise-wide strategies to reduce risk to levels that align with the business’s objectives.

Analyst Recognition and Related Resources
Qualys TruConfirm - Prove Real Exploitability in Production | De-Risk Cyber Threats with Evidence