Secure Your Web Application and API Attack Surface
Increase in web asset visibility with full-stack discovery.
Scan time reduction with deep, optimized runtime coverage.
Noise reduction with confirmed exploitable findings.
TotalAppSec replaces isolated testing tools and static scanners with a modern baseline for AppSec – continuously know your attack surface, identify the exposures that matter most, and move them to remediation faster than an attacker can reach them. TotalAppSec optimizes time-to-risk-reduction by connecting multi-source asset discovery, runtime security assessment, TruRisk™ prioritization, and closed-loop developer remediation into a continuous, unified application risk operations.
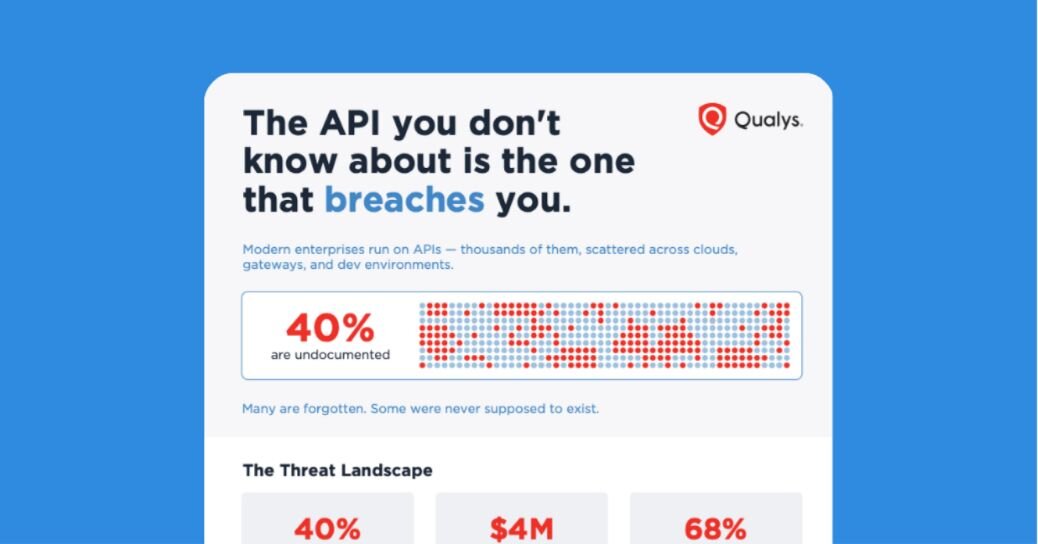
Eliminate coverage blind spots and automatically onboard newly deployed web apps and APIs into continuous security assessments. TotalAppSec automatically normalizes application and API asset data across cloud environments, API gateways, internet-facing assets, AI embedded in modern applications and internal repos. It continuously monitors for change events, identifying unmapped endpoints, rogue deployments, and shadow APIs without manual target list maintenance.
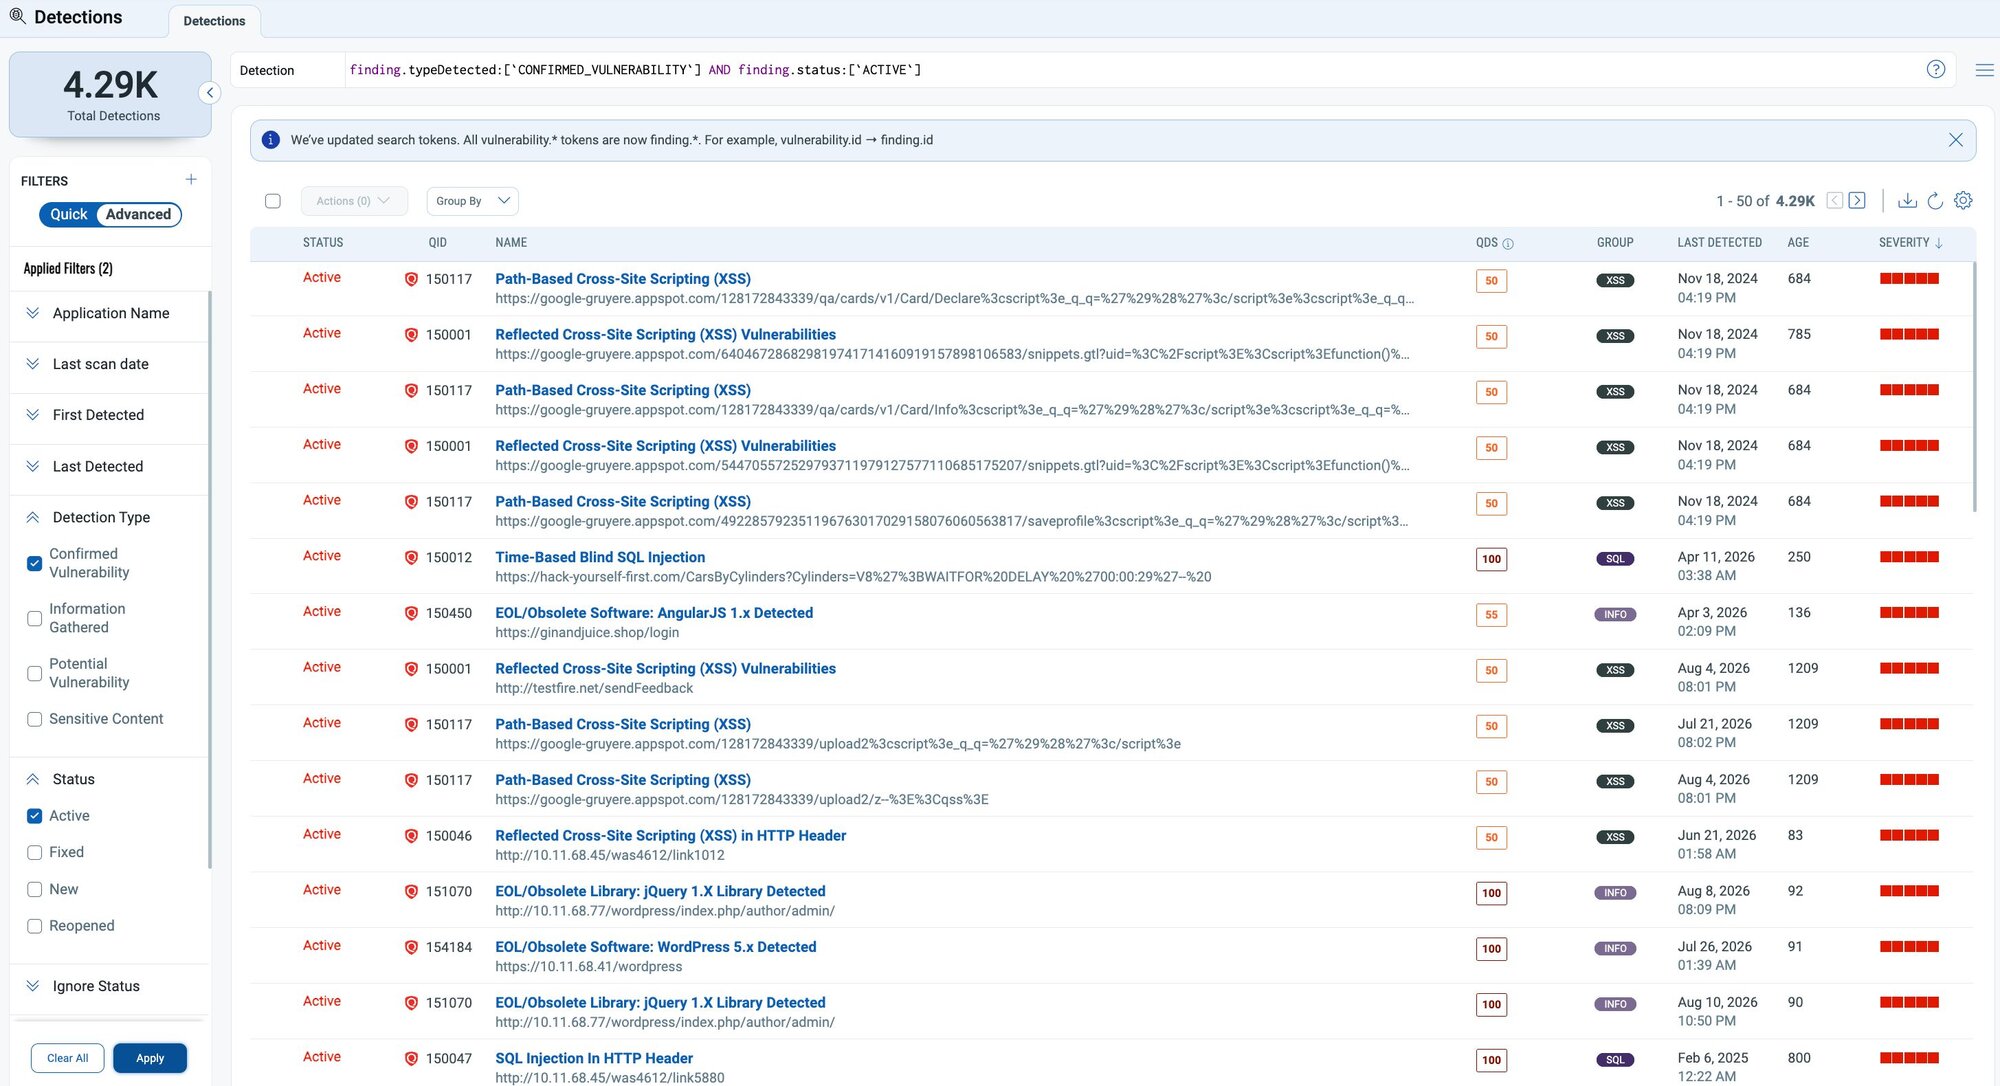
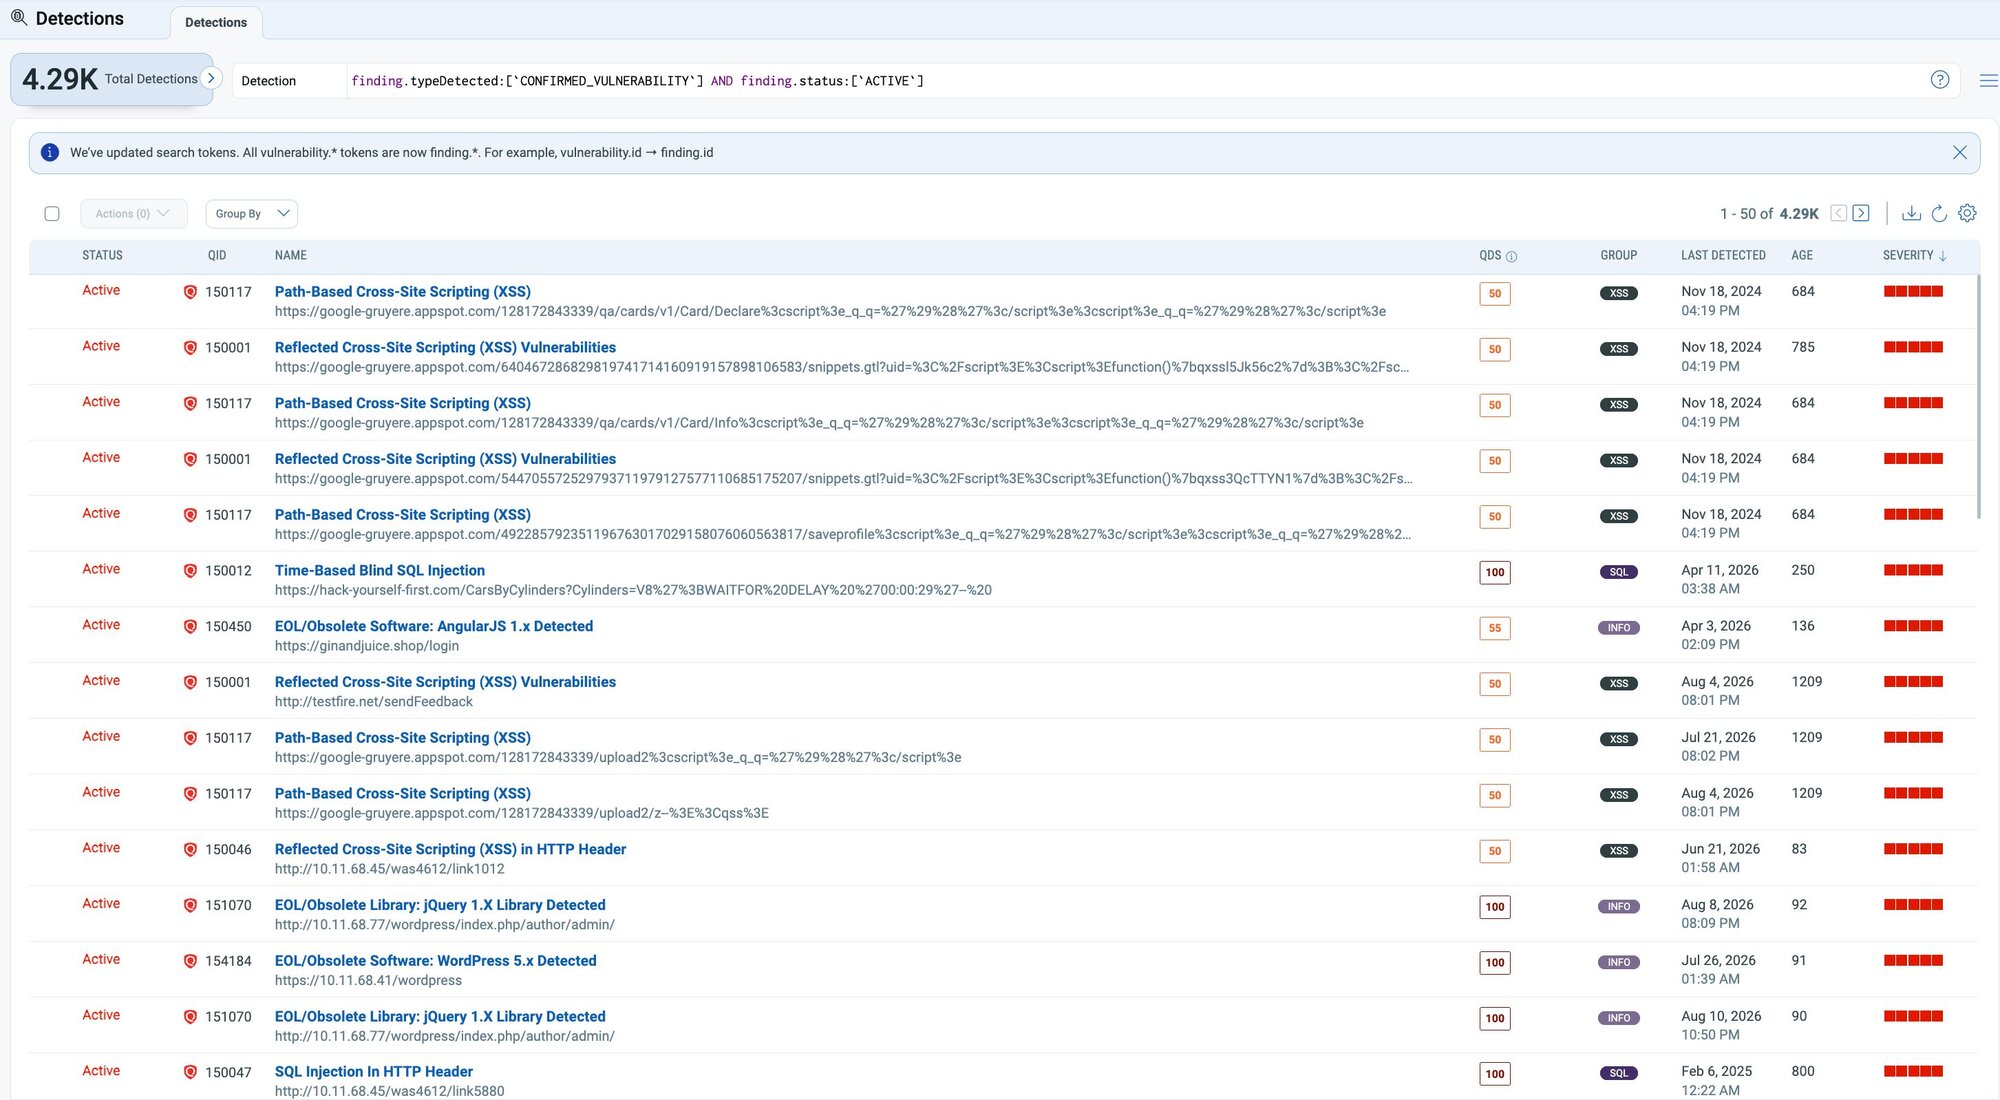
See how TotalAppSec Secures your Entire Application Estate
Combine web DAST, API discovery and security testing, and deep-learning web malware monitoring around one application estate. Discovered shadow assets can move directly into managed inventory and active testing, helping teams replace fragmented scanners with a continuous operating model for finding, assessing, and reducing application risk.
Create custom signatures to detect organization-specific or newly emerging risks without waiting for vendor content. JSON-based framework turns bespoke conditions into repeatable HTTP security tests and can also help identify AI embedded in applications, including exposed AI services, integrations, and related application behavior at scale.
Dynamically test REST and SOAP APIs using OpenAPI, Swagger, Postman, and authenticated workflows. Validate OWASP API Top 10 risks, including BOLA, BFLA, and BUA, supports OAuth token refresh and interactive IdPs, checks OAS conformance, and extends coverage with custom signatures for organization-specific API weaknesses at enterprise scale consistently.
Helps AppSec teams test as frequently as applications change. AI-powered scan optimization reduces unnecessary testing, while progressive scans and Green Windows preserve coverage within approved maintenance windows. Automated OAuth token refresh, interactive Selenium authentication, HAR-based diagnostics, and targeted retests reduce scan failures and reruns, making continuous DAST practical across complex production applications.
Continuously monitor web applications for malware using deep learning, behavioral analysis, heuristics, and reputation checks. Detects known and previously unseen threats, malicious third-party content, injected scripts, and signs of exploitation, helping teams protect customers, prevent blacklisting, preserve brand reputation, and respond faster to compromised web assets at scale.

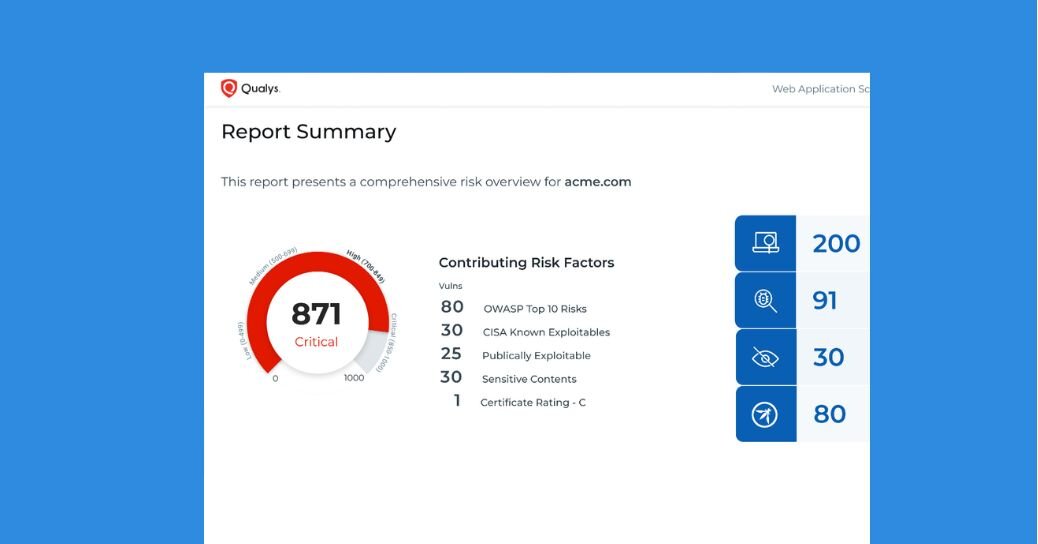
Combine PII and sensitive-content detection with OWASP Top 10 mapping, OWASP API Top 10 testing, OAS v3 conformance scans, PCI DSS workflows, and detailed risk reporting. Extend into payment-page and client-side checks, helping teams identify exposure, validate compliance, and surface risky third-party application behavior.
With TotalAppSec, we can detect runtime vulnerabilities, misconfigurations, and compliance drift across our web applications and APIs in real time. As we continue our digital transformation, TotalAppSec will play a key role in securing a fast-growing number of open APIs.
Qualys gives us a common baseline. It ensures our most advanced teams meet the standards they sell - and helps less mature teams reach that same level.
Cybersecurity is the enabler. We see Qualys as the platform giving us the competitive advantage.... preventing critical issues before they ever reach live customers.
With Qualys WAS, we gain the peace of mind that our websites are effectively managed and maintained on our behalf from a security perspective... If we ever need assistance with interpreting the results of a scan or diagnosing a technical issue with scanning, we know that Qualys support is only an email or a phone call away.
We are now scanning more than 50 web apps with the Qualys solution, including authenticated and unauthenticated scans. We can now see what types of vulnerabilities exist across our application portfolio. We're also able to highlight the top 10 Open Web Application Security Project [OWASP] vulnerabilities in external-facing systems and make sure we take prompt action to protect them.
FedRAMP High Authorized
Deploy Qualys TotalAppSec within authorized federal boundaries without added ATO effort. Continuously discover, test, and remediate every web application and API using 427 audit-ready controls aligned to NIST, FISMA, CISA and Zero Trust.
Watch our recent webinar to learn what your high-impact application estate exposes, and how to prove it, from inside a FedRAMP High boundary.

Analyst Recognition and Related Resources
Comprehensive Discovery and Visibility
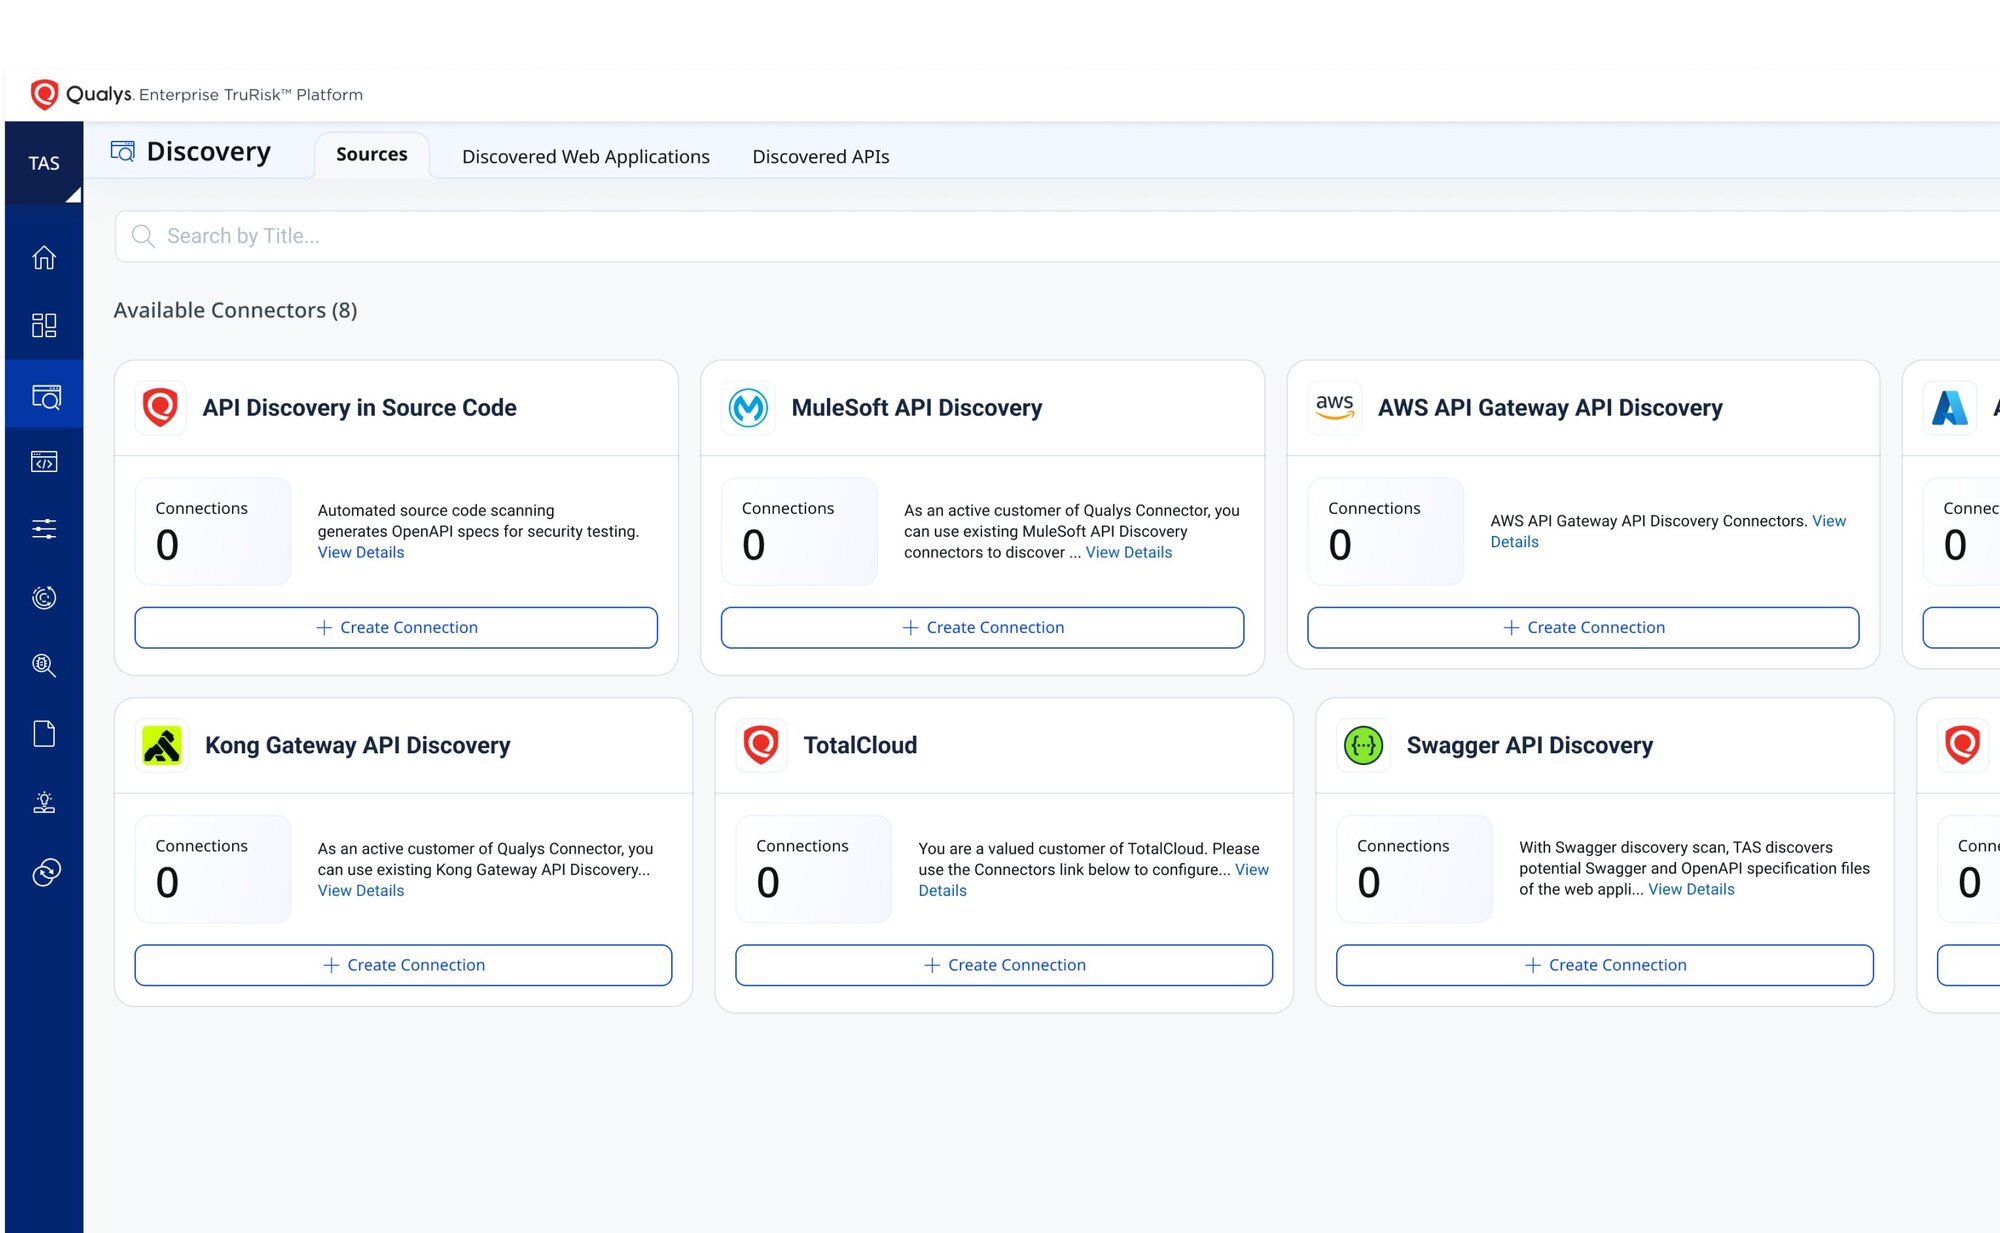
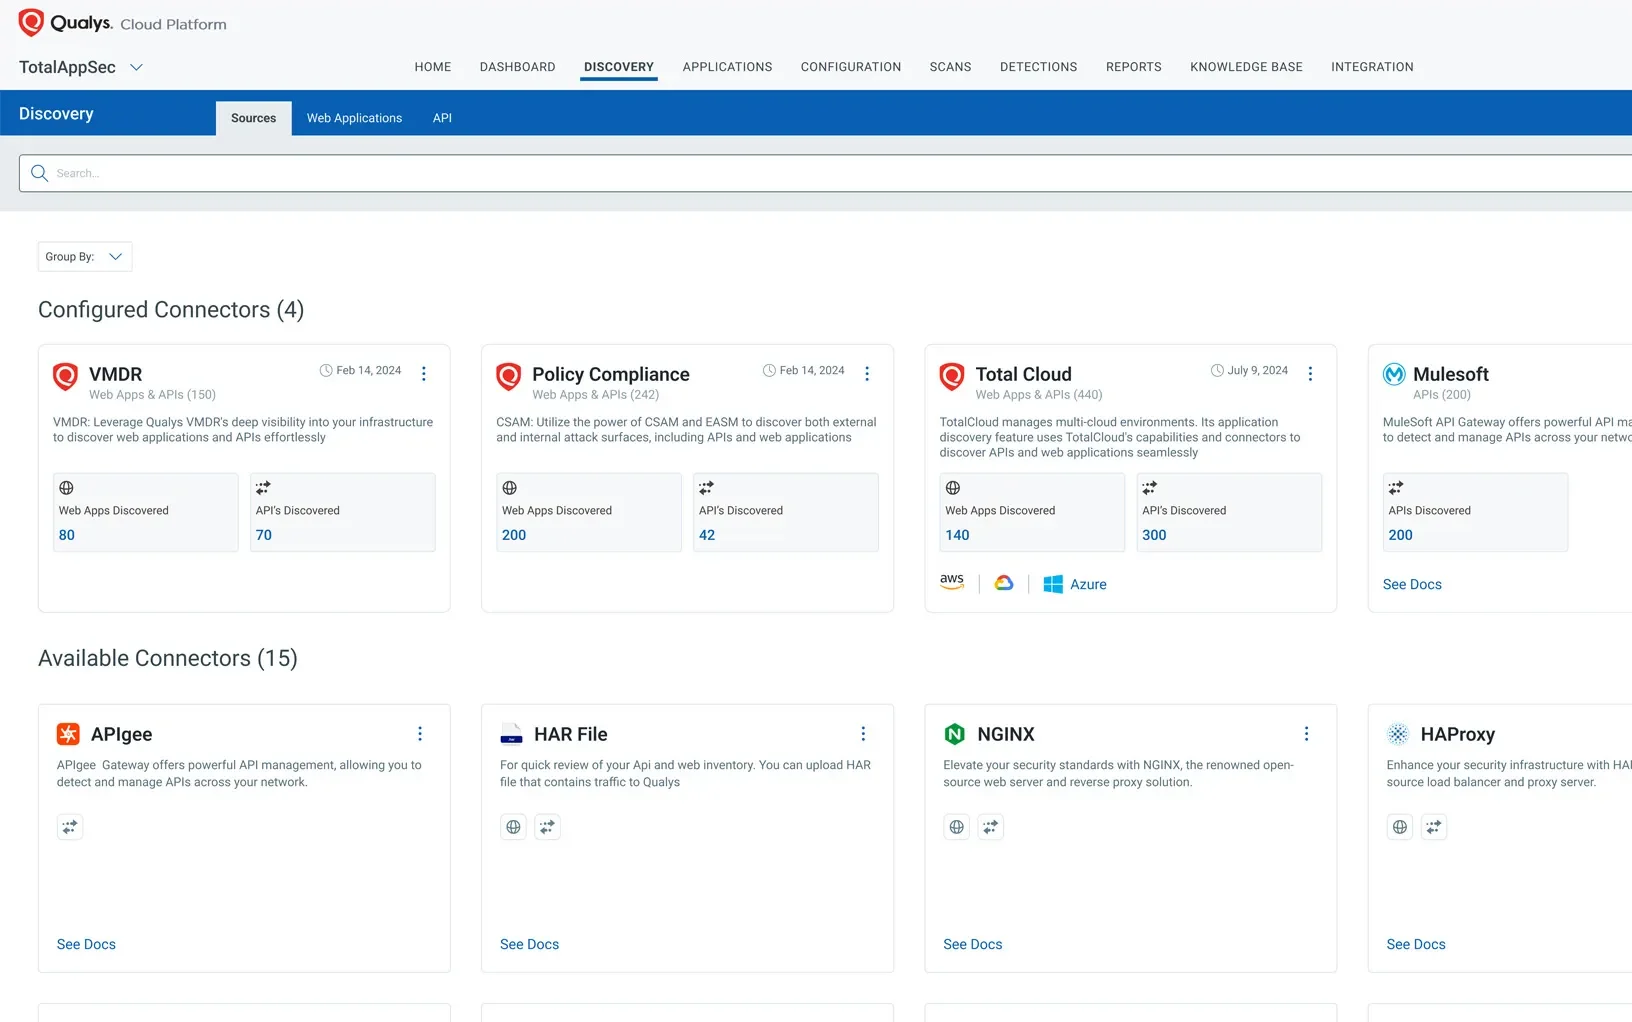
TotalAppSec continuously discovers web applications and APIs across multi-cloud and on-prem environments, detecting known and shadow assets that other tools miss. By integrating with Qualys EASM, CSAM, and third-party sources like Postman and MuleSoft, it creates a single, unified inventory to eliminate blind spots and support continuous risk management.
AI-Powered Scanning and TruRisk™ Prioritization
Automated Remediation and Continuous Compliance
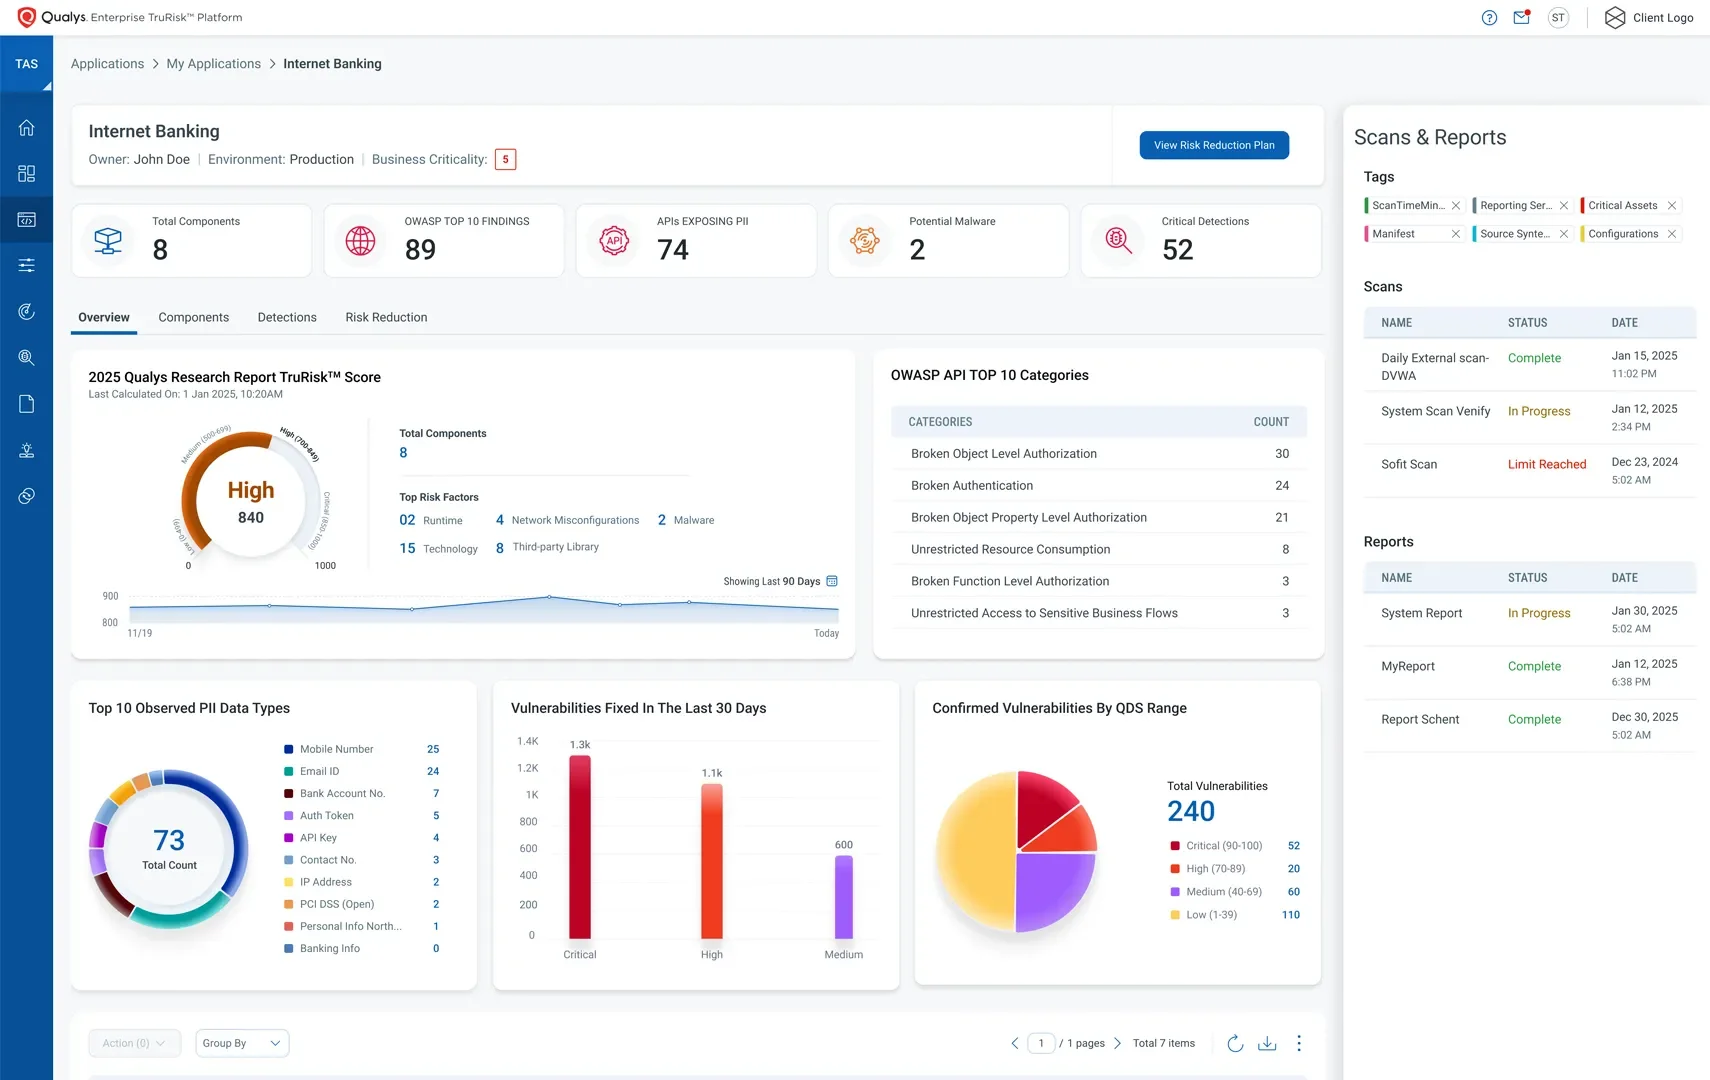

Qualys TotalAppSec is an AI-powered unified application security solution that combines web application scanning, API security testing, and malware detection in a single product. It discovers every web app and API across on-prem, multi-cloud, containers, and API gateways, then tests, prioritizes, and remediates risk from one console.
TotalAppSec automatically discovers APIs and tests them against OWASP API Top 10 vulnerabilities, including authentication bypass, injection flaws, and sensitive data exposure across REST and SOAP APIs. It performs configurable access control testing for BOLA, BFLA, and BUA, and validates API implementations against OpenAPI v3 specifications.
Yes. TotalAppSec provides complete detection-level testing against the OWASP Top 10 for web applications and the OWASP API Security Top 10 for APIs, covering both from a single scan workflow.
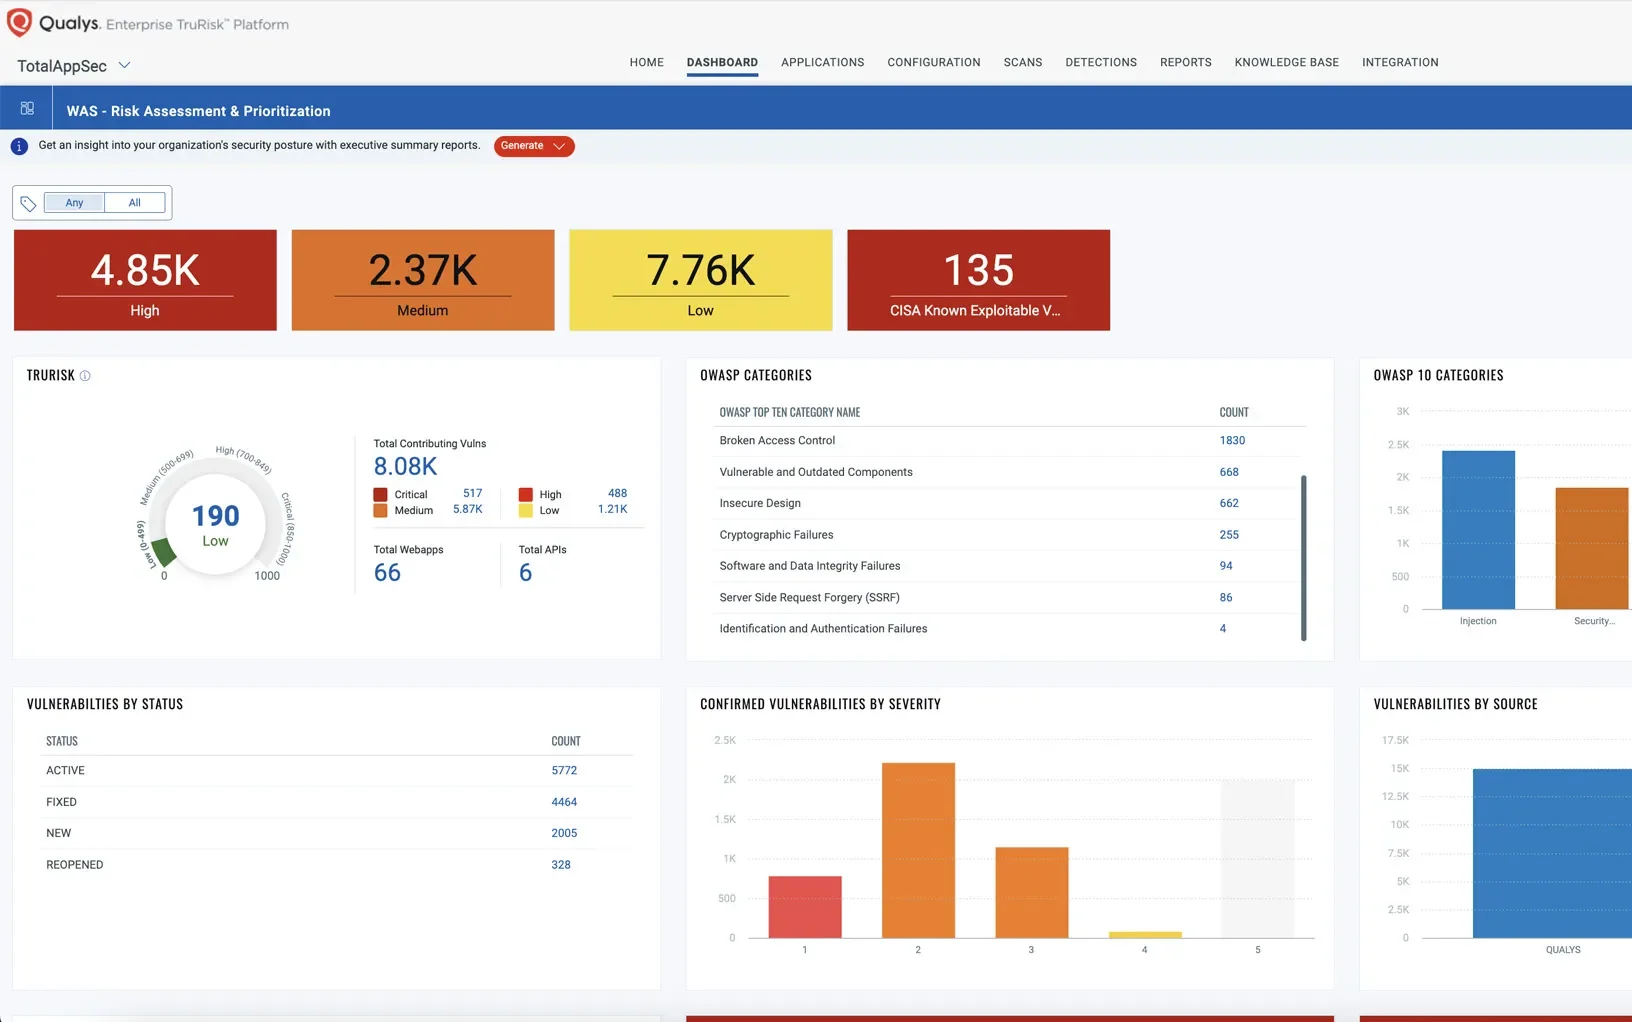
TotalAppSec prioritizes using Qualys TruRisk scoring, which ranks findings by exploitability, asset criticality, and business impact using 25+ threat intelligence feeds instead of CVSS severity alone. TruConfirm validates exploitability before findings reach your triage queue, eliminating 95% of alert noise.
TotalAppSec provides continuous compliance testing for PCI DSS 4.0.1, GDPR, HIPAA, and OpenAPI (OAS) v3. It covers web apps and APIs in a single scan cycle and produces attestation-ready reports for quarterly ASV validation. Compliance evidence comes as a by-product of testing, not something you assemble before an audit.
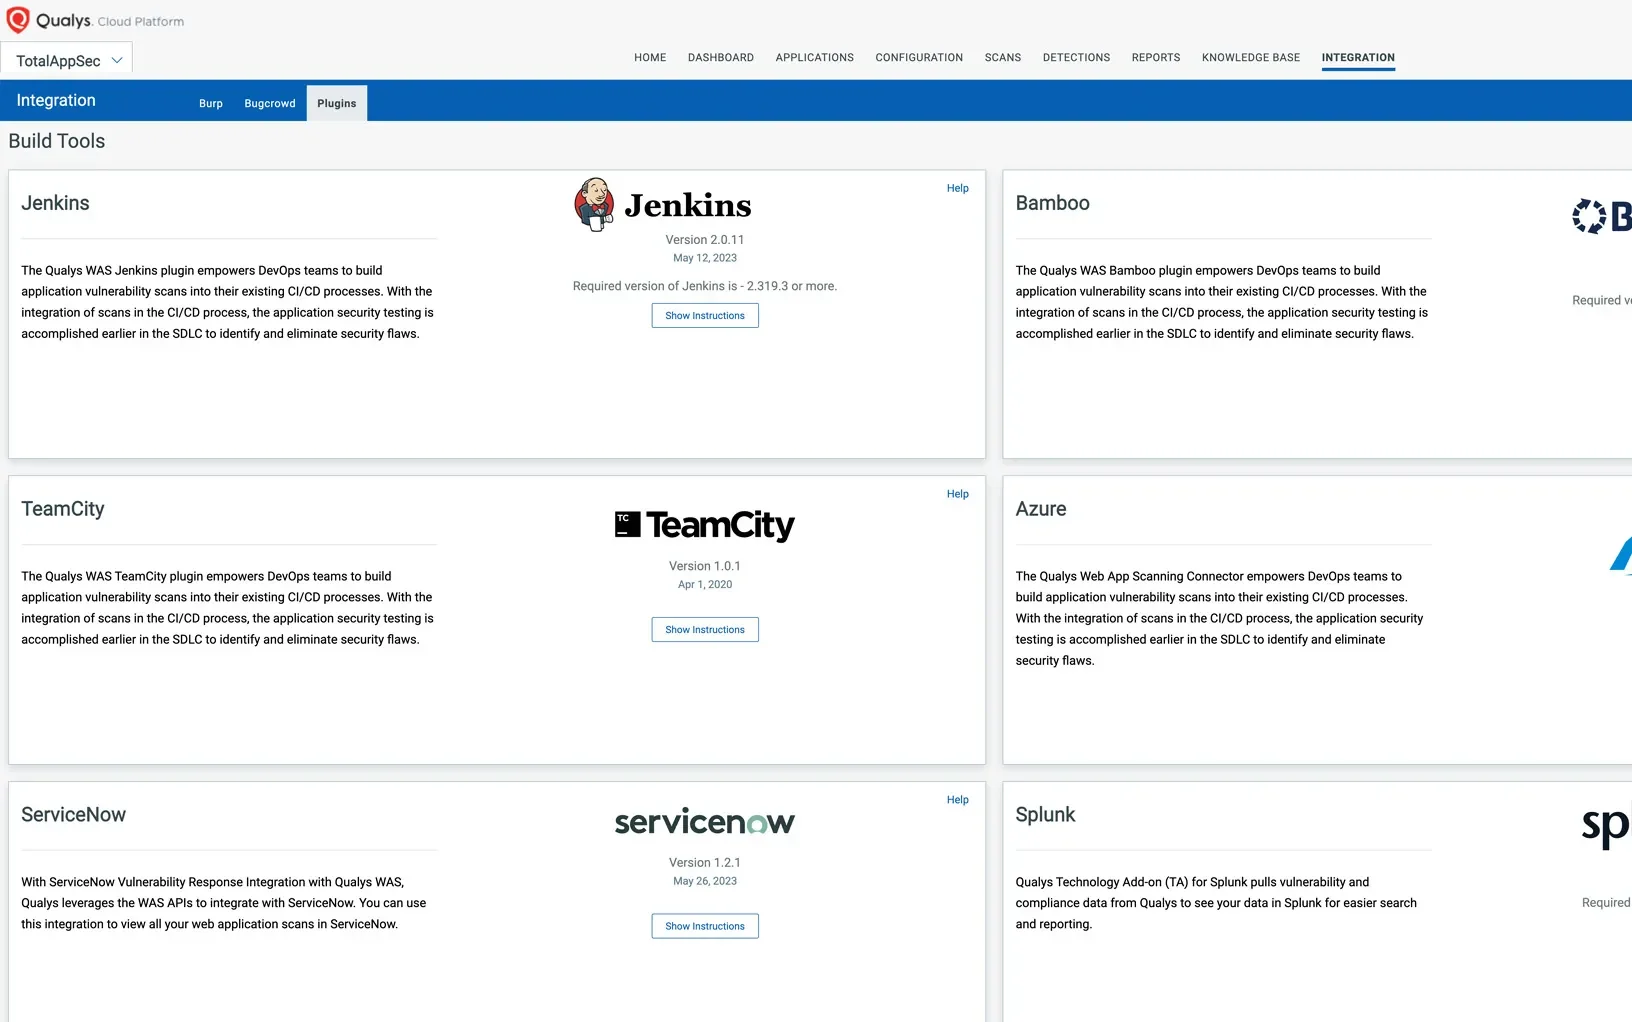
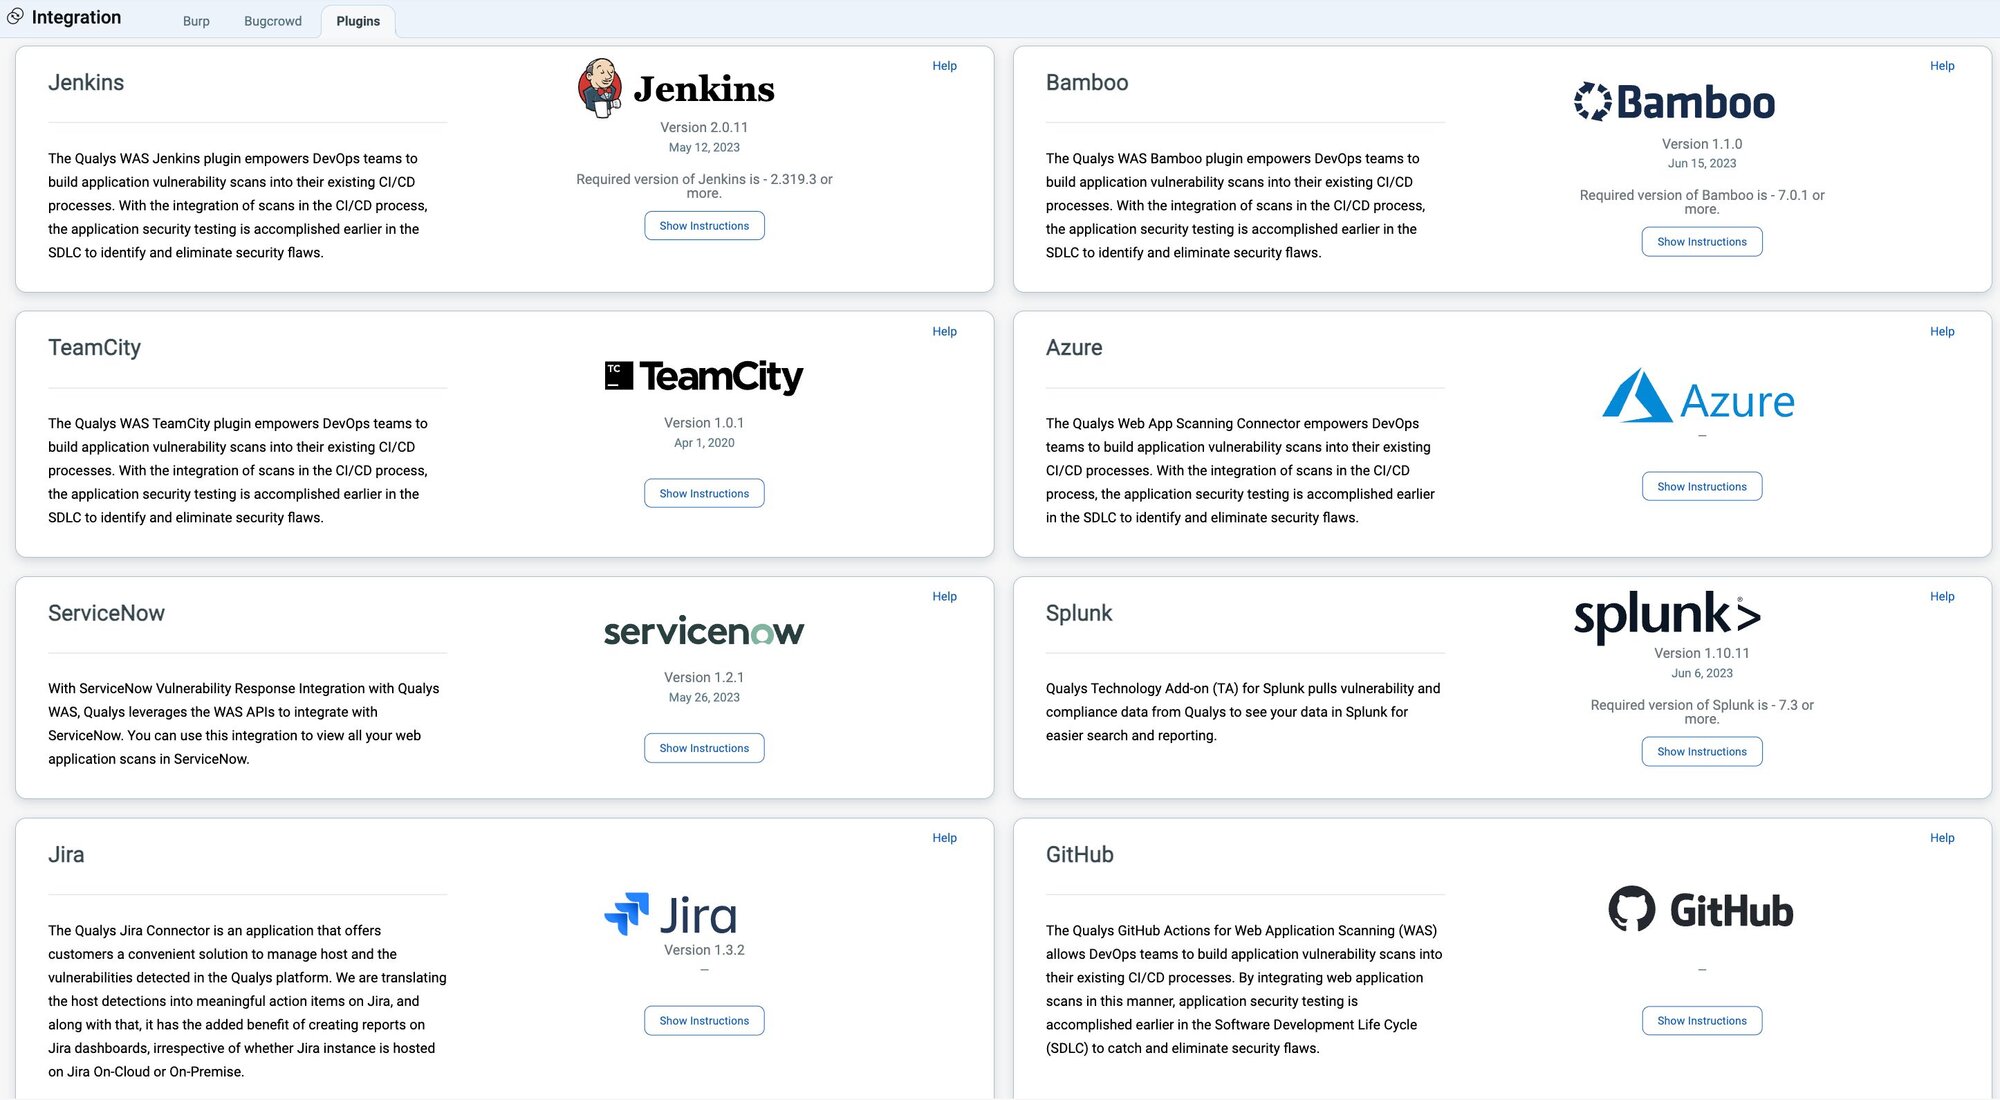
TotalAppSec integrates natively with Jenkins, Azure DevOps, and GitHub Actions for automated pre-deployment testing with pass/fail security gates. It also connects with Jira and ServiceNow for automated ticketing routed to the team that owns the code. This supports both shift-left testing in the pipeline and shift-right remediation in production.
TotalAppSec uses AI to profile each application and focus scanning on high-risk areas, cutting scan time by 50% with no loss in accuracy. It autonomously generates signatures for newly disclosed CVEs, uses deep learning models to detect zero-day web malware at ~99% accuracy, and discovers LLMs, AI agents, and MCP servers embedded in scanned applications.
TotalAppSec uses deep learning-based detection to identify known and zero-day malware in web applications at ~99% accuracy. It continuously monitors malicious code injection, unauthorized modifications, and suspicious behavior patterns that signature-based tools miss.