Comprehensive and flexible vulnerability scanning with Six Sigma accuracy and context-based risk prioritization.
Detect vulnerabilities across all cloud resources with Six Sigma level accuracy from over 180K vulnerabilities from 25+ threat sources.
Introducing TotalCloud™ with TruRisk Insights
Detect vulnerabilities in less than 10 minutes
Scan with flexibility and precision
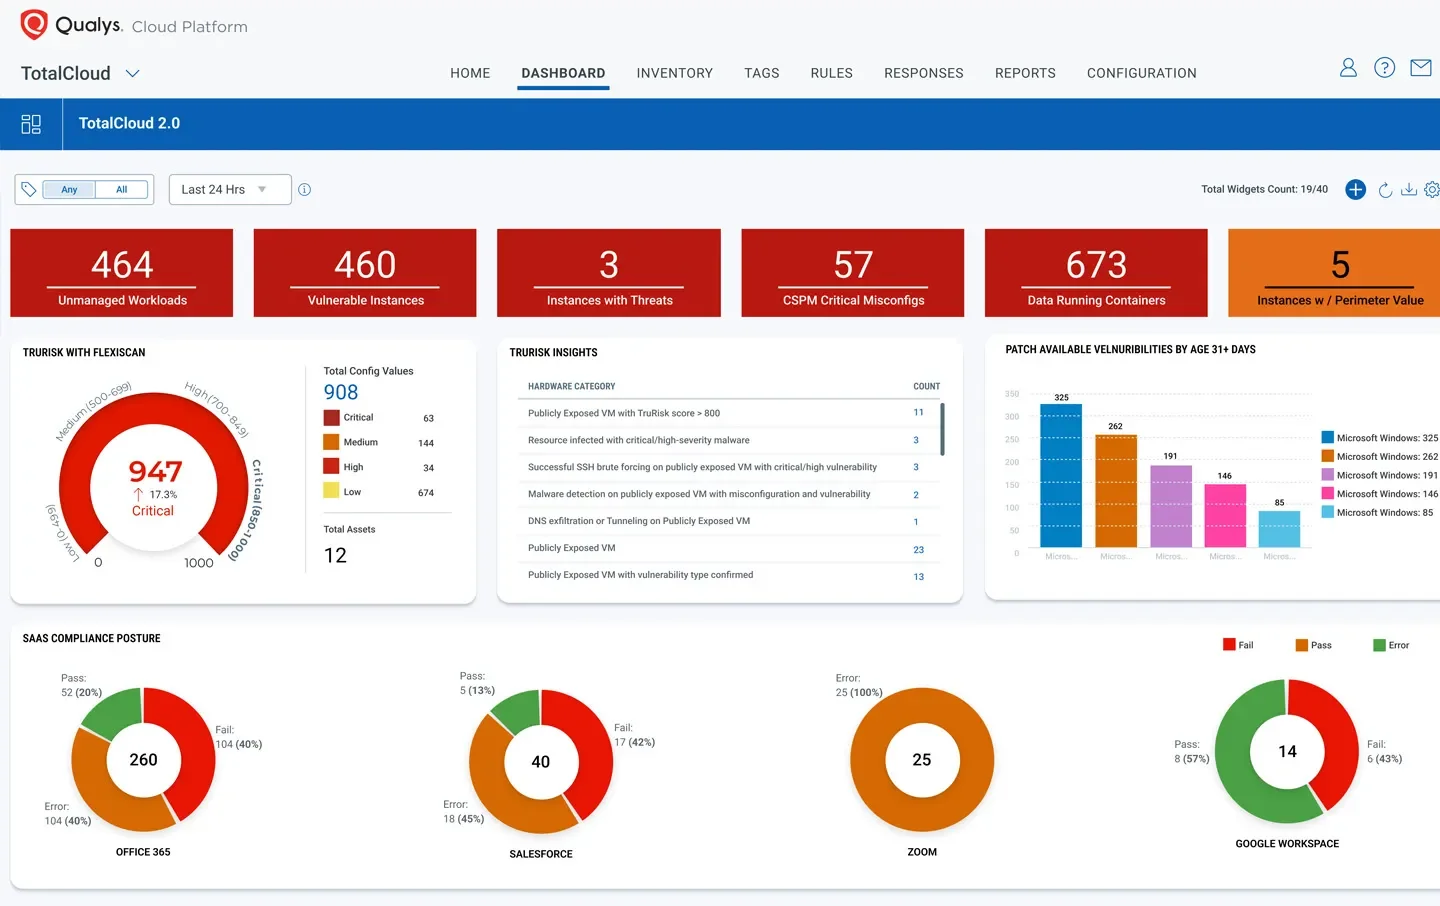
One prioritized view or risk, based on context

Deploying Qualys CDR for AWS and Azure with just a few clicks, in a matter of minutes, across multiple AWS and Azure subscriptions, was a game changer for our security team. We have a complex environment with many controls, and TotalCloud team worked with us on integration with existing solutions including Secure Web Gateways and integrated SIEM. With their engineering team, together made sure all the security finds were tightly integrated with our SIEM platform. I have rarely seen this level of competency and engagement effort from a vendor.
Qualys is enhancing its widely used platform to deliver visibility, context, speed, automation, and orchestration in a comprehensive solution to help organizations scale their security and compliance programs for modern software development. Qualys TotalCloud incorporates security into development workflows, enabling them to release secure, reliable code, while giving security teams the control and visibility they need to manage risk by reducing their attack exposure and rapidly responding to threats.
The Qualys approach [to runtime security] empowers security to follow the container image with built-in instrumentation, enabling visibility and behavior enforcement for running containers across all types of container infrastructure.

The 2024 Verizon Data Breach Investigation Report shows a 180% increase in attacks exploiting vulnerabilities as the initial entry point, accounting for 14% of all breaches.
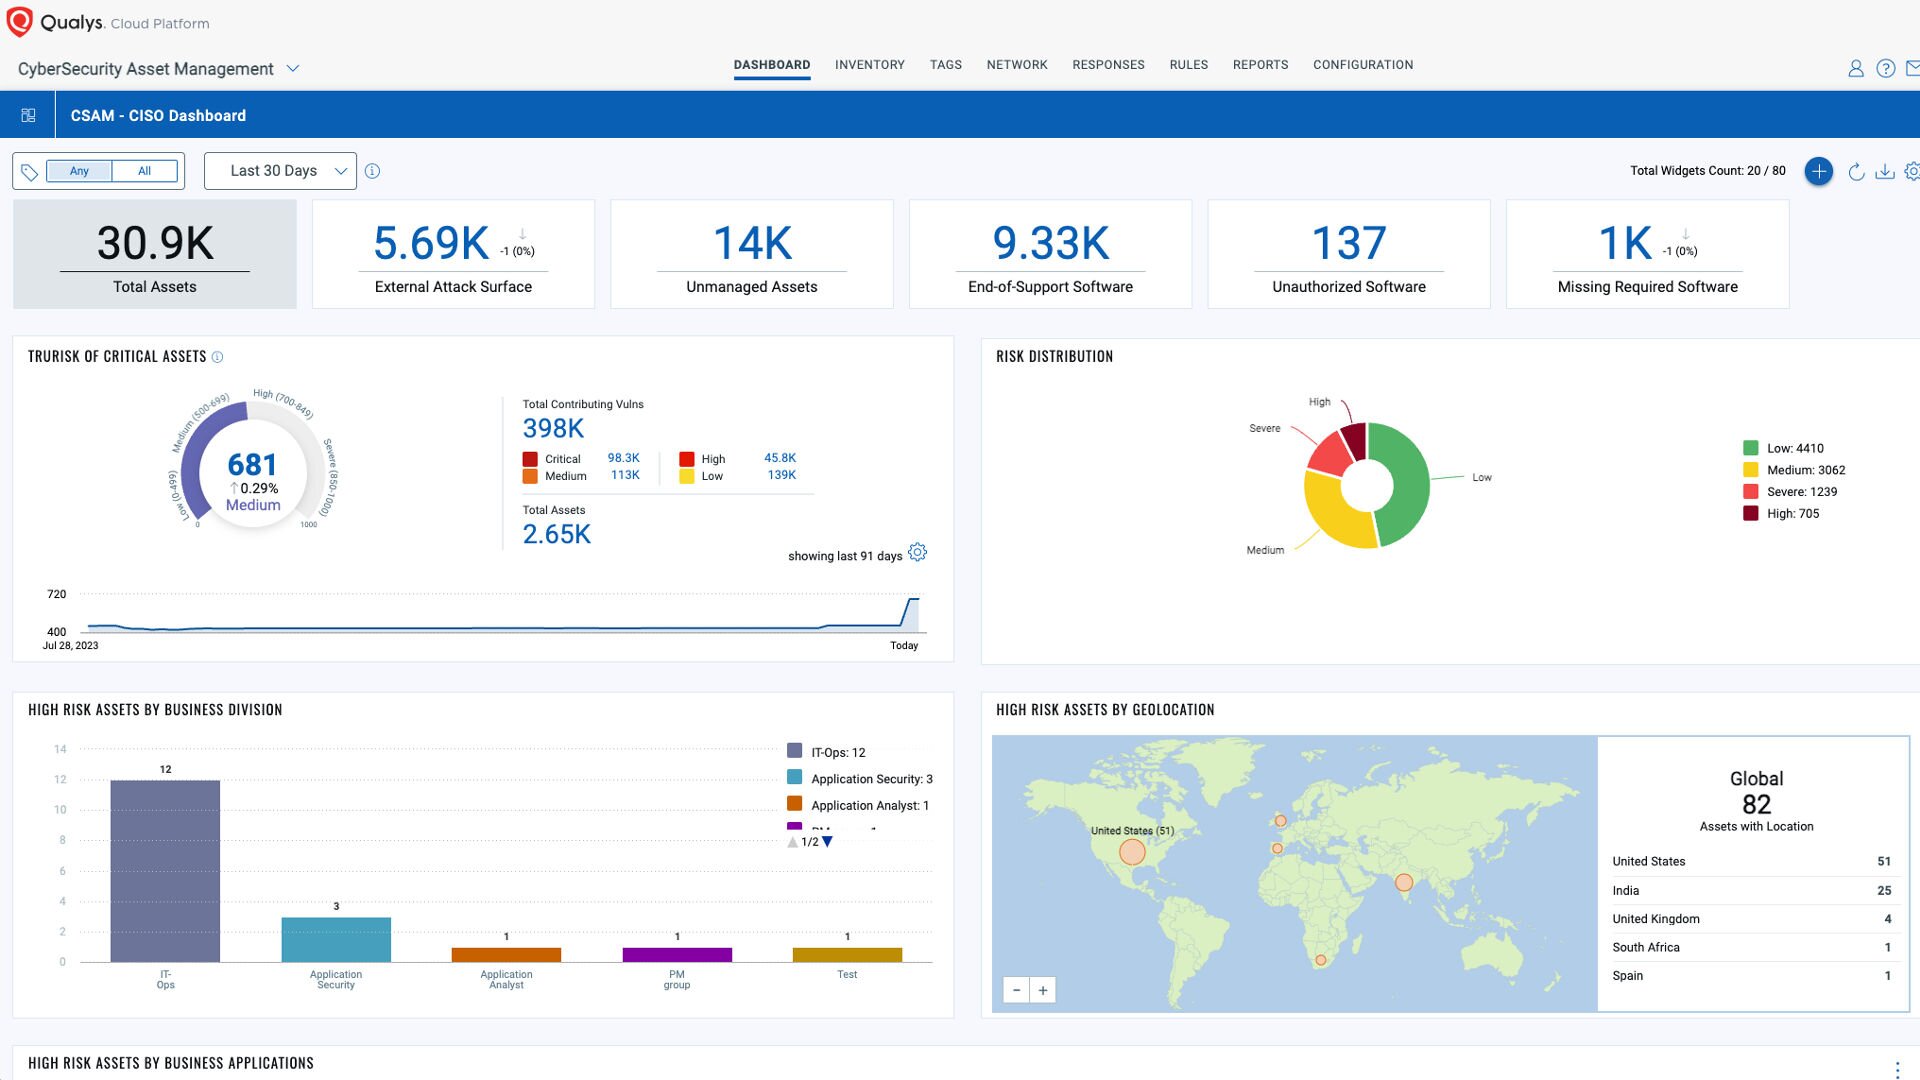
The Enterprise TruRisk Platform provides you with a unified view of your entire cyber risk posture so you can efficiently aggregate and measure all Qualys & non-Qualys risk factors in a unified view, communicate cyber risk with context to your business, and go beyond patching to eliminate the risk that threatens the business in any area of your attack surface.

Cloud Workload Protection secures the operating systems, software, and applications running inside cloud workloads. Qualys CWP identifies vulnerability and workload risk and connects those findings with the broader exposure, posture, identity, and threat context available in TotalCloud.
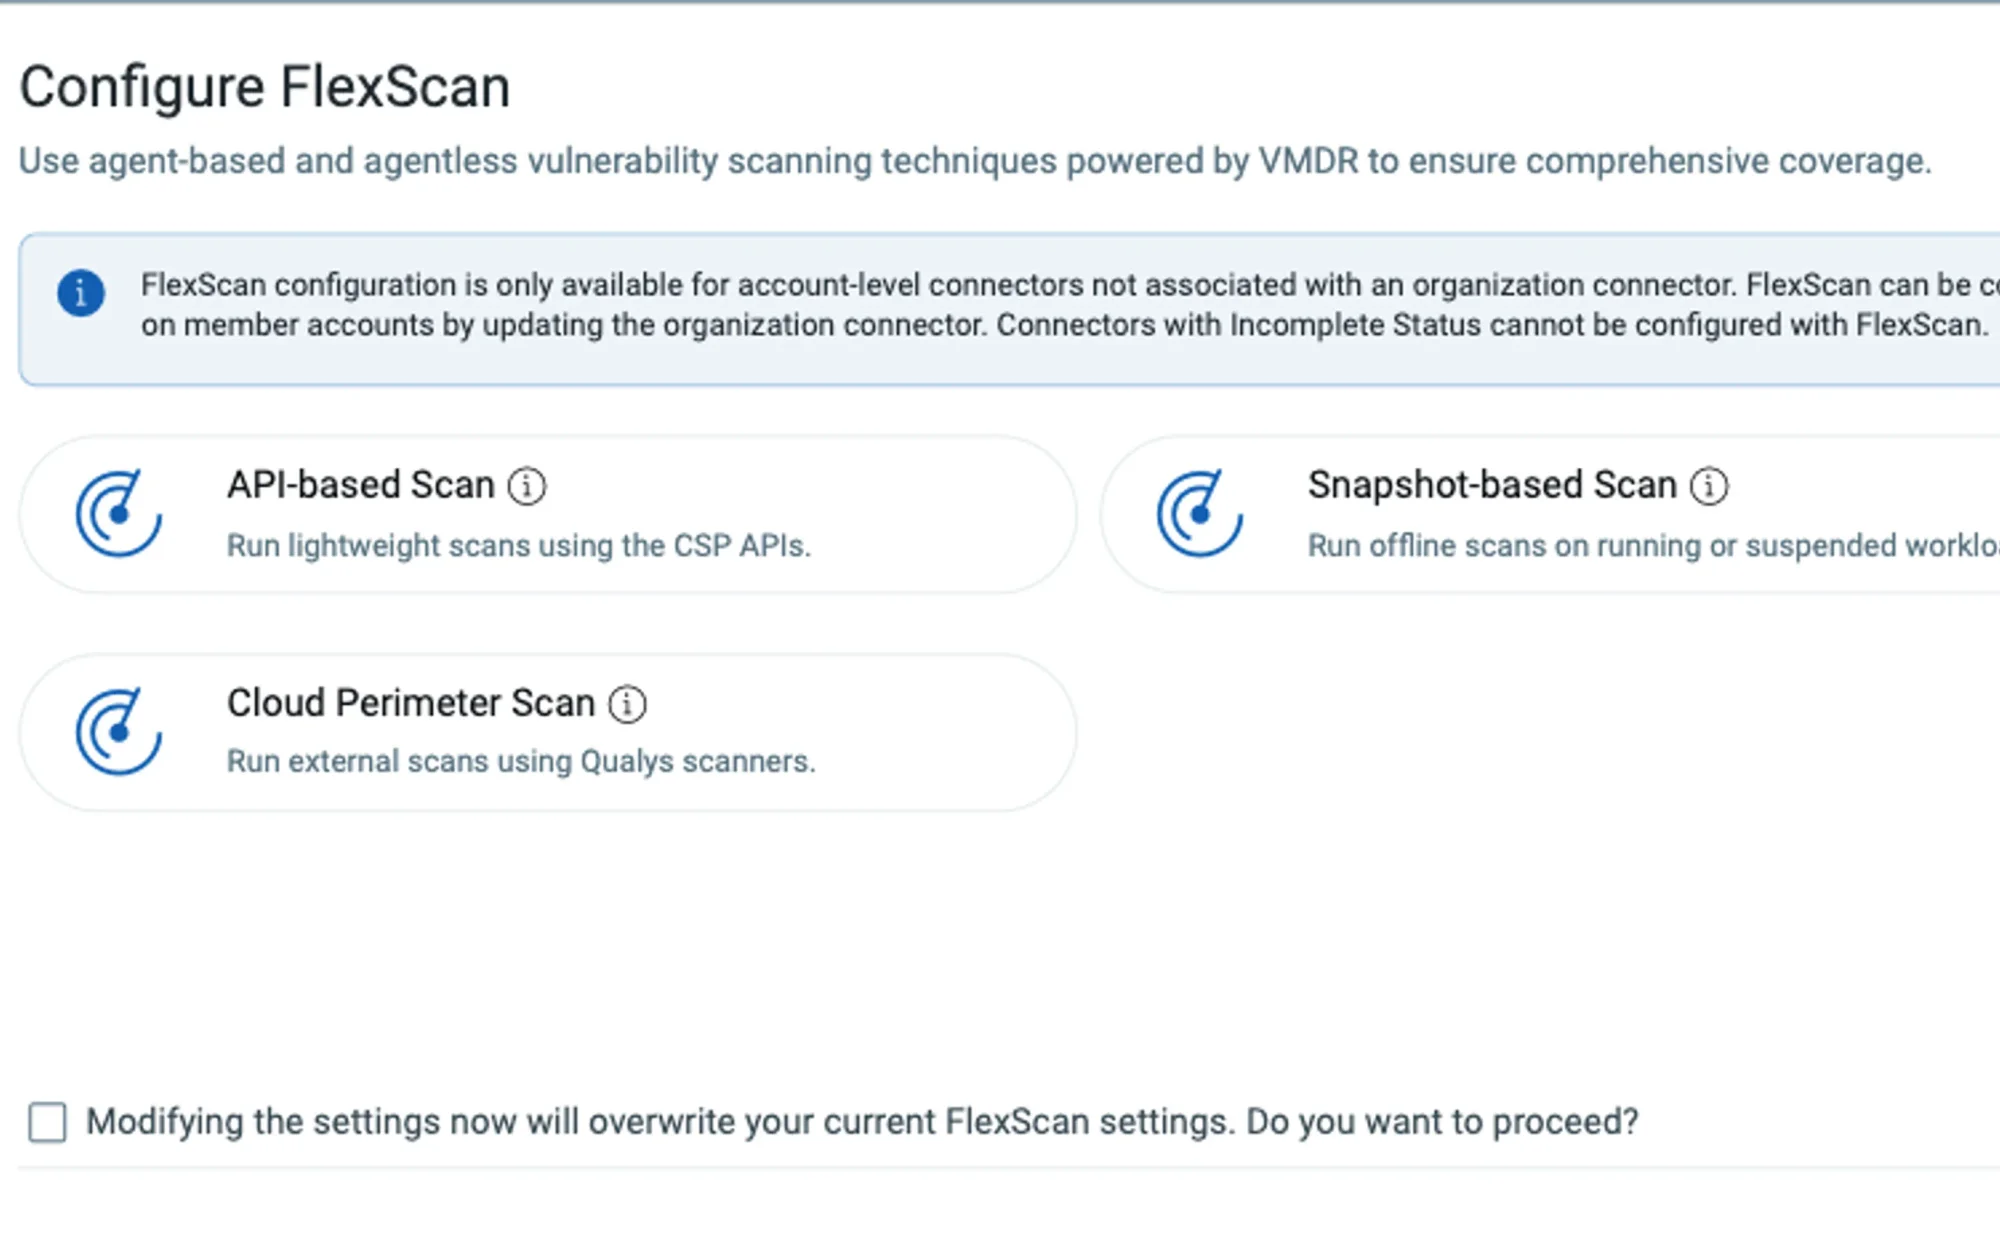
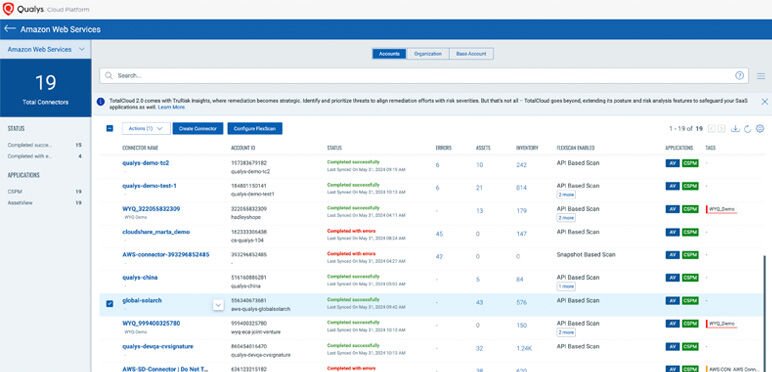
Qualys supports multiple assessment methods so organizations can match security depth to each workload: Cloud Agents for continuous deep visibility, snapshot-based agentless assessment for rapid zero-touch scanning, network-based scanning, and cloud API-based assessment. These methods can be combined through FlexScan rather than forcing one deployment model across the environment.
Qualys FlexScan combines multiple assessment methods so newly discovered and ephemeral workloads can be evaluated without relying exclusively on a traditional agent scan cycle.
For supported serverless services, TotalCloud can provide workload and cloud-security context such as vulnerabilities, software composition, and configuration posture. Serverless findings can be correlated with broader cloud-risk context.
CSPM evaluates how cloud infrastructure is configured. CWP evaluates the software and operating environment running on that infrastructure. For example, CSPM may identify that a VM is publicly exposed while CWP identifies vulnerable software inside the VM.
Agentless assessment is useful for rapid deployment, broad coverage, and ephemeral workloads. Agents can provide deeper and more continuous workload visibility. Combining both helps balance coverage and depth.
Qualys combines vulnerability intelligence with cloud context such as asset criticality, exposure, exploitability, and other security signals so teams can prioritize vulnerabilities that create meaningful risk in the deployed environment.
CWP and adjacent TotalCloud runtime capabilities provide workload and runtime context for supported environments. Runtime threat detection is strengthened when CWP is combined with Container Runtime Security and Cloud Detection & Response.
CWP addresses workload-level risk, while Kubernetes and Container Security adds Kubernetes-aware context such as clusters, pods, images, deployment policy, and orchestration posture. Together they provide a more complete view of cloud-native workload risk.