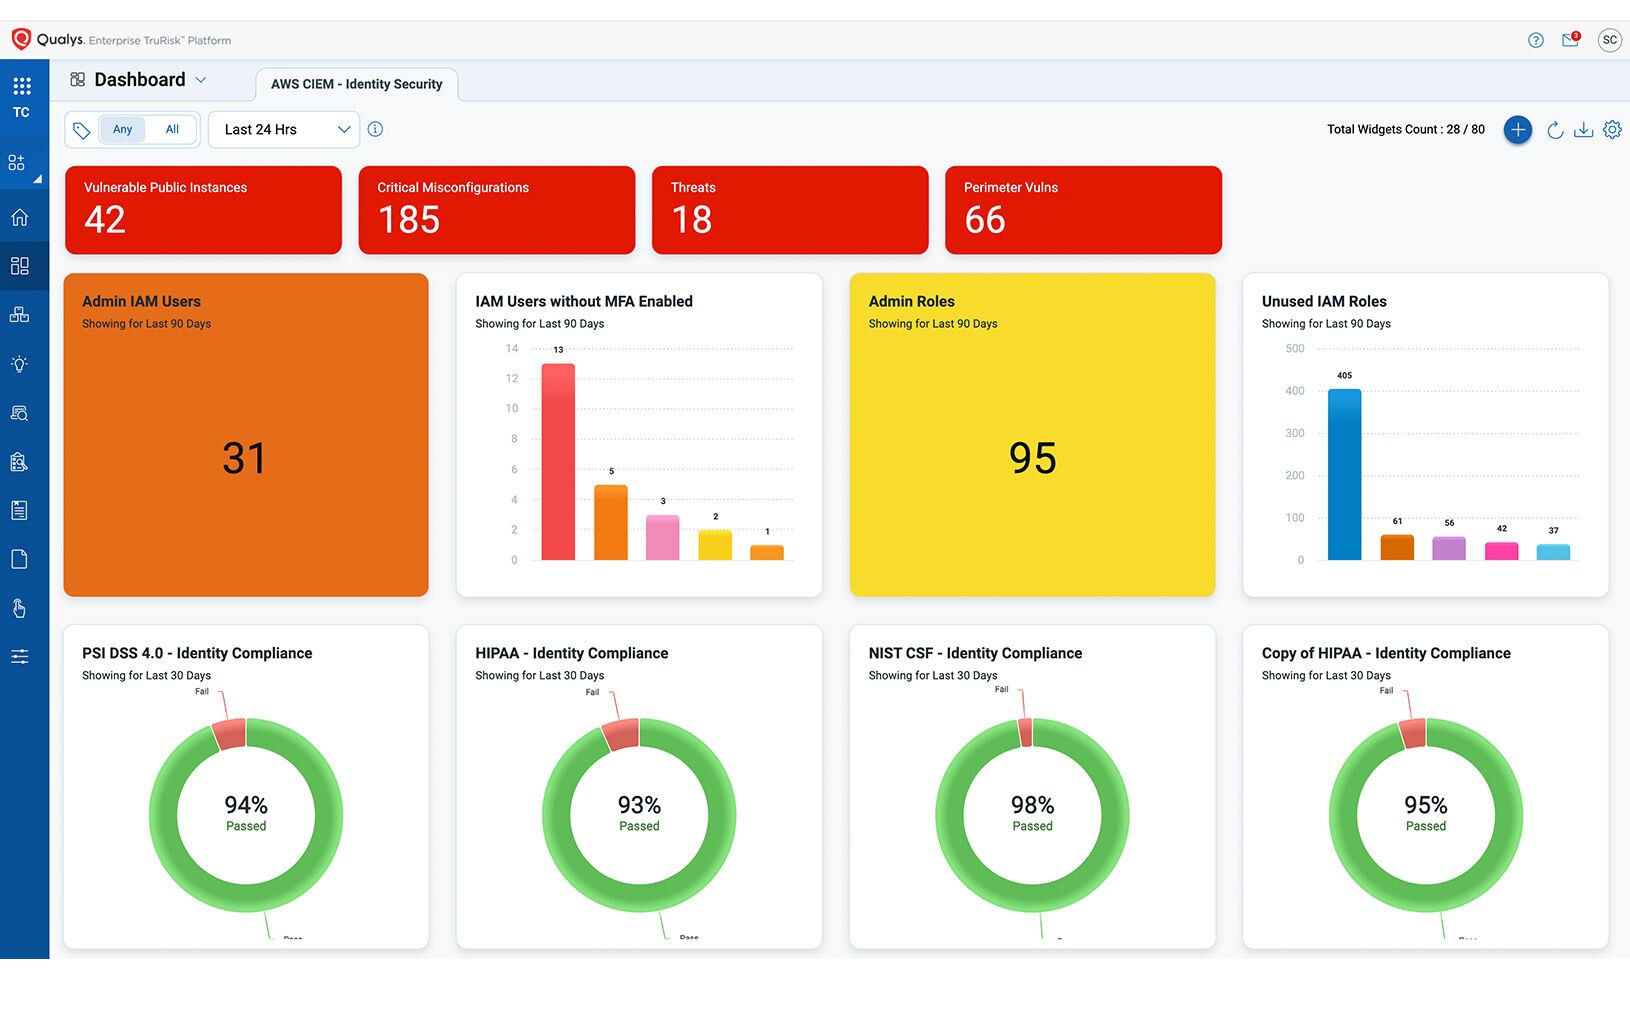
Gain complete visibility and control over cloud permissions to minimize risk and enforce least privilege at scale
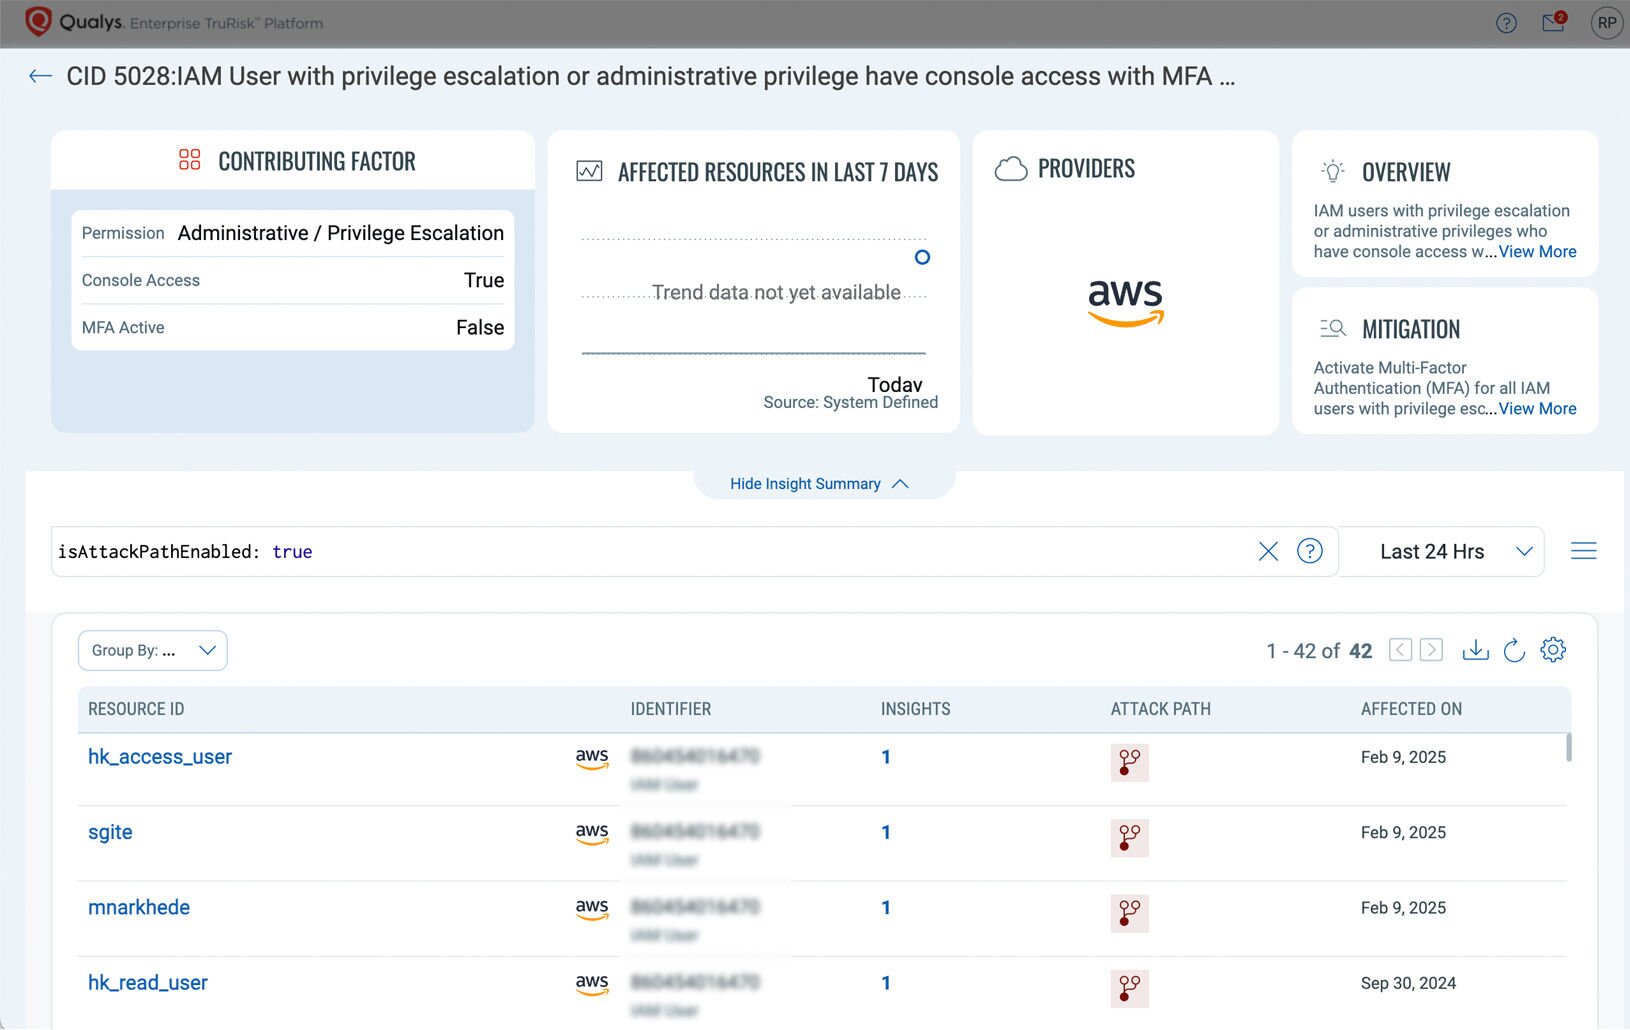
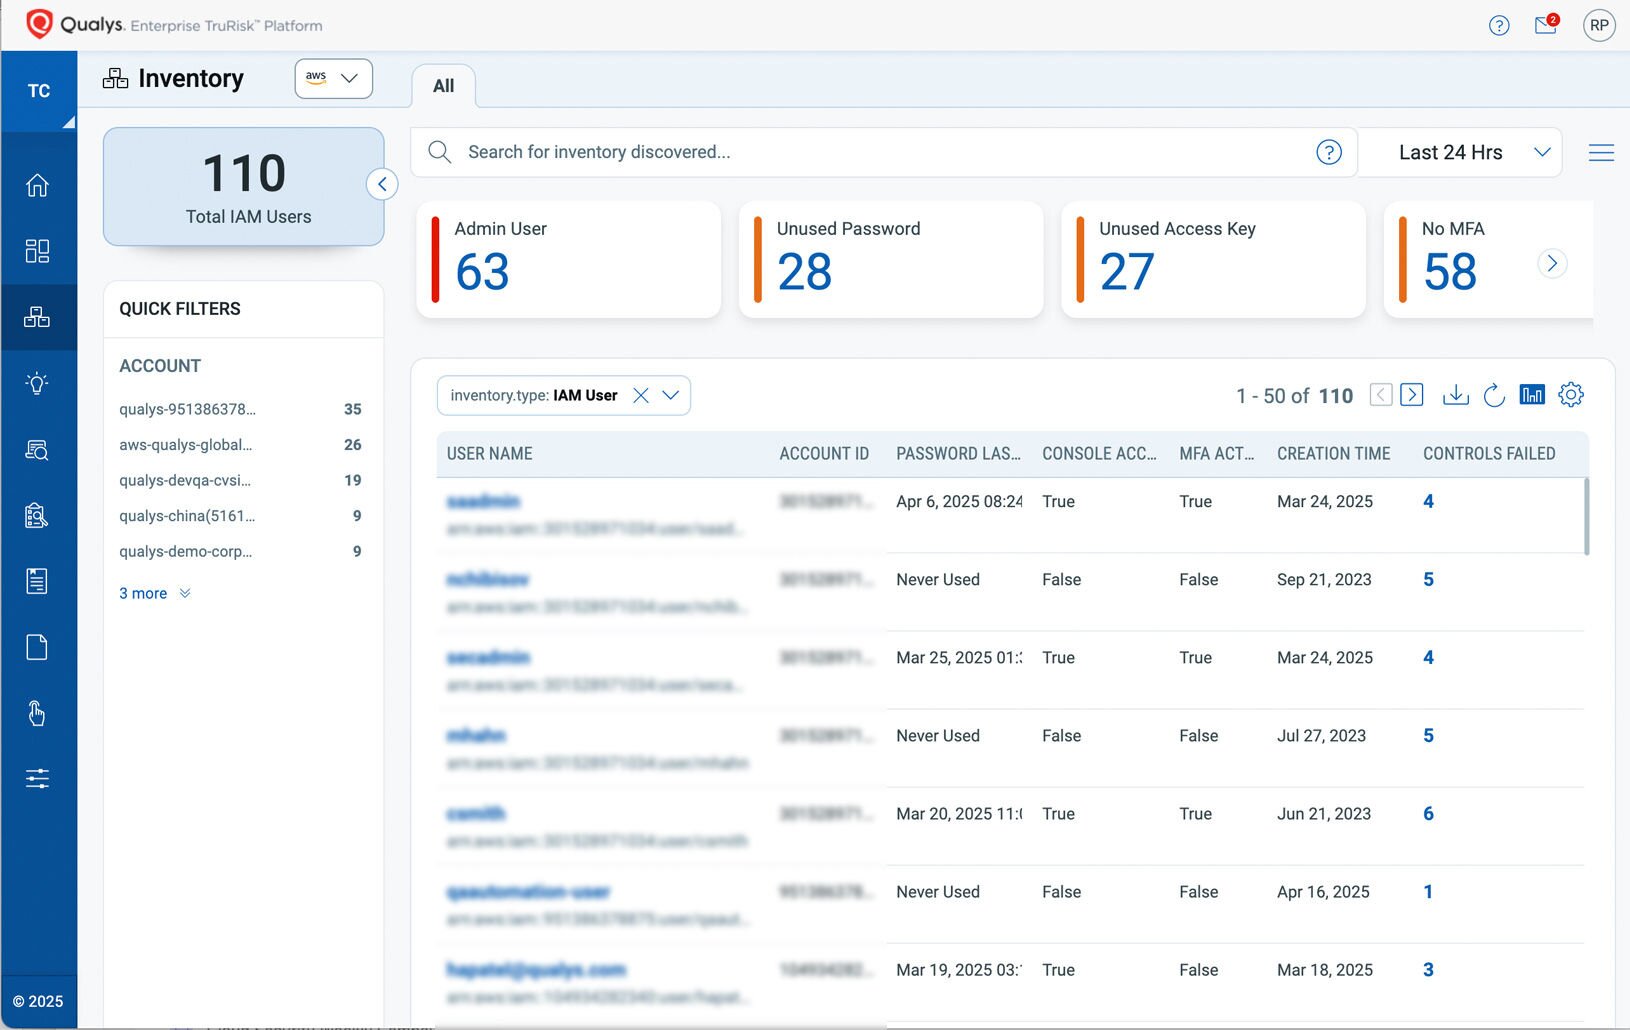
Discover Identities and Entitlements
Compliance Governance
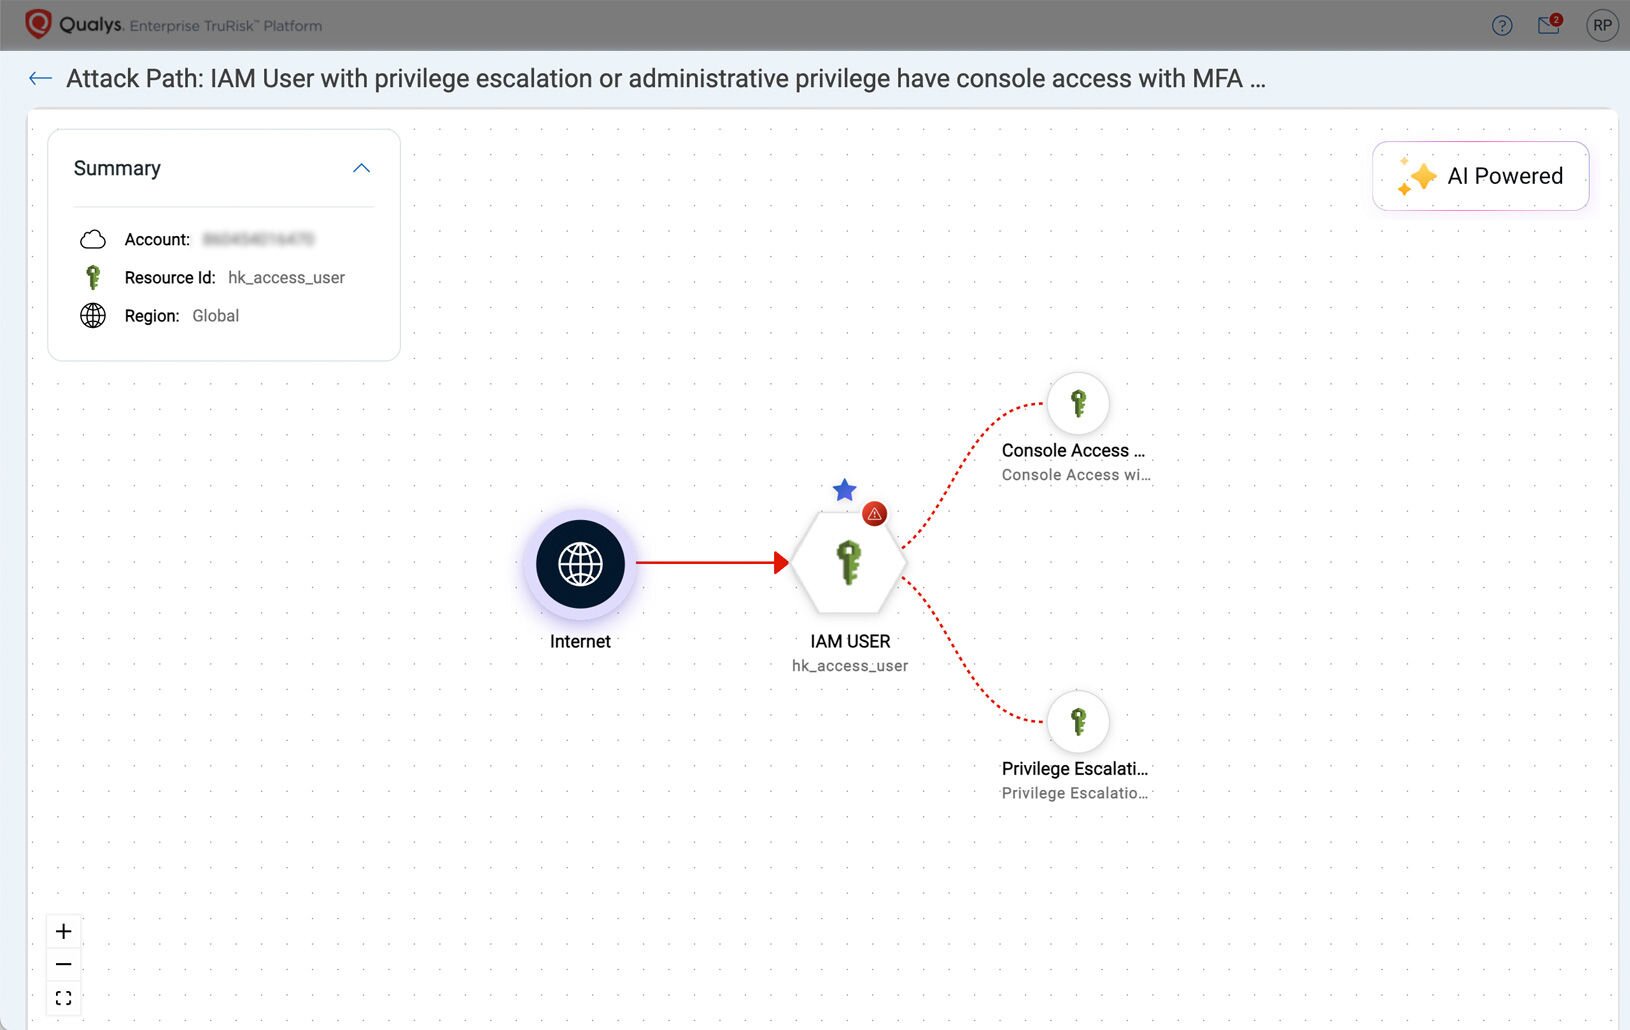
Prioritize with TruRisk Insights
Remediate to Reduce Risk

Deploying Qualys CDR for AWS and Azure with just a few clicks, in a matter of minutes, across multiple AWS and Azure subscriptions, was a game changer for our security team. We have a complex environment with many controls, and TotalCloud team worked with us on integration with existing solutions including Secure Web Gateways and integrated SIEM. With their engineering team, together made sure all the security finds were tightly integrated with our SIEM platform. I have rarely seen this level of competency and engagement effort from a vendor.
Qualys is enhancing its widely used platform to deliver visibility, context, speed, automation, and orchestration in a comprehensive solution to help organizations scale their security and compliance programs for modern software development. Qualys TotalCloud incorporates security into development workflows, enabling them to release secure, reliable code, while giving security teams the control and visibility they need to manage risk by reducing their attack exposure and rapidly responding to threats.
The Qualys approach [to runtime security] empowers security to follow the container image with built-in instrumentation, enabling visibility and behavior enforcement for running containers across all types of container infrastructure.

Detect Risky identities and access privileges across multi-cloud environments, providing visibility, control, and enforcement of least-privilege access.
Introducing TotalCloud™ with TruRisk Insights
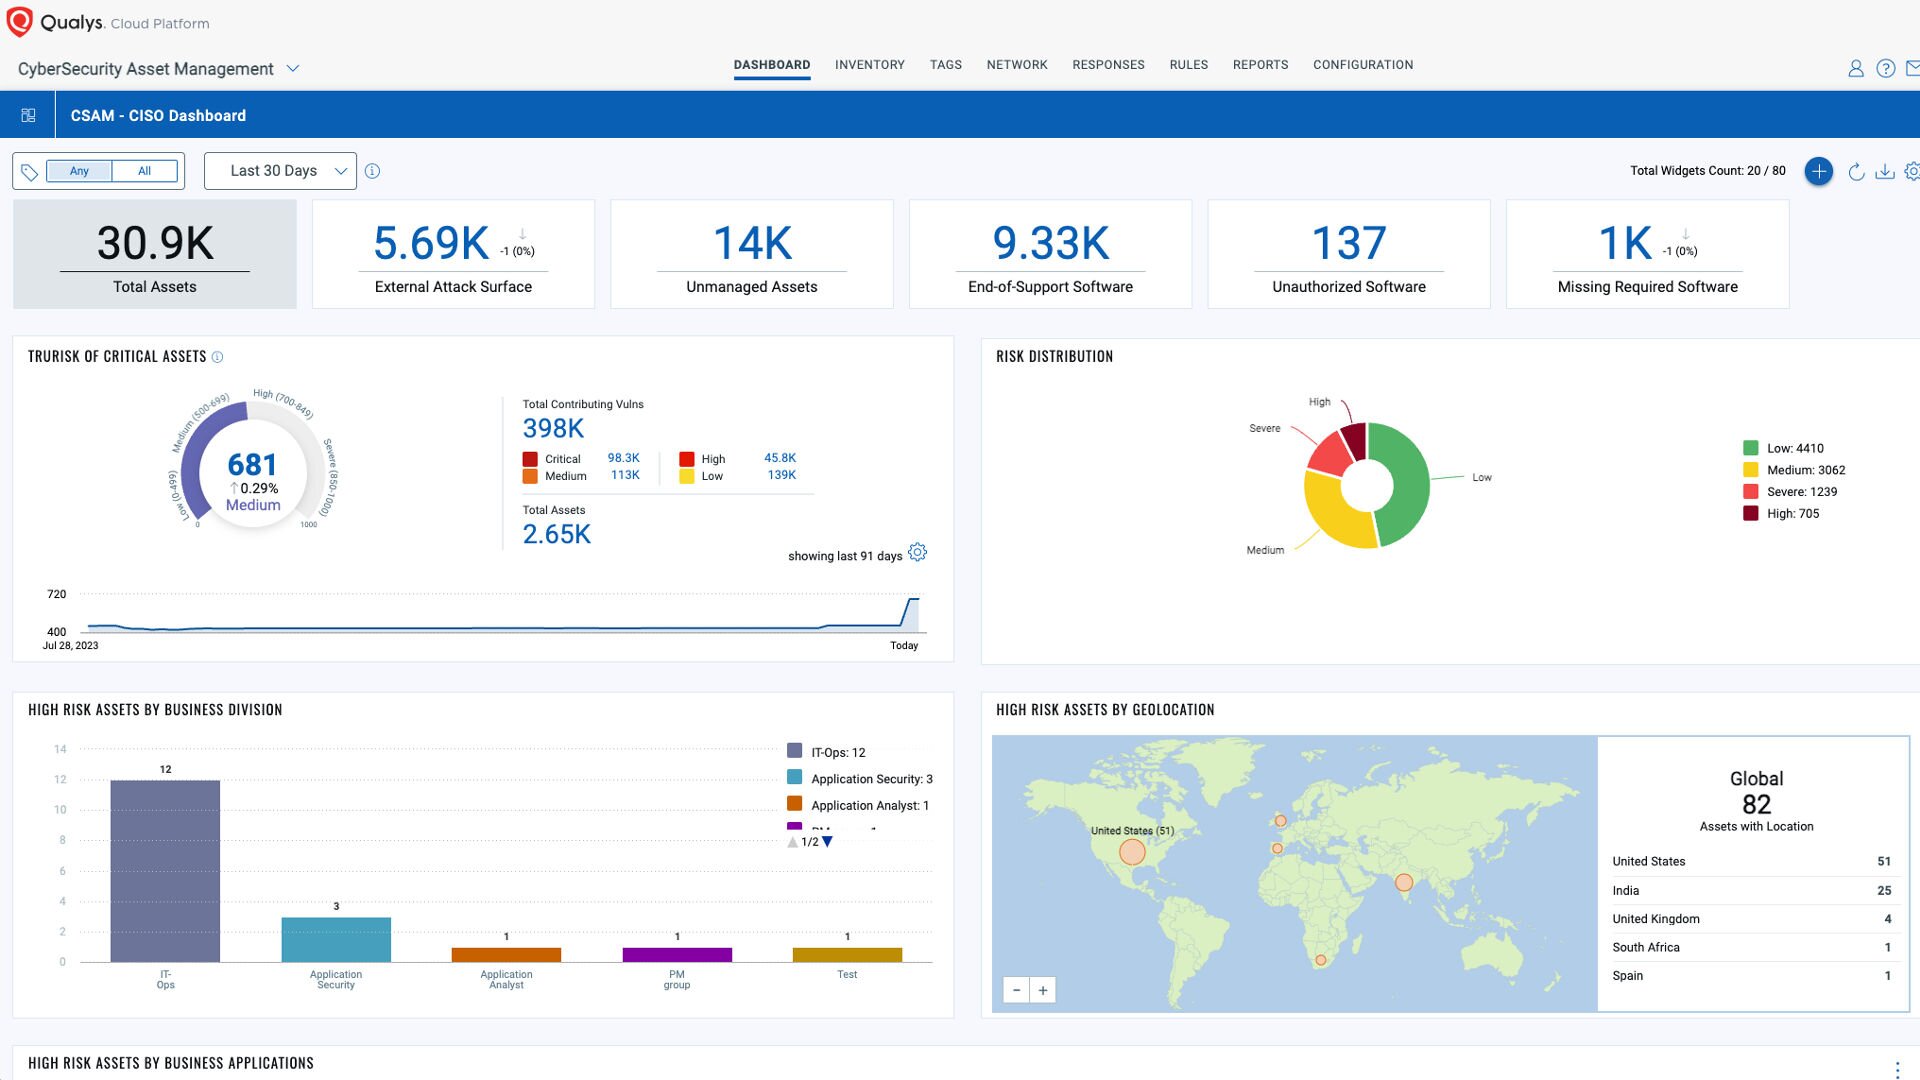
The Enterprise TruRisk Platform provides you with a unified view of your entire cyber risk posture so you can efficiently aggregate and measure all Qualys & non-Qualys risk factors in a unified view, communicate cyber risk with context to your business, and go beyond patching to eliminate the risk that threatens the business in any area of your attack surface.

CIEM helps organizations understand who and what can access cloud resources, identify excessive or risky permissions, and reduce access according to least-privilege principles. Qualys brings identity and entitlement risk into TotalCloud so permissions can be evaluated alongside other cloud risks.
CIEM is designed to analyze both human and nonhuman cloud identities, including users, groups, roles, service principals, managed identities, service accounts, and other supported workload identities.
Yes. Qualys provides inventory and relationship context for supported cloud identities, resources, roles, and permissions so teams can understand who or what can access critical cloud assets.
Effective permissions describe what an identity can actually do after accounting for roles, policy inheritance, group membership, and resource-level access—not simply what one policy document says. This creates a more accurate view of access risk.
CIEM can identify risks such as excessive permissions, unused or risky access, dangerous entitlement combinations, and identity relationships that may enable privilege escalation or lateral movement.
Qualys analyzes entitlement and permission context to highlight identities with access that creates unnecessary risk. Cloud-resource and permission-usage context can then help teams determine where access should be reduced.
CIEM helps teams identify unnecessary or excessive access so permissions can be reduced to what users and workloads actually require. TotalCloud can also correlate identity risk with the assets and resources those identities can reach.
Yes. Supported cloud identity analysis includes workload-oriented identities such as service principals, managed identities, and service accounts, which are important because automation and cloud applications often receive powerful permissions.
By identifying excessive permissions, risky identity relationships, and access paths, CIEM helps teams remove the permissions attackers could use to expand access after compromise.
CIEM capabilities are designed to help surface identities and permissions that appear unused or unnecessary, allowing teams to reduce long-lived access that can become an overlooked attack path.