
TruRiskTM Platform
Interactive Guided Tours Showcasing Essential Features of the Qualys Enterprise TruRisk Platform
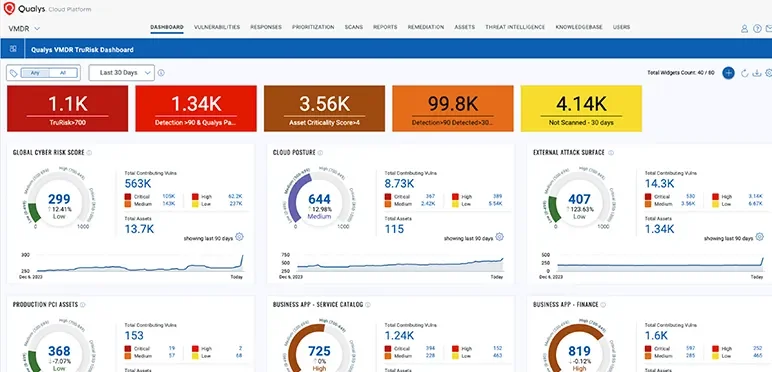
Understand the potential impact of any zero-day vulnerability to prioritize and take action quickly.
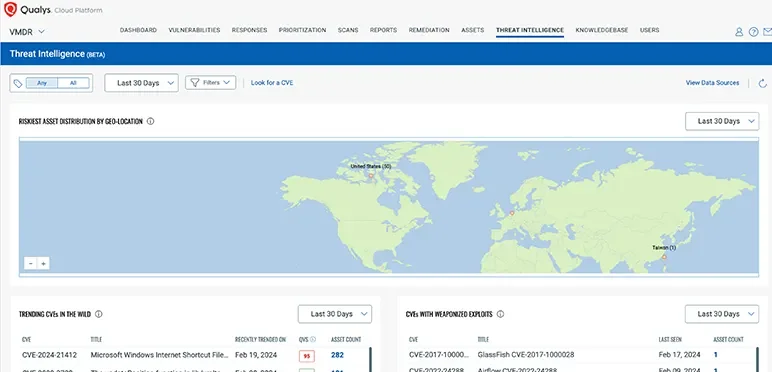
Pinpoint the cyber risk by accounting for multiplying factors beyond CVSS scores.
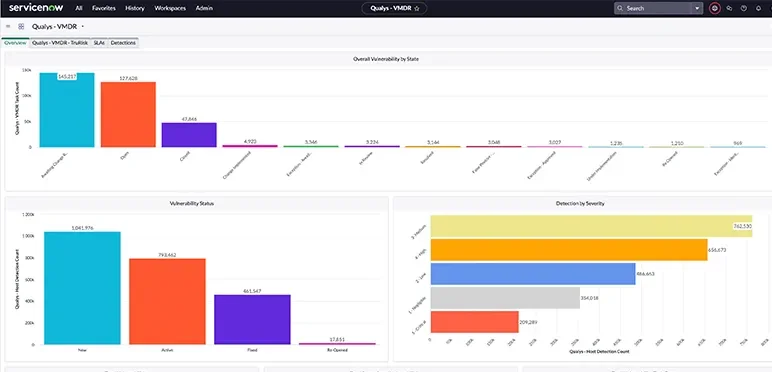
Meet your targeted SLAs for vulnerabilities with auto-assignment.
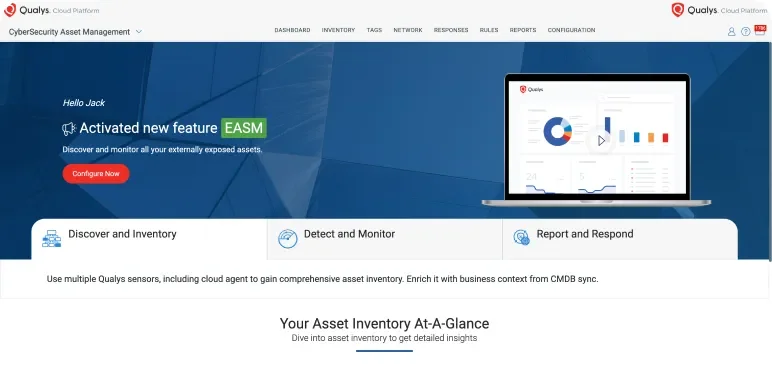
Continuously discover and monitor internet-facing enterprise systems and associated exposure.
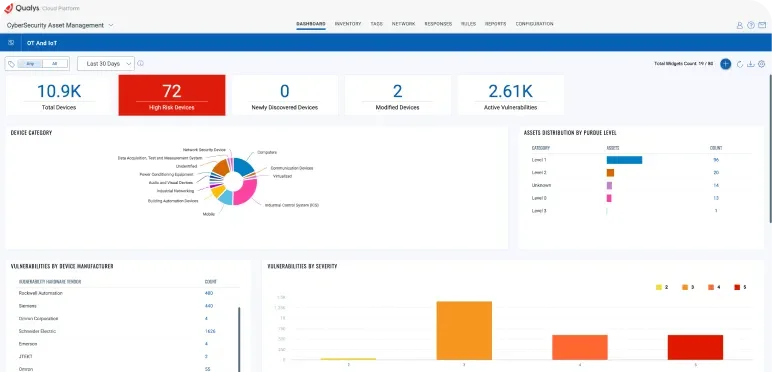
Organizations are increasingly reliant on connected devices, which security teams are often blind to.
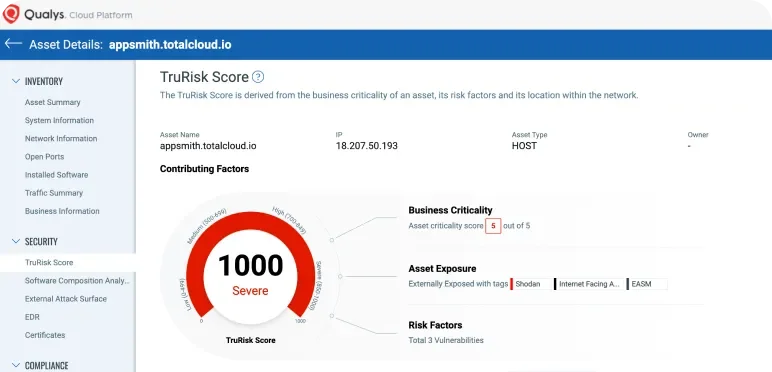
Prioritize risk with business context across your attack surface, beyond just detecting vulnerabilities.
Get continuous, automated scanning to discover and secure web apps & APIs across cloud & on-prem.
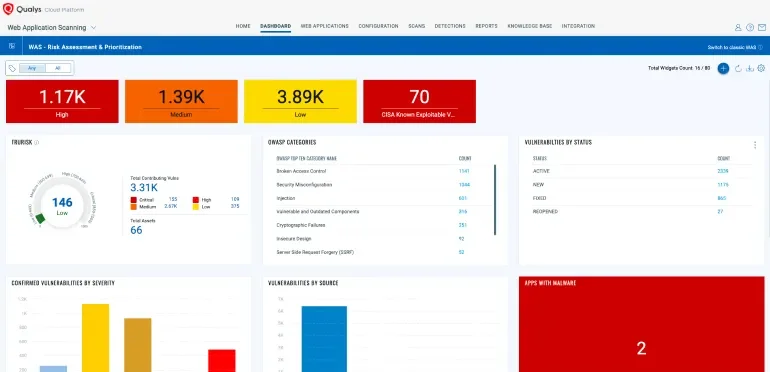
Detect vulnerabilities, misconfigurations, PII exposures & OWASP risks across web apps & APIs.
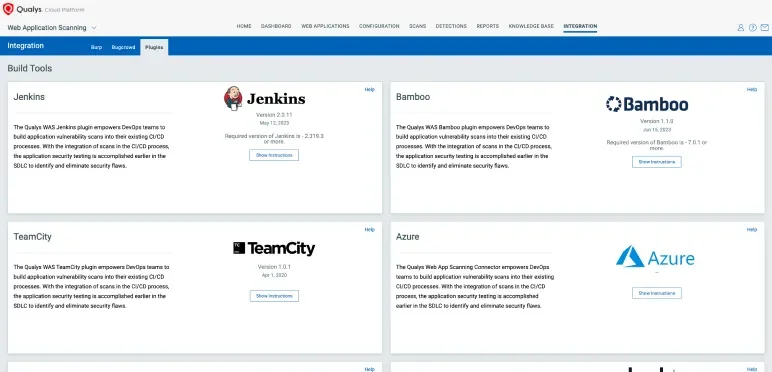
Integrate web app scans in SDLC, using ITSM for quick remediation and fostering DevSecOps collaboration.
Explore ETM Product Tour
Explore TotalAppSec Product Tour
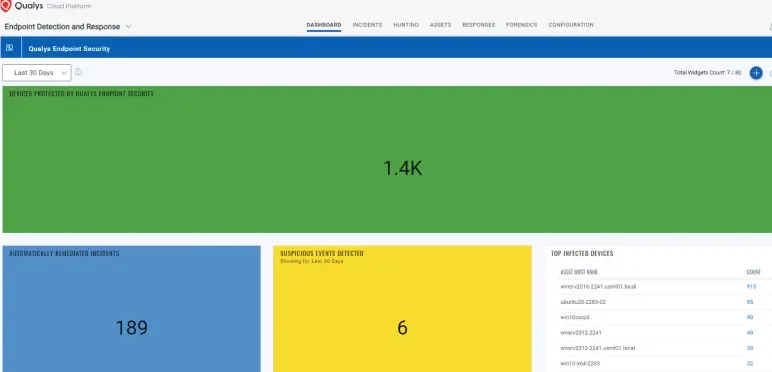
Automatically protect Endpoints from malware such as ransomware, phishing and other forms of attacks.
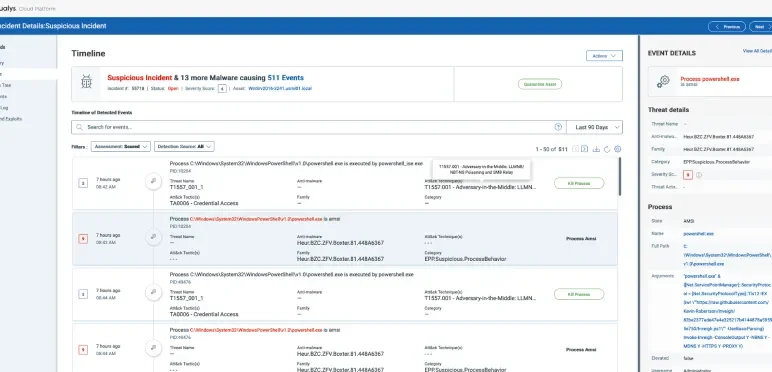
Qualys EDR detects potential threats while also automating investigation and response.
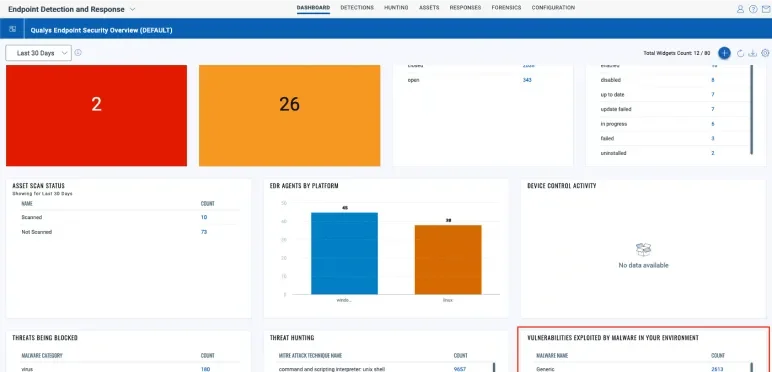
Qualys Detection & Response is the only solution in the industry that unifies multiple context vectors around asset criticality, vulnerabilities, and system misconfigurations associated with detected threats.
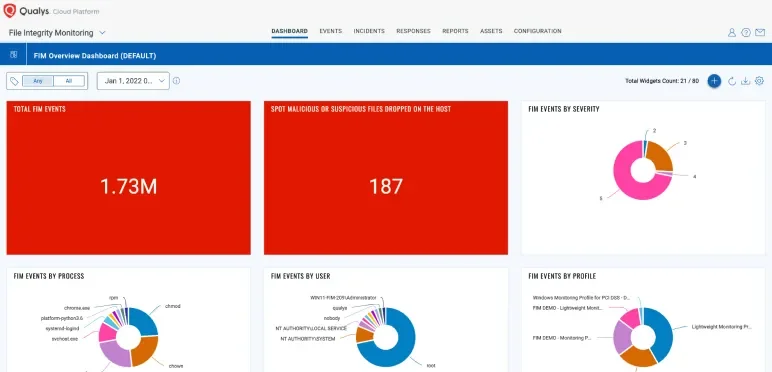
Organizations handling credit cards must comply with PCI DSS 4.0 by implementing FIM.
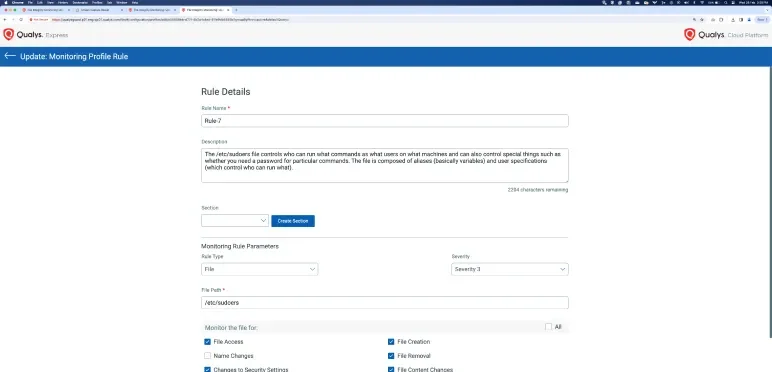
Security practice that involves tracking and logging access to sensitive files.
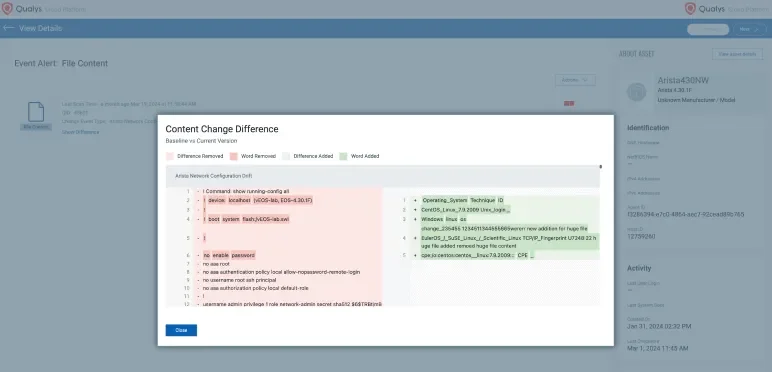
When a network device's configuration changes, logging the modification and timestamp is crucial.
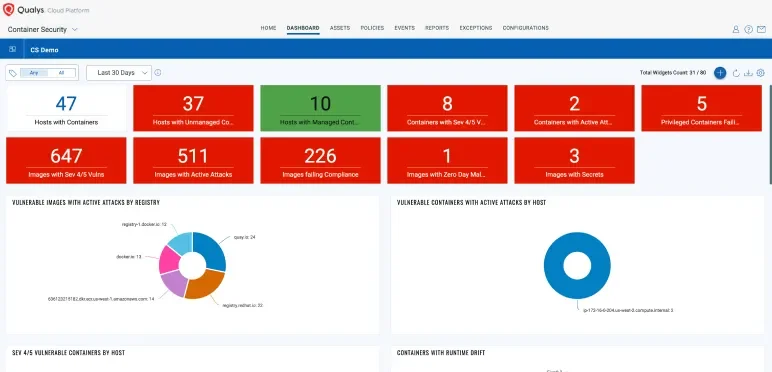
Finding unknown container workloads that are popping up and not in your risk management radar.
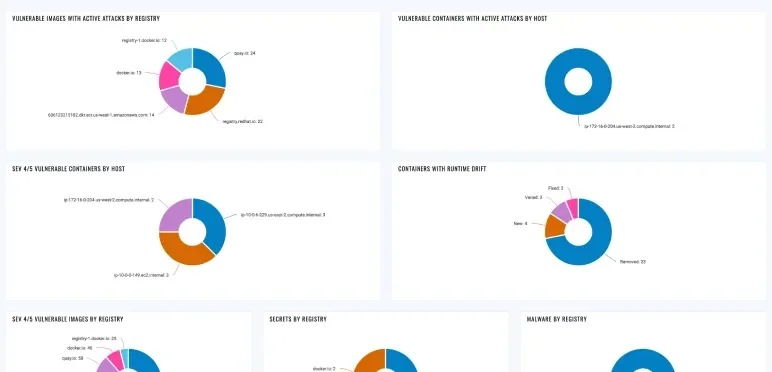
Assessing the risk from your containerized workloads and patching the riskiest ones.
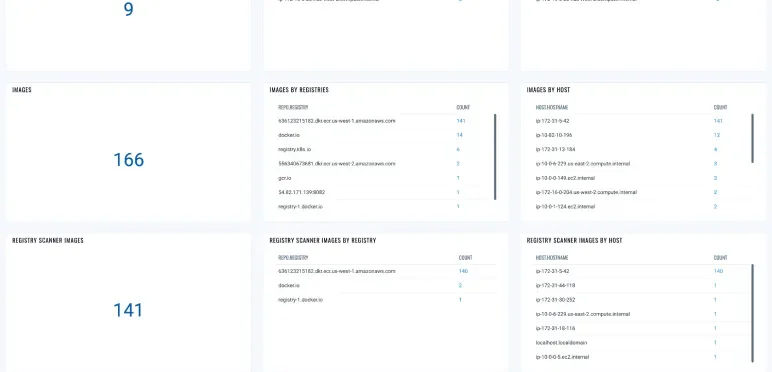
Ensuring container workloads meet industry standard benchmarks for secure configuration (CIS for Docker).
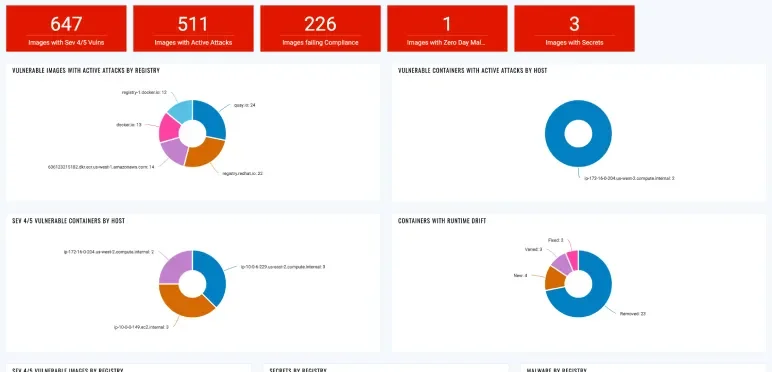
Assessing the risk from images in your container image registry and patching the riskiest ones.
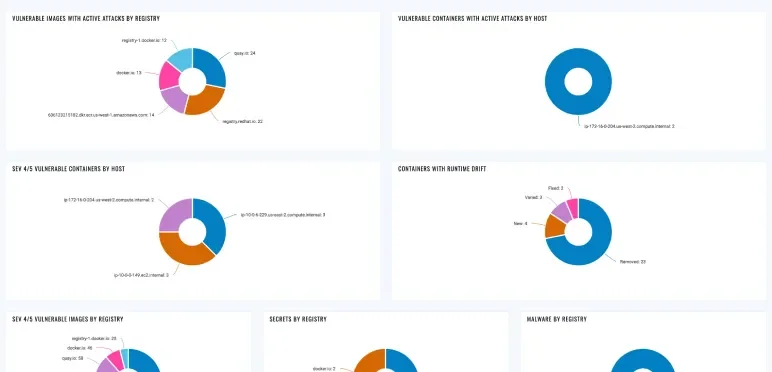
Ensuring container images in registry meet industry standard benchmarks for secure configuration (CIS for Docker).
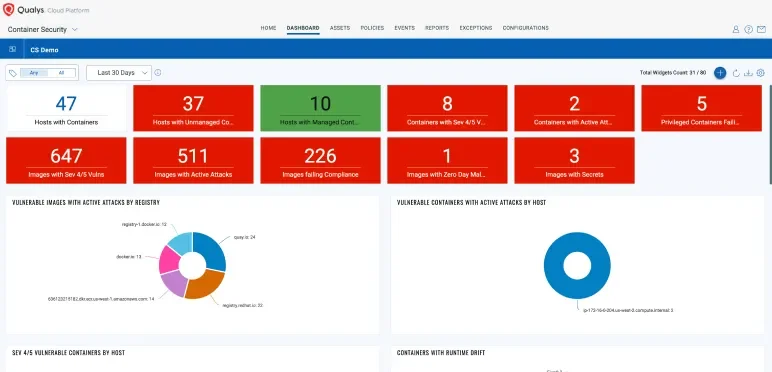
Eliminating (even zero day) malware from images in registry.
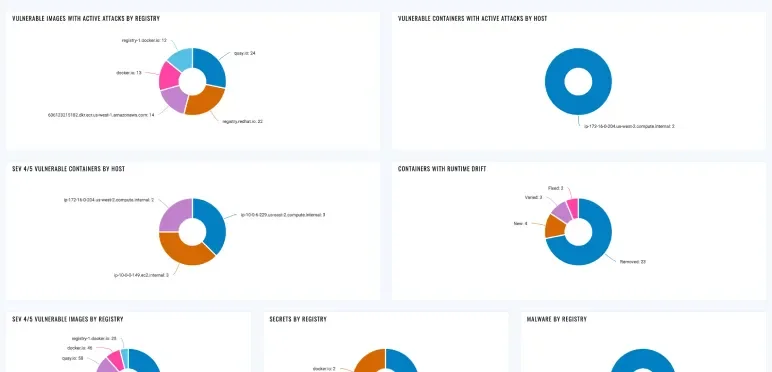
Eliminating secrets from images in registry.
Auto-discover webservers, middleware and classify mission-critical assets for compliance.
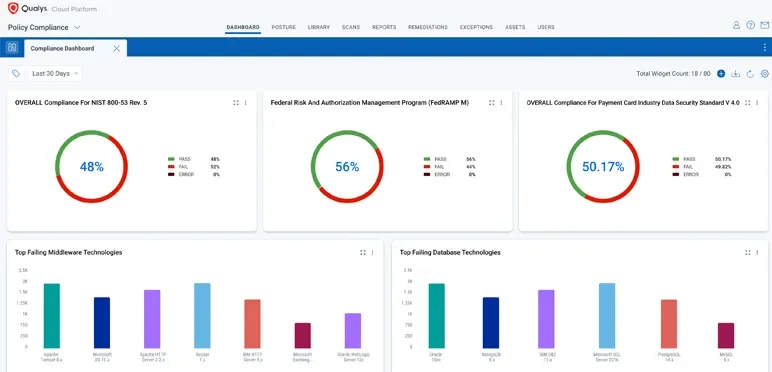
Automatically remediate misconfigurations with out-of-the-box scripts and customization to comply with NIST CSF 2.0 Respond and Recover Functions.
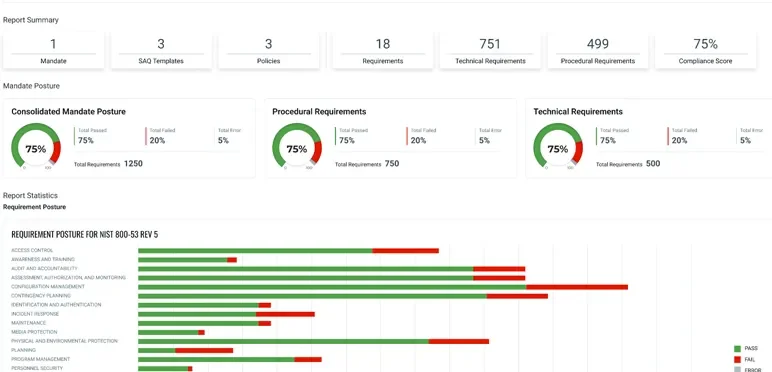
Demonstrate compliance during audits or regulatory inspections
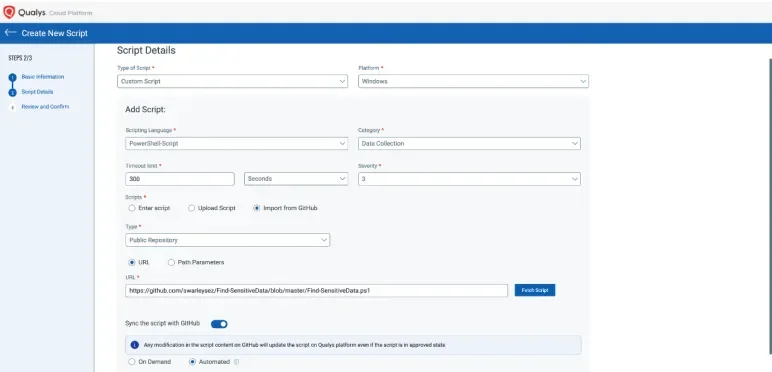
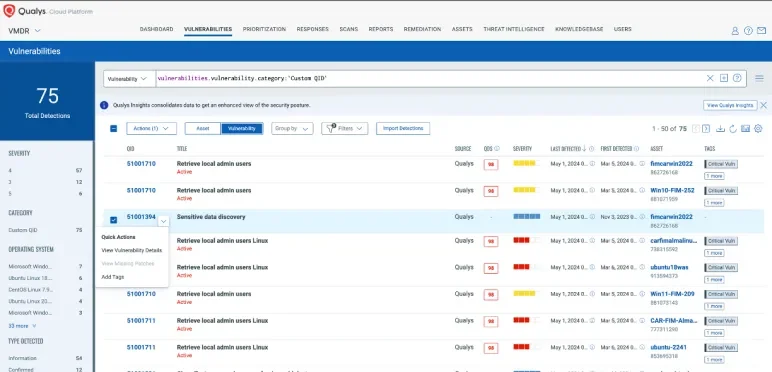
Enhance VMDR with vulnerabilities unique to your environment with Custom QIDs.
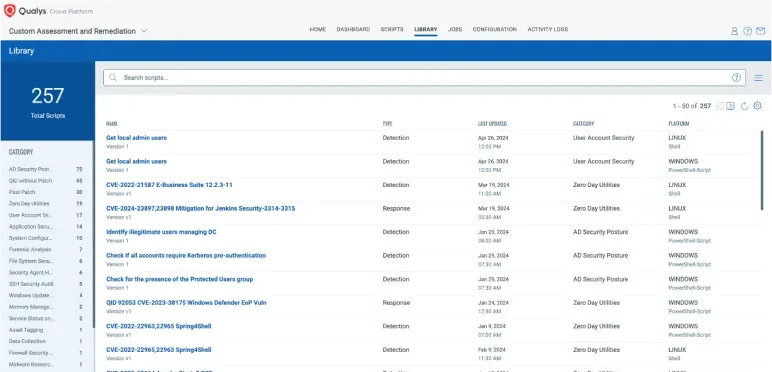
Utilize our script repository to boost security and ensure compliance with industry standards.
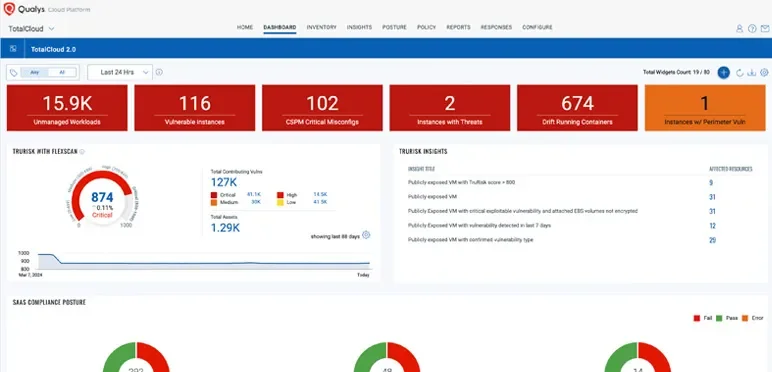
Drive data-driven decisions with actionable insights and customizable security dashboards.
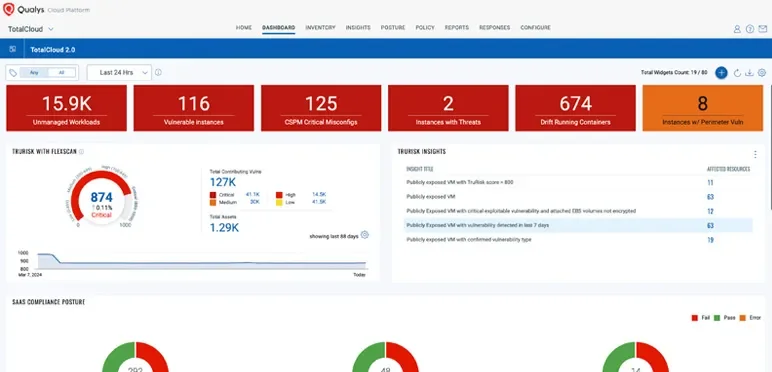
Discover risky assets and factors with actionable insights and customizable dashboards.
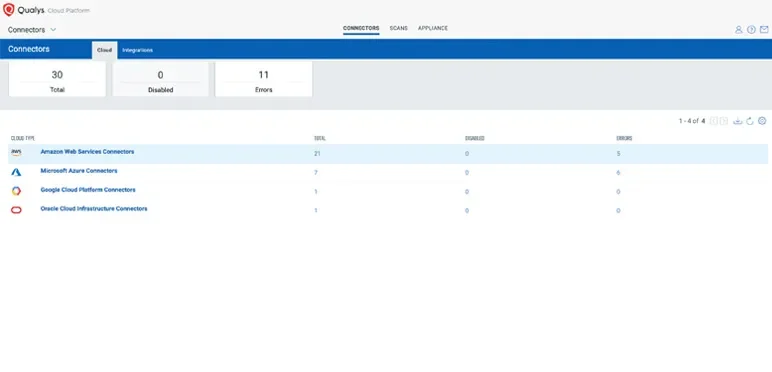
Discover, identify, and remediate cloud risks in a single view.
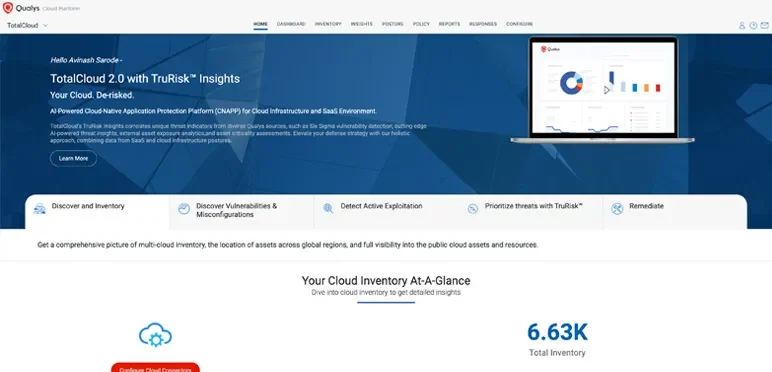
Improve CIS compliance by identifying and auto-remediating failed cloud controls.
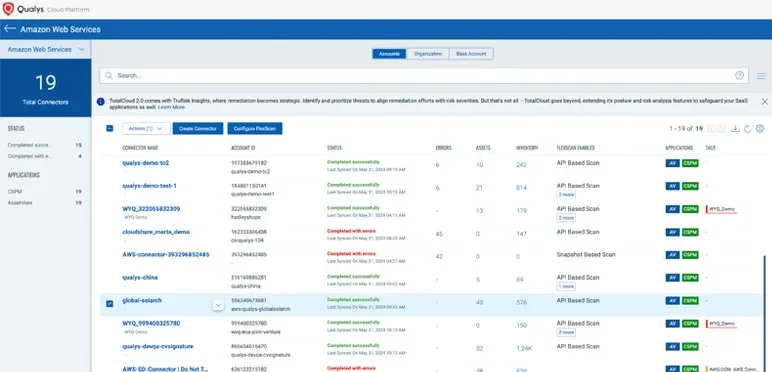
Identifying workloads with vulnerabilities, assessing risk to critical workloads and prioritizing remediation.
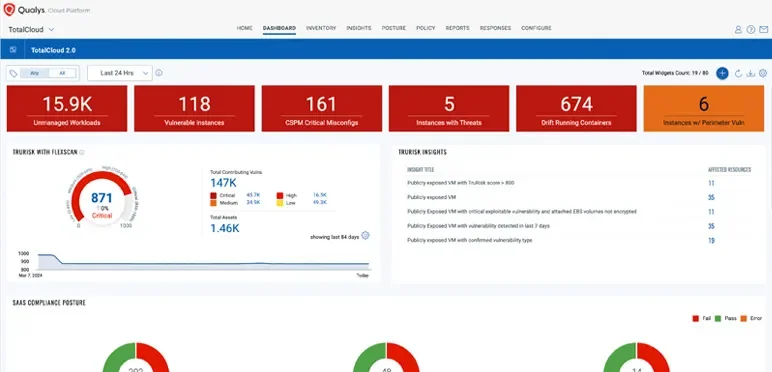
Detect malware, ransomware, crypto-miners, and mutations in real-time using AI/ML.
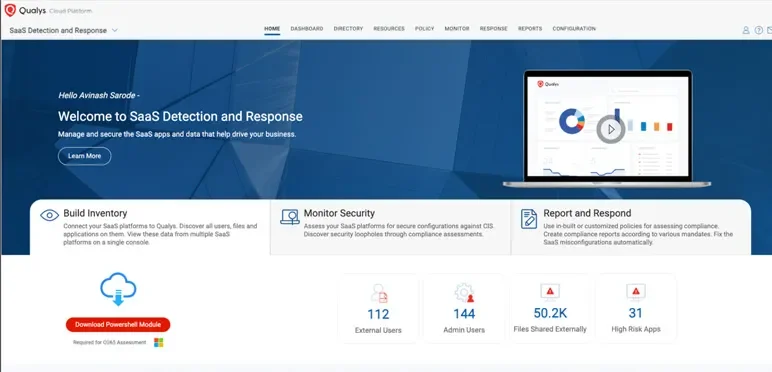
Assessing and improving the compliance of SaaS applications.
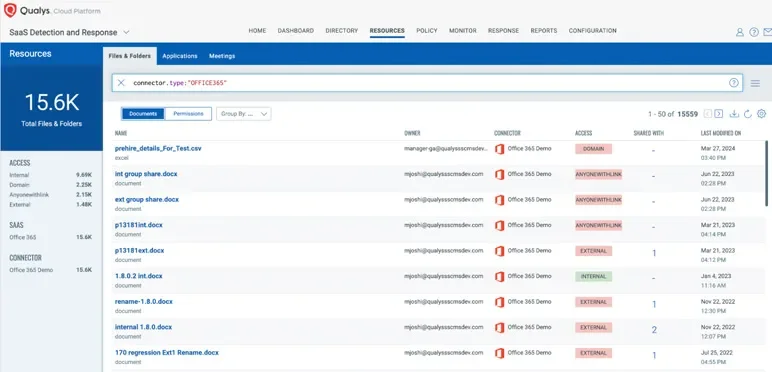
Assessing the risk of data leak by analyzing the external file sharing and excessive API permissions.
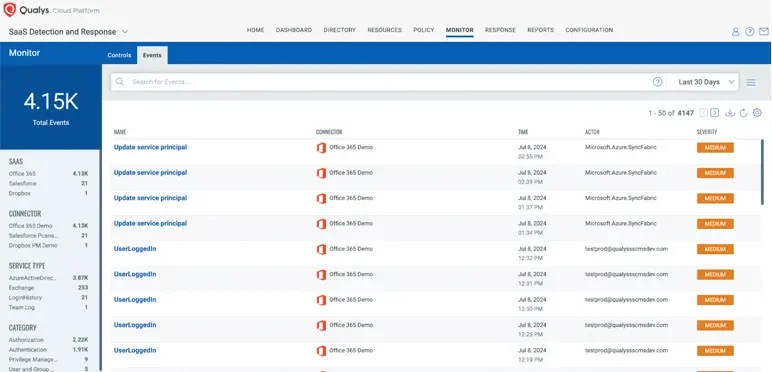
Assessing the risk of breaches by analyzing the event logs.
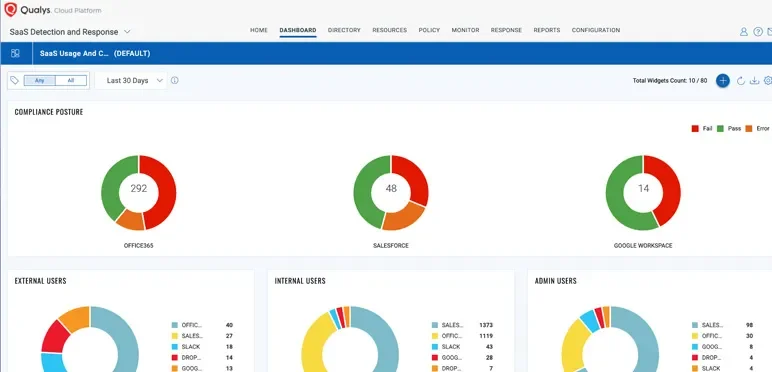
Create and Analyze the informative dashboards.
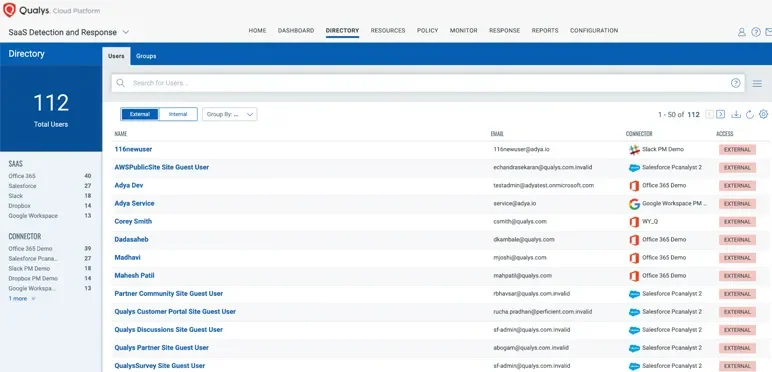
Manage users and groups of all the SaaS applications from single platform.
No software to download or install. Seamlessly deploy Cloud Agents and add users to measure, communicate, and eliminate cyber risk across the extended enterprise.