
70%
of firms have 5+ standards and frameworks
$4M
average lost revenue from one audit failure
424%
Increase in breaches due to misconfigurations in 2022
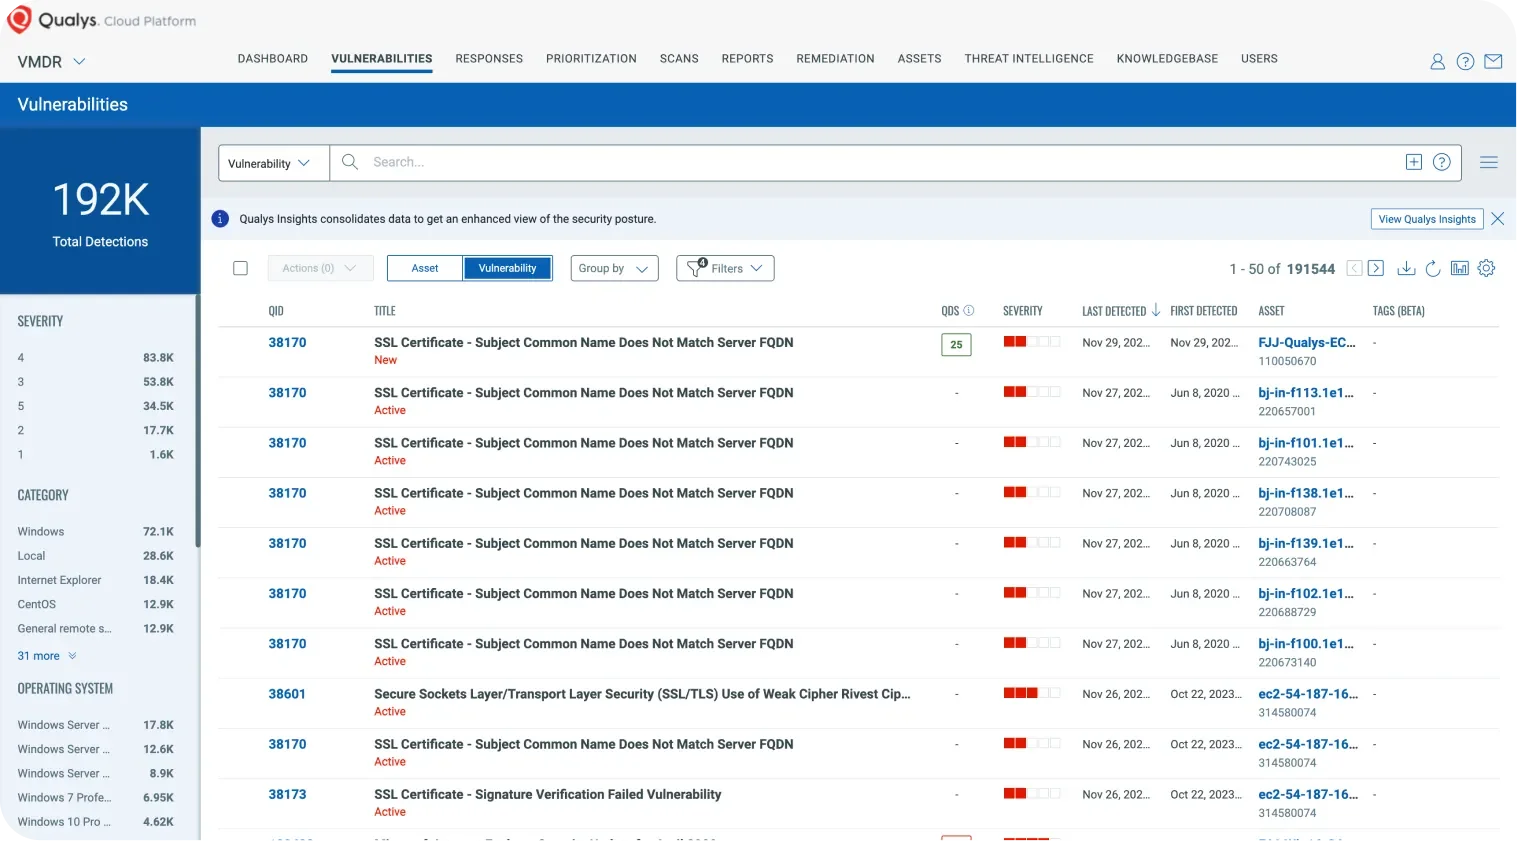
Create compliance dashboards to highlight compliance gaps and provide pre-built templates, profiles, and policies to achieve full compliance.
Measure, communicate, and eliminate cyber risk across the global hybrid IT environment.
Clearly report and articulate risk to internal and external compliance stakeholders across 950 policies, 20,000 controls, and 100 regulations.
Automatically discover and catalog assets, including a 30% improvement in finding previously unknown middleware and databases.
Scan and detect vulnerabilities and identify misconfigurations to build risk profiles, including contributing risk factors and transparent risk scoring.
Leverage TruRisk scoring to prioritize misconfigurations based on ransomware risks, MITRE tactics and techniques, regulatory compliance objectives, and asset business criticality.
Increase security hardening scores to 80% and MITRE ATT&CK coverage to 86% by adding Qualys Compliance Solutions.
Reduce MTTR for misconfigurations by up to 30 days with CMDB and ITSM integrations, out-of-the-box and custom remediation scripts, and CI/CD compliance scans.
Detect and remediate vulnerabilities across your unique environment with customized precision.
Discover all assets with complete business context for all Cardholder Data Environment (CDE) external attack surfaces.
Conduct the quarterly scans required to show compliance with PCI DSS 4.0 with an Approved Scanning Vendor (ASV).
Now we have a dashboard where we’re able to see everything and take action quickly.

Qualys reduces our risk by helping us be constantly present across all our devices.

A simple, consolidated view of security threats across our environment.

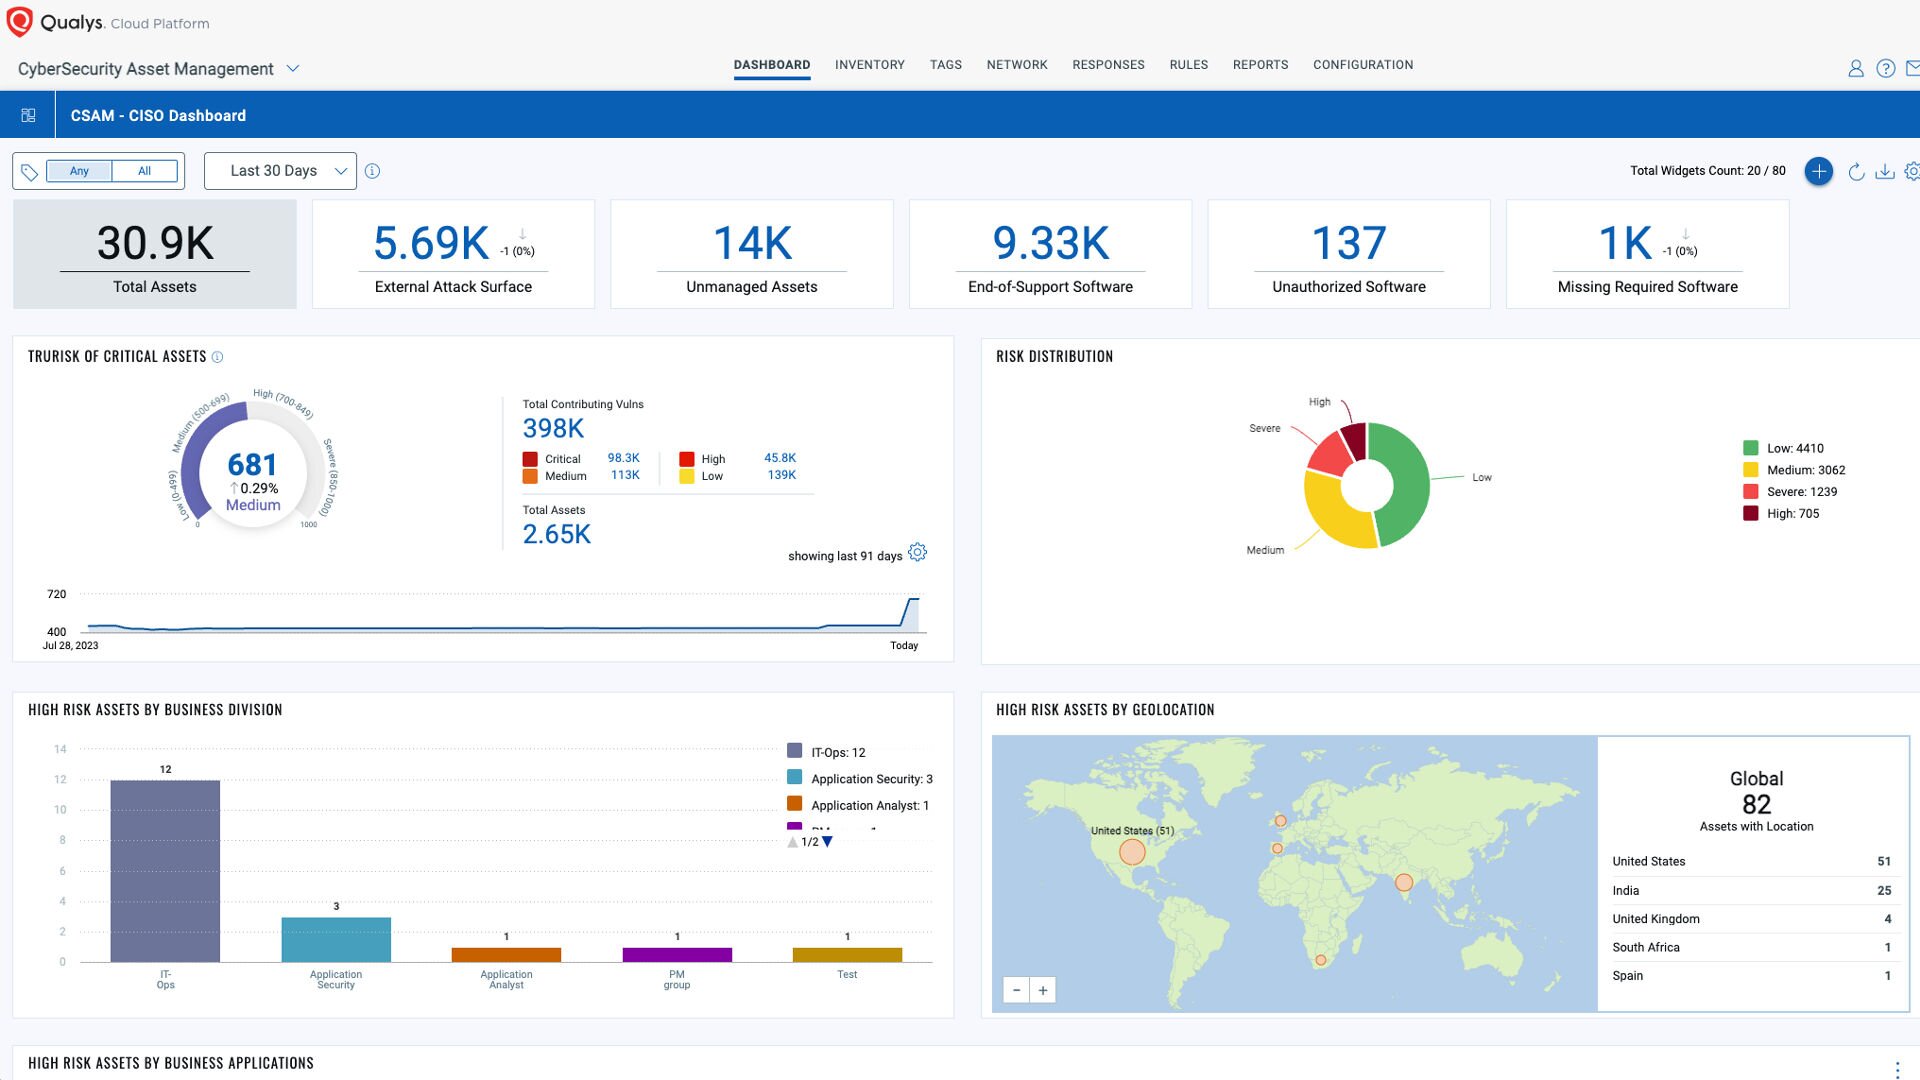
The Enterprise TruRisk Platform provides you with a unified view of your entire cyber risk posture so you can efficiently aggregate and measure all Qualys & non-Qualys risk factors in a unified view, communicate cyber risk with context to your business, and go beyond patching to eliminate the risk that threatens the business in any area of your attack surface.
15 Mins
to Assess your Environment
30% Improvement
in MITRE ATT&CK Coverage
Reduction by 30 days
MTTR Misconfigurations

It is an integrated suite of solutions built on the Enterprise TruRisk™ Platform. It includes Policy Audit (PA), File Integrity Monitoring (FIM), Security Assessment Questionnaire (SAQ), Custom Assessment and Remediation (CAR), CyberSecurity Asset Management (CSAM) and PCI Approved Scanning Vendor (ASV) services. These capabilities simplify compliance across multiple regulations.
Qualys provides audit‑ready compliance for PCI DSS 4.0, GDPR, FedRAMP, NIS2, HIPAA, DORA, FINRA and many other regulations. It also supports frameworks such as CIS, NIST, DISA STIG, ISO, etc.
The platform can automatically discover and classify in‑scope assets and apply compliance policies, FIM profiles, self‑assessment templates and vulnerability scan profiles—allowing you to assess your data environment within 15 minutes.
Qualys visualizes your entire environment across the top 20 control gaps, as reported in the Verizon Payment Security Report. Dashboards show compliance gaps and provide pre‑built templates, profiles and policies.
It provides a library of over 110 mandates mapped to controls and lets you generate custom reports using regulatory‑centric templates. You can clearly report risk to internal and external stakeholders across 1200 policies, 27000 controls and 100 regulations.
Many compliance tools provide point‑in‑time assessments. Qualys offers continuous discovery, policy assessment, TruRisk scoring, extensive control and mandate libraries and unified reporting. Integrations with VMDR and automated remediation streamline compliance management and reduce audit failures.