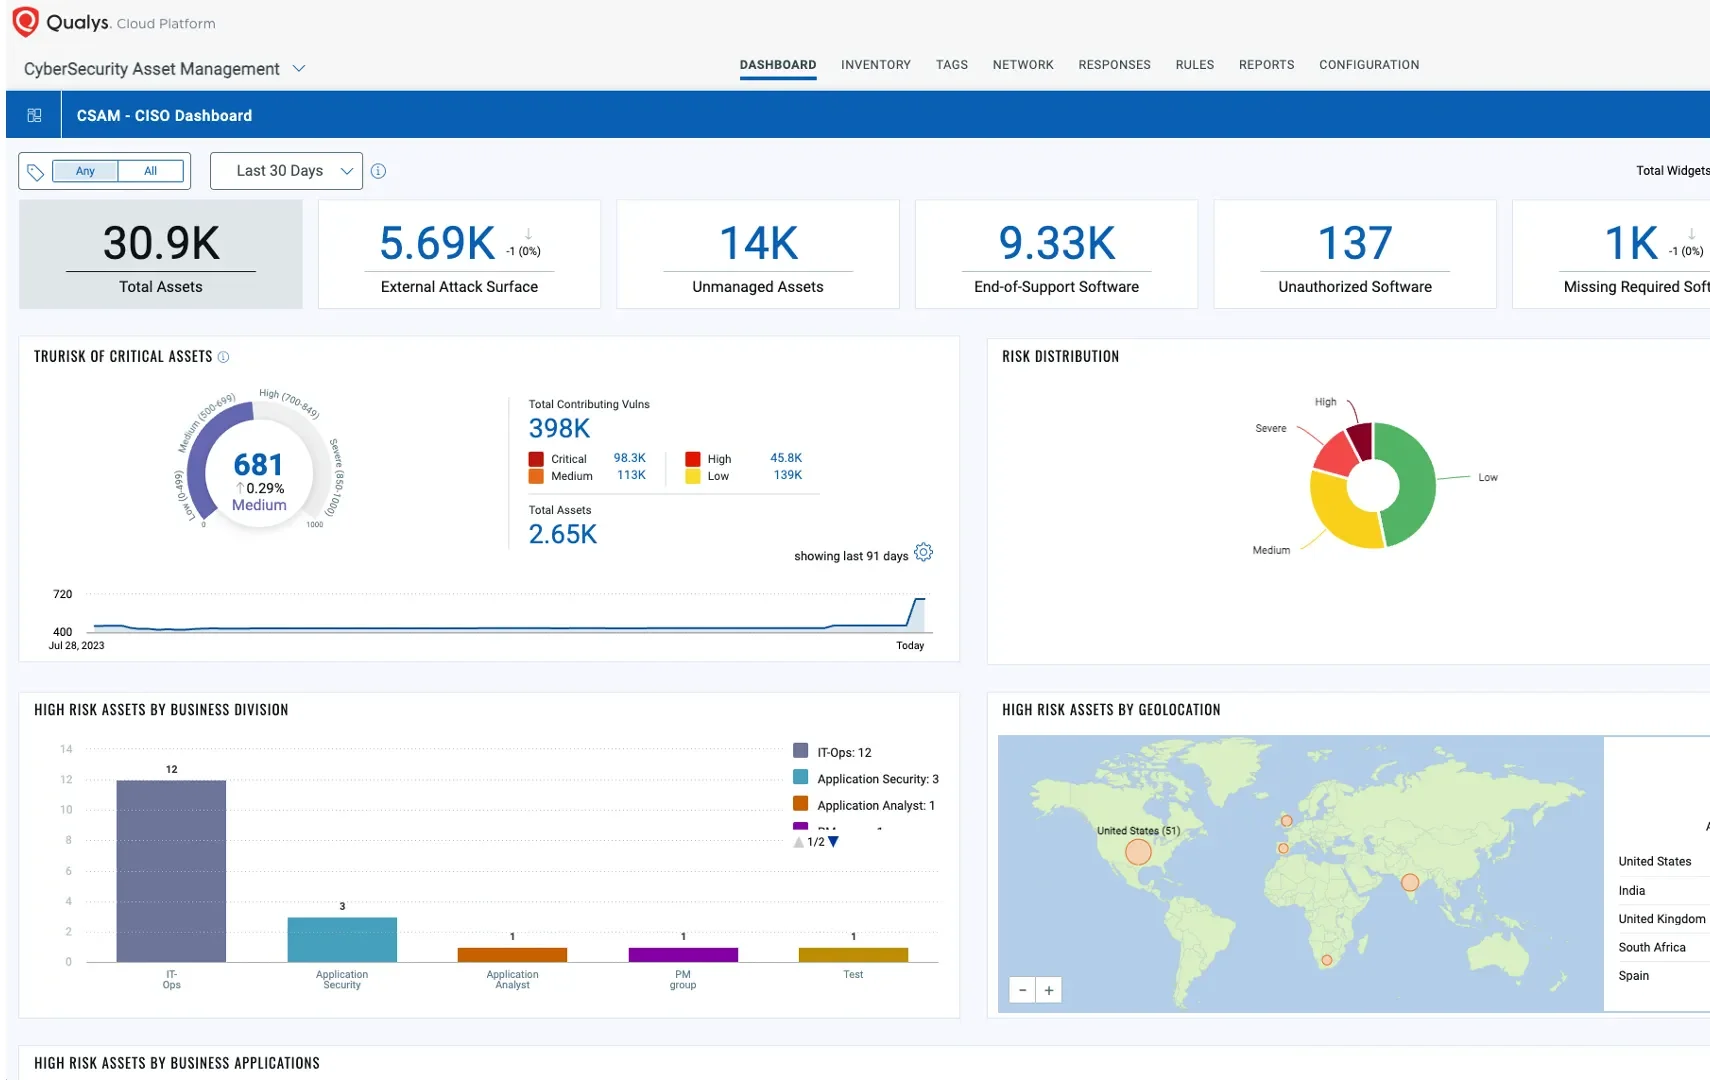
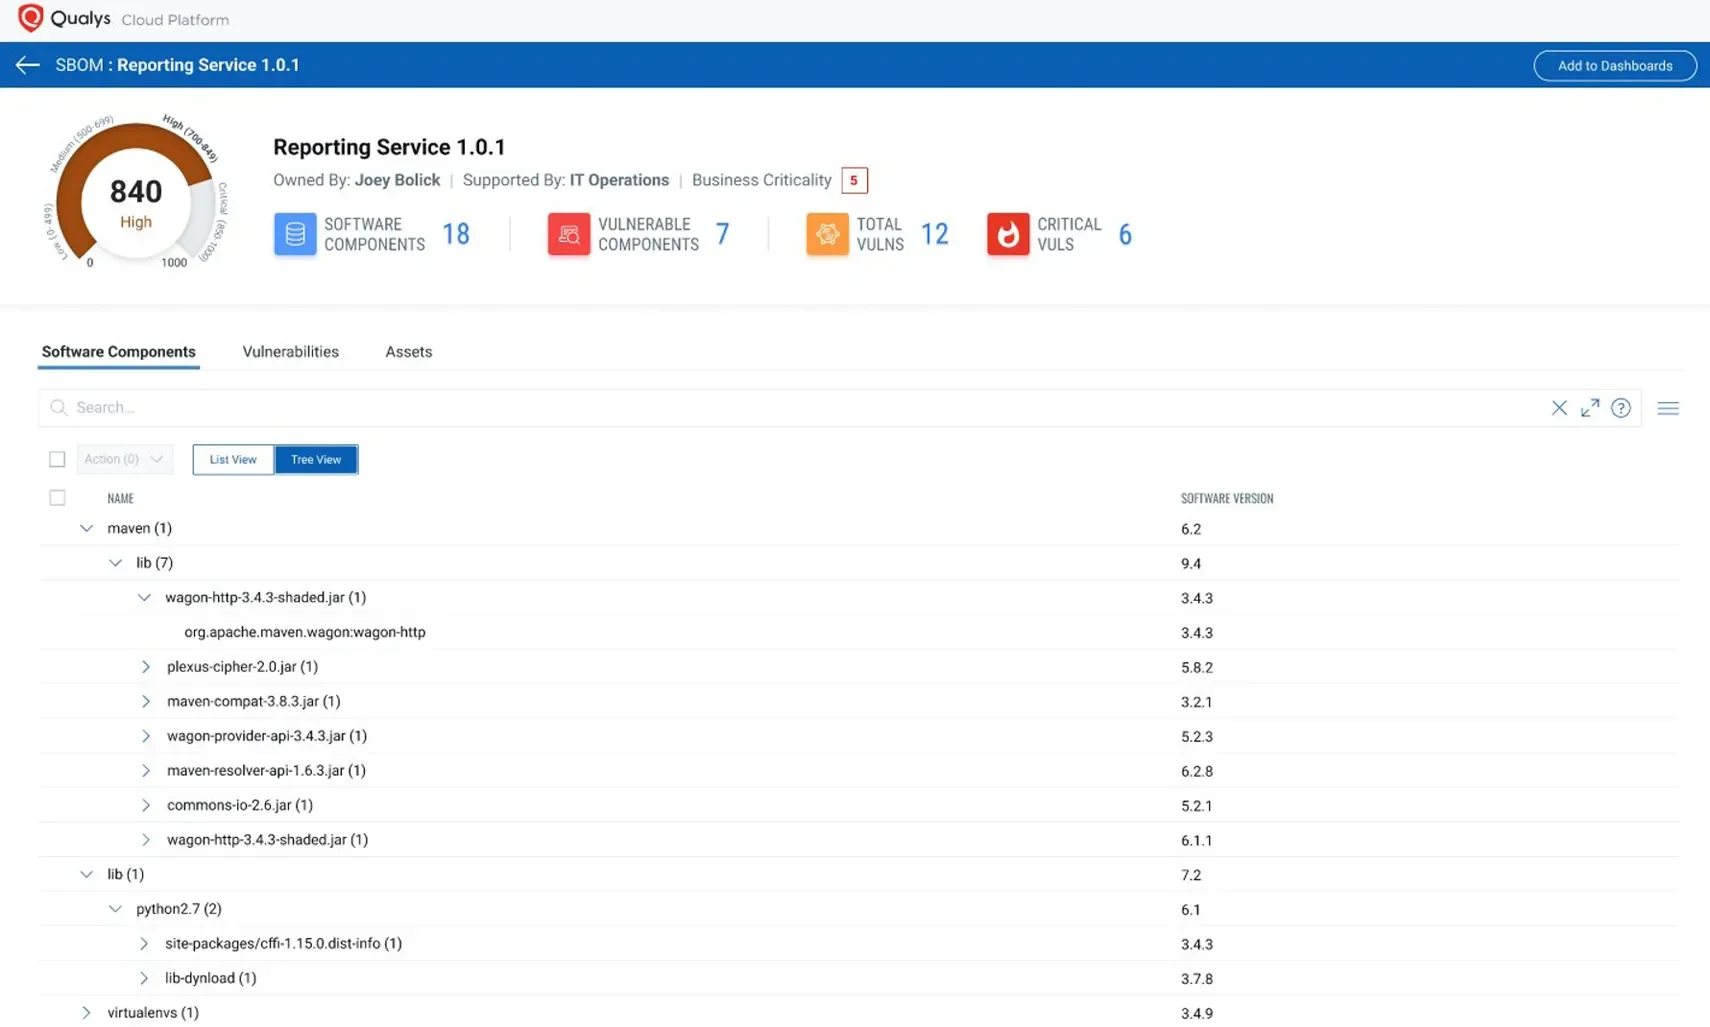
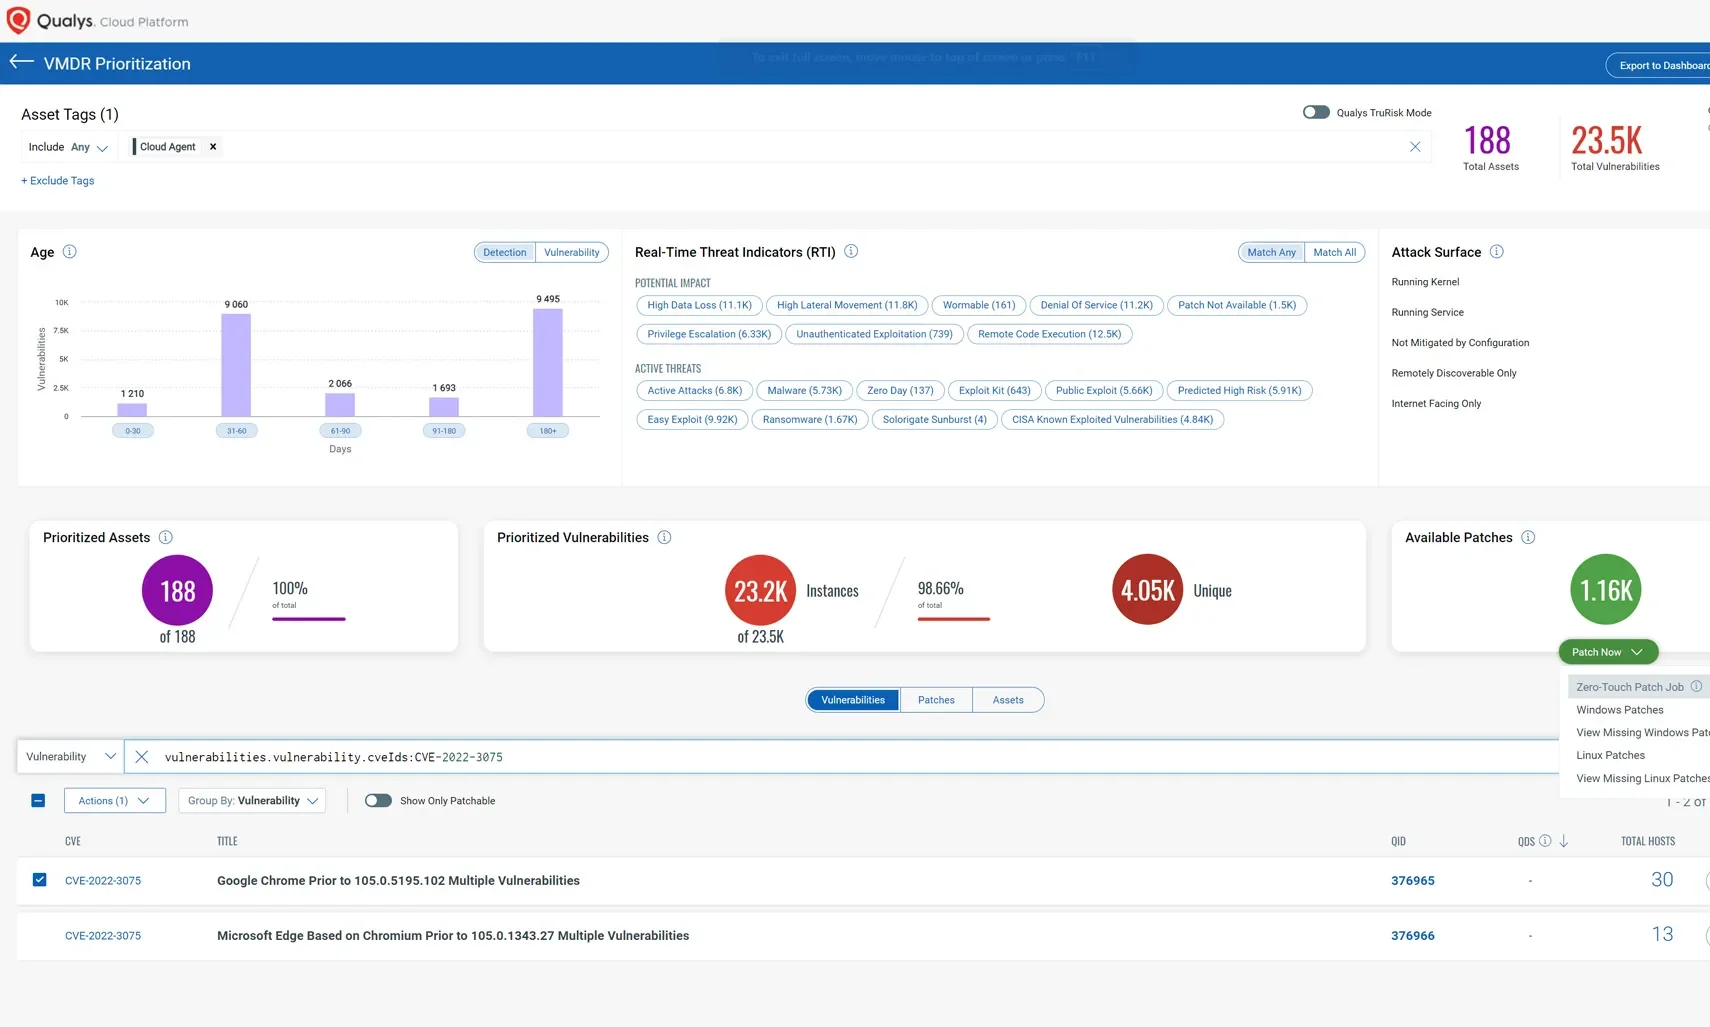
Software supply chain risk management is the ability to identify, prioritize, and mitigate risks from components associated with third-party and first-party (homegrown) software and services. It includes security and compliance practices in the development process and at runtime to mitigate risks related to software components, including zero-day vulnerabilities such as Log4Shell.
Secure your first-party applications
96% of first-party software includes open-source components. Learn how to assess, prioritize, and remediate vulnerabilities associated with components running within your unique environment.
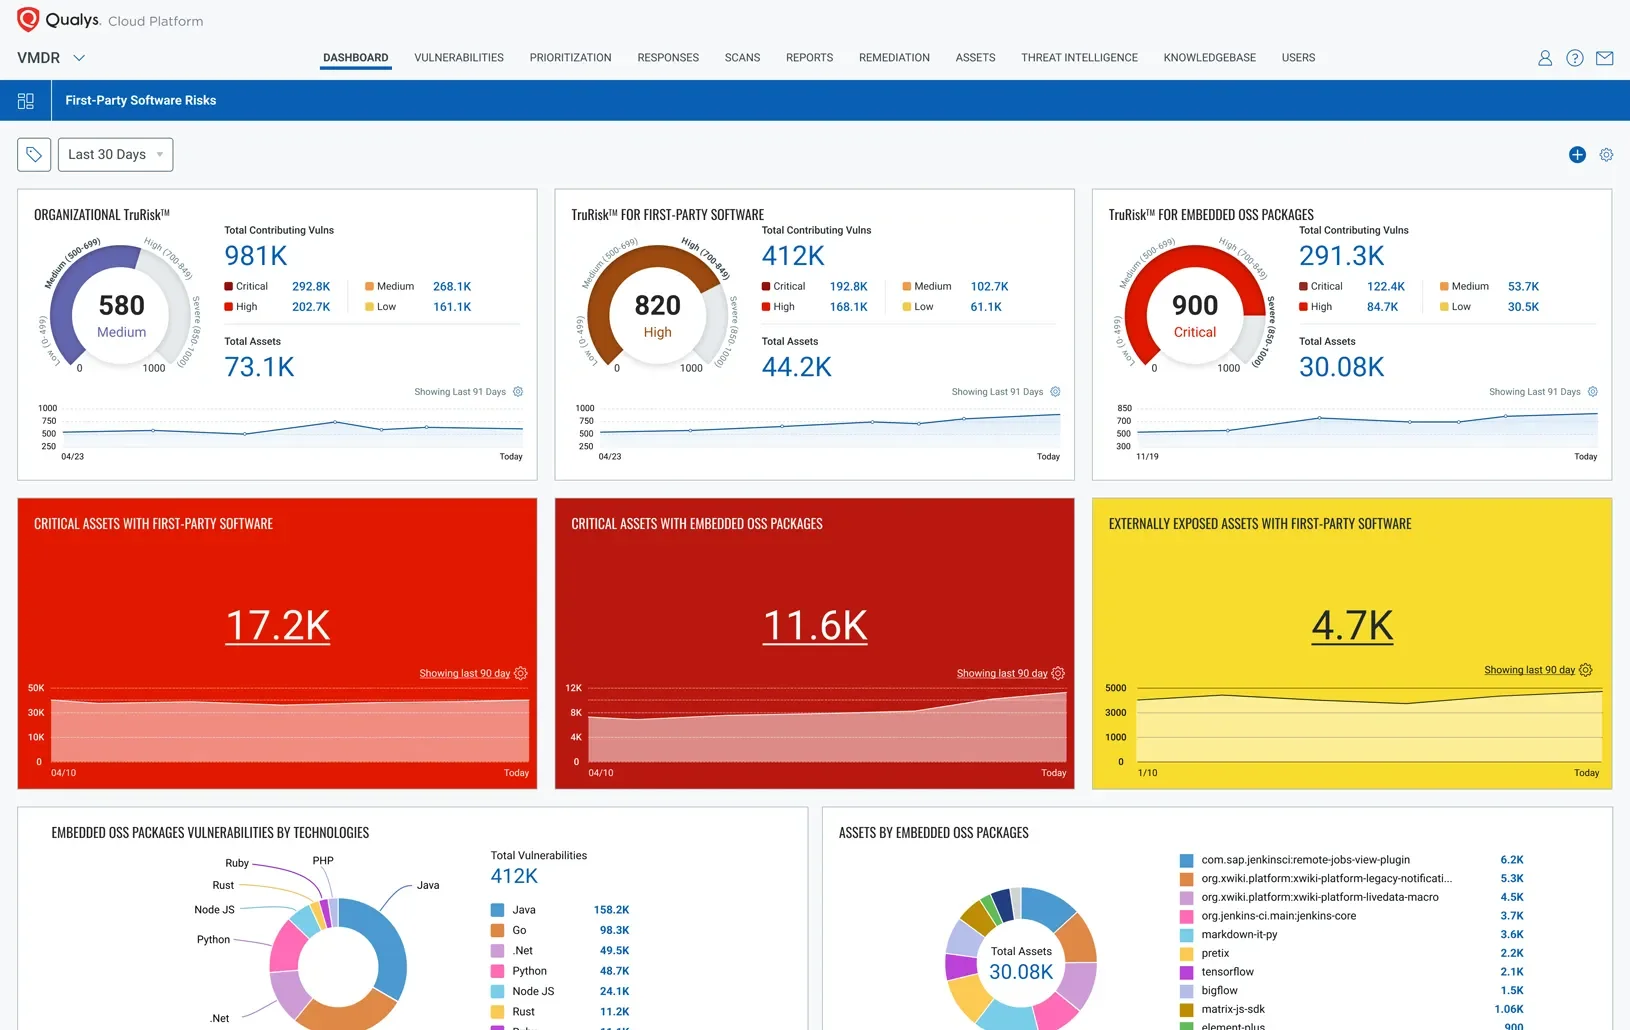
Know the TruRisk of your SBOMs
Turbocharge remediation of software supply chain risks