Your autonomous security workforce, built into ETM

Qualys Agentic AI

Purpose-built Al agents that autonomously validate exploitability, monitor adversaries, eliminate vulnerabilities, and track compliance — around the clock, inside ETM.

Meet the Three Musketeers of Autonomous Defense

Frontier AI has shrunk the time to exploit from weeks to hours. Watch how three Qualys AI Agents detect, validate, and remediate vulnerabilities autonomously, turning AI-speed threats into AI-speed defense.

No-Cost, 30-Day Trial

Powered by Agentic AI, these agents work across vulnerability, identity, cloud, and patch operations to close the loop from signal to mitigation to verified risk reduction.

Scanless Vulnerability Detection

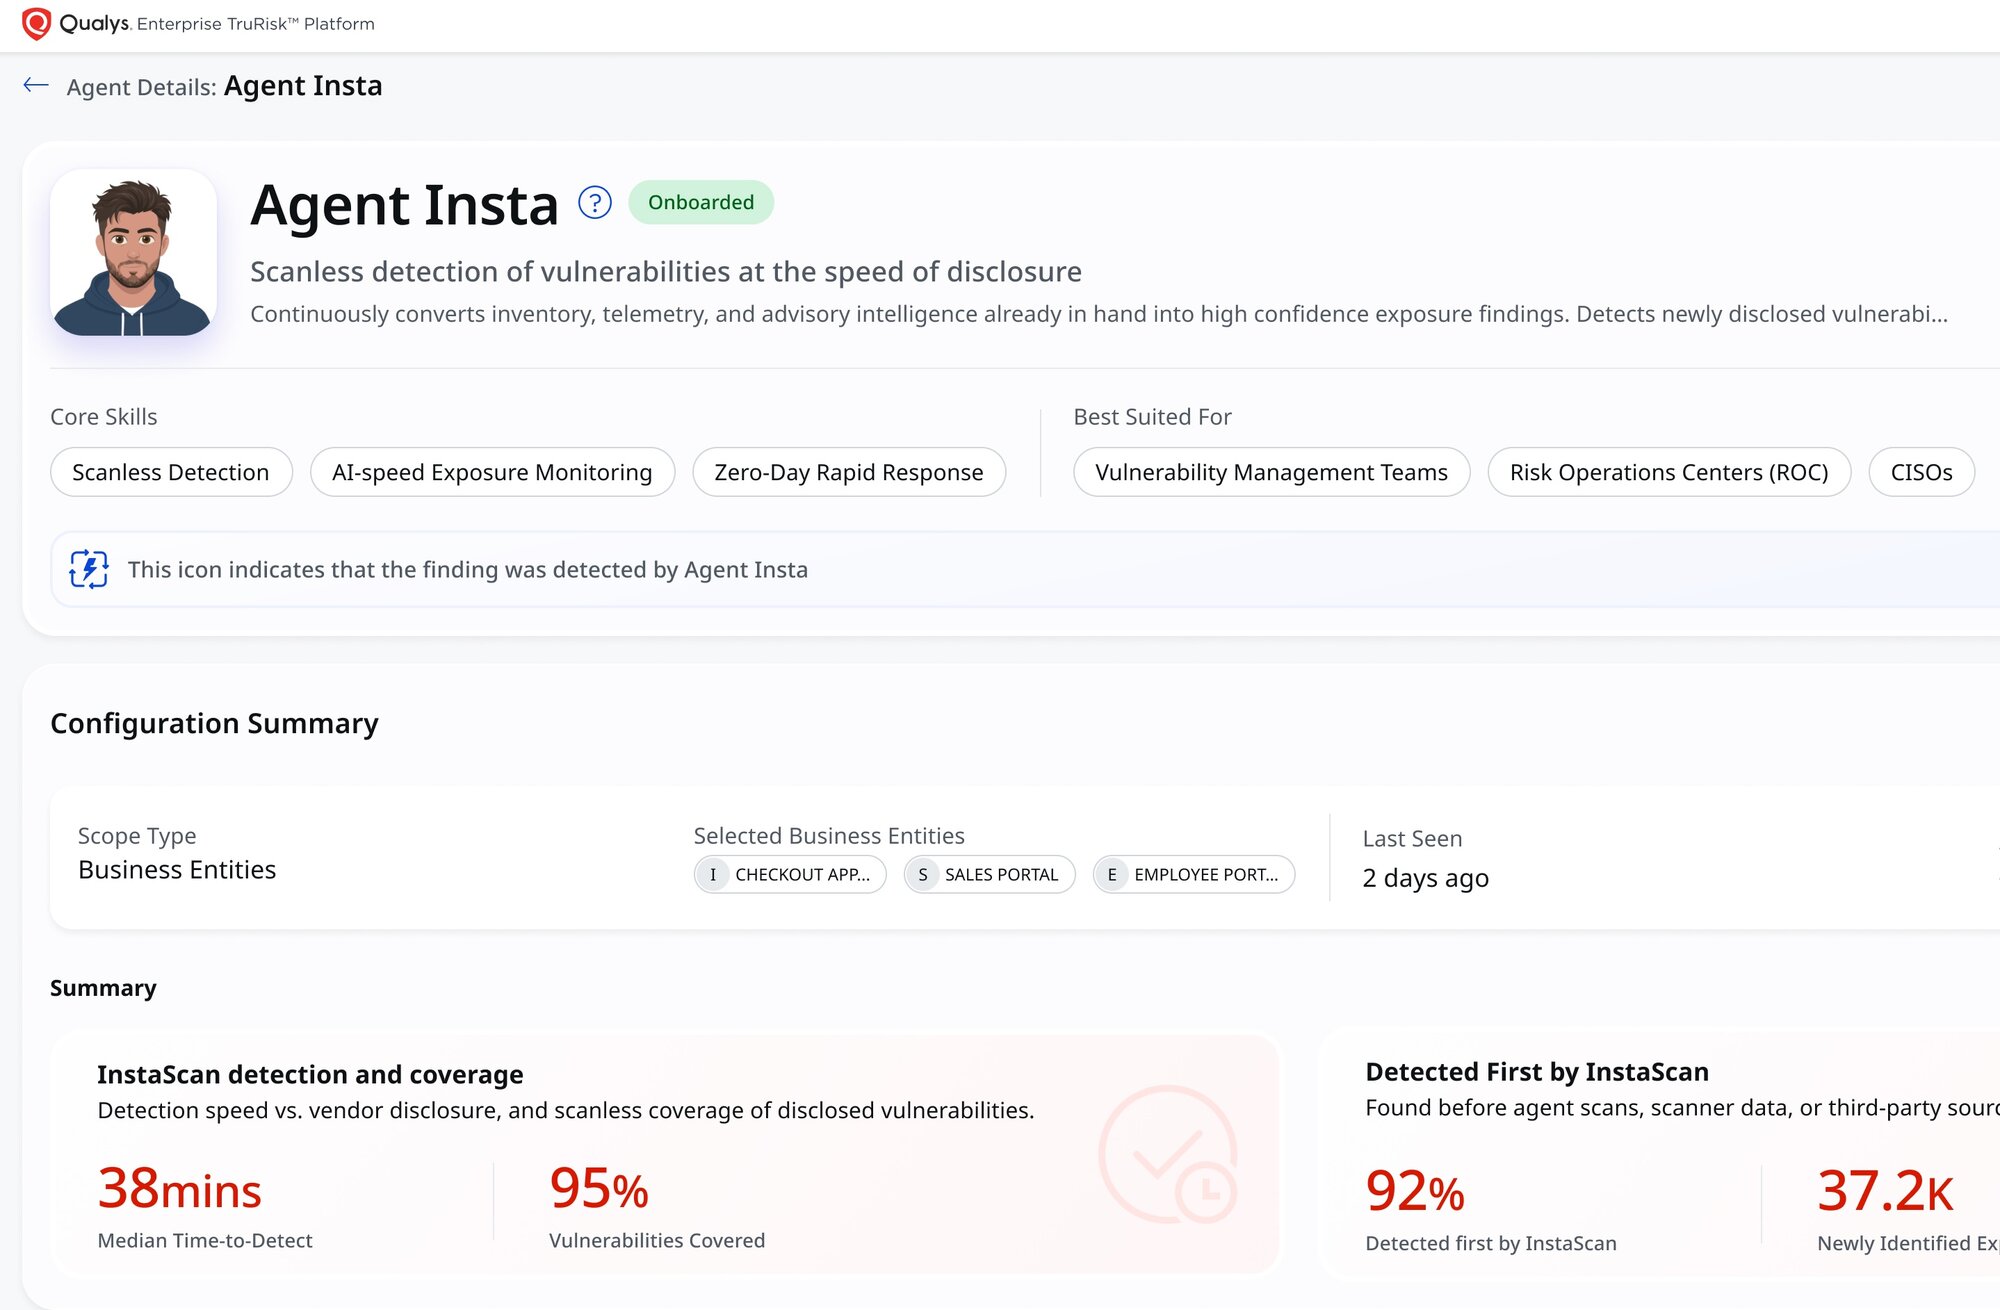
Agent Insta

Continuously operationalize scanless detection at scale. Agent Insta decides what to correlate next based on new advisories, live inventory, and threat context, then turns existing telemetry into high-confidence findings so security teams see real exposure within minutes of disclosure.

Key Capabilities

  • Threat-Aligned Cadence: Surface new exposures as intelligence lands, ahead of agents, scanners, and third-party feeds.
  • Reclaim Time-to-Remediate: Replace detection delays with Al-normalized, confidence-scored signals that accelerate prioritization and remediation.
  • Prove Frontier Al Readiness: Match adversary speed with agentic, scanless detection that moves at machine speed for autonomous defense.

Autonomous Validation Orchestration

Agent Val

Continuously operationalize exploit validation at scale. Agent Val decides what to validate next based on attacker relevance, business context, and exposure risk, then drives safe confirmation and next-best actions so Security and IT Ops focus only on what truly matters.

Key Capabilities

  • Exploit Validation: Uses TruConfirm to safely test if an exposure is reachable and weaponizable by an attacker in your environment.
  • Closed-Loop Mitigation: Prioritizes confirmed risks to the top of the queue and triggers specific mitigations beyond just patching.
  • Continuous Re-Validation: Automatically re-checks for exploit validation after mitigation to ensure the risk has been reduced, providing an audit trail.

Autonomous Validation Orchestration

Agent Val

Continuously operationalize exploit validation at scale. Agent Val decides what to validate next based on attacker relevance, business context, and exposure risk, then drives safe confirmation and next-best actions so Security and IT Ops focus only on what truly matters.

Key Capabilities

  • Exploit Validation: Uses TruConfirm to safely test if an exposure is reachable and weaponizable by an attacker in your environment.
  • Closed-Loop Mitigation: Prioritizes confirmed risks to the top of the queue and triggers specific mitigations beyond just patching.
  • Continuous Re-Validation: Automatically re-checks for exploit validation after mitigation to ensure the risk has been reduced, providing an audit trail.

Autonomous Remediation at Scale 

Agent Sara

Automously executes confidence-gated waves based on AI patch reliability scoring —high-confidence patches deploy hands-free, risky ones get staged rollout. When patches don't exist or can't deploy, she executes patchless strategies: mitigate, uninstall, run custom script, fix, isolate. Monitors every deployment, rolls back on issues, and proves exploits are actually closed.

Key Capabilities

  • Confidence-gated waves: AI patch reliability scoring determines deployment approach—zero-touch on high-confidence patches, ring-staged on medium, manual CAB on low—mapped to BOD 26-04 tiers.  
  • Patchless remediation: When patches are unavailable or operationally risky, executes mitigate, uninstall, run custom script, fix, and isolate across every vulnerability class. 
  • Automatic rollback: If deployment causes issues, remediation rolls back automatically to keep production running. 
  • Verification of closure: Confirms the vulnerability is actually fixed, not just that the ticket was closed. 

Threat-Informed Risk Prioritization

Agent Nyra

Cut through exposure noise by correlating real-time adversary behavior with your organization's specific exposure profile. Agent Nyra tracks active threat actor campaigns, maps weaponized CVEs to your impacted assets, and dynamically re-ranks your risk backlog based on what adversaries are exploiting actively.

Key Capabilities

  • Active Threat Mapping: Leverages the global threat intelligence to identify which adversary TTPs are targeting your industry right now.
  • Strategic Defense: Shifts your strategy from reactive patching to predictive denial by isolating weaponized exposures.
  • Precision Triage: Provides a stack-ranked list of assets that match the playbooks of active threat actors.

Threat-Informed Risk Prioritization

Agent Nyra

Cut through exposure noise by correlating real-time adversary behavior with your organization's specific exposure profile. Agent Nyra tracks active threat actor campaigns, maps weaponized CVEs to your impacted assets, and dynamically re-ranks your risk backlog based on what adversaries are exploiting actively.

Key Capabilities

  • Active Threat Mapping: Leverages the global threat intelligence to identify which adversary TTPs are targeting your industry right now.
  • Strategic Defense: Shifts your strategy from reactive patching to predictive denial by isolating weaponized exposures.
  • Precision Triage: Provides a stack-ranked list of assets that match the playbooks of active threat actors.

Operationalize Threat Exposure and Asset Context

Agent Sid

Focus on the "how" and "where" of your exposure. Gain the deep operational context needed to understand the blast radius of a vulnerability and orchestrate the technical response across complex infrastructure.

Key Capabilities

  • Contextual Analysis: Evaluates the business criticality and technical environment of an asset to determine the true impact of an exposure.
  • Workflow Automation: Bridges the gap between security findings and IT operations by generating actionable technical plans.
  • Resource Optimization: Ensures that remediation efforts are directed toward the systems that provide the most significant reduction in organizational risk.

Identity Attack Surface Management

Agent Grant (Coming Soon)

Continuously collects telemetry from across AD, Entra ID, Okta, and other IDaaS/IdPs, correlates users, service accounts, machine identities, entitlements, with asset and vulnerability context to compute Identity TruRisk™, a quantitative score that expresses how identity weaknesses expand or shrink your overall attack surface.

Key Capabilities
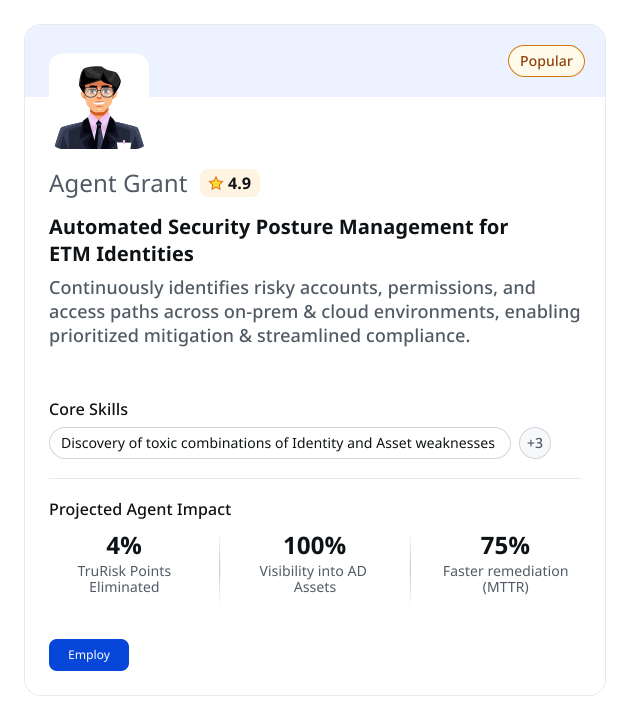
  • Identity TruRisk scoring: Quantifies identity-driven exposure across AD, Entra ID, Okta, and cloud IdPs
  • Attack path mapping: Identifies toxic privilege chains, domain trust abuse, and AD-to-cloud lateral movement paths
  • Automated remediation: Enforces MFA, de-privileges accounts, opens tickets, and quarantines high-risk identities

Your Cyber Risk Assistant

ROCky

ROCky is the conversational AI interface embedded in the Risk Operations Center. Rather than replacing analyst judgment,ROCky amplifies it by enabling security teams to query exposure data, surface prioritized insights, and navigate remediation workflows through plain-language conversation.

Key Capabilities

  • Natural Language Query: Ask ROCky about your most critical exposures or the status of a remediation project.
  • Strategic Reporting: Instantly generate executive-level summaries or board-ready reports on risk reduction.
  • Actionable Guidance: Receive proactive suggestions on where to focus your team's efforts based on the latest data from the agent team.

Your Cyber Risk Assistant

ROCky

ROCky is the conversational AI interface embedded in the Risk Operations Center. Rather than replacing analyst judgment, ROCky amplifies it by enabling security teams to query exposure data, surface prioritized insights, and navigate remediation workflows through plain-language conversation.

Key Capabilities

  • Natural Language Query: Ask ROCky about your most critical exposures or the status of a remediation project.
  • Strategic Reporting: Instantly generate executive-level summaries or board-ready reports on risk reduction.
  • Actionable Guidance: Receive proactive suggestions on where to focus your team's efforts based on the latest data from the agent team.

Your Cyber Risk Assistant

ROCky

ROCky is the conversational AI interface embedded in the Risk Operations Center. Rather than replacing analyst judgment, ROCky amplifies it by enabling security teams to query exposure data, surface prioritized insights, and navigate remediation workflows through plain-language conversation.

Key Capabilities

  • Natural Language Query: Ask ROCky about your most critical exposures or the status of a remediation project.
  • Strategic Reporting: Instantly generate executive-level summaries or board-ready reports on risk reduction.
  • Actionable Guidance: Receive proactive suggestions on where to focus your team's efforts based on the latest data from the agent team.

Powered by the Enterprise TruRisk™ Management

Qualys Enterprise TruRisk Management (ETM) is the unified, AI-augmented Risk Operations Center that ingests and correlates data from all your security tools, quantifies cyber risk in business terms, and automates remediation—so you can focus time and resources only on what truly matters.
Qualys TotalCloud™ Cybersecurity Asset Management Dashboard

Put Your security program on autonomous footing.

Agentic AI is built into Qualys Enterprise TruRisk Management (ETM). No separate deployment, no added complexity.

Request a demo and a 30-day trial

By submitting this form, you consent to Qualys' privacy policy

Email or call us at 1 (800) 745-4355