Fragmented tools can't keep pace with evolving identity threats. Reduce identity exposure with complete visibility, contextual prioritization, and guided remediation.
As enterprises become agentic, every AI agent that can act on its own expands the attack surface. Qualys ETM Identity discovers every identity that can act, whether human, service, machine, or AI agent. It maps where each identity can go, prioritizes its risk by business impact, and orchestrates safe remediation with Agent Grant. The result is measurable risk reduction and continuous audit readiness.
With 74% of breaches involving credential misuse, identity is the most exploited, least quantified attack surface. Qualys ETM Identity brings identity risk into the same platform you use for vulnerability, compliance, and asset risk. It answers what's exploitable, whether remediation actually closes the risk, and whether you can prove it. ETM Identity turns fragmented identity signals into one measured, audit-ready risk posture.

As enterprises become agentic, every AI agent that can act on its own expands the attack surface. Qualys ETM Identity discovers every identity that can act, whether human, service, machine, or AI agent. It maps where each identity can go, prioritizes its risk by business impact, and orchestrates safe remediation with Agent Grant. The result is measurable risk reduction and continuous audit readiness.

ETM Identity is Now FedRAMP High Certified
Native discovery across AD, Entra ID, Okta, local identities, and other identity providers to uncover exposures across hybrid environments.
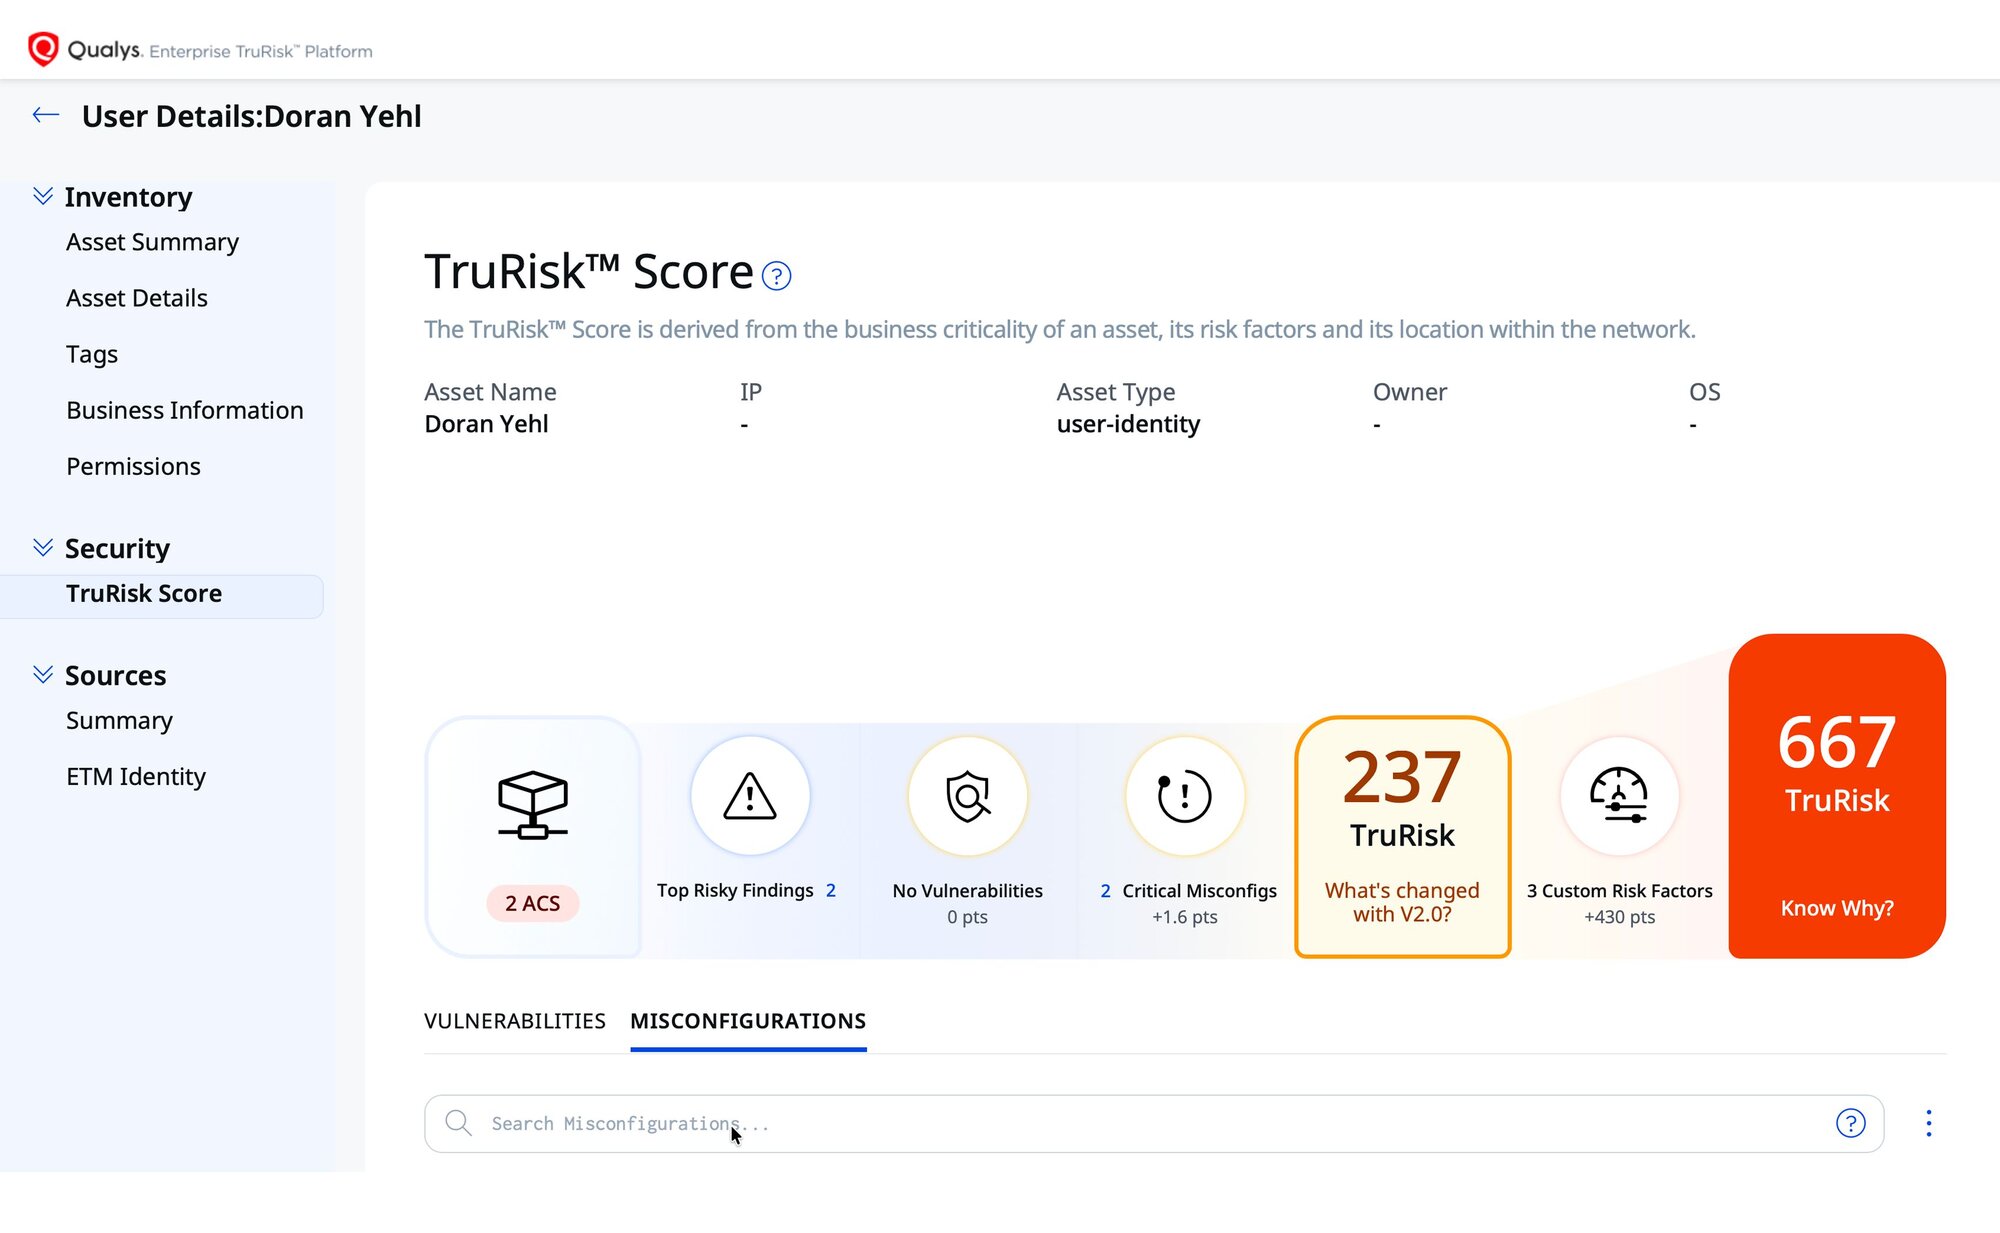
TruRisk™ Score correlating identities, assets & privileges into business risk metrics.
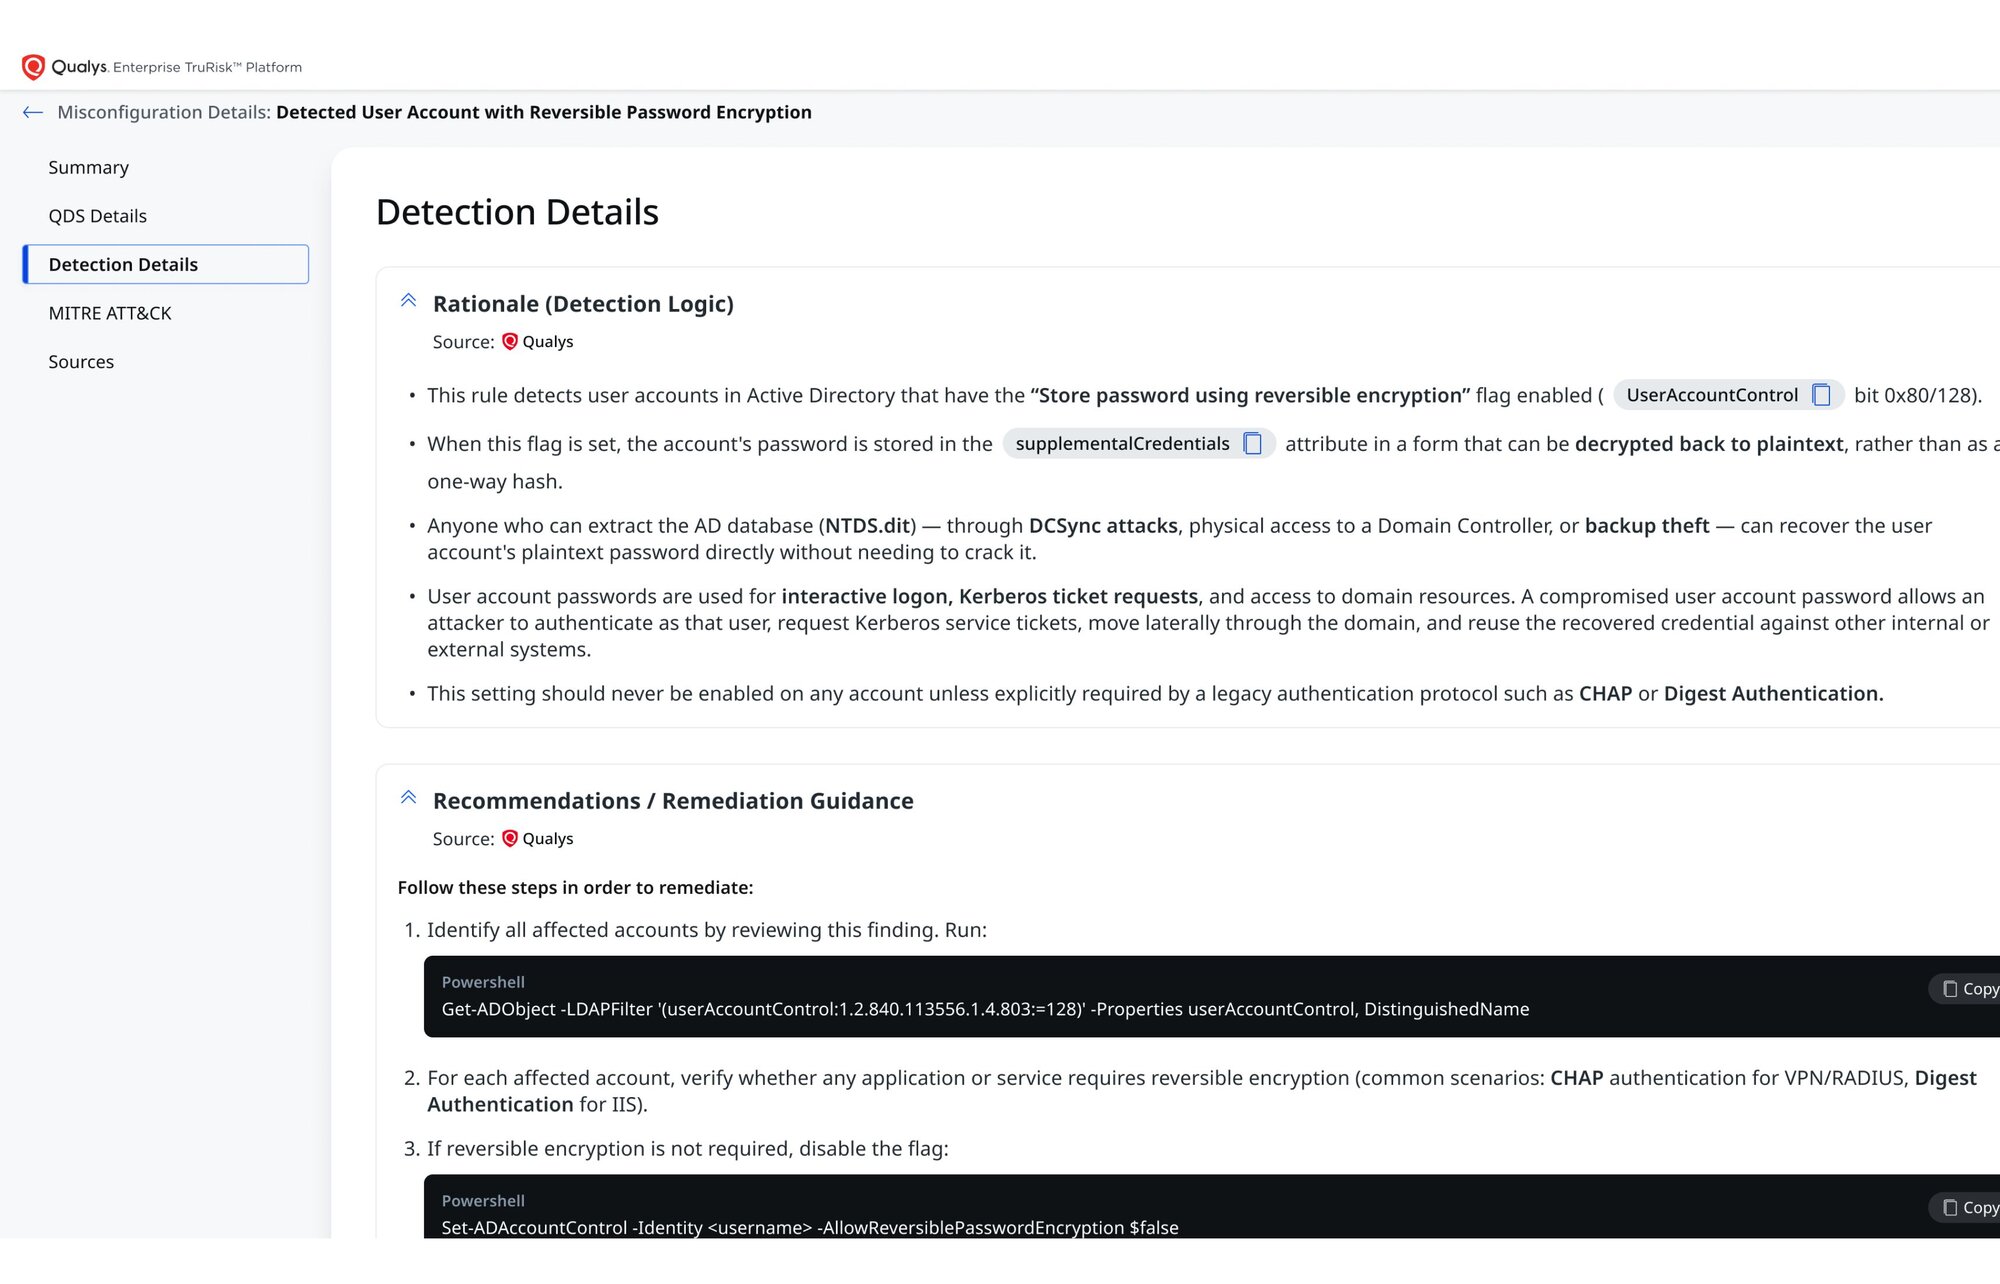
Out-of-the-box policy controls and scripts for Active Directory (AD), with closed-loop validation on every fix.
Identity risk doesn't wait for your next audit review. Qualys ETM Identity continuously unifies identity exposure, correlating it with asset risk into a single TruRisk™ score inside the Enterprise TruRisk™ Management platform — so security teams prioritize the exposures that matter most across your multi-cloud and hybrid environment.
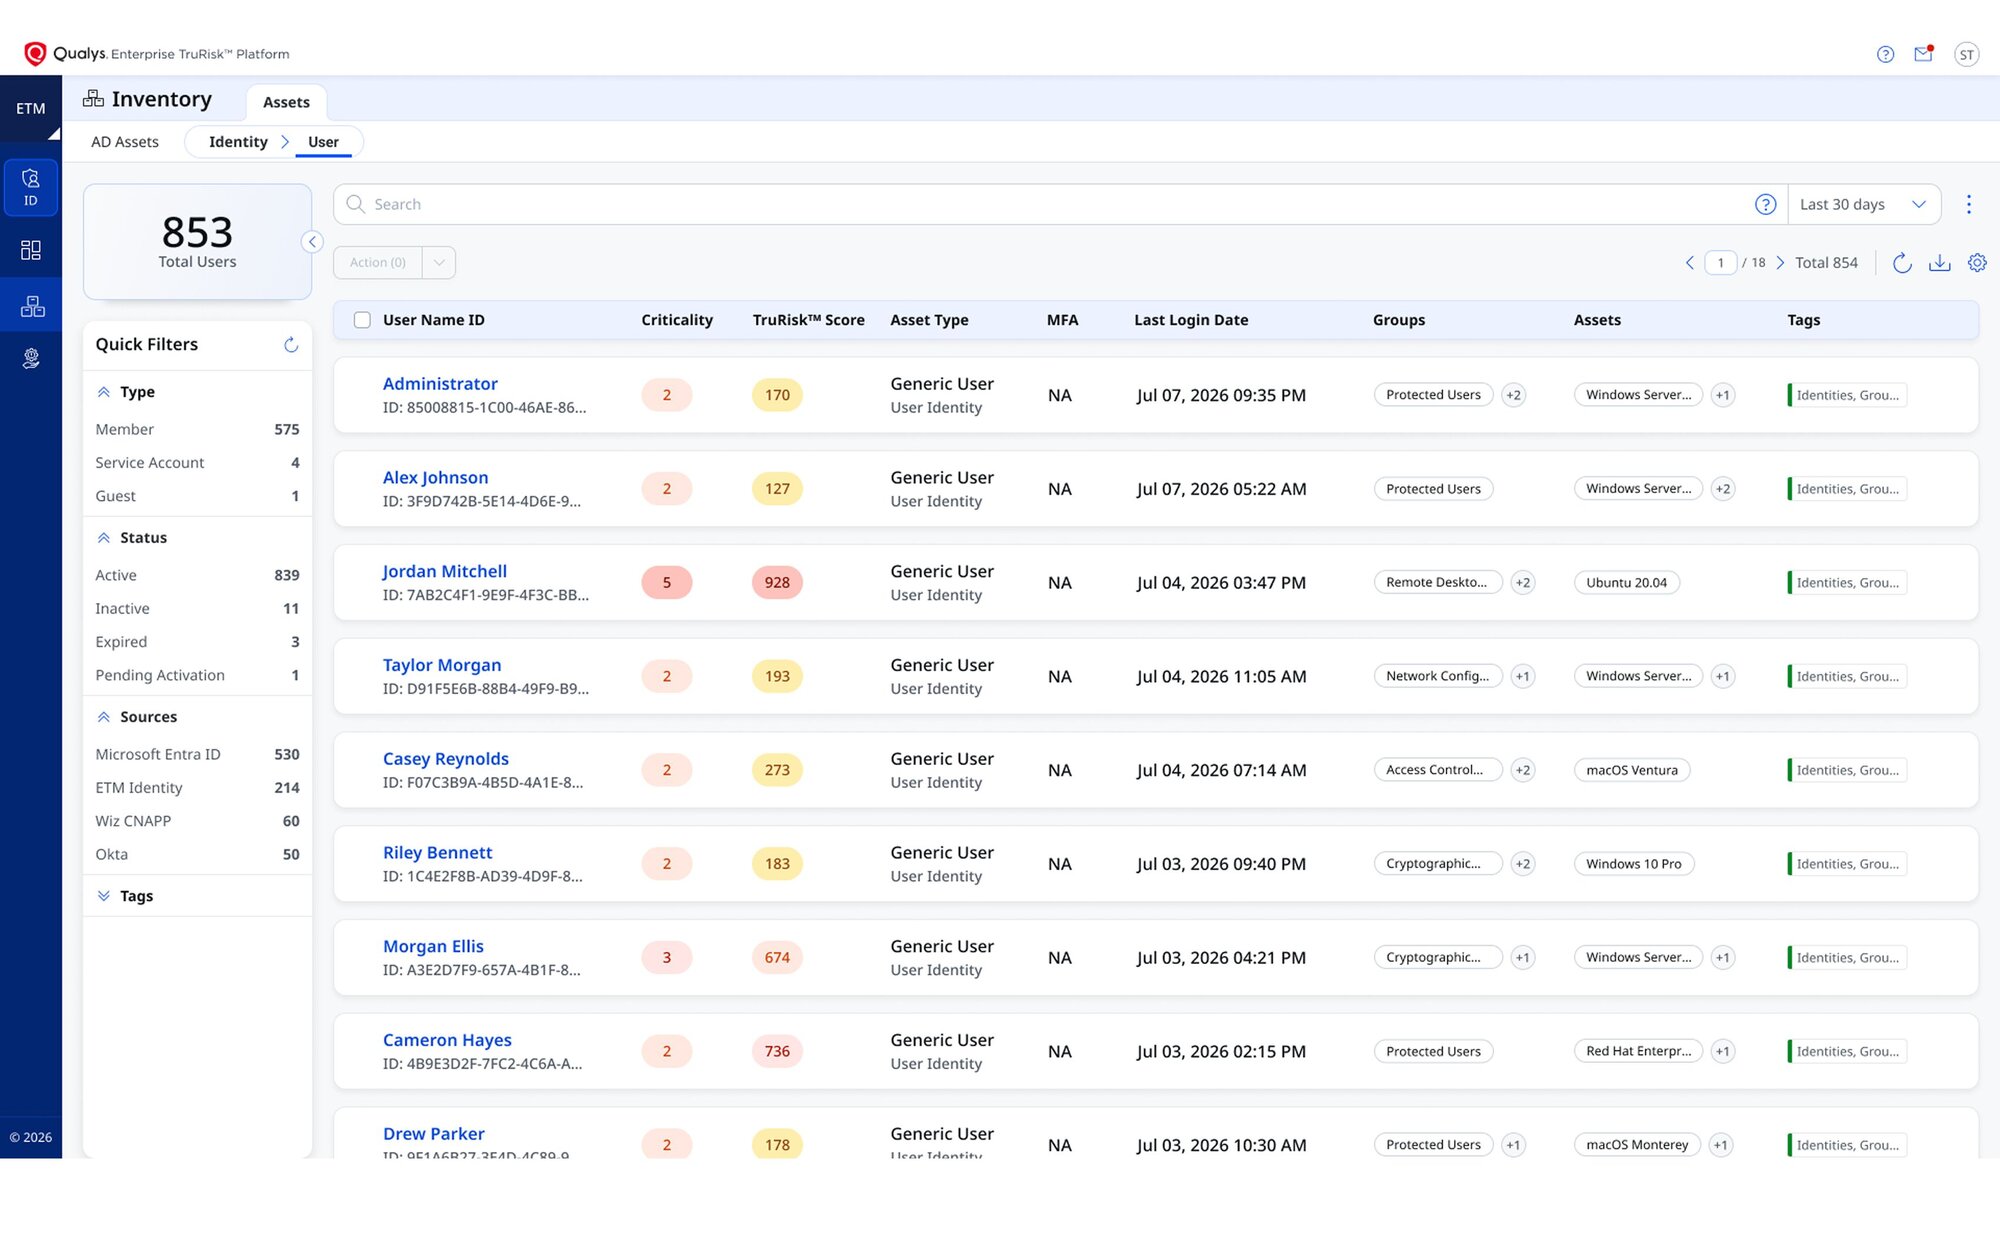
Unified Identity Inventory
Discover every identity — shadow admins, guest accounts, local identities, and service accounts — and uncover the vulnerabilities, misconfigurations, and excessive privileges attached to them. Agentless AD discovery closes the gap where agents can't reach, and every identity rolls into a scalable asset view used across the ETM platform.
Identity TruRisk™ Prioritization
Accelerated Identity Risk Remediation
See How ETM Identity Secures Every Identity, Before Attackers Find the Gap
Eliminate Identity Blind Spots. Reduce Exposure Before It's Exploited.
Get graph-based visualization of privilege chains, Group Policy Object (GPO) influence, and toxic combinations, ranked by real asset risk, not privilege count. Map blast radius by showing how far a compromised account can reach through inherited memberships, nested permissions, and delegated rights, including how easily it can reach critical assets like Domain Controllers. Every chain comes with an AI-generated explanation of why it matters, and converts into a ranked, actionable item. Foreign Security Principal detection surfaces external access hiding in cross-forest trusts.
Go beyond individual findings to spot MFA gaps, toxic combinations, stale accounts, and privileged users. Enrich raw identity data with 25+ threat intelligence and directory sources, mapped to MITRE ATT&CK for real exploitability, not just policy violations.
Monitor AD objects in real time for anomalies like privilege escalation, MFA disablement, and policy tampering. Every modification is tracked who-changed-what-when-where, cutting attacker dwell time before the next scan cycle.
Unify identity risk by bringing together native AD, Entra ID, and Okta connectors with findings from the third-party identity tools you already run, into one consolidated Identity TruRisk™ view.
Enforce Zero Trust principles by continuously mapping findings to DISA STIG, CIS, HIPAA, PCI-DSS, GDPR with audit trails and non-repudiation, generated continuously.
Qualys Enterprise TruRisk Management (ETM) is the unified, AI-augmented Risk Operations Center that ingests and correlates data from all your security tools, quantifies cyber risk in business terms, and automates remediation—so you can focus time and resources only on what truly matters.
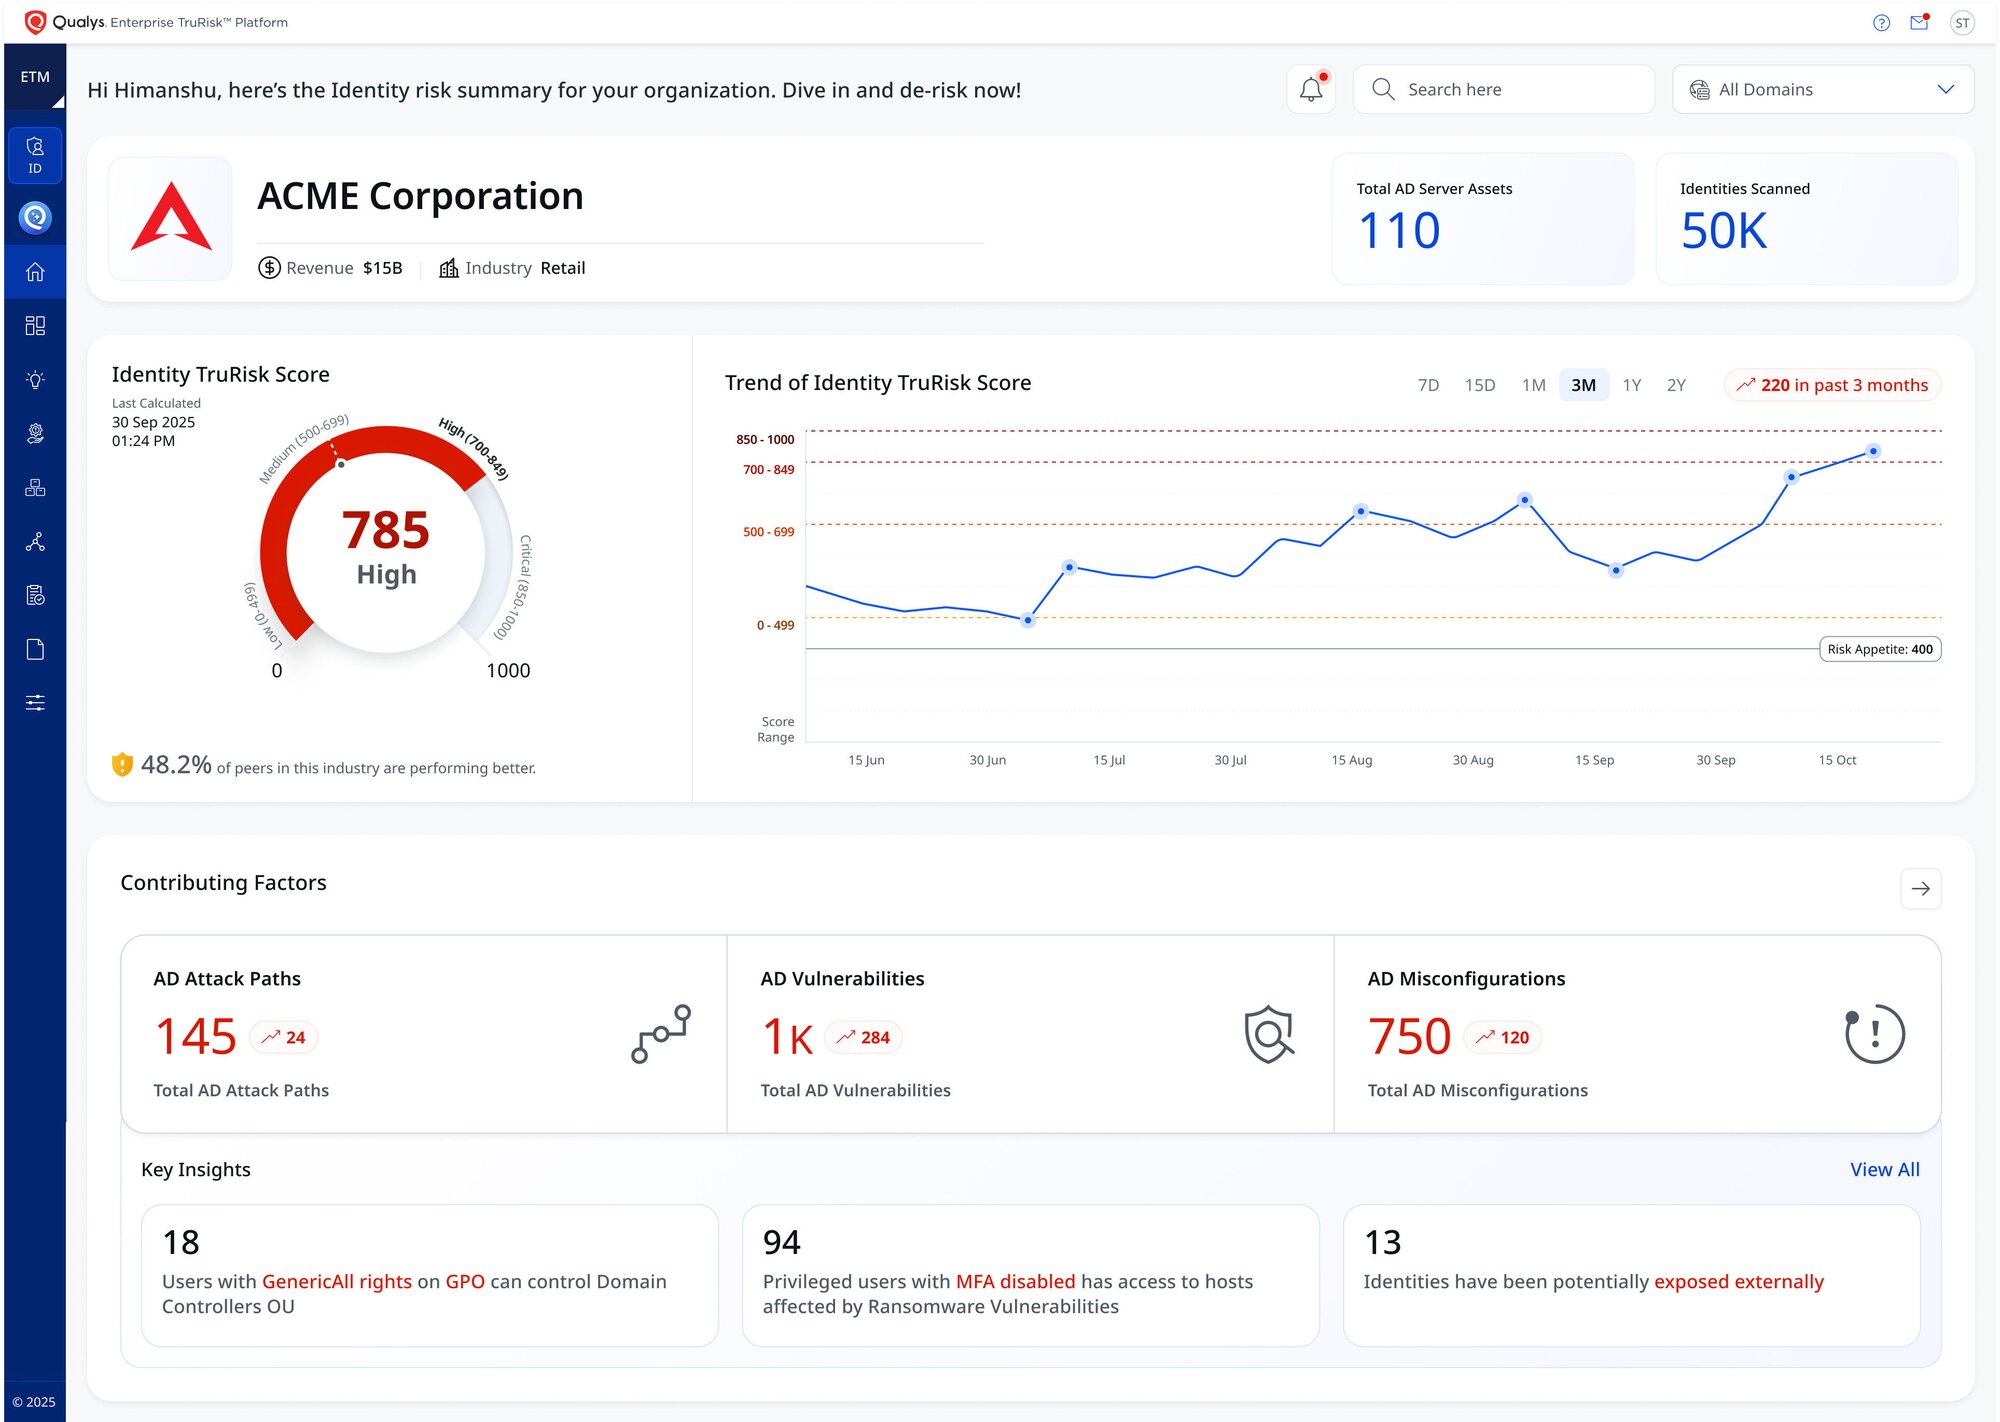
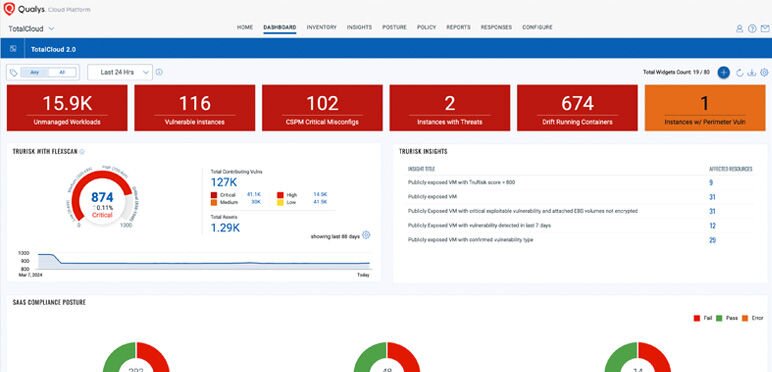
Drive data-driven decisions with actionable insights and customizable security dashboards.
Cloud environments challenge IT security teams in prioritizing risk remediation. With evolving attack techniques, organizations need efficient tools and strategies to preemptively mitigate risks.
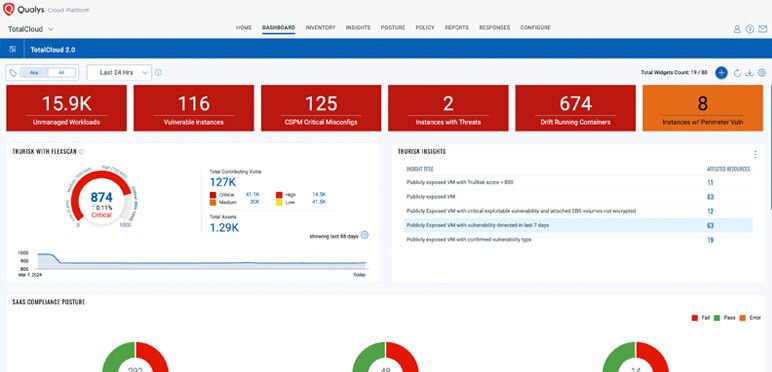
Discover risky assets and factors with actionable insights and customizable dashboards.
As attack techniques evolve, cloud environments face constant risk. Organizations need comprehensive solutions to learn trends and mitigate threats preemptively.
Discover risky assets and factors with actionable insights and customizable dashboards.
As attack techniques evolve, cloud environments face constant risk. Organizations need comprehensive solutions to learn trends and mitigate threats preemptively.
Related Resources
From Active Directory Visibility to Identity Risk Prioritization - What’s New in ETM Identity
Qualys ETM Identity: Transform identity intelligence into prioritized action with complete attack path visibility and contextual risk.

Qualys ETM Identity (Enterprise TruRisk Management for Identity) is a solution that provides a unified view of identity-related security risks across hybrid environments. It addresses the problem of identity silos by centralizing the security posture of both human and machine identities, allowing organizations to measure, prioritize, and eliminate identity exposures that pose the greatest threat.
ETM Identity uses a single, unified platform to ingest and aggregate identity data from various sources, including Active Directory, Azure AD, and privileged access management (PAM) solutions. It then correlates these identity exposures with the risk status of connected IT assets, providing a full, contextual understanding of the potential attack surface.
The Identity TruRisk score is a dynamic, calculated metric that quantifies the real-world risk associated with each identity and asset in the environment. It is used to move teams beyond simple vulnerability counts by prioritizing the most dangerous identity exposures that are weaponized, exploited, or linked to critical assets, ensuring focused remediation.
ETM Identity uses a single, unified platform to ingest and aggregate identity data from various sources, including Active Directory, Azure AD, and privileged access management (PAM) solutions. It then correlates these identity exposures with the risk status of connected IT assets, providing a full, contextual understanding of the potential attack surface.
ETM Identity utilizes advanced graph database analysis to visualize complex relationships. It maps and displays all possible lateral attack paths an attacker could take, originating from a compromised identity. It also clearly visualizes domain trusts and misconfigurations, helping security teams understand and harden their least-privilege boundaries and reduce lateral movement risk.
Yes, ETM Identity is designed to be highly interoperable. It can ingest findings and context from third-party identity solutions, such as Privileged Access Management (PAM) tools and other Identity Governance and Administration (IGA) solutions. This consolidation ensures that all identity data is unified within the TruRisk Platform for centralized scoring and risk analysis.
Qualys ETM Identity (Enterprise TruRisk Management for Identity) provides unified risk operations to secure identity posture. By centralizing visibility and risk scoring for both human and machine identities, it directly supports Zero Trust mandates and helps agencies continuously monitor and adhere to identity-related security controls required by frameworks like NIST.