TotalCloud DSPM helps you continuously discover, classify, and protect sensitive data across your cloud and container workloads using agentless scanning to identify data exposure risks and take rapid, appropriate action.
Know exactly what sensitive data exists, where it lives, and who has access to it, across VMs, container images, object storage, and AI models.

Deploying Qualys CDR for AWS and Azure with just a few clicks, in a matter of minutes, across multiple AWS and Azure subscriptions, was a game changer for our security team. We have a complex environment with many controls, and TotalCloud team worked with us on integration with existing solutions including Secure Web Gateways and integrated SIEM. With their engineering team, together made sure all the security finds were tightly integrated with our SIEM platform. I have rarely seen this level of competency and engagement effort from a vendor.
Within just a few months of deploying Qualys Container Security, we designed an automated workflow to support our continuous integration and continuous delivery [CI/CD] pipeline in Jenkins. By automatically scanning our Docker images before deployment, we help our DevOps teams to ensure that they do not push vulnerable software into production.
Another thing that really impressed us about Qualys was the expertise, professionalism and dedication of their team. Throughout the implementation process and beyond, we have always been able to count on Qualys to give us the support and guidance we need.

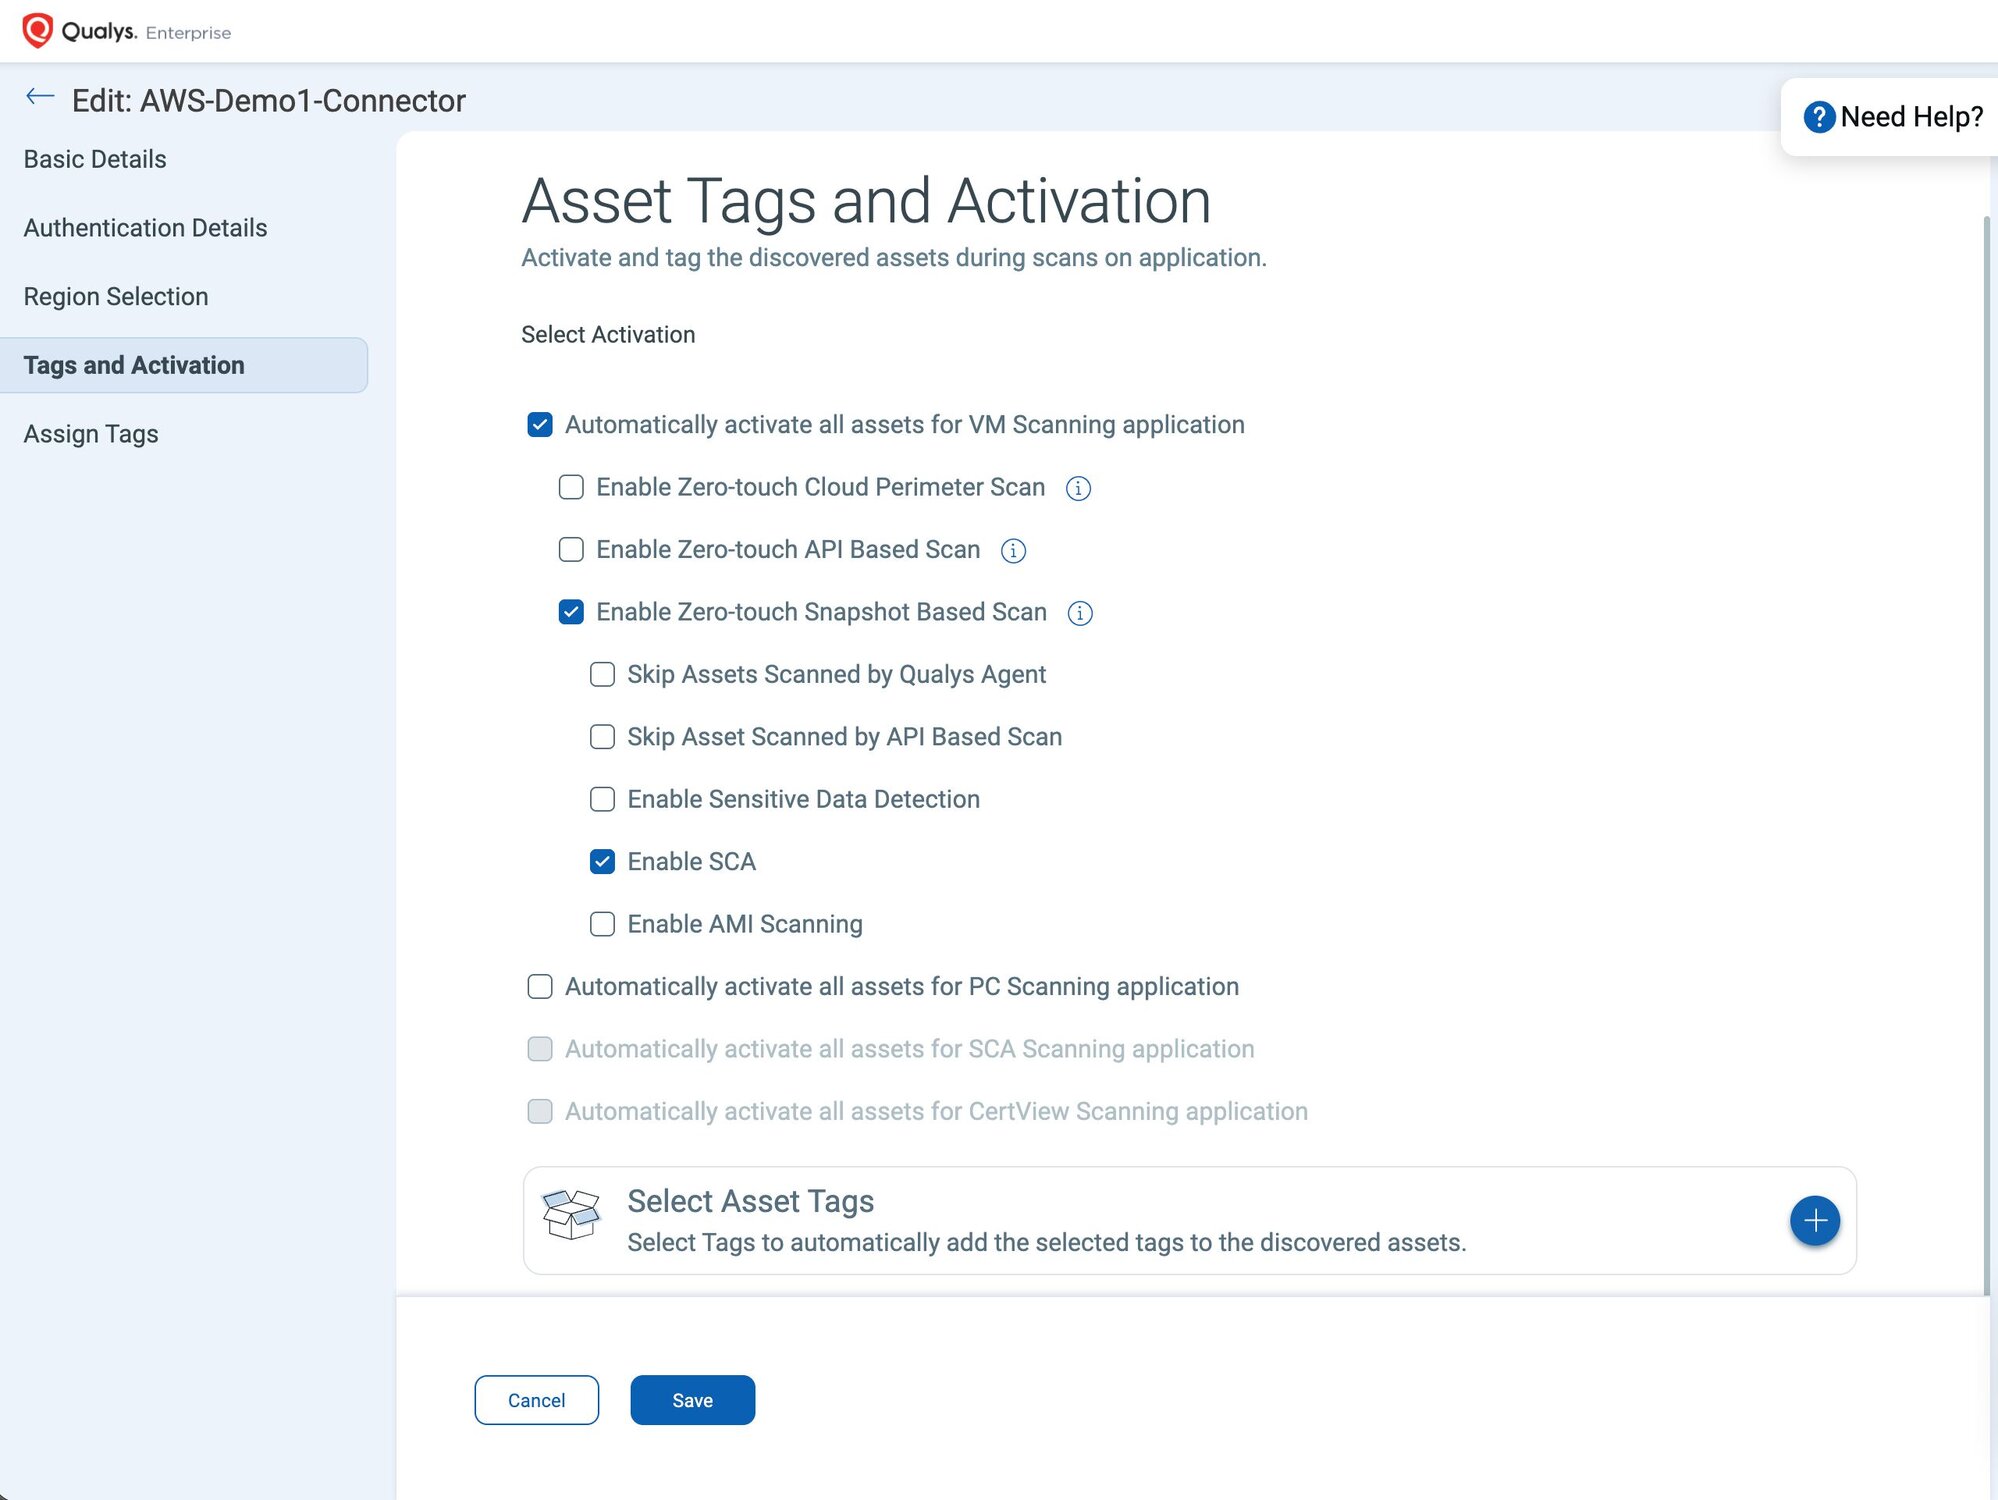
Automatically discover sensitive data across VMs, container images, object storage, and AI models using agentless or snapshot-based scanning with no performance impact on production workloads.

Classify PII, PHI, PCI data, hardcoded credentials, and secrets using built-in detectors across all scanned cloud resources. Always know what sensitive data you’re storing and where.

View, filter, and drill into all sensitive data findings across every cloud resource in one unified investigate tab with direct links to the owning resource, identities, and access exposures.

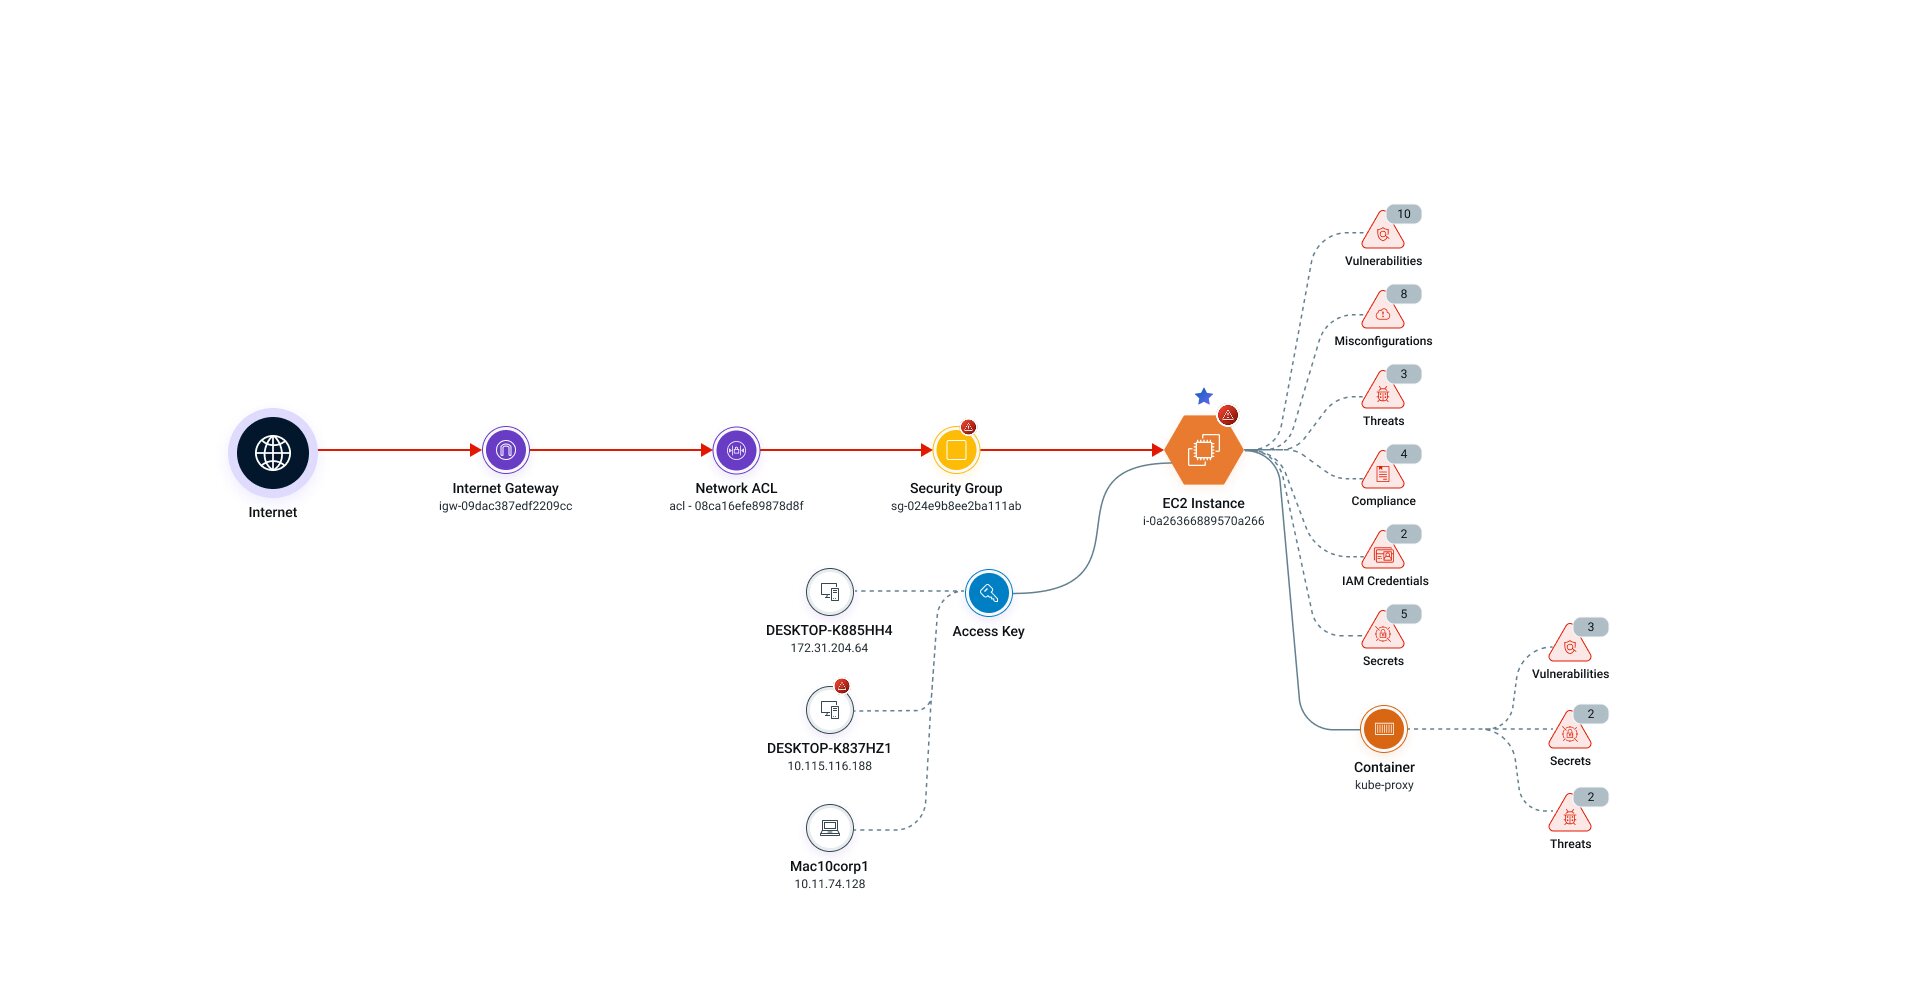
Enriched attack path analysis with sensitive data context to automatically elevate and prioritize paths that can expose PII, PHI, or credentials. Jump directly to findings from any attack path node.
Empower your security team to discover, classify, and protect sensitive data from VMs and containers to object storage and AI models in a single, unified DSPM platform integrated with Qualys TotalCloud™.
No-Cost, 30-Day Trial
Introducing TotalCloud™ with TruRisk Insights
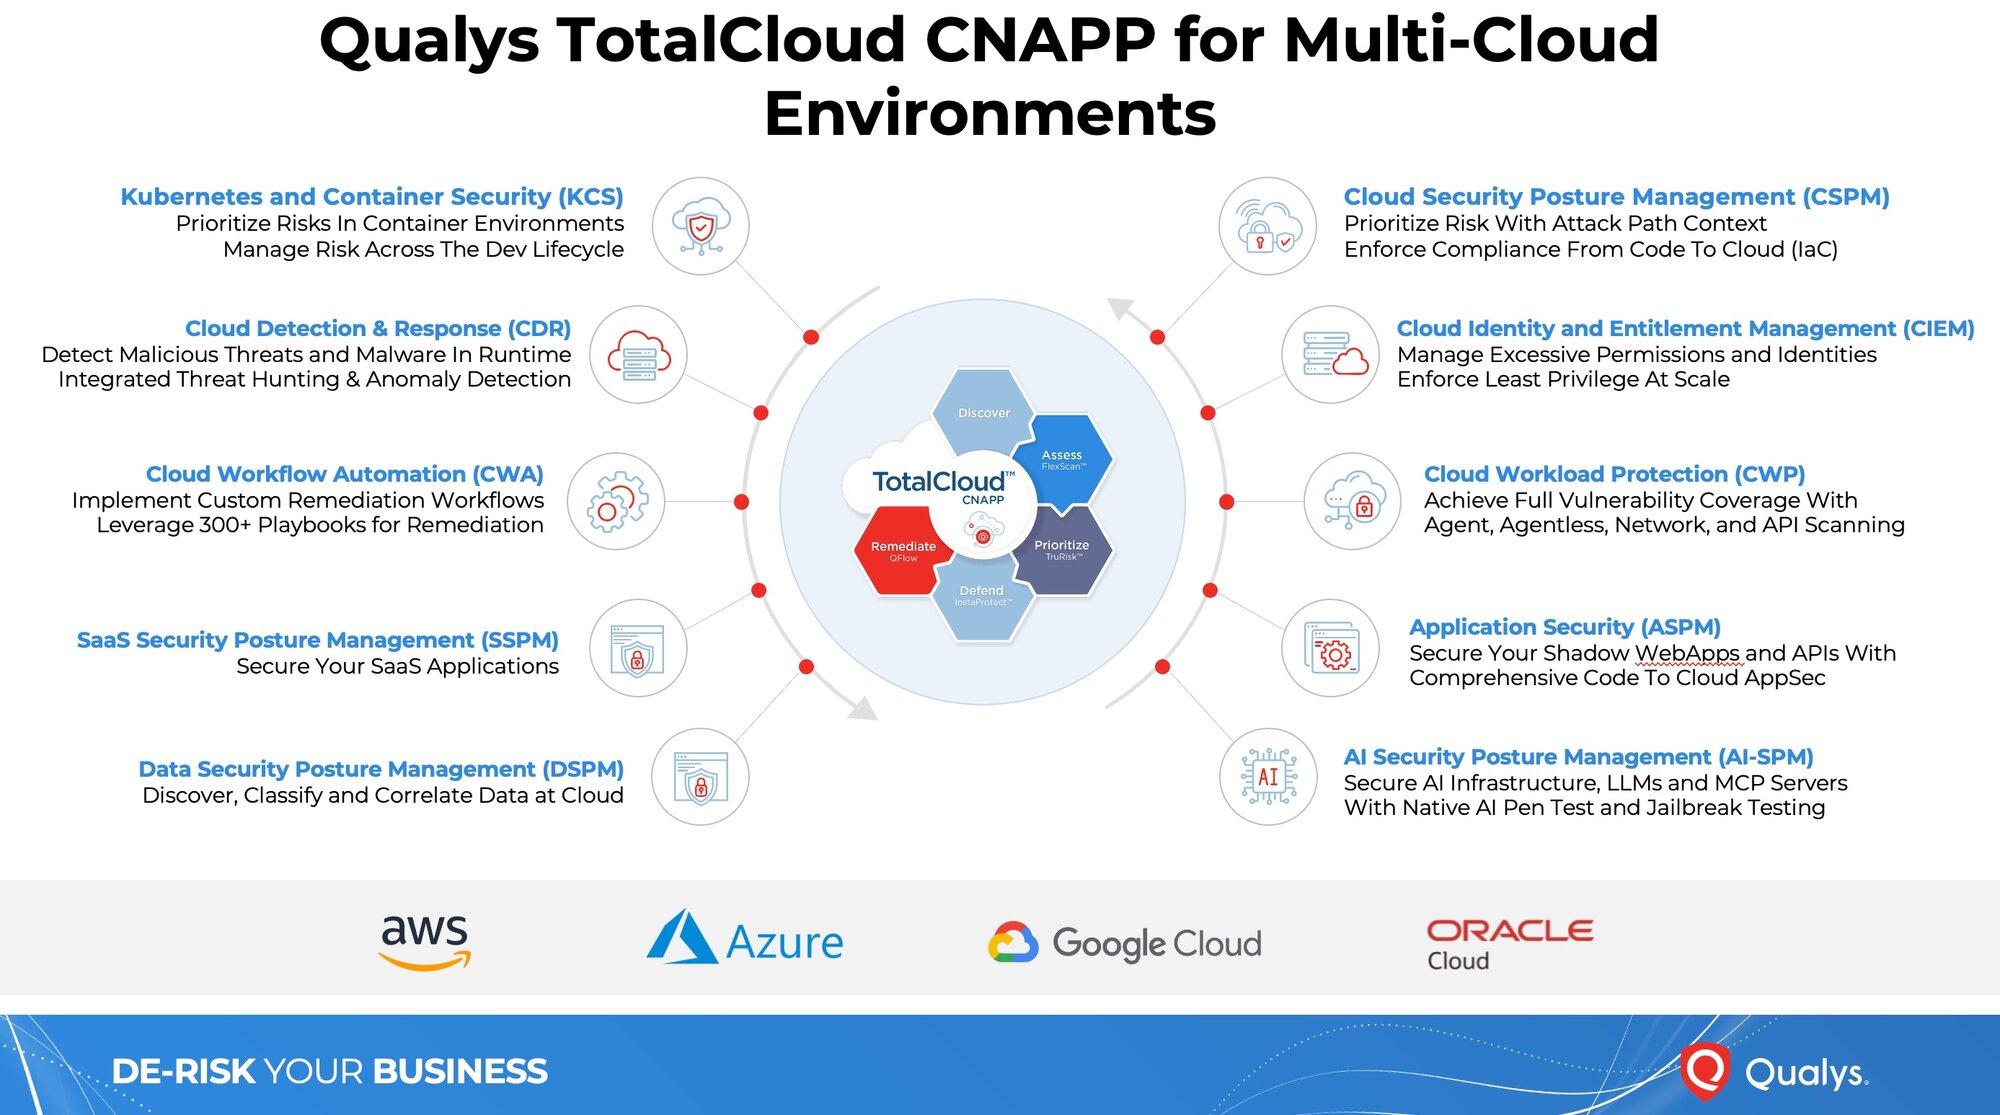
The Enterprise TruRisk Platform provides you with a unified view of your entire cyber risk posture so you can efficiently aggregate and measure all Qualys & non-Qualys risk factors in a unified view, communicate cyber risk with context to your business, and go beyond patching to eliminate the risk that threatens the business in any area of your attack surface.
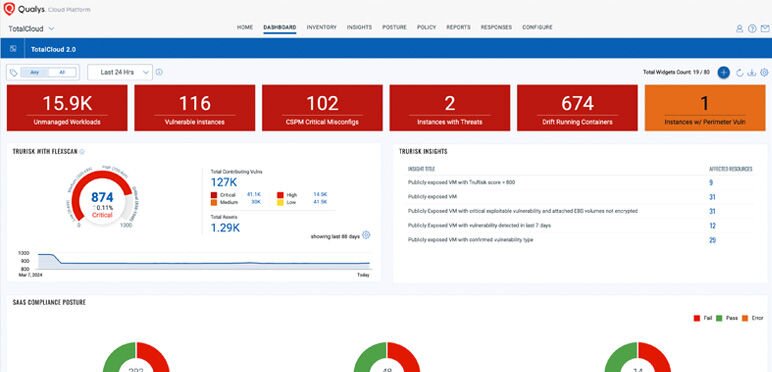
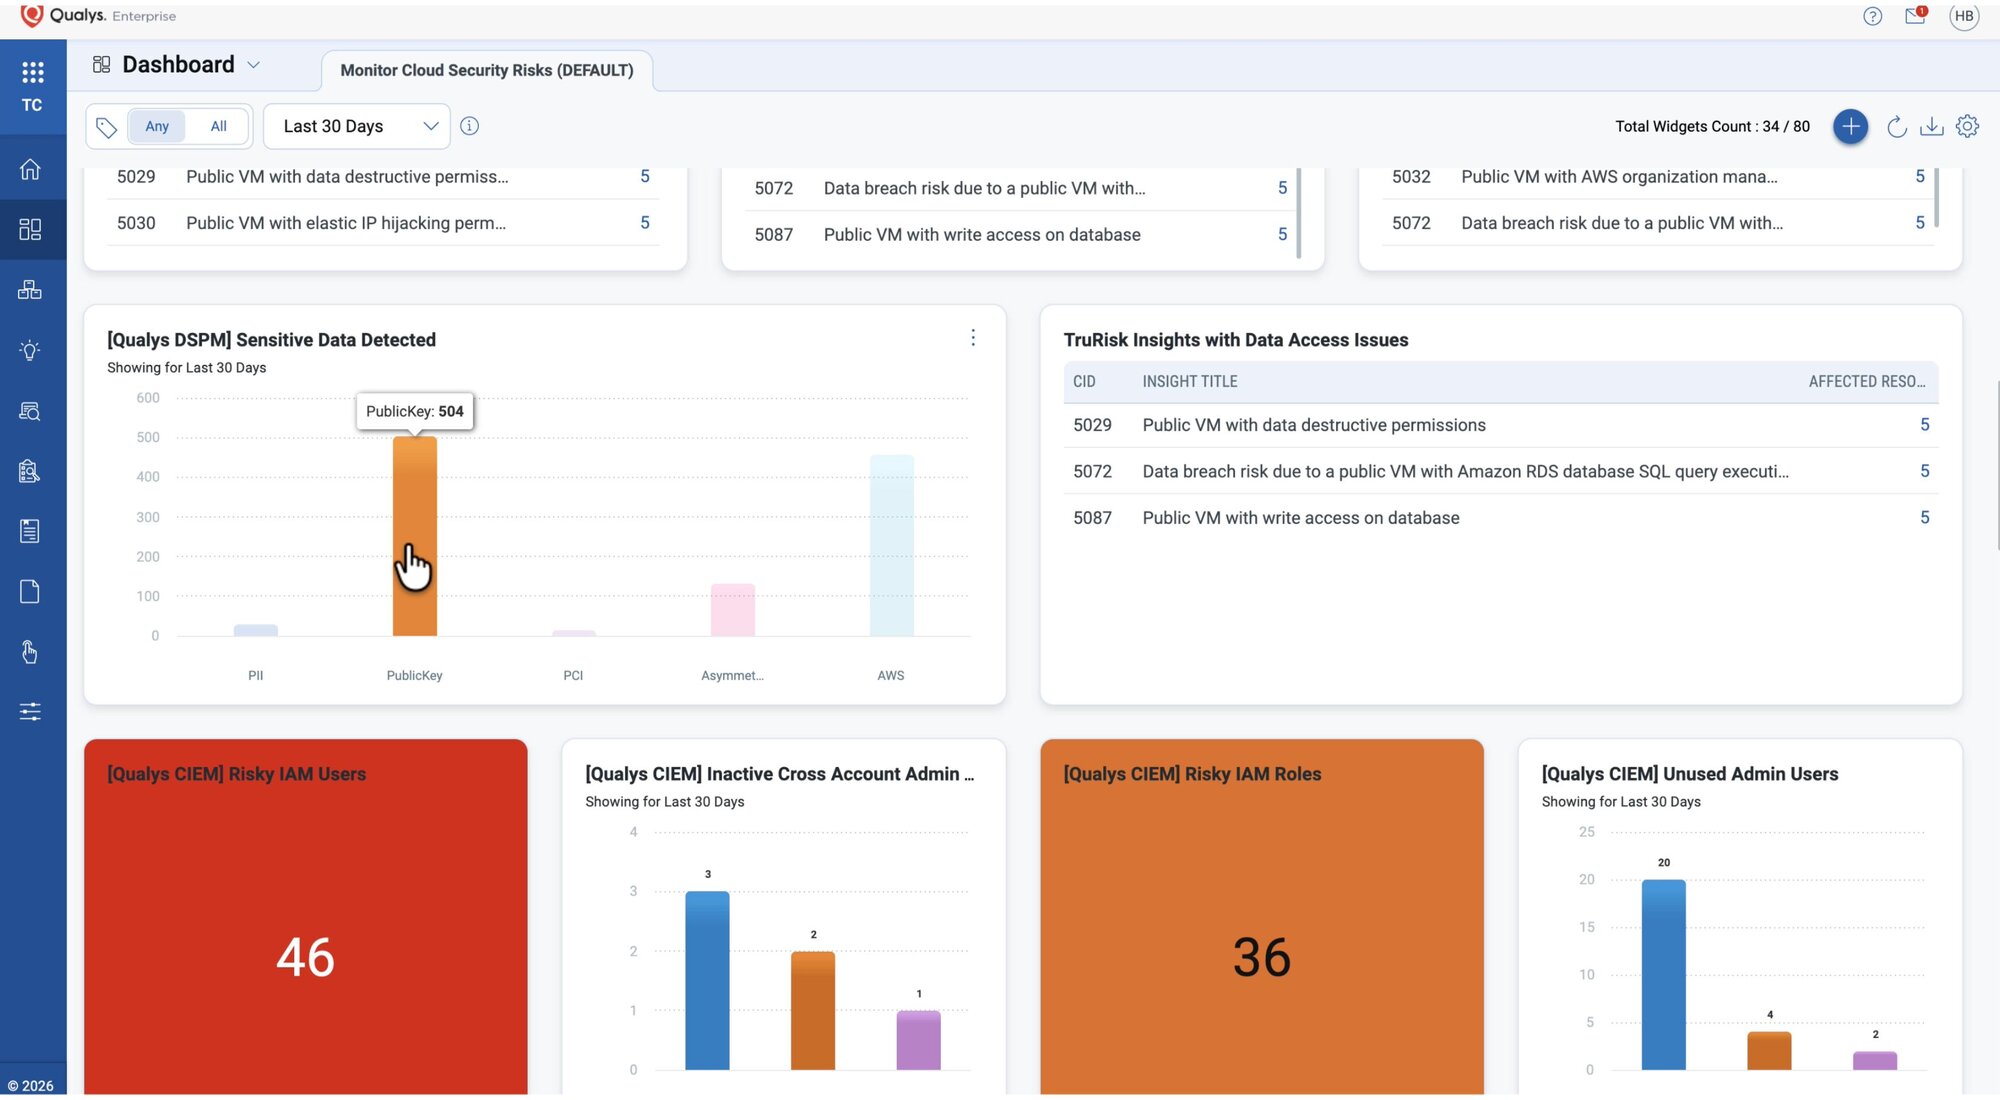
Drive data-driven decisions with actionable insights and customizable security dashboards.
Cloud environments challenge IT security teams in prioritizing risk remediation. With evolving attack techniques, organizations need efficient tools and strategies to preemptively mitigate risks.
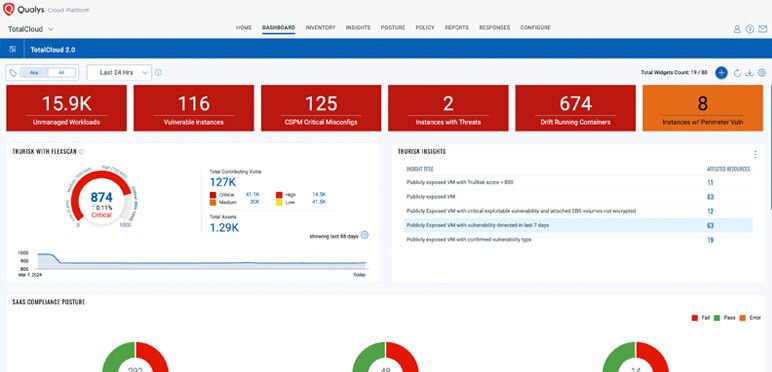
Discover risky assets and factors with actionable insights and customizable dashboards.
As attack techniques evolve, cloud environments face constant risk. Organizations need comprehensive solutions to learn trends and mitigate threats preemptively.

Qualys DSPM is a TotalCloud capability focused on discovering sensitive data and adding data exposure context to cloud security risk, investigation, and prioritization.
Qualys can identify sensitive artifacts such as credentials, API keys, passwords, tokens, and other secrets that could create unauthorized access or exposure risk.
Yes. TotalCloud can detect secrets during snapshot-based assessments, identifying hardcoded credentials and other sensitive artifacts in workload files and configurations.
Yes. TotalCloud supports sensitive-data detection for supported GCP Linux instances using zero-touch snapshot-based scanning and a configured GCP connector.
Data context helps teams identify cloud exposures that could affect sensitive information, allowing higher-risk assets and attack paths to receive faster attention.
Sensitive-data discovery helps teams identify insecure data locations and credential exposure that may create data-protection and compliance concerns requiring remediation.
Yes. TotalCloud can surface sensitive-data detections in investigation workflows, helping analysts connect data exposure with suspicious activity and runtime threats.
Vulnerability scanning finds exploitable software weaknesses. DSPM adds visibility into sensitive data and secrets, providing additional context about what may be exposed.
DSPM extends TotalCloud CNAPP with data-risk context, correlating sensitive-data exposure with cloud assets, configurations, identities, threats, and broader attack paths.