FREE SERVICE · CVE-2026-109618 · CVE-2026-109619
PHP2Shell: Know Your Exposure and Mitigate It With Qualys
Our free service finds PHP2Shell across your internet-facing assets, proves which servers attackers can actually exploit, and gives you a patch or mitigation path for each one, including versions PHP will never fix.
Read the Qualys Threat Research Unit’s PHP2Shell analysis →
Qualys · PHP2Shell exposure
Anonymized customer data
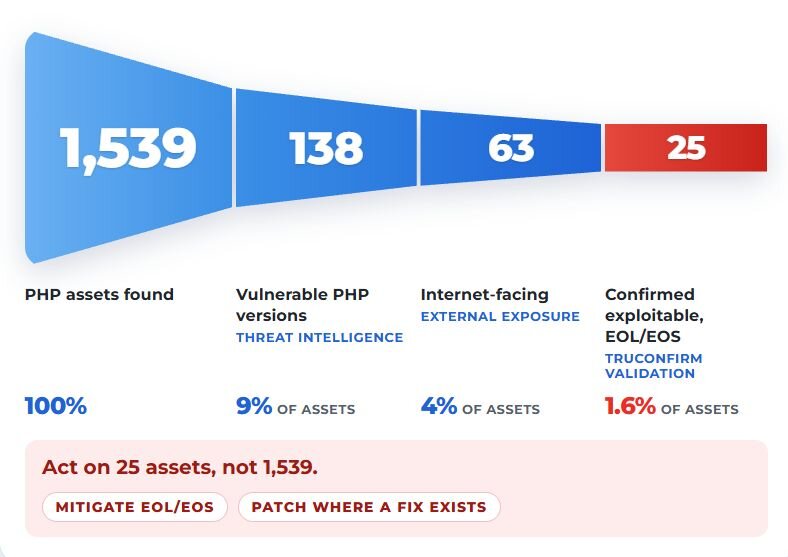

Anonymized customer data captured by Qualys from a real-world environment. Your results depend on your environment.
Start at your internet edge. Finish with a verified fix.
1
Discover
Find every PHP instance, including PHP running in containers or bundled inside other applications.
2
Prioritize and validate
Put internet-facing servers and legacy PHP versions first. See which instances are vulnerable, pinpoint the ones attackers can actually reach, and confirm exploitability.
3
Remediate and mitigate
Patch supported PHP versions, then restart PHP services so the fix takes effect. On PHP 8.1 and earlier, apply OS vendor backports where they exist, or isolate those systems and plan to retire them.
4
Verify
Rescan to confirm every exposure has been closed.
Get our free service
What you'll walk away with:
By submitting this form, you consent to Qualys' privacy policy

A clear view of your internet-exposed PHP
Proof of what attackers can actually exploit
Mitigation for the PHP you can’t patch fast
No agents needed to scan.
WHAT THE FREE SERVICE DELIVERS
Detect, prioritize and mitigate PHP2Shell risk
See what’s exposed, know what’s exploitable, and cut risk even where patching can’t keep up.
DETECT
Early PHP2Shell detection with Qualys InstaScan across your internet-facing assets, scanned from the Qualys cloud with no agents.
WHY IT MATTERS
Replace guesswork, and version strings that can mislead, with a verified list.
Proof of what attackers can exploit
PRIORITIZE
Exploitability confirmed by Qualys TruConfirm with harmless validation payloads, layered with threat intelligence.
WHY IT MATTERS
Your team works on the few that matter. In one environment, 1,539 PHP assets came down to 25.
Mitigate risk where patching can’t keep up
MITIGATE
71% of PHP installations sit on EOL/EOS branches with no upstream fix, and PHP often runs business-critical apps, so patching won’t be fast. Mitigate through the scanner, with no agents required.
WHY IT MATTERS
Cut exposure now on the PHP you can’t patch quickly, without waiting on an upgrade.
How the free service works

Activate the service
We enable the Qualys products your team needs to respond to PHP2Shell, for up to 1,000 assets.

Detect and validate
Scan your internet-facing assets from the Qualys cloud, with no agents to install. See which PHP instances are vulnerable and which ones attackers can actually exploit.

Mitigate or patch
Mitigate EOL/EOS versions through the scanner, with no agents required, and patch where a fix is available.

Free service valid for 15 days, for up to 1,000 assets, from the time of activation.
Proof from the field
Real-world example · InstaScan, powered by Agent Insta
PHP2Shell detected in 10 minutes
CVE-2026-109618 and CVE-2026-109619 were flagged 10 minutes after disclosure, from inventory customers already had.
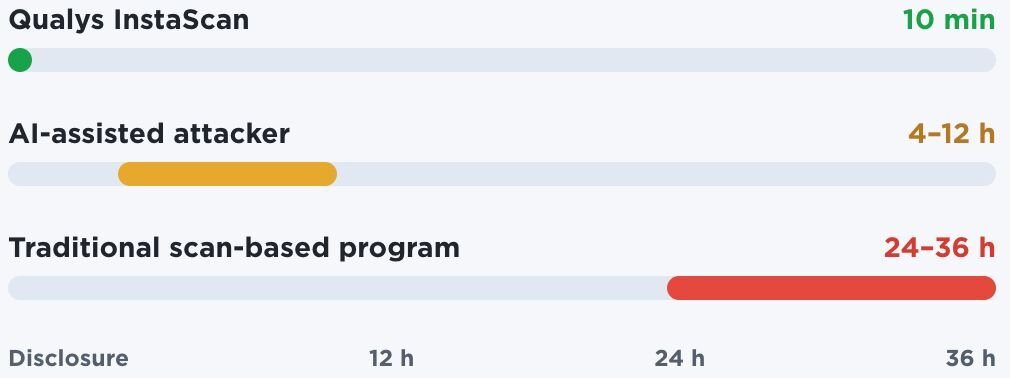
The attacker’s clock starts at disclosure. Now yours does too.
Qualys Threat Research · Anonymized data
99% of PHP installations are vulnerable or EOL/EOS.
Exposure to CVE-2026-109618 and CVE-2026-109619. Updated October 22, 2026.
167M
PHP package installations found
73%
on internet-facing assets
Breakdown by PHP version 155M installations with a known version
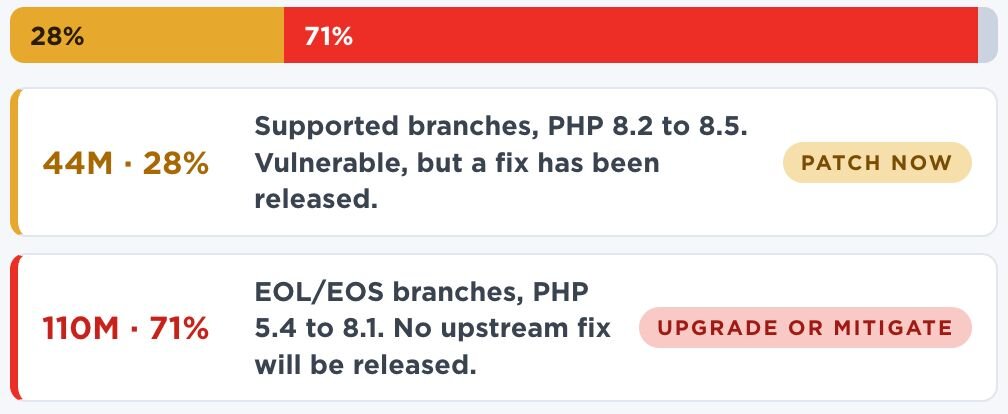
Percentages are of the 155M PHP package installations with a known PHP version.
Mitigation · No agents required
Mitigate the PHP you can’t patch fast
71%
of PHP installations sit on EOL/EOS branches, PHP 5.4 to 8.1, with no upstream fix coming. And PHP often runs business-critical apps, where patching can’t move fast.
How you can mitigate
1
Mitigate through the Qualys scanner, with no agents required.
2
Apply PHP’s recommended configuration mitigations, such as disabling session upload progress and capping request size.
3
Restrict public access or isolate systems that can’t be patched yet, then rescan to confirm exposure is reduced.
Mitigations reduce exposure while you plan upgrades. Updating remains the only complete fix.
PHP’s fixed versions
PHP has released these upstream versions, which fix both vulnerabilities. Updating is the only complete fix.
| PHP branch | Fixed version |
|---|---|
PHP 8.5 | 8.5.12 |
PHP 8.4 | 8.4.27 |
PHP 8.3 | 8.3.36 |
PHP 8.2 | 8.2.35 |
Running PHP 8.1 or earlier? Apply your OS vendor’s backport where one exists, or upgrade to a supported release. Distribution packages may carry the fix under an older version number, so check your vendor’s advisory.
ON-DEMAND emergency briefing
PHP2Shell: 70% of the Web Is at Risk. Find and Fix It Now
Watch the Qualys Threat Research Unit walk through how to find every exposed PHP server and close the door before attackers walk through it.
Wednesday, October 21 · 5:00pm PT
Americas & APAC
Thursday, October 22 · 7:00am PT
Americas & EMEA
With Saeed Abbasi, Head of Threat Research Unit, and Lavish Jhamb, Manager, Product Management, Qualys
Why PHP2Shell can’t wait
The flaws sit in PHP itself, not in your application code. Apache mod_php is most urgent: PHP reports a demonstrated exploit that can trigger before any application code runs. PHP-FPM, php-cgi, FrankenPHP and LiteSpeed are at risk too.
9.2
CVSS v4.0 score for both vulnerabilities
CVE-2026-109618 and CVE-2026-109619
~70%
of websites run on PHP
W3Techs, October 2026
0
credentials an attacker needs
Unauthenticated remote code execution
© 2026 Qualys, Inc. All rights reserved.
