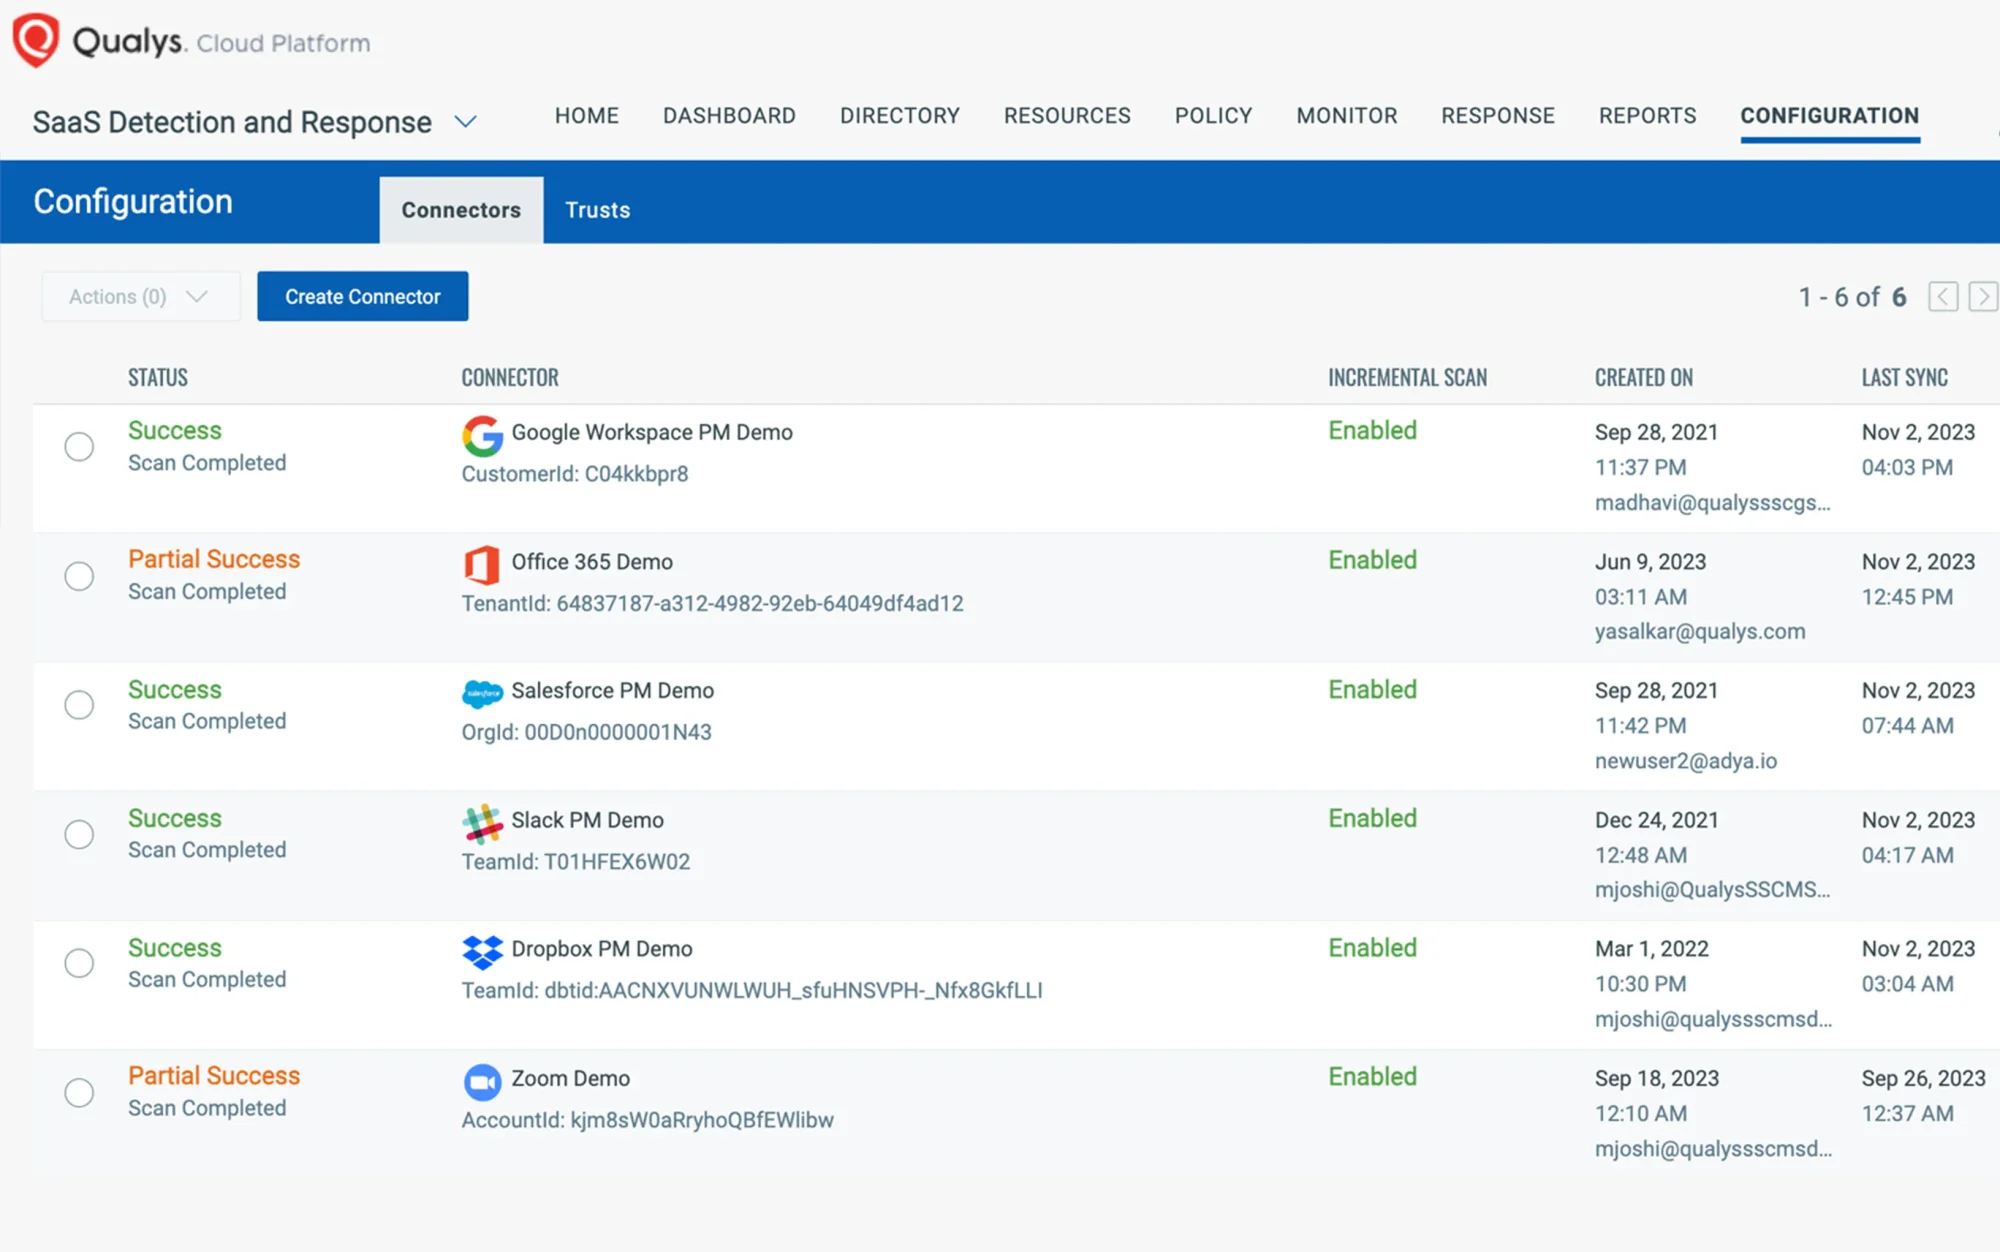
Our SSPM tool helps you automate the process of managing your SaaS apps, including global settings, user privileges, licenses, files, and their security and compliance posture.
A single-pane-of-glass view
To secure your SaaS applications and prevent your confidential data from being exposed, you need continuous, end-to-end visibility of all your deployments.
Simple, native integration with leading SaaS apps
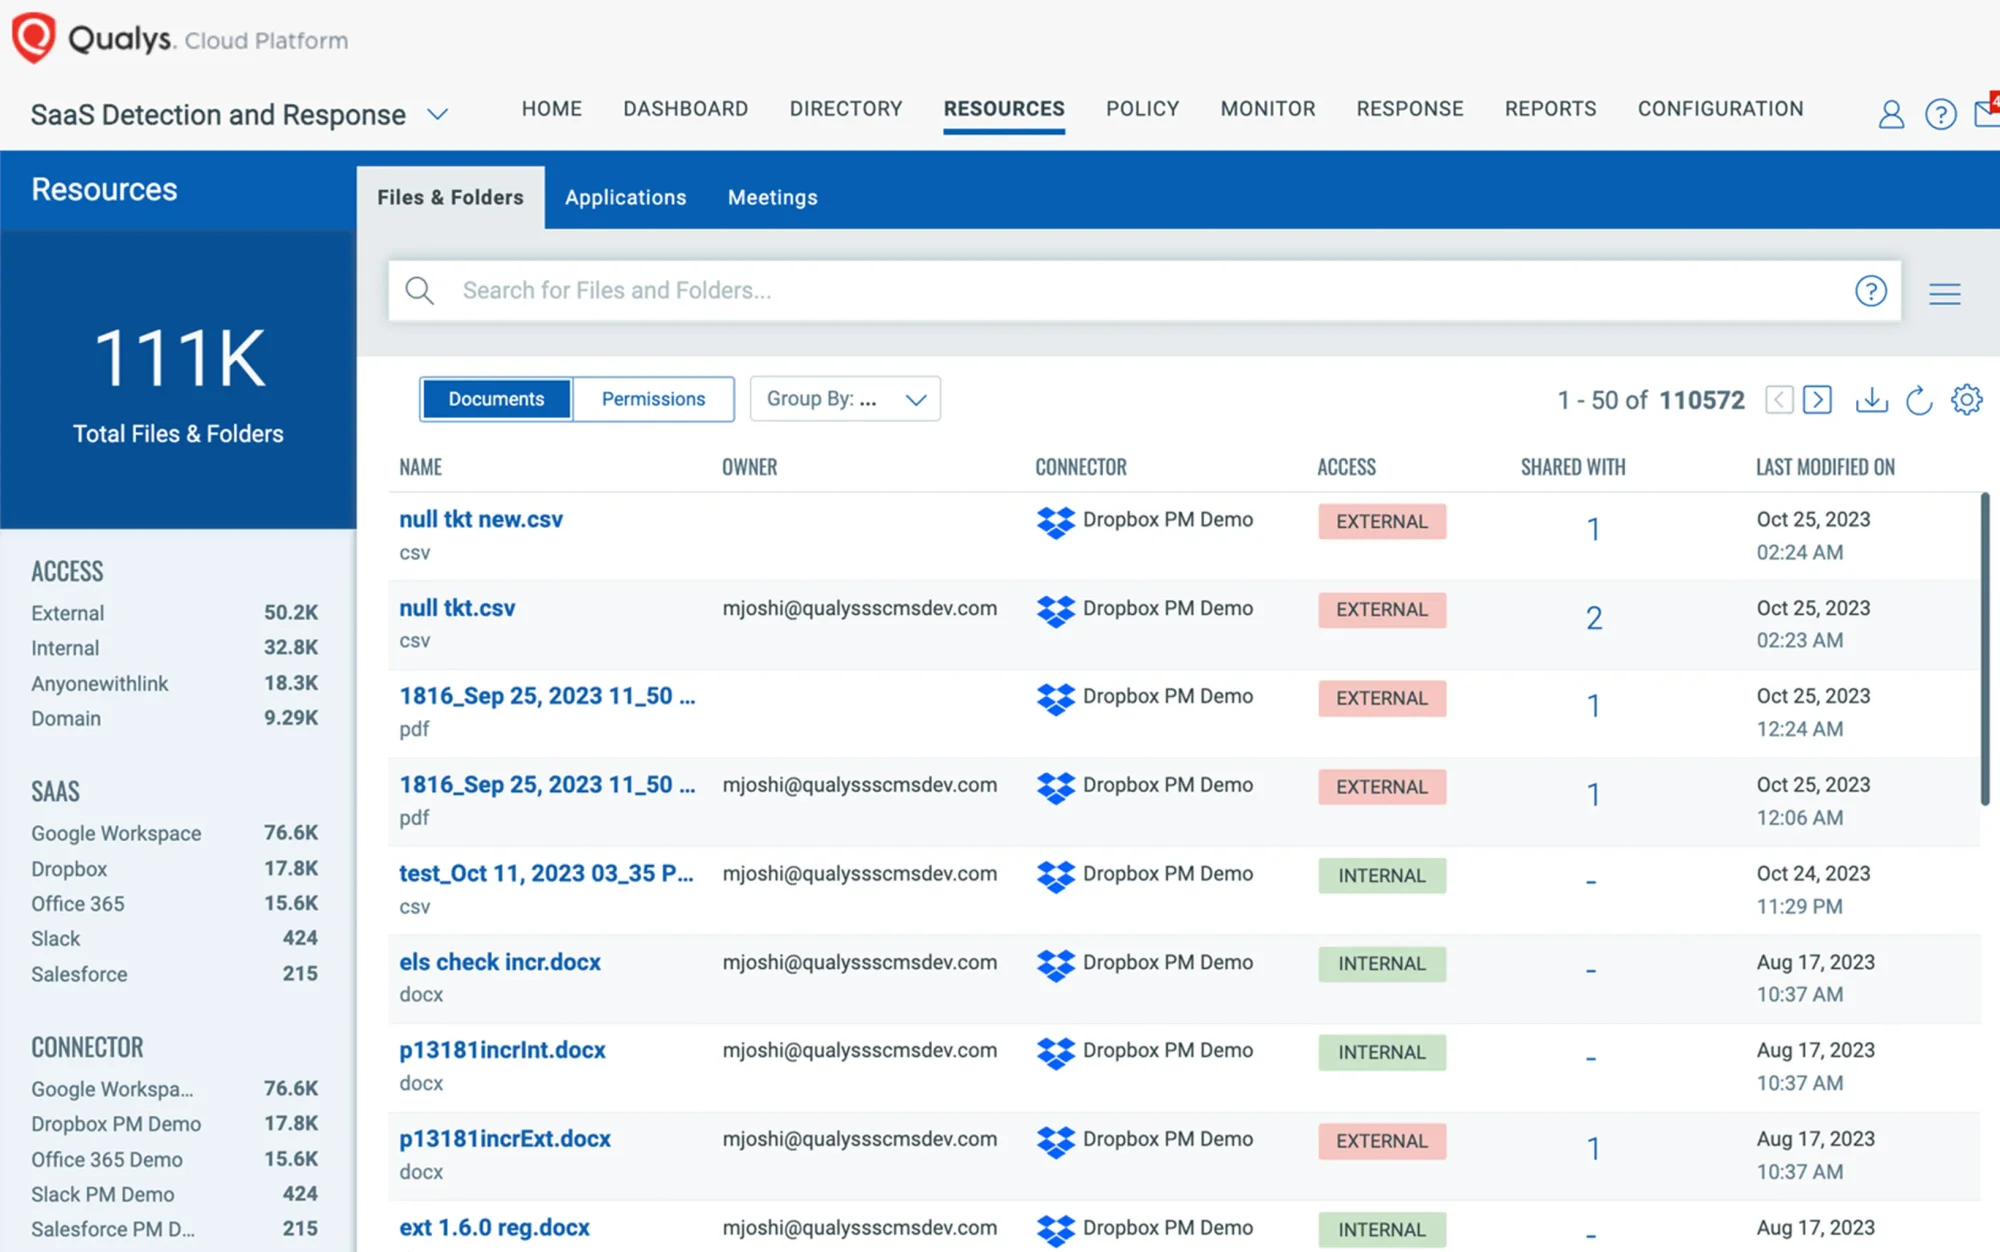
A full, detailed directory of users and files

Deploying Qualys CDR for AWS and Azure with just a few clicks, in a matter of minutes, across multiple AWS and Azure subscriptions, was a game changer for our security team. We have a complex environment with many controls, and TotalCloud team worked with us on integration with existing solutions including Secure Web Gateways and integrated SIEM. With their engineering team, together made sure all the security finds were tightly integrated with our SIEM platform. I have rarely seen this level of competency and engagement effort from a vendor.
Qualys is enhancing its widely used platform to deliver visibility, context, speed, automation, and orchestration in a comprehensive solution to help organizations scale their security and compliance programs for modern software development. Qualys TotalCloud incorporates security into development workflows, enabling them to release secure, reliable code, while giving security teams the control and visibility they need to manage risk by reducing their attack exposure and rapidly responding to threats.
The Qualys approach [to runtime security] empowers security to follow the container image with built-in instrumentation, enabling visibility and behavior enforcement for running containers across all types of container infrastructure.

Automatically inventory all your SaaS application users and user groups (internal and external), including the files and folders they own and have access to, as well as asset data with cyber risk context.
Take control to quickly manage users and data access rights at a granular level – all from a single interface.
Identify security weaknesses like incorrect permissions, at-risk files, file changes, misconfiguration issues, critical vulnerabilities, and exploits using advanced threat intelligence.
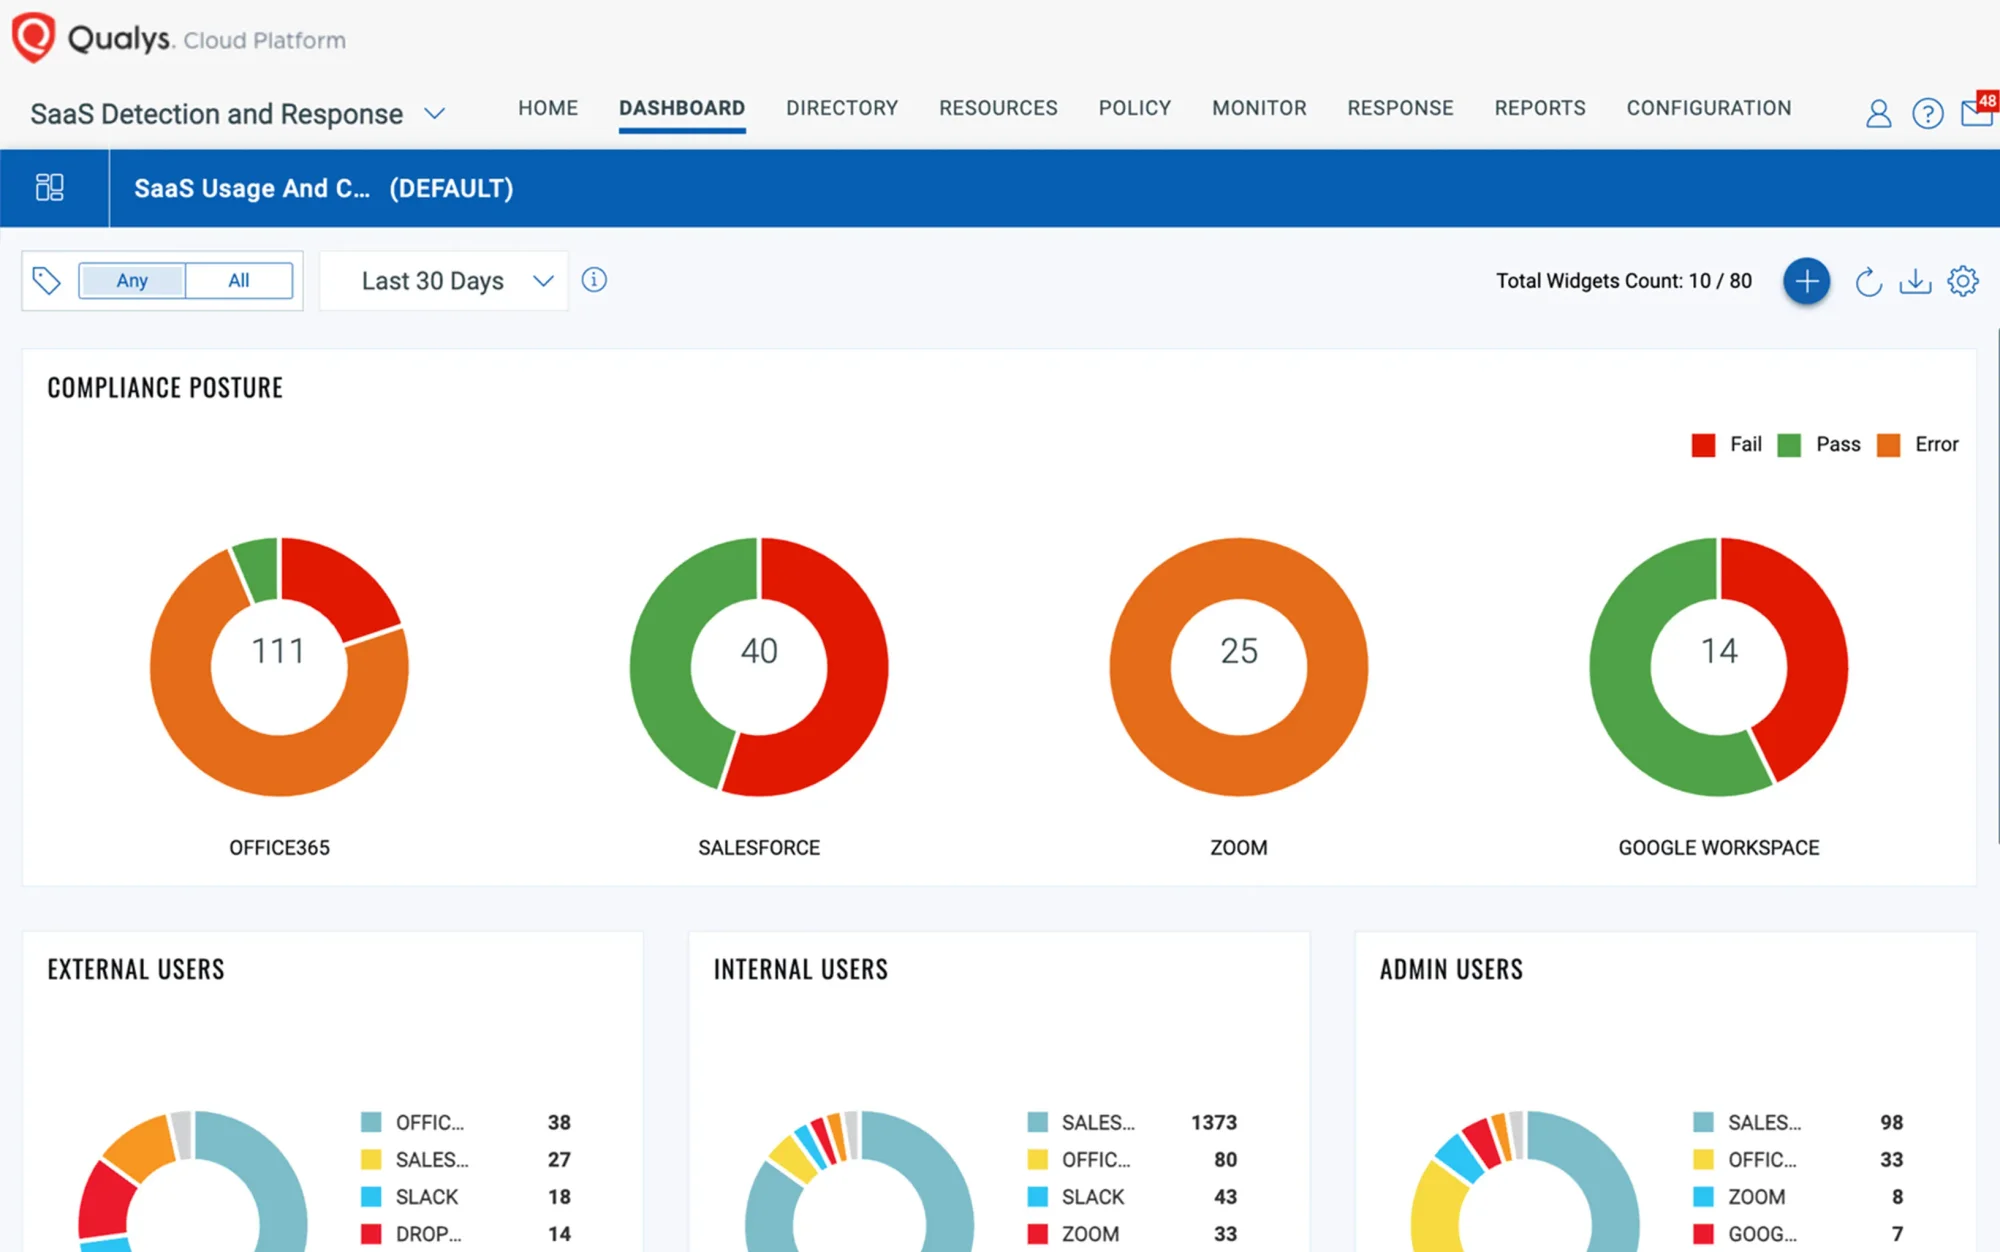
Leverage continuous and automated security posture and configuration assessments of your SaaS applications and enforce compliance with industry benchmarks like O365 via CIS, PCI-DSS, and NIST.
Get real-time alerts based on the full context of users and their endpoints to accurately determine risk. Use multiple data insights to configure alerts for user rights, device location, file changes, vulnerabilities, misconfigurations, advanced threats, and more.
Set up custom alerts for critical security misconfigurations and automatically patch vulnerabilities, misconfigurations, and threats with a single click.
Get continuous visibility of your SaaS applications and fix security and compliance issues in a single pane of glass
Gain clarity and control of your SaaS stack by providing in-depth user and device visibility, data security insights, proactive posture monitoring, and automated remediation of threats - all from a single screen.
No-Cost, 30-Day Trial
Introducing TotalCloud™ with TruRisk Insights
Gain clarity and control of your SaaS stack by providing in-depth user and device visibility, data security insights, proactive posture monitoring, and automated remediation of threats - all from a single screen.
Introducing TotalCloud™ with TruRisk Insights
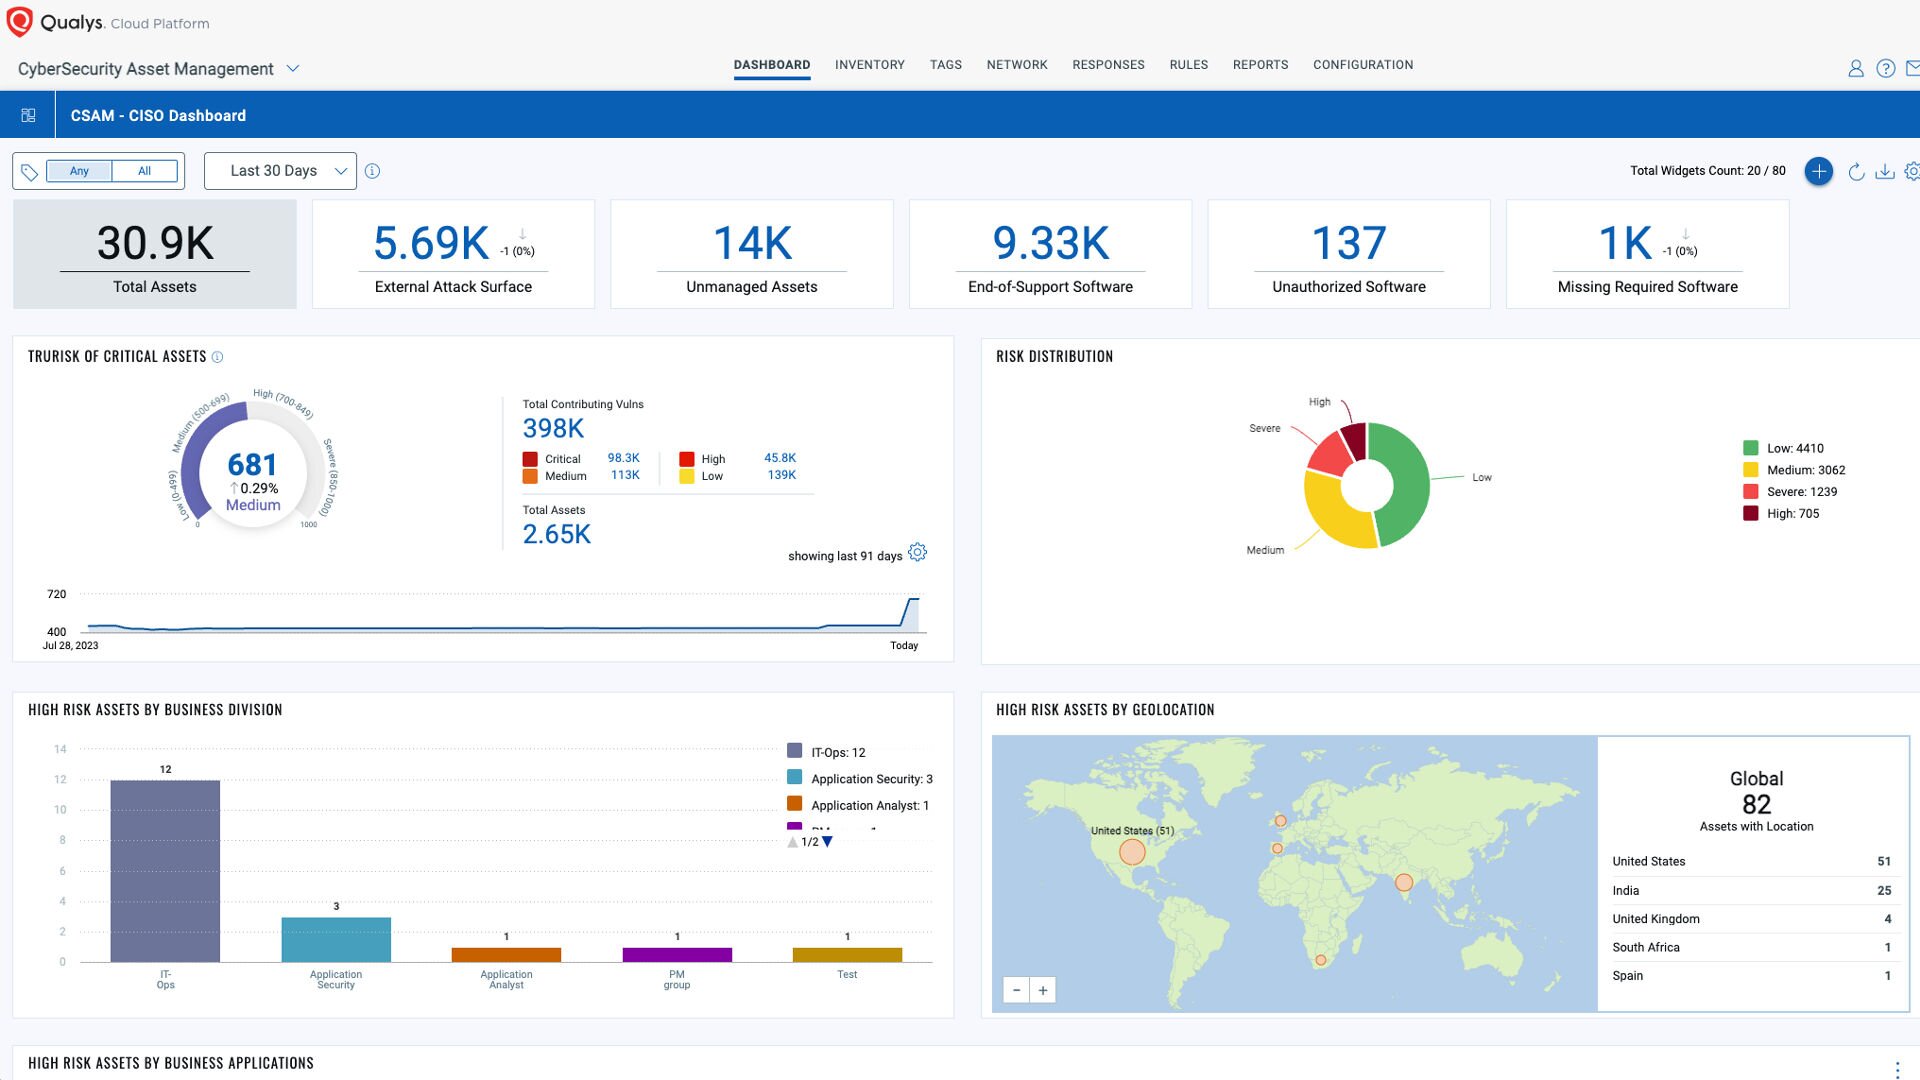
The Enterprise TruRisk Platform provides you with a unified view of your entire cyber risk posture so you can efficiently aggregate and measure all Qualys & non-Qualys risk factors in a unified view, communicate cyber risk with context to your business, and go beyond patching to eliminate the risk that threatens the business in any area of your attack surface.
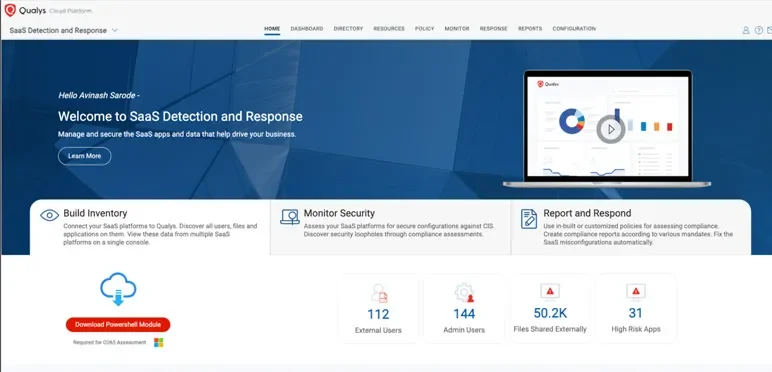
On an average, 63% of breaches start from an misconfigurations that are not identified by the Security analysts and the administrators.
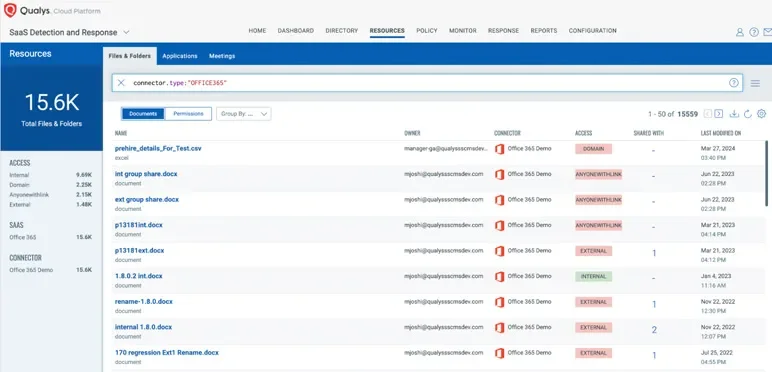
On an average, 20% of data leakage and exfiltration attacks happen due to uncontrolled external sharing of files and excessive API permissions.
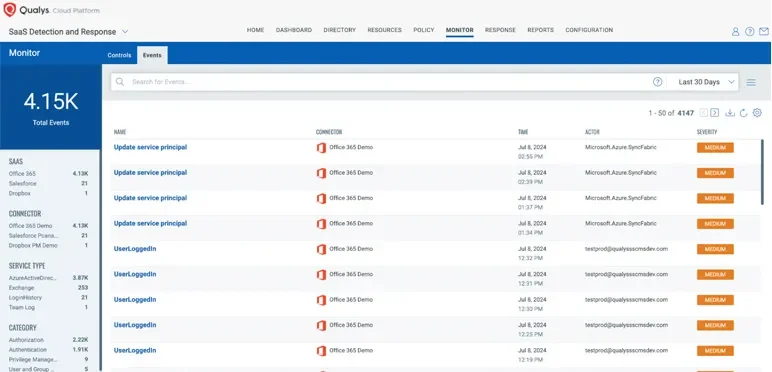

SSPM continuously evaluates the security configuration of supported SaaS applications to identify misconfigurations, risky permissions, and compliance gaps. Qualys SSPM helps centralize SaaS posture management so security teams can reduce configuration risk across business-critical applications.
SaaS providers secure the service itself, but customers remain responsible for how applications are configured, who has access, how data is shared, and which third-party applications are connected. SSPM helps manage these customer-controlled risks.
Qualys SSPM supports popular apps like Anthropic Claude, Microsoft 365, Google Workspace, Salesforce, Zoom, Slack, and more. It continuously monitors these platforms for security issues, configuration risks, and user activity.
Absolutely. Qualys SSPM maps SaaS configurations to compliance frameworks like HIPAA, GDPR, and ISO 27001. It helps you identify non-compliant settings and generate reports to support audits.
Yes. Qualys continuously evaluates supported SaaS application configurations and posture so teams can identify changes that create security or compliance risk.
No traditional endpoint agent is installed inside the SaaS application. SSPM uses supported SaaS and identity integrations to collect configuration and security context.
Yes. Qualys provides guided and supported automated remediation capabilities for selected SaaS findings. Available actions depend on the connected SaaS application and issue type.
SSPM focuses on preventive SaaS security such as configuration posture, permissions, and compliance. SaaS Detection & Response combines that posture context with broader SaaS discovery, identity, data exposure, and security signals. —
Qualys SSPM gives full visibility into SaaS settings, user permissions, sharing configurations, activity logs, and compliance posture. This helps security teams understand risks and act faster to fix them.