Leveraging a policy engine, notifications are sent to specific first responders on operations teams responsible for priority assets requiring remediation
Multiple intervals can be set for event notification, matching them to criticality levels, so that alerts for the most important events will be triggered right away, and on the other extreme, low level incidents are communicated once a day, or once a week
Alerts can be sent to people who are not authorized users of Qualys services but who nonetheless should be aware about urgent vulnerabilities or other important issues
Alert rules can be configured for common, general scenarios, or specific ones, and for multiple conditions affecting a variety of assets and elements
Security teams are freed from the delays and burdens of waiting for scheduled scanning windows and from sifting through long reports
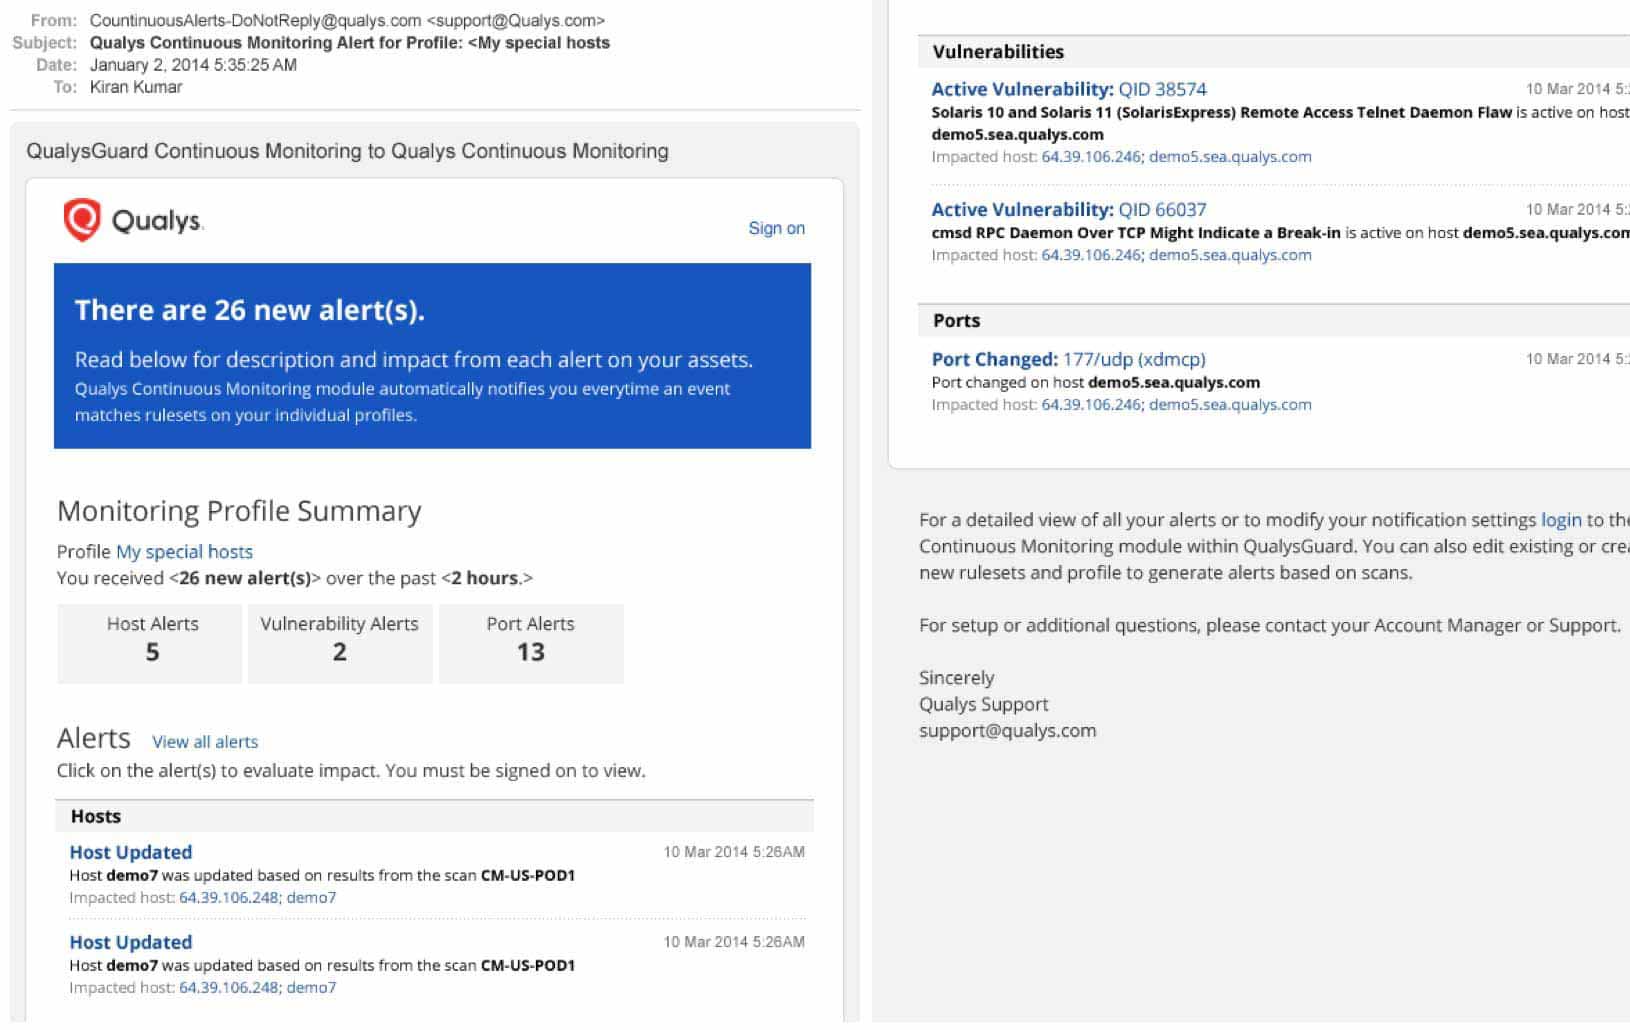
Email notifications display the number of new alerts for each category in your selected timeframe. Alerts are also grouped by category. For each alert, you will see the impacted host’s IP address and hostname as well as other event specific details, such as the vulnerability detected, software added or open ports.
Using the Qualys CM API (application programming interface), you can integrate Qualys CM alerts with your Security Information and Event Management (SIEM) solutions