Our CSPM tool helps you continuously discover, monitor, and analyze your cloud assets for misconfigurations and non-standard deployments so you can take rapid and appropriate actions.
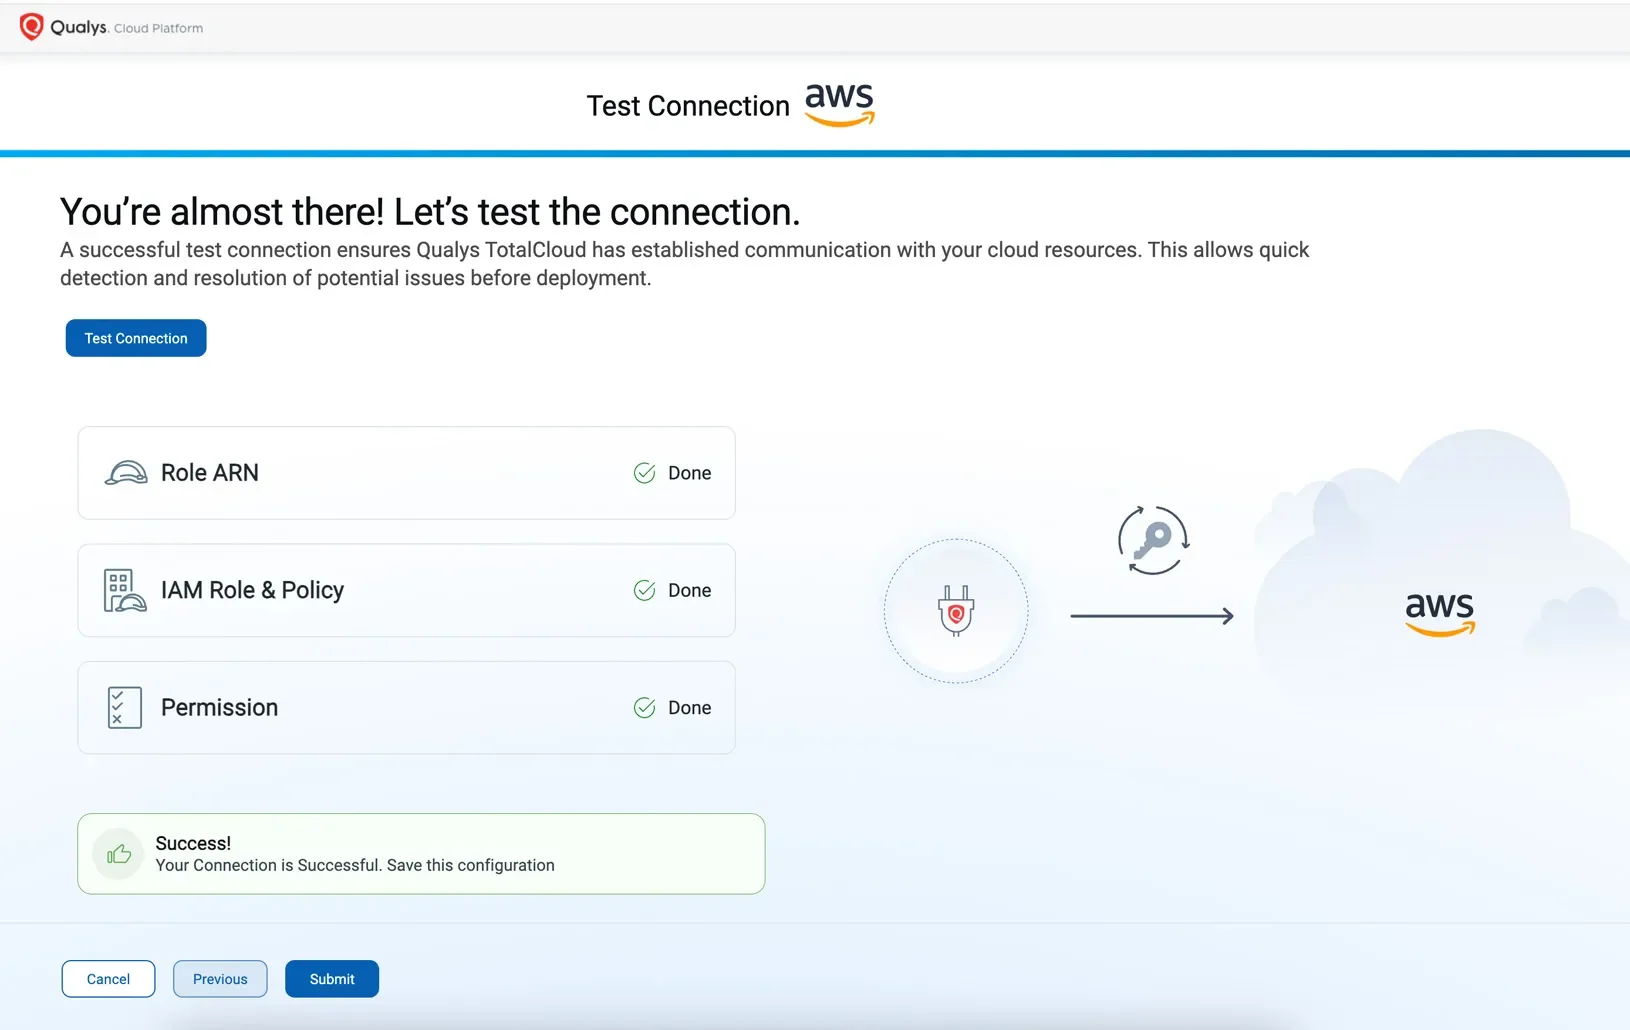
Seamless 3-Step Onboarding
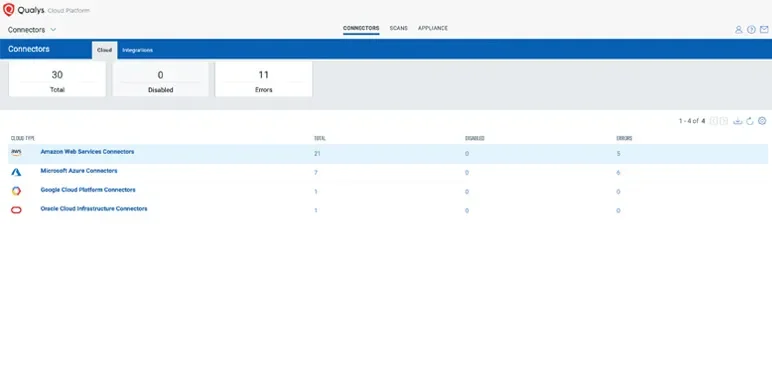
Set up in minutes without deploying agents. CSPM collects data from your accounts using the cloud providers’ APIs without disrupting your workloads. The inventory is built instantly with detailed metadata, relationship mapping and analysis begin as soon as data flows in.
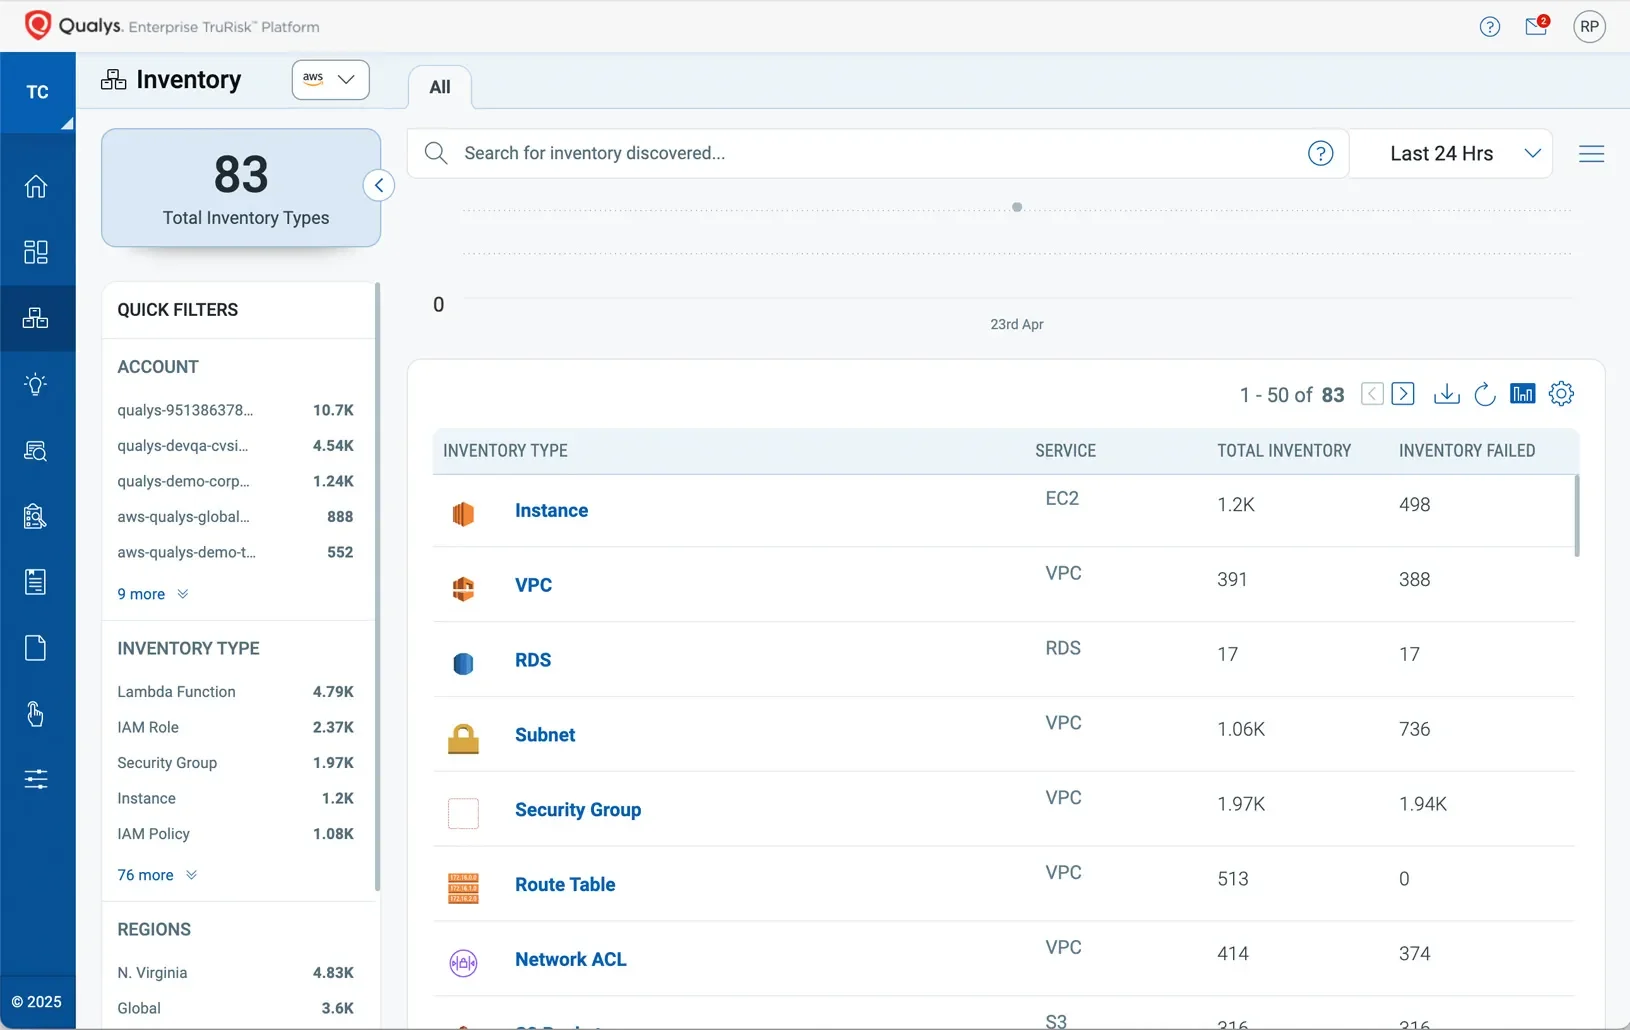
Unified Multi-Cloud Visibility
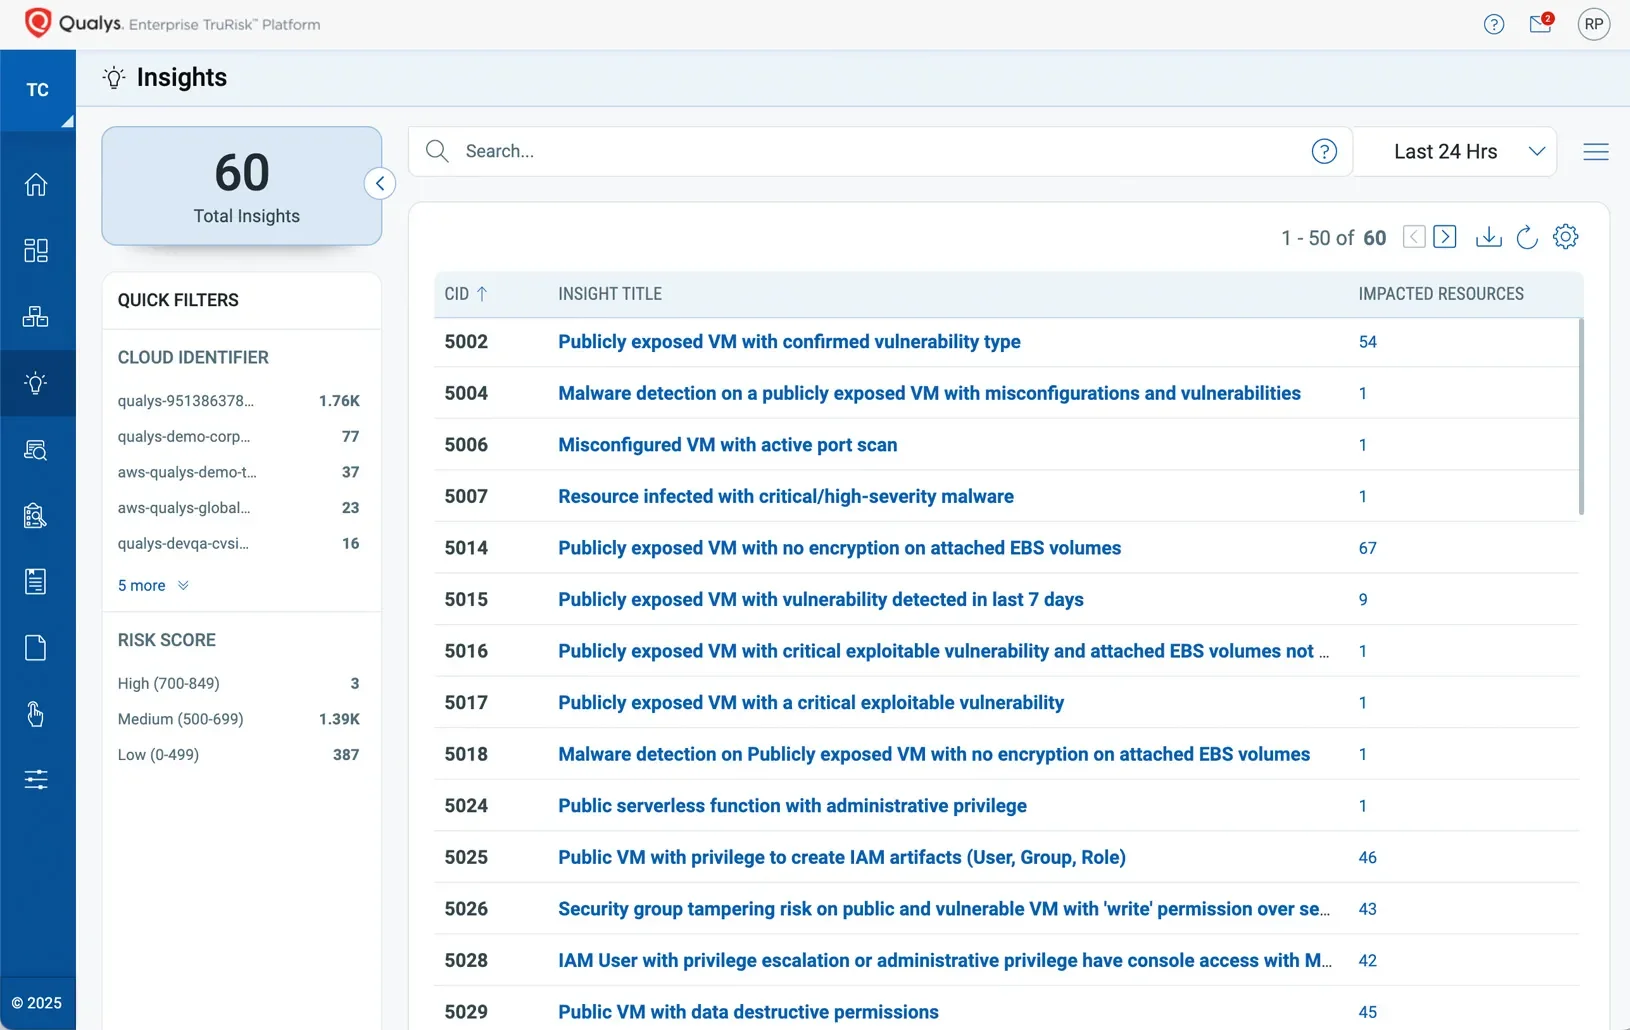
Prioritize Risk with TruRisk Insights
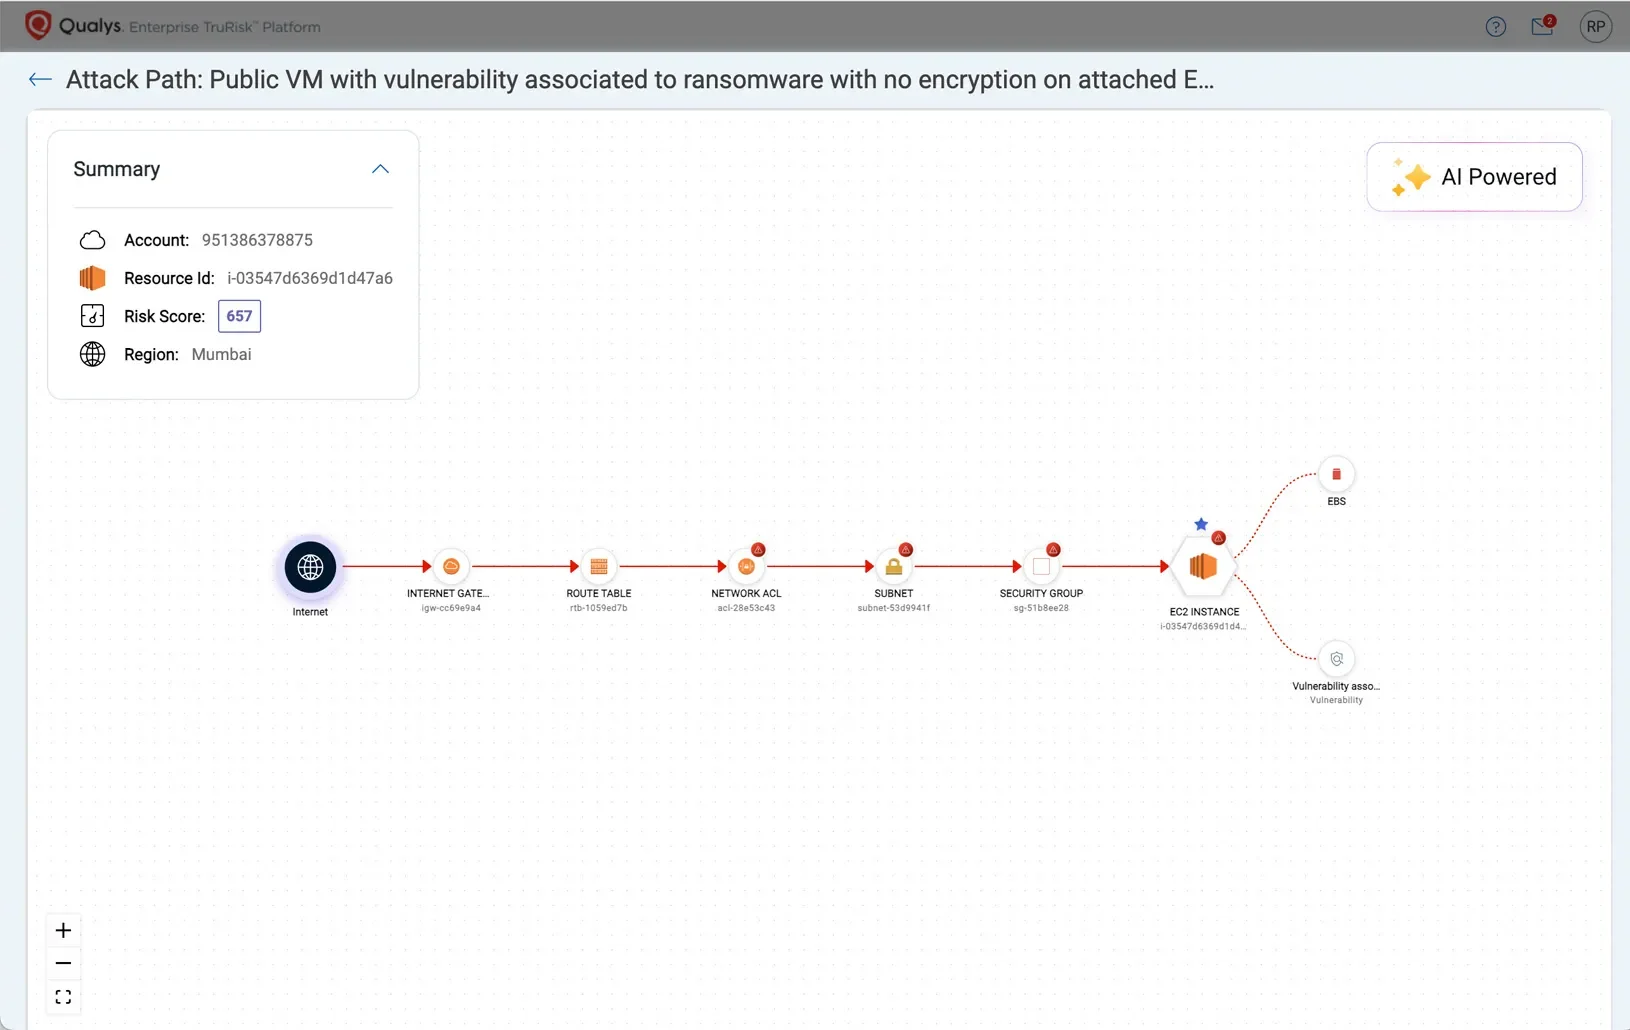
Visualize Risk with Attack Path
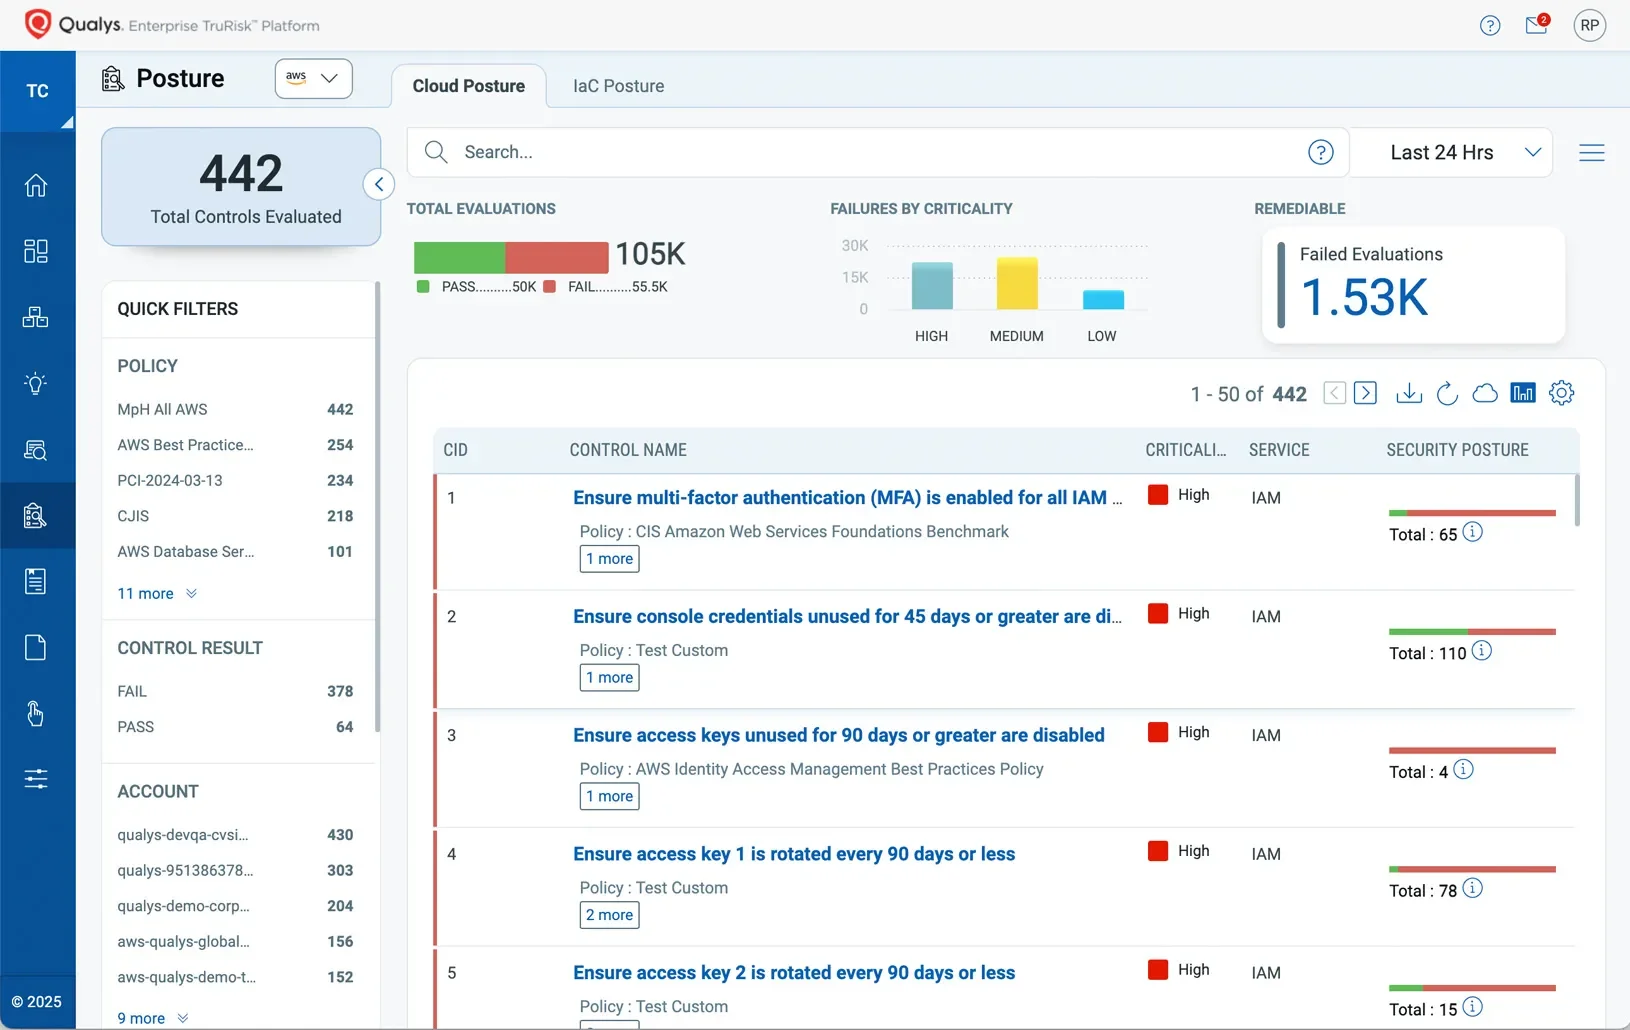
Ensure Compliance Resiliency with Over 40+ Mandates

Deploying Qualys CDR for AWS and Azure with just a few clicks, in a matter of minutes, across multiple AWS and Azure subscriptions, was a game changer for our security team. We have a complex environment with many controls, and TotalCloud team worked with us on integration with existing solutions including Secure Web Gateways and integrated SIEM. With their engineering team, together made sure all the security finds were tightly integrated with our SIEM platform. I have rarely seen this level of competency and engagement effort from a vendor.
Qualys is enhancing its widely used platform to deliver visibility, context, speed, automation, and orchestration in a comprehensive solution to help organizations scale their security and compliance programs for modern software development. Qualys TotalCloud incorporates security into development workflows, enabling them to release secure, reliable code, while giving security teams the control and visibility they need to manage risk by reducing their attack exposure and rapidly responding to threats.
The Qualys approach [to runtime security] empowers security to follow the container image with built-in instrumentation, enabling visibility and behavior enforcement for running containers across all types of container infrastructure.

Run continuous security checks on your cloud assets and resources with 1000+ out-of-the-box security controls across the cloud to identify resource misconfigurations.
Get complete coverage of CIS foundation benchmarks as well as Qualys best practices and architecture checks, including a breakdown of every control’s security posture, threat inventory at-a-glance, and clear steps to drive remediation.
Supports over 40 compliance mandates such as PCI DSS, HIPAA, NIST CSF, and GDPR. Continuously monitor compliance with versatile reporting and CIS benchmarks.
Instantly improve compliance scores across over 50 high-visibility controls with one click remediations for misconfigurations.
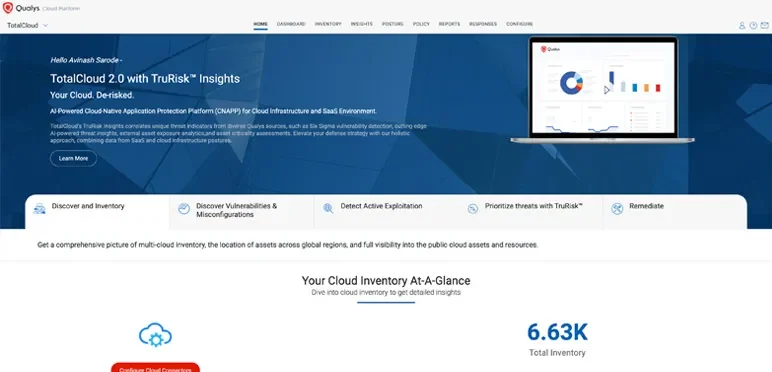
Empower your security team to measure, communicate, and eliminate risk with a single view of inventory to continuously discover resources across your multi-cloud environments.
Introducing TotalCloud™ with TruRisk Insights
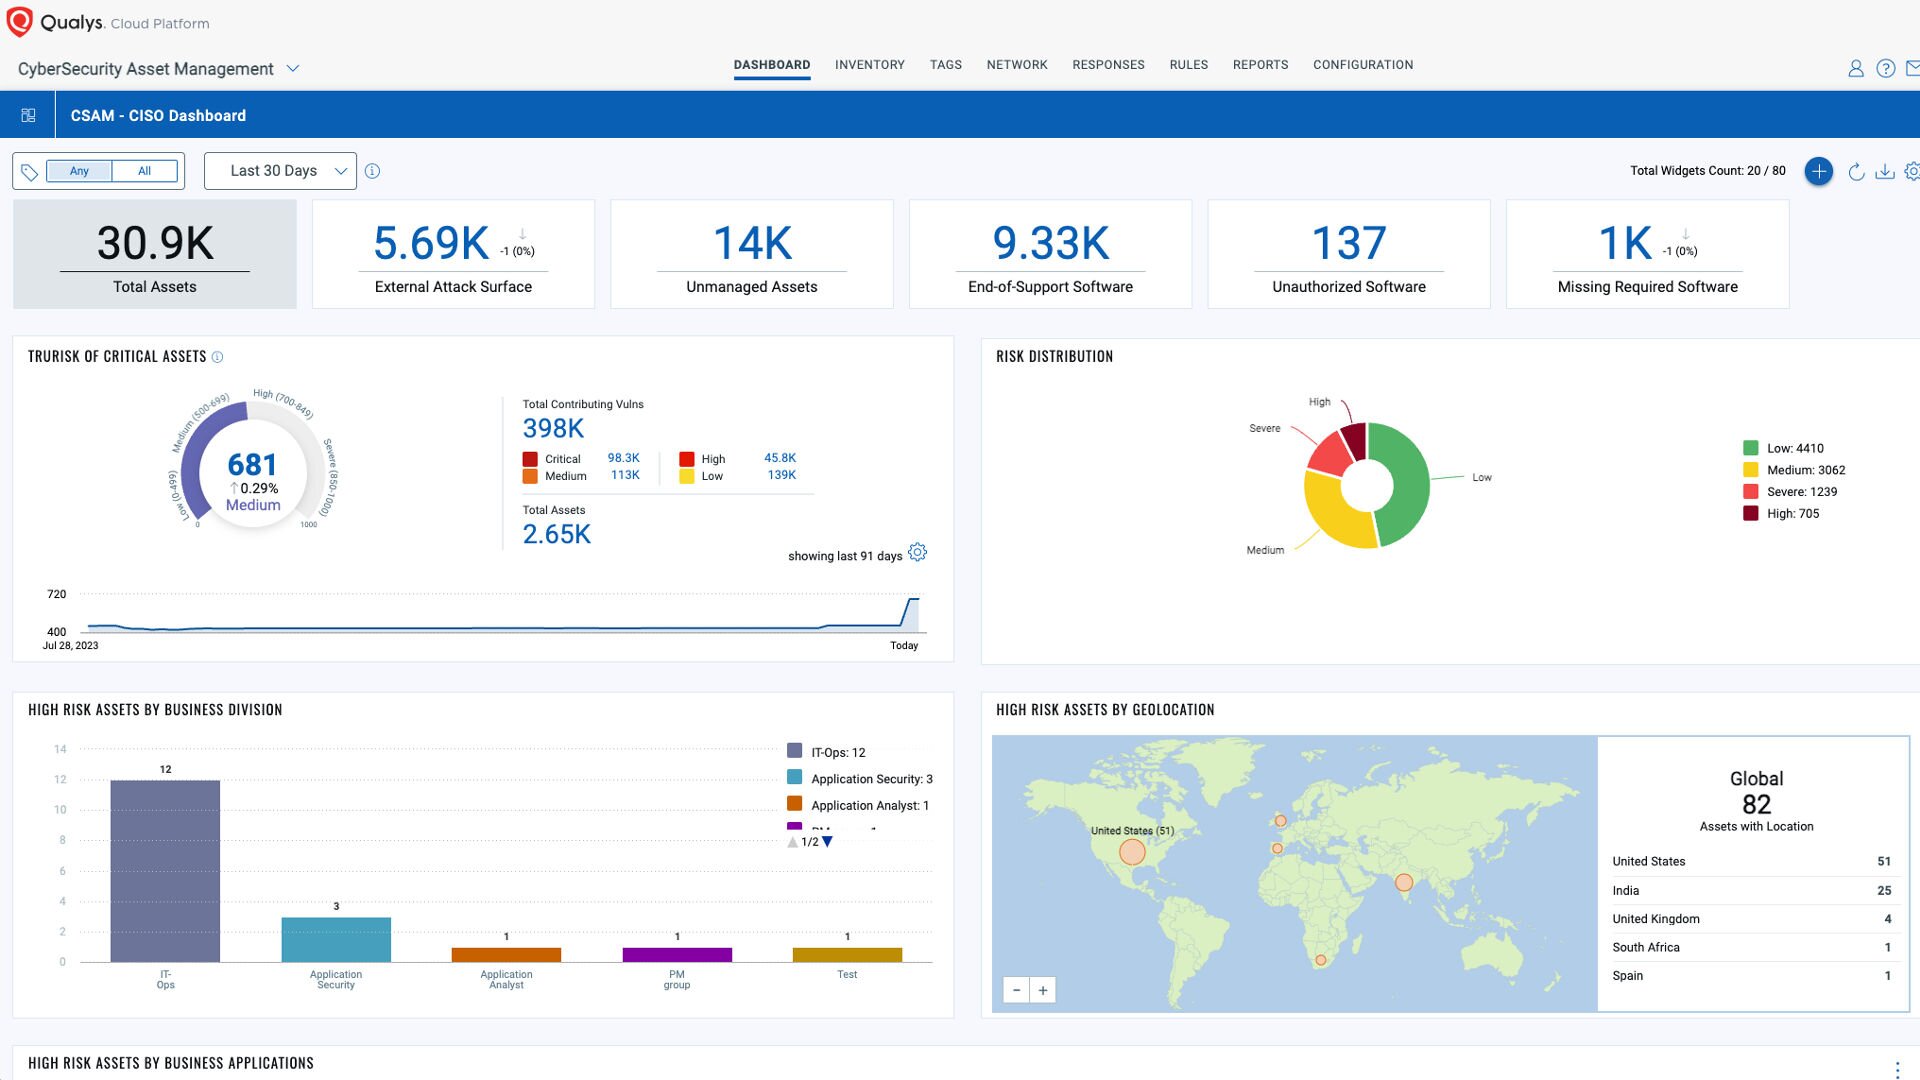
The Enterprise TruRisk Platform provides you with a unified view of your entire cyber risk posture so you can efficiently aggregate and measure all Qualys & non-Qualys risk factors in a unified view, communicate cyber risk with context to your business, and go beyond patching to eliminate the risk that threatens the business in any area of your attack surface.

CSPM continuously evaluates cloud resources and configurations for misconfigurations, policy violations, compliance gaps, and other control-plane security risks. It helps cloud and security teams understand whether their cloud environment is configured according to organizational and industry security requirements.
Qualys maps cloud posture to widely used security benchmarks and regulatory frameworks such as CIS, NIST, PCI DSS, HIPAA, ISO 27001, and other supported industry and regional requirements. Continuous assessment helps teams identify drift and maintain audit-ready evidence as cloud resources change.
Qualys CSPM supports major cloud platforms including AWS, Microsoft Azure, Google Cloud, and OCI. Coverage spans supported cloud services across compute, storage, networking, databases, identity and access, Kubernetes, serverless, logging, encryption, and other managed services so teams can evaluate posture beyond only virtual machines.
CSPM can identify risky cloud conditions such as public exposure, overly permissive network access, insecure storage, weak logging or encryption settings, policy violations, and other deviations from approved cloud-security baselines.
TotalCloud enriches posture findings with vulnerability, exposure, identity, threat, and asset context. This helps teams focus on misconfigurations that materially increase attackability or business risk instead of treating every failed control as equally urgent.
Yes. TotalCloud can correlate posture weaknesses with other risk factors to visualize attack paths and highlight combinations of issues that create meaningful routes to compromise.
CSPM identifies configurations that create unnecessary exposure, while TotalCloud adds attack-path and risk context to show which findings most contribute to exploitable risk. Fixing those conditions helps shrink the reachable attack surface.
Supported misconfigurations can be addressed through guided remediation, workflow integration, and Qualys Flow automation. Organizations can choose manual, approval-based, or automated remediation approaches according to their change-control requirements.
CSPM evaluates infrastructure configuration and posture. Vulnerabilities and activity inside VMs, containers, and other workloads are addressed by workload and runtime-security capabilities. TotalCloud correlates these findings so posture and workload risk can be evaluated together.
IaC security evaluates intended infrastructure before deployment, while CSPM evaluates the actual environment after deployment. Using both helps identify insecure infrastructure earlier and detect drift or unapproved changes after resources are created. —