While CrowdStrike’s agent-focused coverage limits it to managed hosts, Qualys FlexScan™ provides real-time, blind-spot-free discovery across all cloud accounts, containers, serverless assets, and on-prem infrastructure.

Complete coverage: Unified inventory for AWS, Azure, GCP, OCI, on-prem, and SaaS in a single pane.
Zero-Touch Discovery: Identifies shadow IT, unmanaged assets, and risky exposures automatically.
Integrated Asset Context: Correlates resources, exposures, and workload details for maximum context.
Narrow Discovery: Limited agentless support; most visibility only where agents are deployed.
Gaps in Serverless & PaaS: Misses cloud-native and unmanaged resources.
Fragmented View: Siloed visibility makes multi-cloud risk management harder.
Complete coverage: Unified inventory for AWS, Azure, GCP, OCI, on-prem, and SaaS in a single pane.
Zero-Touch Discovery: Identifies shadow IT, unmanaged assets, and risky exposures automatically.
Integrated Asset Context: Correlates resources, exposures, and workload details for maximum context.
Narrow Discovery: Limited agentless support; most visibility only where agents are deployed.
Gaps in Serverless & PaaS: Misses cloud-native and unmanaged resources.
Fragmented View: Siloed visibility makes multi-cloud risk management harder.
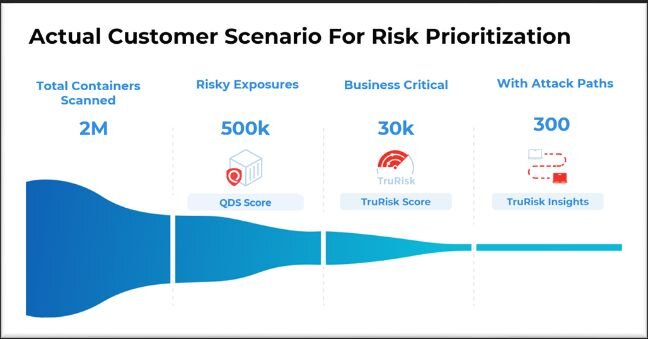
Qualys TruRisk™ analyzes exploitability, business context, exposure, and upstream/downstream relationships to drive decision-making with business-aligned risk reduction.
Business Impact Scoring: Translates vulnerabilities into financial and operational risk.
Noise Elimination: AI-powered ranking filters out the noise so teams can act on what matters most.
Attack Path Analysis: Visualizes how threats could propagate, mapping blast radius.
Generic CVSS: Can't link exposures to business risk or quantify impact.
Excessive Alerts: Triage by severity, not risk, slowing response and overloading teams.
Limited Risk Context: Focus remains on active endpoint threats rather than latent cloud risk.
Business Impact Scoring: Translates vulnerabilities into financial and operational risk.
Noise Elimination: AI-powered ranking filters out the noise so teams can act on what matters most.
Attack Path Analysis: Visualizes how threats could propagate, mapping blast radius.
Generic CVSS: Can't link exposures to business risk or quantify impact.
Excessive Alerts: Triage by severity, not risk, slowing response and overloading teams.
Limited Risk Context: Focus remains on active endpoint threats rather than latent cloud risk.
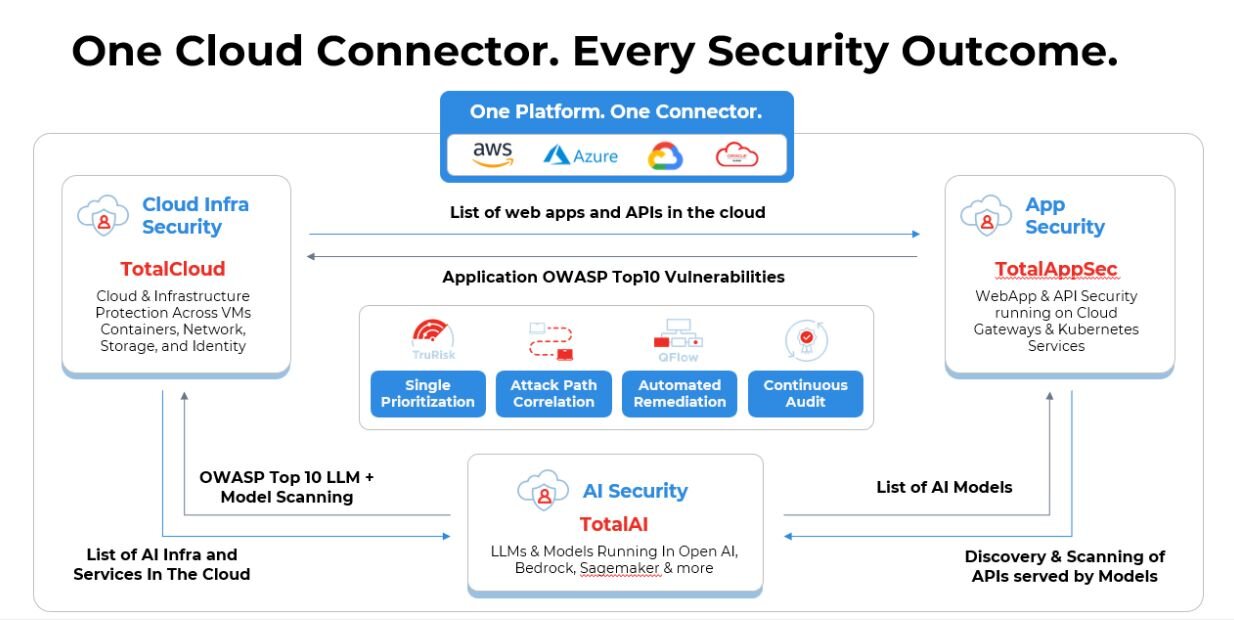
TotalCloud’s QFlow™ enables remediation through no-code/low-code workflows, from instant patching to quarantine to remove human bottlenecks.
Autonomous no-code remediation at scale: with 300+ workflows and ITSM integration
AI-driven patching and runtime validation: fixes real exploitable vulnerabilities, not noise
Code-to-cloud risk correlation: eliminates attack paths across applications, workloads, and identities
Focuses on detection, requiring manual or external remediation workflows
Limited native code-level remediation within CI CD pipelines
Lacks unified CNAPP correlation across posture, identity, and application layers
Autonomous no-code remediation at scale: with 300+ workflows and ITSM integration
AI-driven patching and runtime validation: fixes real exploitable vulnerabilities, not noise
Code-to-cloud risk correlation: eliminates attack paths across applications, workloads, and identities
Focuses on detection, requiring manual or external remediation workflows
Limited native code-level remediation within CI CD pipelines
Lacks unified CNAPP correlation across posture, identity, and application layers
Takeaway: For Glasswing-style threats, detection alone is insufficient. Organizations must validate exploitability and remediate risks at the same speed as attackers operate.
Regulated industries need real, sustainable audit readiness. Qualys streamlines mapping to 40+ mandates while collecting evidence continuously to eliminate audit fatigue and manual work.
Policy Coverage: Out-of-the-box controls for PCI DSS 4.0, NIST 800-53, HIPAA, ISO 27001, and more.
Continuous Auditing: Automated, real-time evidence collection and reporting.
Drift Detection & Response: Instantly flags compliance violations before they become findings.
Manual Mapping: No built-in compliance content for cloud.
Slow Auditing: Lacks workflows for evidence collection and reporting.
Limited to Endpoints: Can't show full hybrid compliance posture.
Policy Coverage: Out-of-the-box controls for PCI DSS 4.0, NIST 800-53, HIPAA, ISO 27001, and more.
Continuous Auditing: Automated, real-time evidence collection and reporting.
Drift Detection & Response: Instantly flags compliance violations before they become findings.
Manual Mapping: No built-in compliance content for cloud.
Slow Auditing: Lacks workflows for evidence collection and reporting.
Limited to Endpoints: Can't show full hybrid compliance posture.
Qualys extends coverage to DevOps, containers, APIs, and SaaS to offer context and protection that EDR-centric platforms like CrowdStrike can’t reach.
TotalAppSec: Dynamic application and API security testing within the same platform.
KSPM & Container Security: Deep protection for Kubernetes, microservices, and ephemeral workloads.
SSPM: Full SaaS posture management for environments like Microsoft 365 and Salesforce.
No Native Application Security: Must use third-party tools for DAST, API, and SaaS visibility.
Limited Cloud Runtime Coverage: Traditional EDR, not cloud-native runtime defense.
Gaps in Container Only Deployments: Agentless, serverless, and CI/CD risks persist.
TotalAppSec: Dynamic application and API security testing within the same platform.
KSPM & Container Security: Deep protection for Kubernetes, microservices, and ephemeral workloads.
SSPM: Full SaaS posture management for environments like Microsoft 365 and Salesforce.
No Native Application Security: Must use third-party tools for DAST, API, and SaaS visibility.
Limited Cloud Runtime Coverage: Traditional EDR, not cloud-native runtime defense.
Gaps in Container Only Deployments: Agentless, serverless, and CI/CD risks persist.
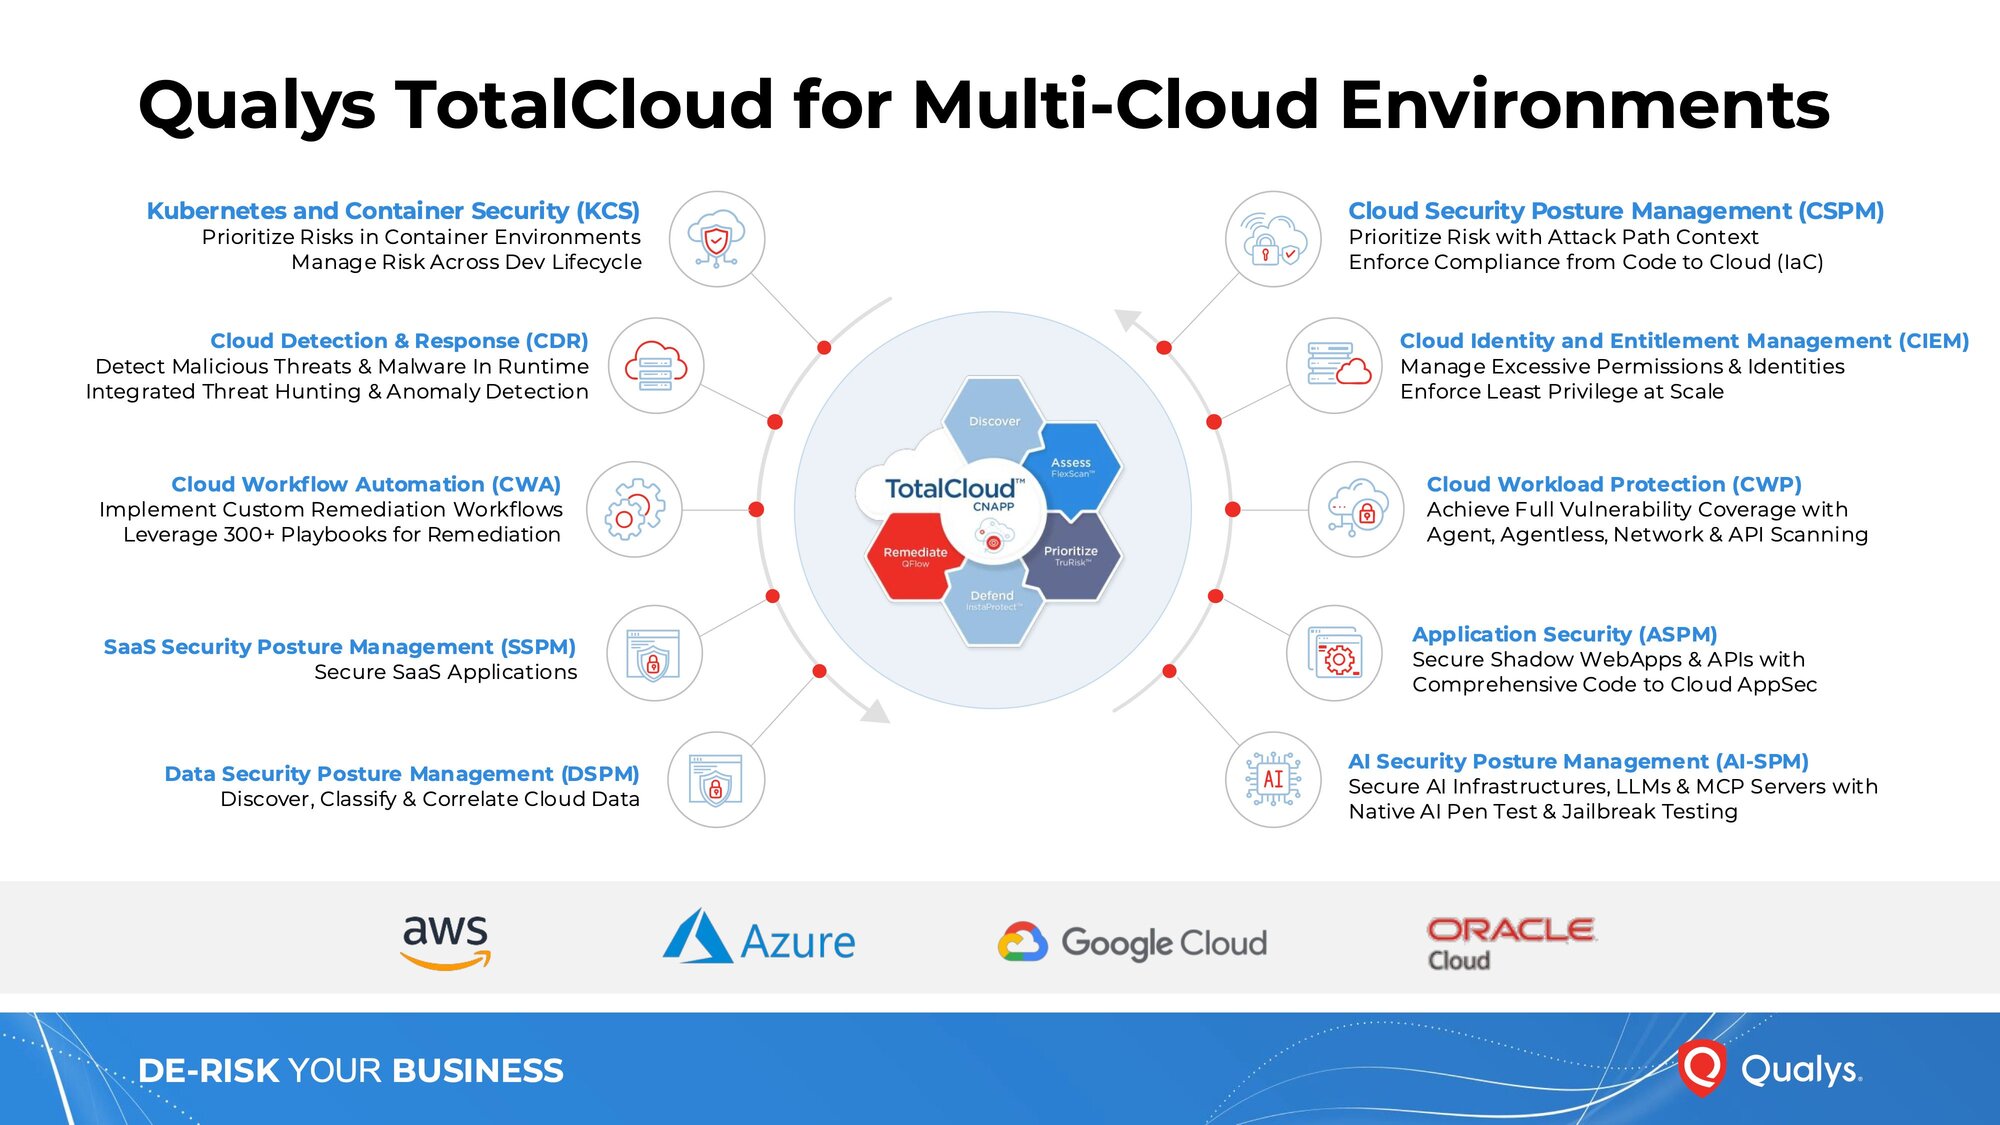
Security, risk, and cloud teams break through silos, managing policies, detection, and response consistently across assets—physical, virtual, and cloud-native.
Policy-as-Code: Automates enforcement and rapid response across public and private clouds.
Multicloud Mastery: Out-of-the-box support for AWS, Azure, GCP, OCI, and more.
Unified Dashboard: Full-stack monitoring in one platform; faster, smarter operations.
Siloed Control: No policy-based automation across hybrid estates.
Cloud Platform Gaps: Requires separate tools for deep multi-cloud management.
Manual Operations: More operational overhead, less scale.
Policy-as-Code: Automates enforcement and rapid response across public and private clouds.
Multicloud Mastery: Out-of-the-box support for AWS, Azure, GCP, OCI, and more.
Unified Dashboard: Full-stack monitoring in one platform; faster, smarter operations.
Siloed Control: No policy-based automation across hybrid estates.
Cloud Platform Gaps: Requires separate tools for deep multi-cloud management.
Manual Operations: More operational overhead, less scale.
Detailed Capability Breakdown
Deployment and Architecture
Agentless and agent-based, full hybrid support.
Rapid onboarding and comprehensive coverage.
Unified platform reduces operational complexity.
Limited agentless scanning coverage, mainly managed hosts.
Architectural silos increase deployment complexity.
Gaps in dynamic cloud and ephemeral environments.
Agentless and agent-based, full hybrid support.
Rapid onboarding and comprehensive coverage.
Unified platform reduces operational complexity.
Limited agentless scanning coverage, mainly managed hosts.
Architectural silos increase deployment complexity.
Gaps in dynamic cloud and ephemeral environments.
Correlates code, image, and runtime exposure to reduce friction between Dev and Sec
Full Software Composition Analysis (SCA) across 9+ languages and secrets scanning in code repositories, images, AMIs, and registries
Customizable policy-as-code and secret detection with CI/CD-native enforcement
Provides IaC and code visibility primarily through posture and workload lenses
Focuses on detection and visibility rather than prioritized developer workflows
Requires additional tooling to enforce policy and orchestrate remediation across the SDLC
Correlates code, image, and runtime exposure to reduce friction between Dev and Sec
Full Software Composition Analysis (SCA) across 9+ languages and secrets scanning in code repositories, images, AMIs, and registries
Customizable policy-as-code and secret detection with CI/CD-native enforcement
Provides IaC and code visibility primarily through posture and workload lenses
Focuses on detection and visibility rather than prioritized developer workflows
Requires additional tooling to enforce policy and orchestrate remediation across the SDLC
Qualys TotalCloud embeds risk-based security directly into the SDLC. By applying TruRisk scoring across SCA, IaC, images, and runtime, developers see what is truly exploitable—not just long lists of vulnerabilities. Customizable policies and secret detectors allow organizations to enforce guardrails from code through production, while maintaining flexibility for different teams and environments.
Takeaway: Qualys creates DevSecOps harmony by aligning developers and security teams around prioritized, actionable risk from code to cloud.*
Uses deep learning based packet inspection of network and cloud traffic to catch novel zero-day malware and threats across
Integrates runtime protection using eBPF for cloud/container workloads for FIM and threat response
Prioritizes threats using business impact and exploitability context enabling prioritization across thousands of signals
Excels at high-fidelity behavioral detection on endpoints and managed workloads
Generates alerts based on host-level activity and event severity
Provides limited exposure context beyond the affected workload
Uses deep learning based packet inspection of network and cloud traffic to catch novel zero-day malware and threats across
Integrates runtime protection using eBPF for cloud/container workloads for FIM and threat response
Prioritizes threats using business impact and exploitability context enabling prioritization across thousands of signals
Excels at high-fidelity behavioral detection on endpoints and managed workloads
Generates alerts based on host-level activity and event severity
Provides limited exposure context beyond the affected workload
Qualys TotalCloud delivers risk-minded Cloud Detection & Response by linking runtime activity with broader exposure context across cloud infrastructure, identities, applications, and data. Deep-learning detections combined with agentless and eBPF runtime telemetry surface active exploitation and novel threats, then prioritize them based on real attack paths and business impact—not alert volume alone.
CrowdStrike is a leader in behavioral runtime detection on managed workloads. While highly effective for identifying active threats, prioritization is centered on host-level signals, which may provide less context across interconnected cloud resources.
Takeaway: Qualys detects novel zero-day threats and prioritizes by business context; CrowdStrike emphasizes workload-level behavioral detection.
.