Modernize, Secure, and Simplify Compliance with the Enterprise TruRisk™ Platform
State and local agencies are navigating a perfect storm: evolving cyber threats, legacy systems, critical infrastructure vulnerabilities, and tightening compliance demands — all while managing budget and staffing constraints.
This exclusive solution brief reveals how Qualys helps public sector organizations meet these challenges head-on. With deep alignment to NIST CSF 2.0 and other key regulatory frameworks, the Qualys Enterprise TruRisk Platform enables agencies to consolidate tools, eliminate audit fatigue, and strengthen cyber resilience — all from a single, unified platform.
What’s Inside
Practical roadmap to align with NIST CSF 2.0, NIST 800-171, HIPAA, FISMA, and other mandates
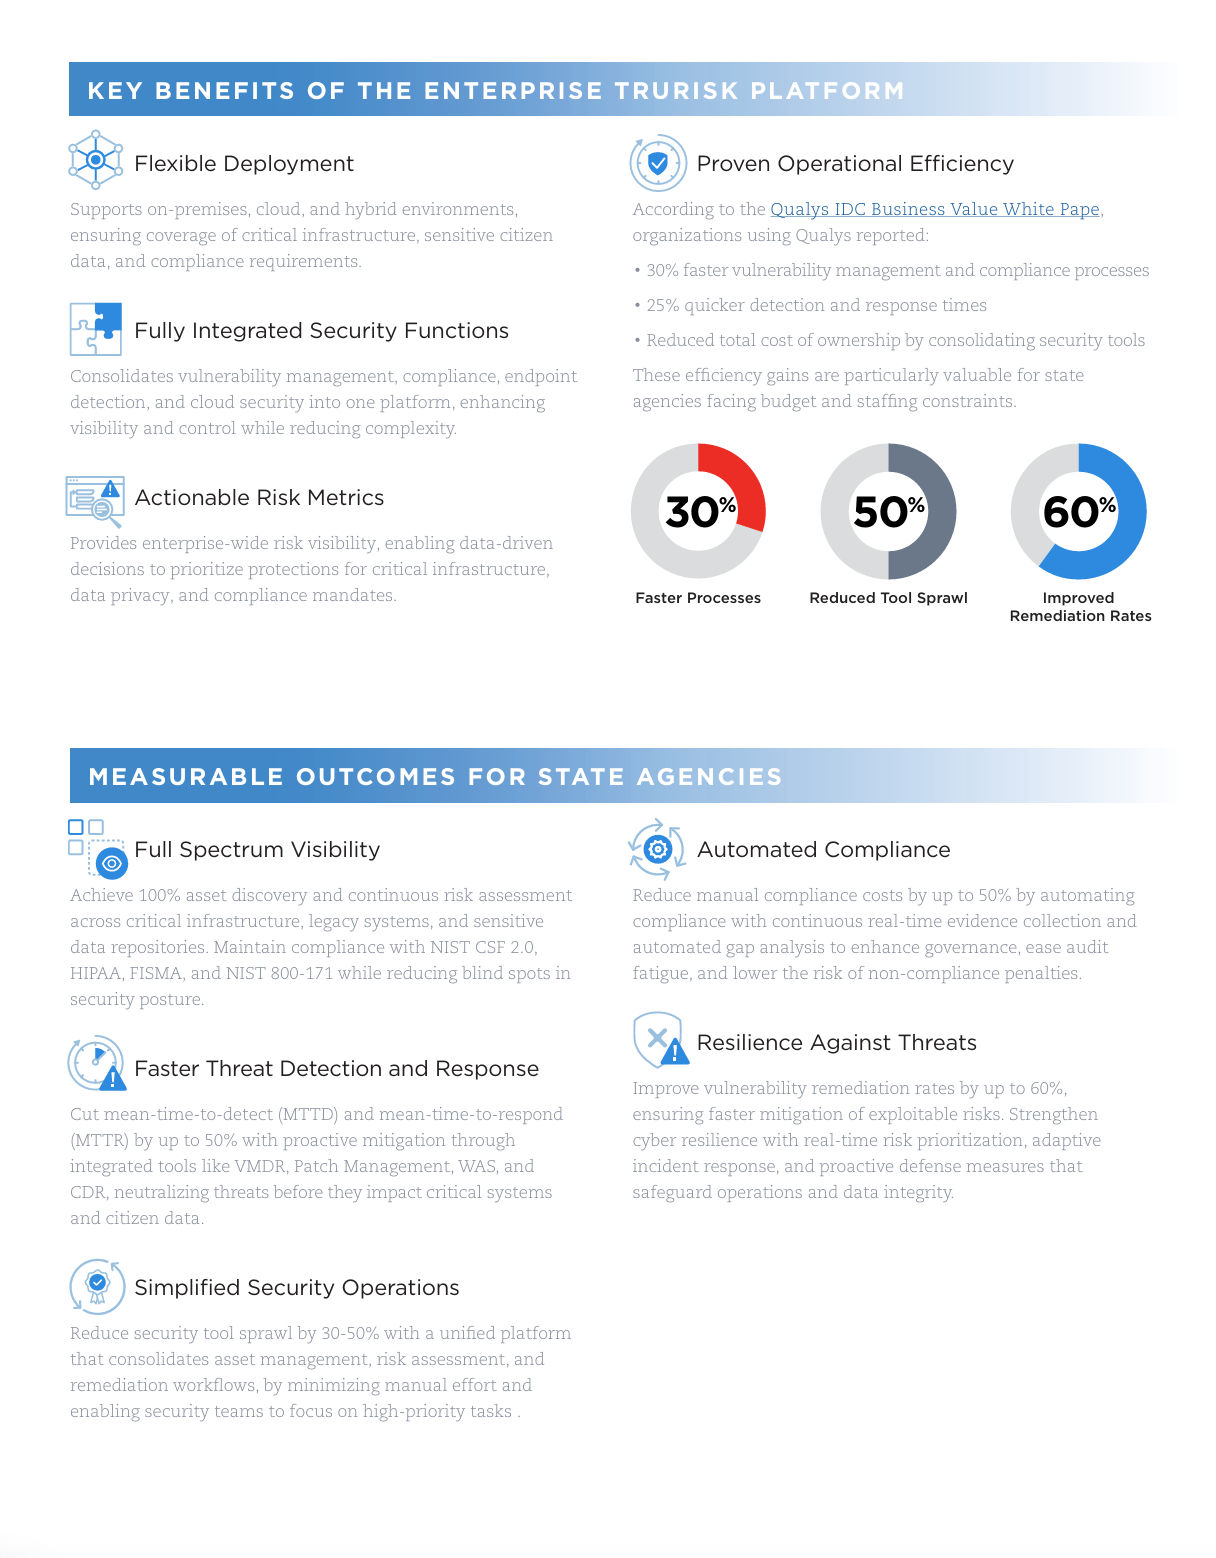
How Qualys reduces mean-time-to-detect and respond by up to 50% while improving remediation rates by 60%
Ways to achieve full visibility across on-prem, cloud, and legacy environments
Strategies for automating compliance workflows and minimizing manual effort
Real-world outcomes that help state governments modernize cybersecurity without expanding headcount
Why Read This Brief
Whether you're building a more resilient security program or trying to stay ahead of regulatory mandates, this resource will show you how to reduce complexity, improve response times, and make the most of every cybersecurity dollar.
Get started today — simplify compliance, reduce risk, and protect critical infrastructure with Qualys.