
Start Your 30-Day No-Cost Trial.
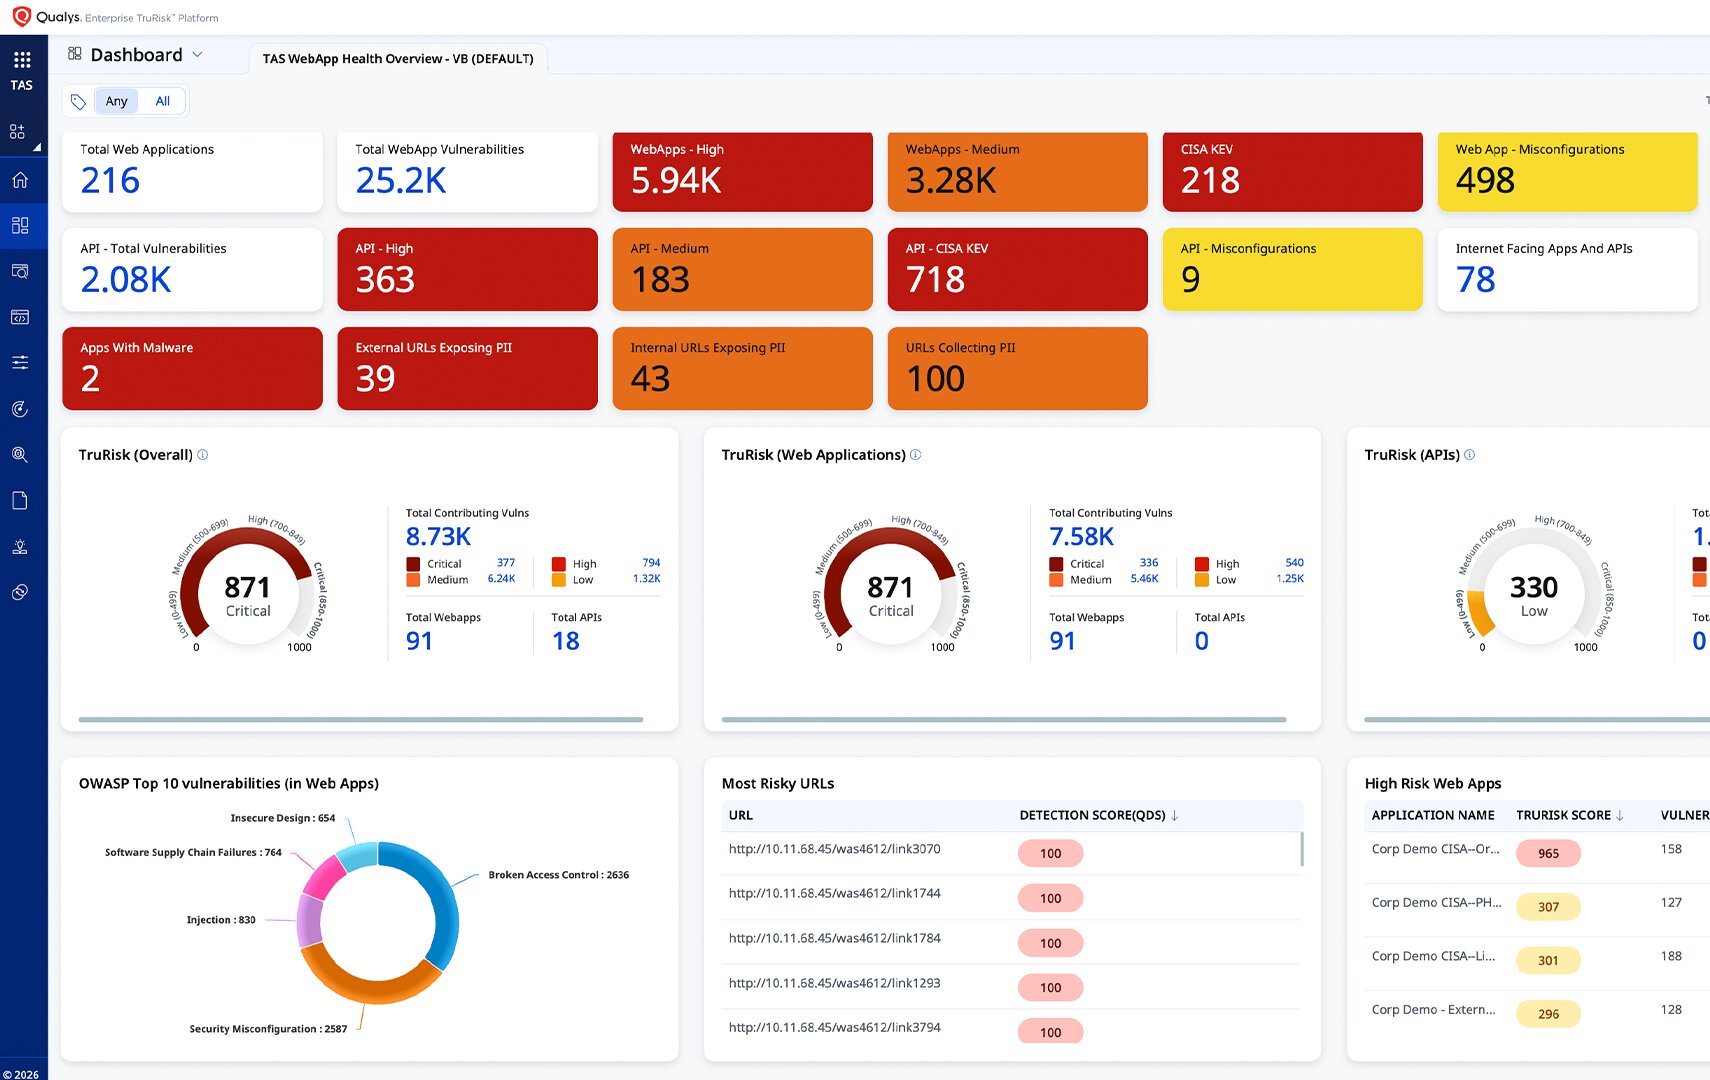
Qualys TotalAppSec replaces broken, fragmented AppSec with continuous application risk operations by unifying enterprise DAST, API Security Testing and Zero-Day Malware detection.
With your 30-day free-trial you can:
AI-Powered DAST
API Security Testing
Zero-Day Malware Detection
OWASP Top 10
OWASP API Top 10
CI/CD Integration
PCI DSS 4.0.1
GDPR Compliance
HIPAA Compliance
OpenAPI v3 Validation
BOLA
BFLA
BUA
Shadow API
AI-Powered AppSec
Jira Integration
ServiceNow Integration
Green Window Scheduling
Green Window Scheduling
Custom Signatures
Access Control Testing
Authenticated Scanning

TotalAppSec is an AI-powered unified application security platform that combines web application scanning, API security testing, and malware detection in a single solution — discovering and testing everything you own across web apps and APIs from one console.
TotalAppSec automatically discovers APIs and tests them against the OWASP API Top 10, including authentication bypass, injection flaws, and sensitive data exposure across REST and SOAP APIs, and validates implementations against OpenAPI v3 specifications.
Yes. TotalAppSec provides detection-level testing against the OWASP Top 10 for web applications and the OWASP API Top 10 for APIs, covering both from a single scan workflow.
AI-assisted scanning profiles each application before testing and directs scan effort toward the areas most likely to carry exploitable risk, cutting scan time without sacrificing coverage.
TotalAppSec uses deep learning-based detection to identify known and zero-day malware in web applications, continuously monitoring for malicious code injection, unauthorized modifications, and suspicious behavior patterns.
TotalAppSec uses Qualys TruRisk scoring, ranking findings by exploitability, business impact, and threat intelligence rather than severity scores alone — so you see what’s actually dangerous, not just what’s technically high-CVSS.
TotalAppSec integrates natively with Jenkins, Azure DevOps, and GitHub Actions for pre-deployment testing, and connects with Jira and ServiceNow for automated ticketing — supporting shift-left testing in the pipeline and shift-right remediation in production.
Yes. TotalAppSec is built for modern architectures — containers, microservices, and cloud-native deployments — alongside on-prem, multi-cloud, hybrid environments, and API gateways.
