Find misconfigurations, prioritize risk, and remediate automatically to avoid manual scrambling before the next audit.
Why Compliance Programs Fail Between Audits
Discovery is slow. Prioritization is guesswork. Remediation doesn't stick. Policy Audit fixes all three.

AI-powered Detection
Identify misconfiguration, automate evidence collection, and deliver actionable compliance insights.

Risk-Based Prioritization
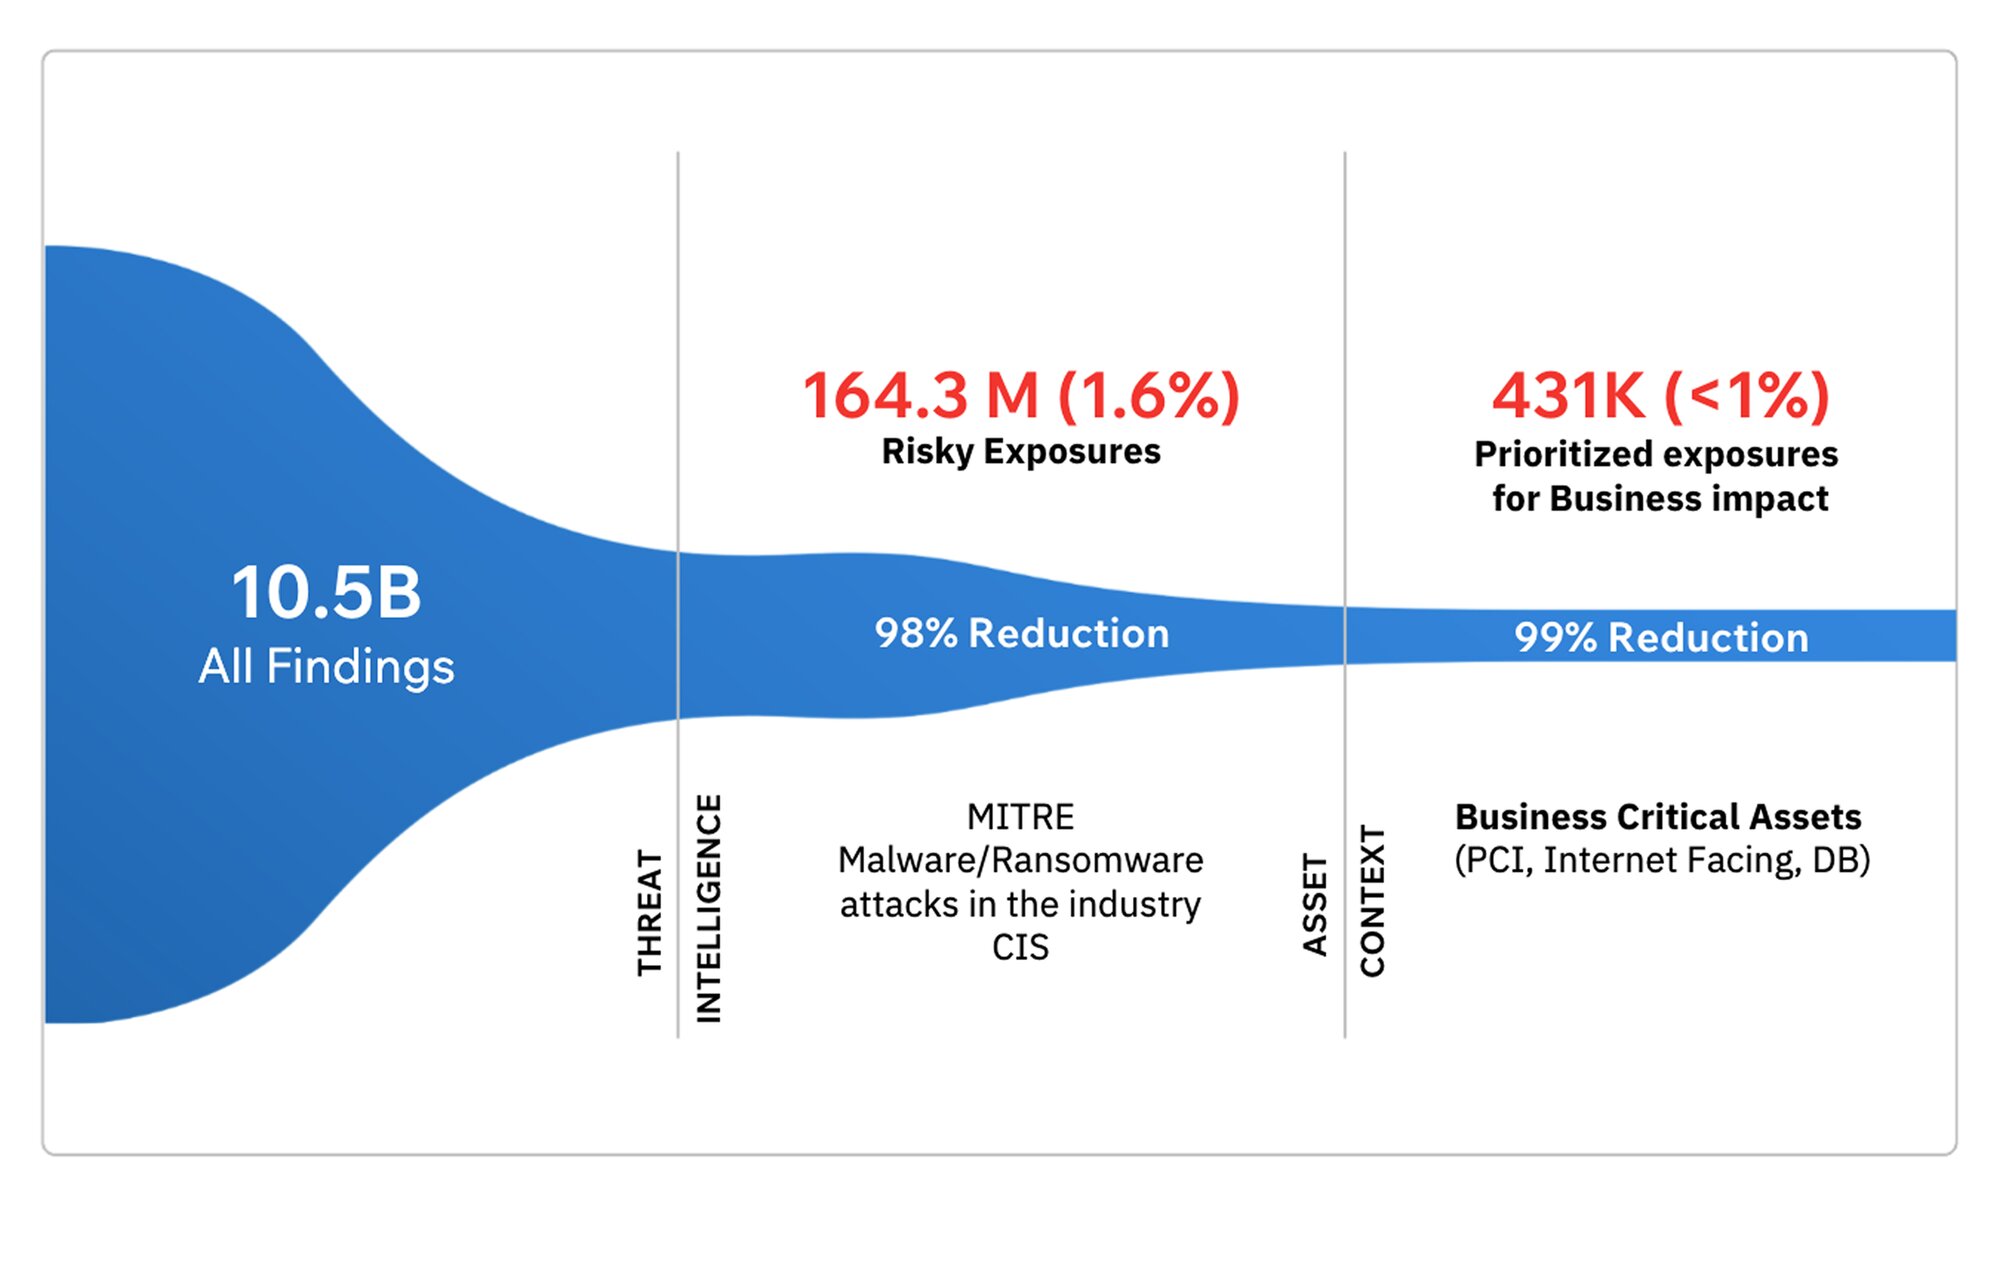
Eliminate compliance noise and prioritize exploitable, high impact findings.

Automated Remediation
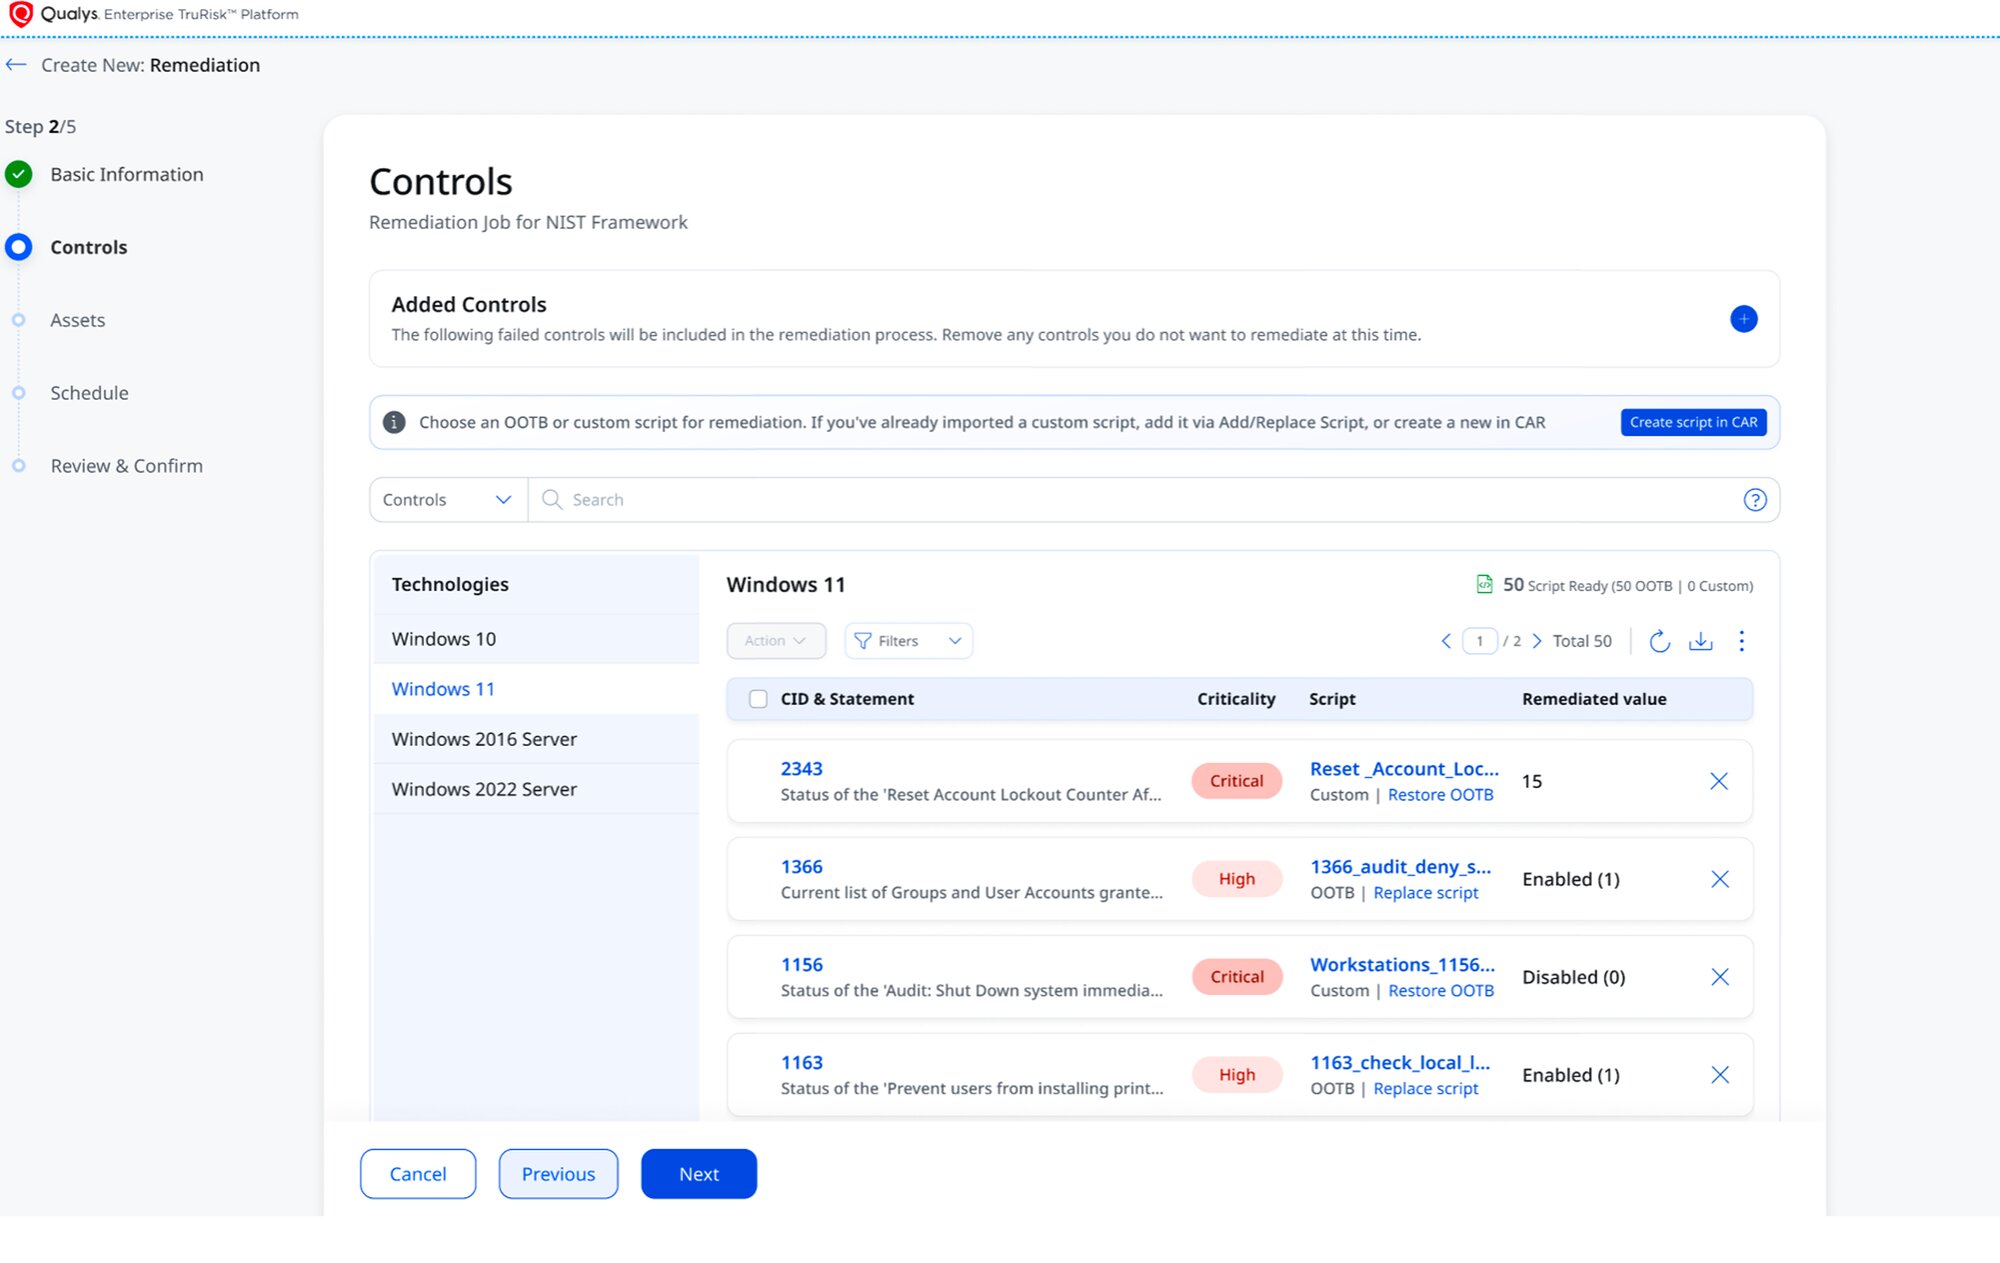
Fix failed controls at scale with Audit Fix to reduce gaps and audit risks
AI-Driven Compliance Readiness
Automate compliance checks, enforce security policies, and reduce risk with real-time monitoring and audit-ready reporting.
Introducing TotalCloud™ with TruRisk Insights
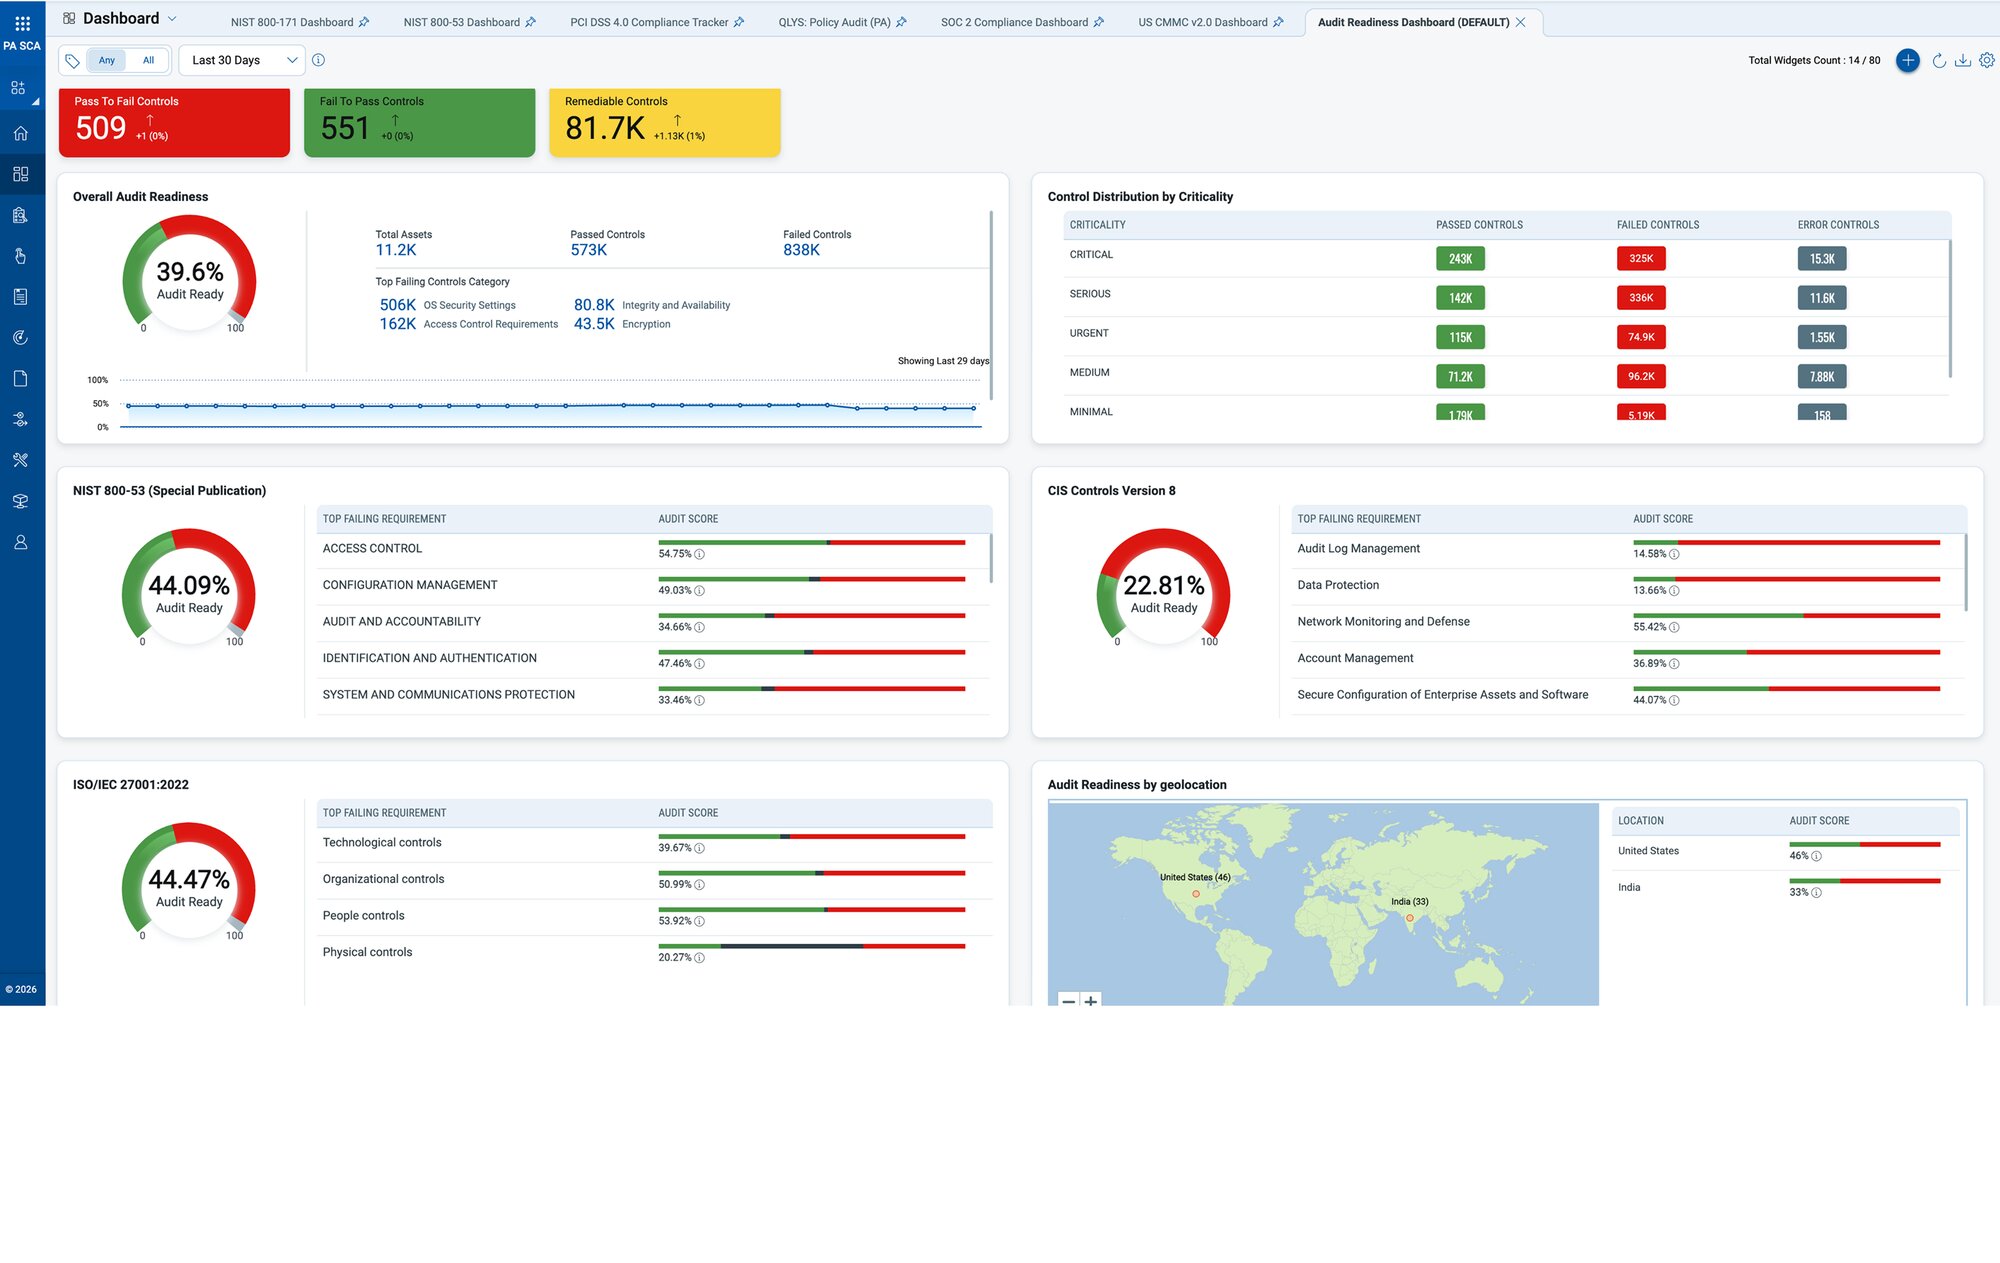
Automated evidence collection and real-time reporting eliminate manual effort.
Gaps surfaced and closed before auditors ever find them.
Zero manual prep with evidence and reports always ready.
From finding misconfigurations to staying continuously audit-ready — Policy Audit turns visibility into measurable outcomes.
One Workflow. Five Steps. Continuous Audit Readiness.
Policy Audit connects discovery, prioritization, remediation, reporting, and monitoring into a single closed loop — so audit readiness isn't manual process every cycle. It's always on.
Step 1: Discover everything that matters
Continuously identify servers, middleware, databases, and software across environments, automatically classifying critical assets and uncovering compliance gaps in real time.
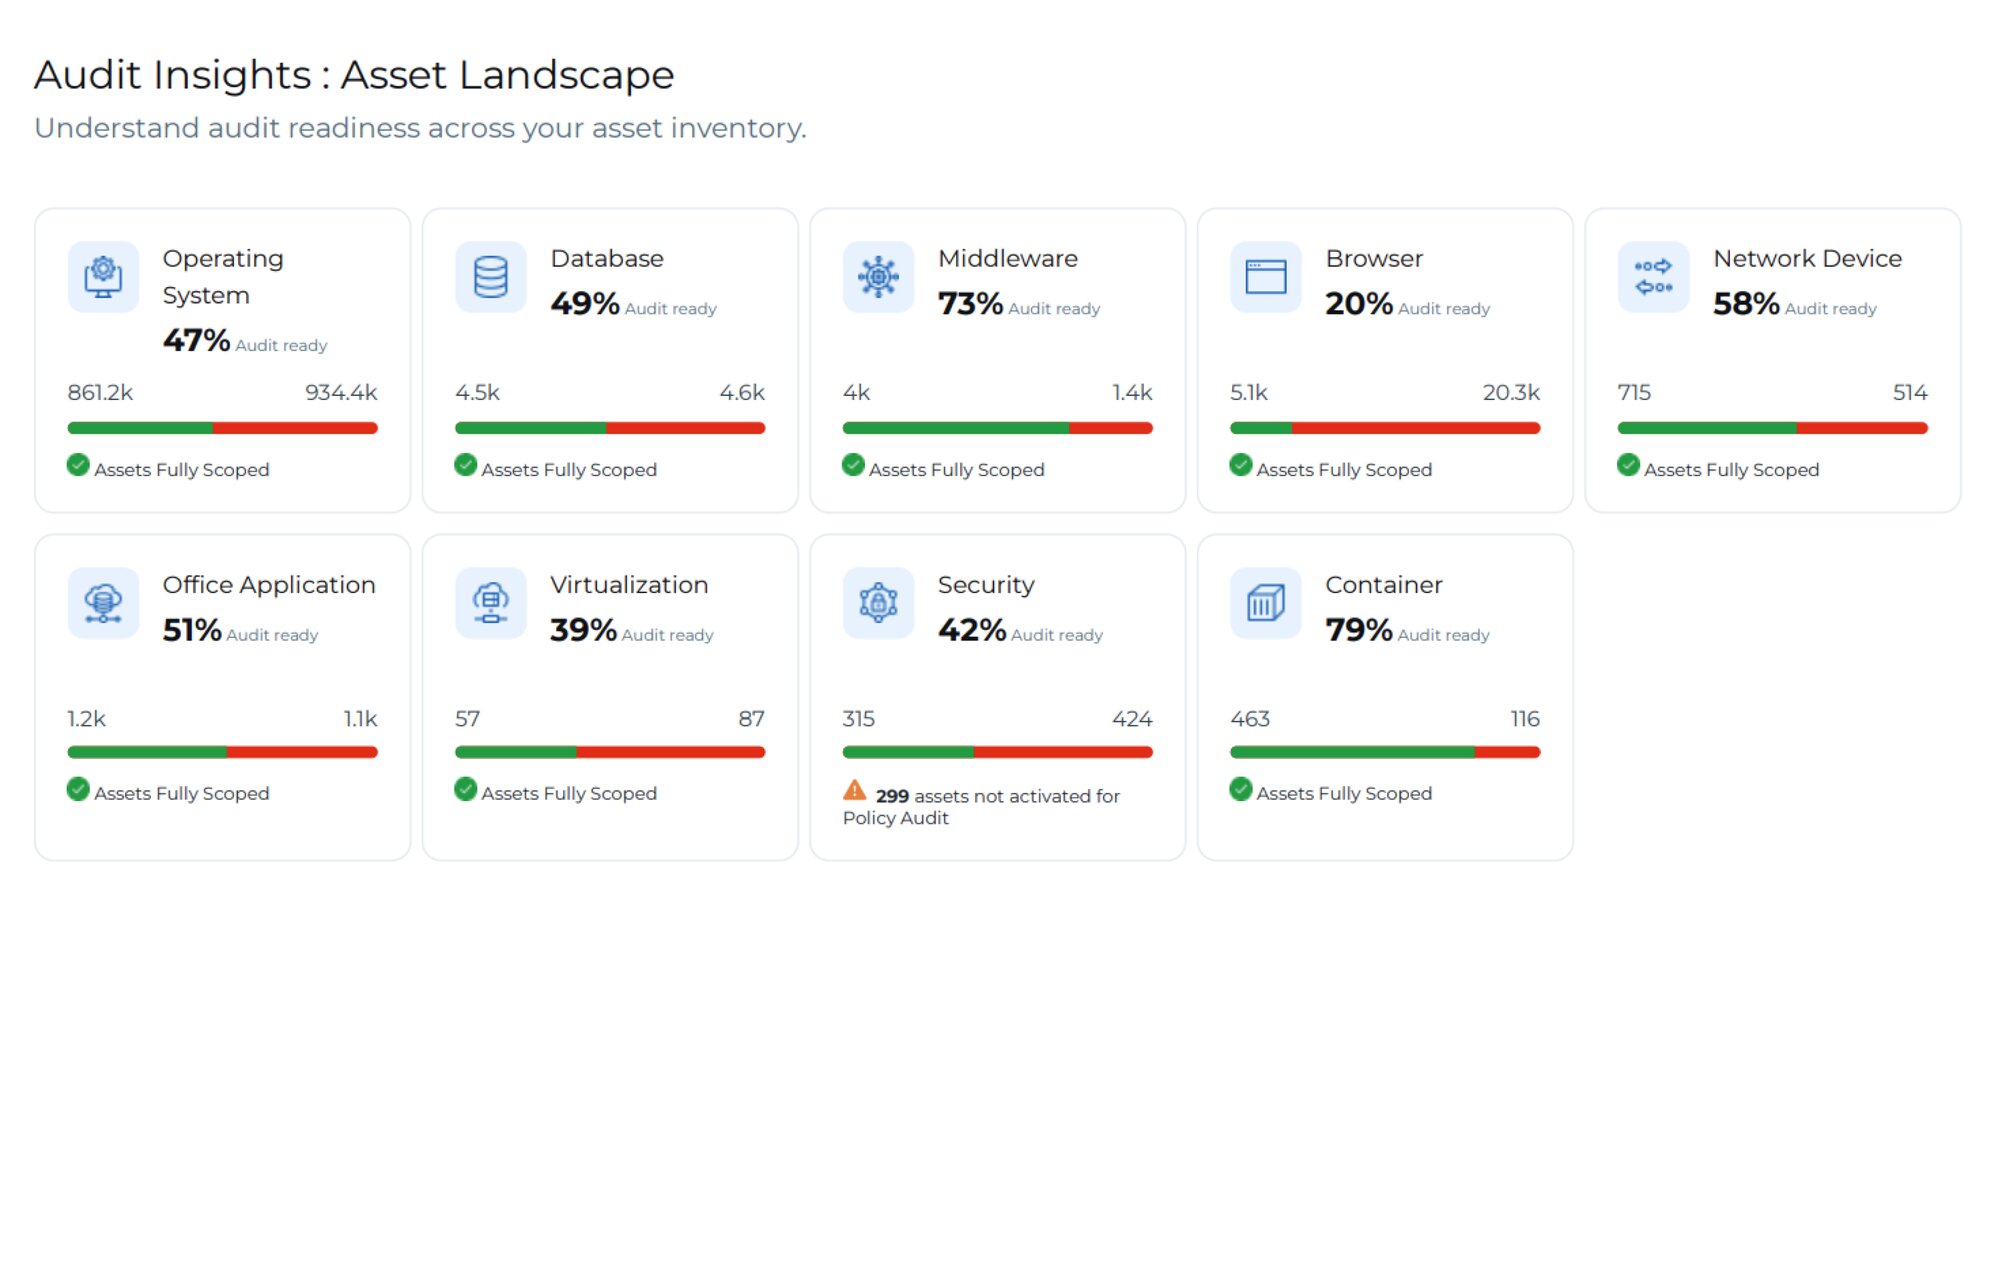
Step 2: Prioritize what drives risk powered by TruRisk
Step 3: Remediate at scale with Audit Fix
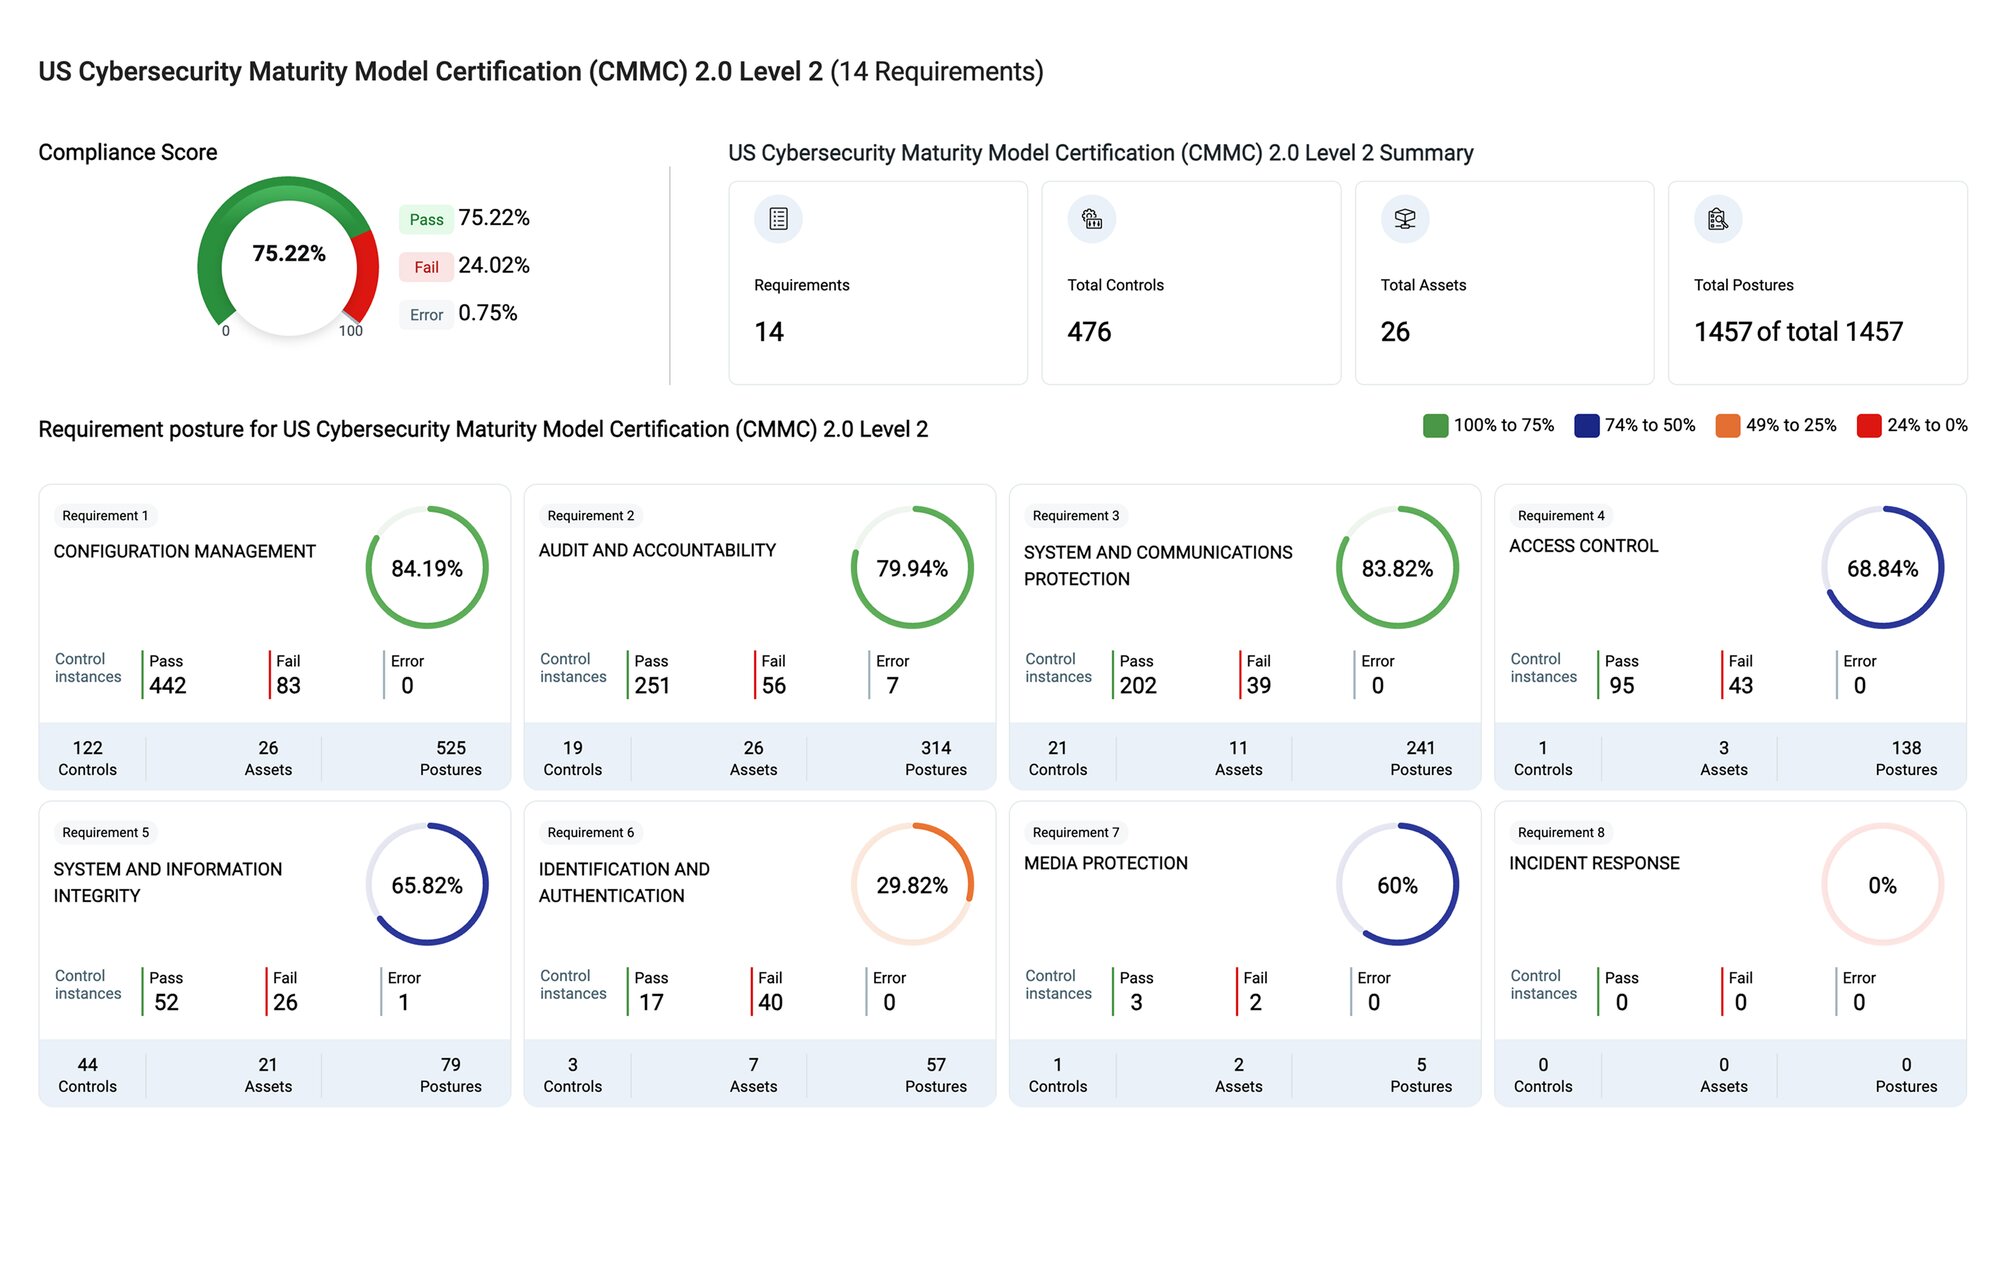
Step 4: Report with audit-ready precision
Step 5: Monitor continuously with no blind spots
What Sets Qualys Policy Audit Apart
AI-powered Policy Authoring, automated evidence collection, control mapping, and gap analysis across 100+ mandates and 500+ technologies, reducing manual effort by up to 90%.
Move from checklists to risk-informed compliance. The Qualys Detection Score (QDS) and TruRisk rank failing controls by business impact, asset exposure, and threat context, so teams fix what matters most first.
Close gaps at scale using out-of-the-box scripts and golden policies, with validation and rollback while maintaining hardened controls through CI/CD and ITSM workflows.
One data collection generates multiple framework reports cross-mapped to 100+ benchmarks (CIS, NIST, PCI DSS 4.0, DORA, FedRAMP), giving auditors a unified, real-time view.
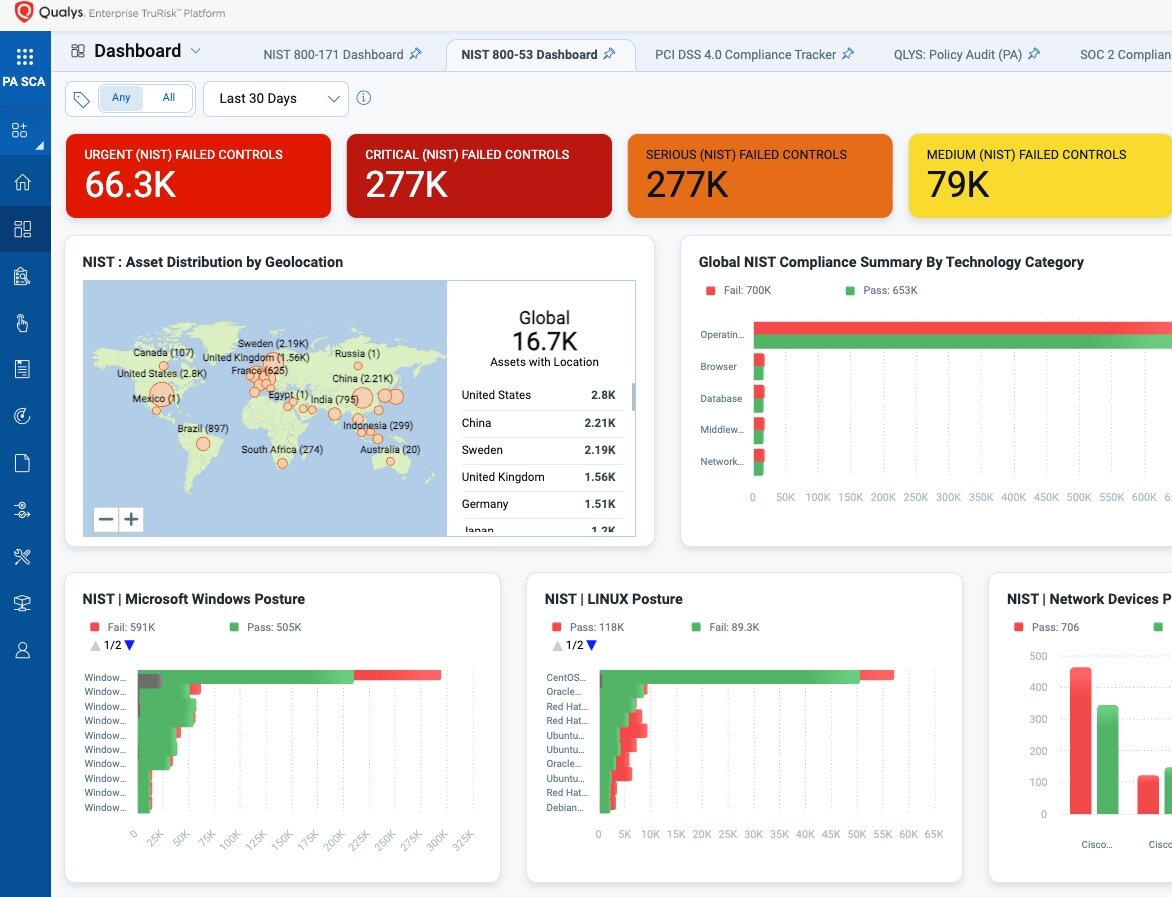
Qualys Policy Audit with Audit Fix AI-Driven Compliance Readiness
Qualys Policy Audit unifies continuous discovery, risk-based prioritization, and automated remediation with Audit Fix, providing real-time compliance readiness at scale across all assets.
Analyst Recognition and Related Resources

Qualys Policy Audit is a solution that automates the assessment of IT system configurations against security policies. It helps you reduce risk and ensure continuous compliance with internal standards and external regulations.
It supports over 110 regulations and frameworks, with a library of over 1,200 policies and 27,000 controls. This includes major standards like CIS Benchmarks, NIST, DISA STIGs, FedRAMP, PCI DSS, and HIPAA, providing broad compliance coverage.
Yes. While it offers a vast library of out-of-the-box policies, you can also customize existing controls or create your own from scratch to match your organization’s specific security standards and audit requirements.
Yes. It is designed for modern hybrid environments, providing unified compliance coverage across on-premises systems, multi-cloud infrastructure, containers, and legacy platforms using a combination of agents, scanners, and out-of-band assessment.
Yes. The solution integrates with ITSM tools like ServiceNow to automate ticketing for compliance gaps. It also integrates with remediation tools and can leverage custom scripts to quickly fix misconfigurations and restore compliance automatically.
Yes. You can schedule compliance scans to run automatically on a recurring basis, daily, weekly, or monthly. This ensures you always have an up-to-date view of your compliance posture without manual intervention.
IT security, compliance, and audit teams should use this solution. It is essential for any organization that needs to enforce security hardening standards, reduce the risk of breaches from misconfigurations, and demonstrate compliance with regulations.