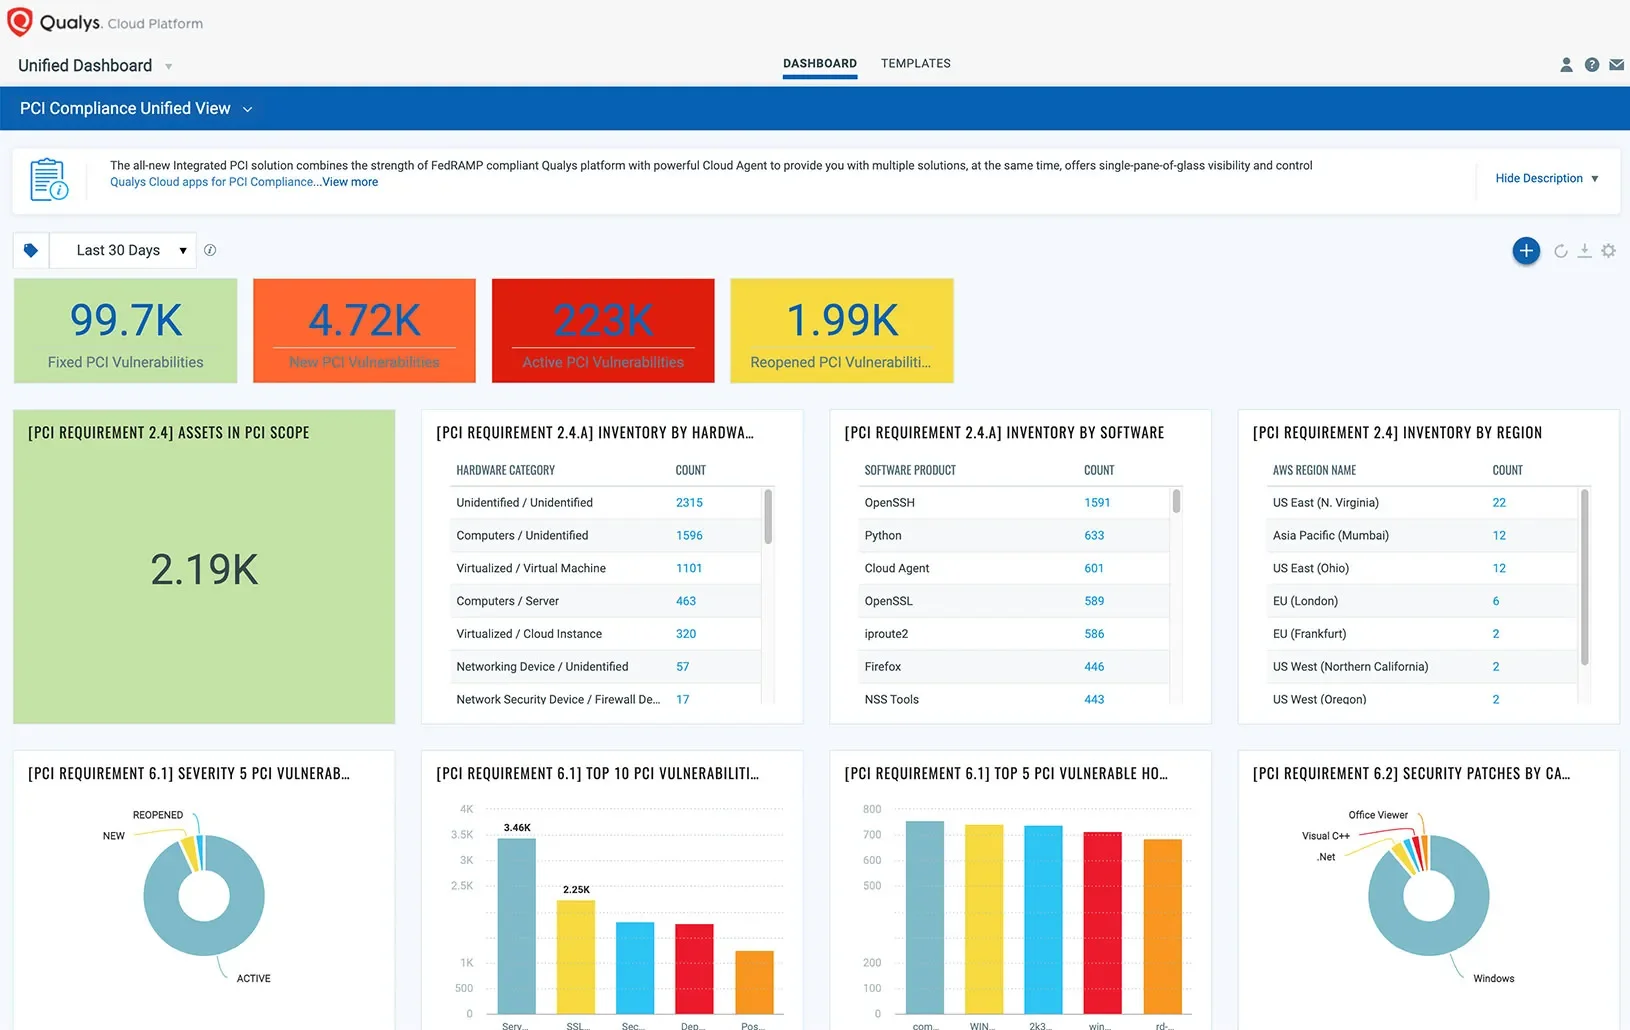
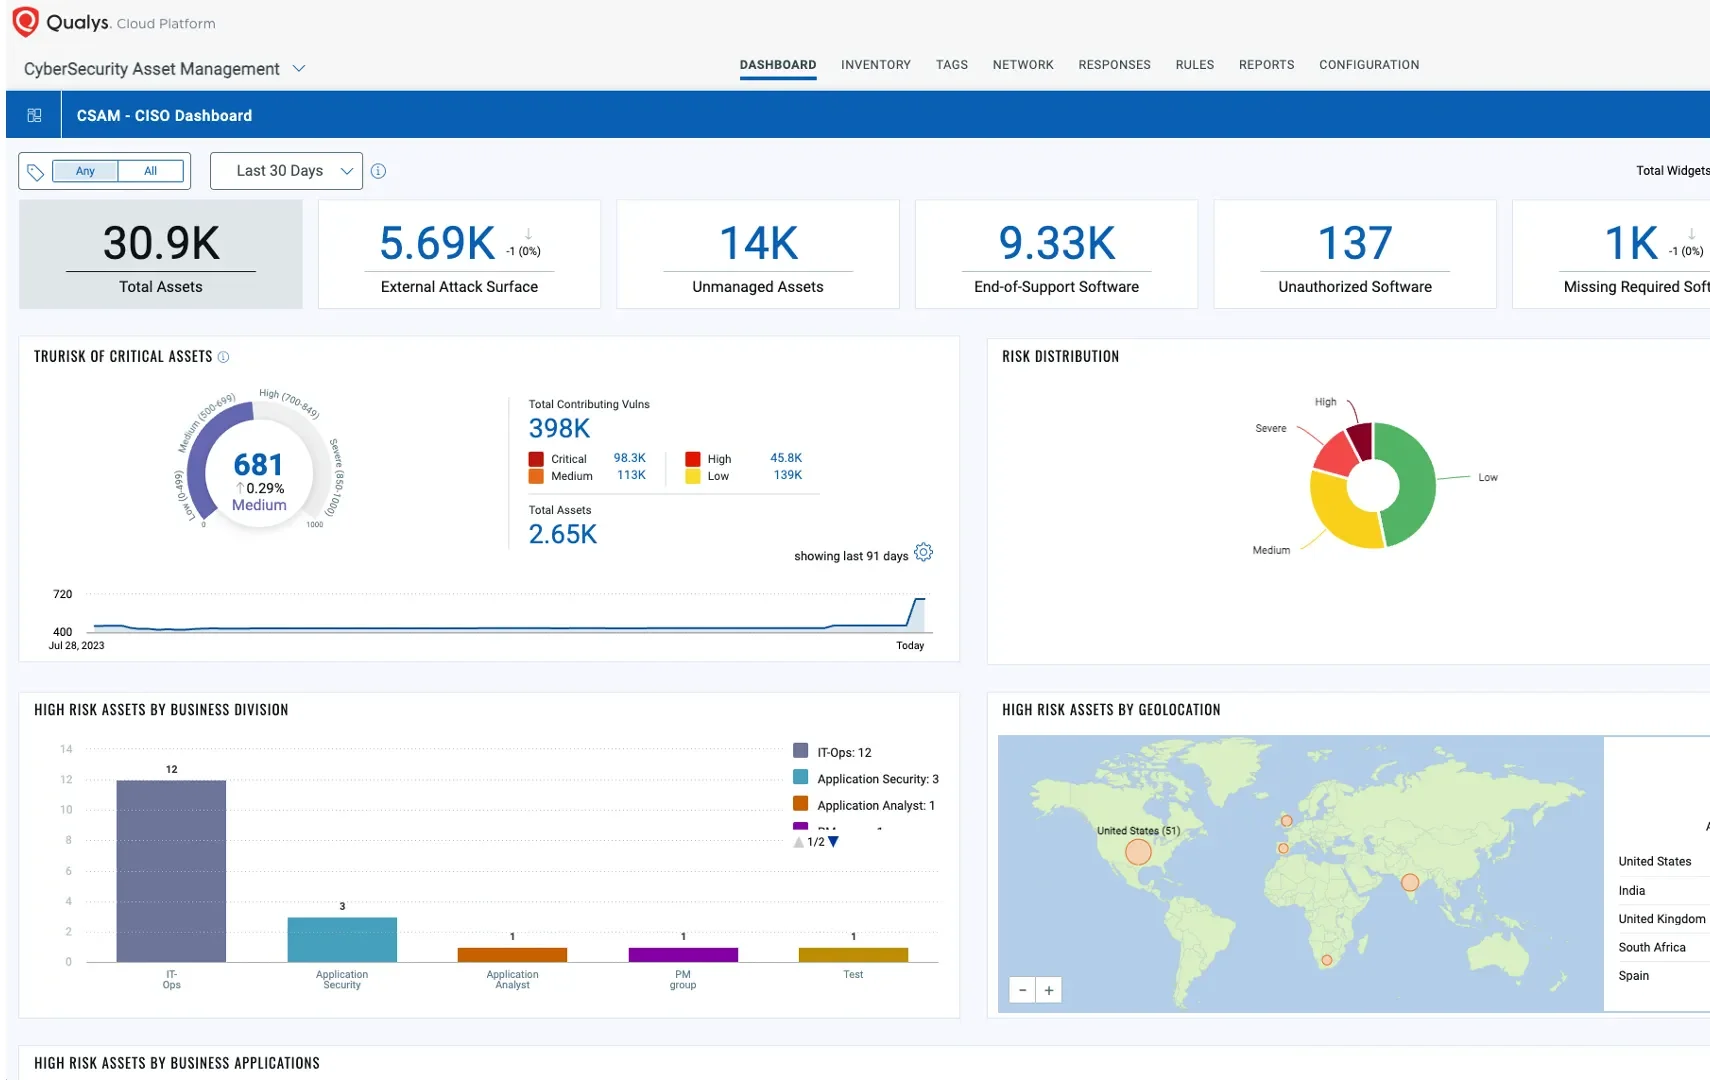
PCI DSS 4.0 introduces a more flexible and risk-based approach to cybersecurity compared to its predecessor, PCI DSS 3.2.1. This updated standard emphasizes continuous monitoring and allows organizations to tailor their security measures to align with their unique risks and business priorities. By enabling customization based on real-world scenarios, such as adopting cloud-native solutions for large cloud infrastructures, companies can implement more effective controls while maintaining compliance.
Under PCI DSS 4.0, firms are encouraged to adopt a risk-based approach to cybersecurity implementation. By leveraging robust threat intelligence, organizations can better understand and prioritize their true risks, ensuring efficient resource allocation and faster resolution of critical issues. This proactive stance enhances overall security posture and helps businesses stay ahead of evolving cyberthreats. The Qualys Enterprise TruRisk Platform includes more than a dozen apps that can help ensure audit ready compliance with PCI DSS 4.0.