The next evolution of QSC, where the brightest minds in cybersecurity unite to chart the future of cyber risk management.

De-risk Your Business
Join us at ROCon Americas, the premier cybersecurity event where top security leaders and practitioners come to get cutting-edge strategies, insights, and discover new solutions that proactively manage and reduce cyber risk.
ROCon, The Risk Operations Conference, delivers thought-provoking keynotes, high-impact sessions, and hands-on workshops on threat detection, cloud security, automation, and risk-driven security strategies. You will discover how to streamline security operations, reduce noise, maximize ROI, and strengthen business resilience, and align security initiatives with your leadership. Don’t miss this opportunity to shape the future of modern cybersecurity and de-risk your organization.
Keynote Speakers
About
As President and CEO, Sumedh leads the company’s vision, strategic direction and implementation. He joined Qualys in 2003 in engineering and grew within the company, taking various leadership roles focused on helping Qualys deliver on its platform vision. From 2014 to 2021, he served as Qualys’ Chief Product Officer, where he oversaw all things product, including engineering, development, product management, cloud operations, DevOps, and customer support. A product fanatic and engineer at heart, he is a driving force behind expanding the platform from Vulnerability Management into broader areas of security and compliance, helping customers consolidate their security stack. This includes the rollout of the game-changing VMDR (Vulnerability Management, Detection and Response) that continually detects and prevents risk to their systems, Multi-Vector EDR, which focuses on protecting endpoints as well as Container Security, Compliance and Web Application Security solutions. Sumedh was also instrumental in the build-up of multiple Qualys sites resulting in a global 24x7 follow-the-sun product team.
About
Kip Boyle has 24 years of experience serving in cybersecurity and IT risk management roles for organizations in the insurance, financial services, technology, military, and logistics industries.Over his entire career, Kip has helped executives change their cyber risks from business blockers to business enablers. As Chief Information Security Officer at PEMCO Insurance, he transformed a frustrating, cumbersome cybersecurity program into one that both protected customers’ information and enabled the business to grow at a faster pace. As Chief Security Officer of PEMCO Technologies, a debit and credit card transaction processor, and PEMCO Corporation, an IT services provider to financial institutions, Kip successfully led the companies through their first ever SAS70 type II certifications, removing a serious sales objection to the continued growth of those companies. At Expeditors International, he led a cross-functional IT governance team that significantly reduced the number of critical events and failures created by much-needed system and technology changes. While at Stanford Research Institute (SRI) Consulting, Kip led a team of six in a comprehensive security review and smartcard/encryption upgrade of the Windows-based FedLine, an instant-settlement funds transfer application for more than 12,000 U.S. financial institutions. For the USAF F-22 Advanced Tactical Fighter program, Kip successfully transformed the network security governance model from one of rigid centralized decision-making to one of delegated decision making by the prime contractors: Lockheed-Martin, Boeing, and Pratt & Whitney.Kip earned a Masters of Science in Management from Troy State University. He earned a Bachelor of Science in Computer Information Systems from the University of Tampa. He has also received a graduate certificate in Executive Leadership from the Albers Business School at Seattle University.Kip earned his Certified Information Systems Security Professional (CISSP) and Certified Information Systems Manager (CISM) credentials in 1997 and 2003, respectively. He has taught information security courses to hundreds of students all over the world.Fire Doesn't Innovate. Kip Boyle compares fire safety to cybersecurity, emphasizing that cyber threats constantly evolve unlike static risks. He argues organizations must abandon outdated approaches, manage cyber as dynamic risk, and embrace AI-powered resilience (being “hard to hack and fast to fix”) for proactive defense in today’s volatile digital landscape.
About
As the Chief Risk Technology Officer at Qualys, Richard helps customers and the broader security community measure, communicate, and eliminate risk. With over 10 years of experience as a CISO, he's led and supported security strategy, operations, and governance across critical infrastructure and cloud-native organizations. Richard has published two books, 'How To Measure Anything In Cybersecurity Risk' and 'The Metrics Manifesto: Confronting Security With Data.' Each provides practical and innovative approaches to quantifying and reducing security risk. His first book is the main curriculum at the US Dept of Defense (DoD) CISO program at Carnegie Mellon University and numerous other institutions of higher education.
Featured Speakers
About
Antonio Anderson is a seasoned technology executive with over two decades of experience driving enterprise-wide IT and cybersecurity strategies. As a strategic VP, Information Security & IT, he has successfully led digital transformation initiatives, accelerated cloud adoption, and integrated AI/ML solutions to deliver measurable business outcomes. Antonioholds advanced degrees in Law and Computer Science, and is a trusted advisor in aligning technology investments with business goals while ensuring strong governance and regulatory compliance. His leadership has enabled organizations to achieve operational efficiency, reduce cyber risk, and unlock new revenue streams through security assurance.
A recognized expert in cybersecurity, risk management, and data privacy, Antonio holds the CISSP (Certified Information Systems Security Professional), CISA (Certified Information Systems Auditor), and CDPSE (Certified Data Privacy Solutions Engineer) certifications. His expertise spans SOX, HIPAA, GDPR, PCI-DSS, and NIST frameworks, making him a sought-after thought leader for organizations navigating complex compliance landscapes. Known for building high-performance teams and fostering cultures of innovation and accountability, Antonio brings both strategic vision and hands-on expertise to every engagement.
About
Terry hails from Santa Cruz California originally and began his career in Information Technology at Mighty Net, Inc. (founding company for Creditreport.com) as CTO – Director of Systems and Security while attending California State University Northridge. There he was responsible for all Infrastructure, networking, and security. In 2007, Terry took a Director of IT position at Protocol and left the company as Director of US IT Operations when they were acquired by Expert Global Solutions.
At EGS he ventured back into Information Security role full-time and worked alongside his CISO as the two man team responsible for achieving PCI compliance across the Enterprise. In 2015 he transitioned to American Express Global Business Travel as an Information Security Manager. Today his responsibilities include Cyber Security Metrics, Managing the Vulnerability management platforms including Qualys and several other Information Security platforms at GBT.
About
With nearly 20 years of executive experience running enterprise software companies, Tom Berquist announced his retirement in September 2025 as CFO of Cloud Software Group, an entity resulting from the merger of Citrix Systems and TIBCO Software in September 2022. Before the merger, Tom served as CFO of TIBCO Software for seven years. Tom’s professional journey includes serving as the CFO of Alludo (formerly Corel) and Actian (formerly Ingres), as well as being the CEO of Saba Software (acquired by Cornerstone OnDemand) and Alludo.
Tom spent a decade on Wall Street, acting as a managing director of Software Equity Research at various institutions such as Citigroup (formerly Salomon Smith Barney), Goldman Sachs, and Piper Sandler. His purview encompassed major enterprise software companies like Microsoft and Oracle, rapidly expanding cloud software entities like Salesforce and Concur, and security software companies like Symantec, McAfee, and Checkpoint Software. Tom spent the early part of his career at Deloitte Consulting as a management consultant developing software strategy plans for Fortune 500 customers including Honeywell, Liberty Mutual, and US Bancorp. Before Deloitte Consulting, Tom developed enterprise software for Wells Fargo and Fortis. Tom has previously served on the board of directors of Alludo, Saba Software, and Serus Corporation (acquired by E2open). Tom holds a BA in accounting and an MBA in management and marketing from the University of St. Thomas, Saint Paul, Minnesota.
About
Brendan Hall is a Senior Vice President and one of the leaders of the cyber insurance and consulting practice at Alliant Insurance Services. In his role, Brendan focuses on business development, strategy and execution for the cyber vertical, which includes counseling clients on their insurability and designing advisory solutions to improve cyber resilience.Brendan also works closely with private equity clients helping them deploy tailored cross-portfolio cyber risk mitigation solutions, as well as transactional cyber diligence.
Prior to his current position, Brendan was a Senior Vice President at Stroz Friedberg, an Aon Company where he was a leading producer for the firm’s cyber security practice which provided data breach incident response services, security advisory, technical testing, threat intelligence, investigations and cyber insurance to their clients.
Brendan regularly contributes to trade publications and is often invited to lend his expertise on industry panel discussions and podcasts.
Brendan received his Bachelor of Arts in Economics from Hobart College where he also played four years of collegiate basketball.
He is an avid triathlete and distance runner having completed two Ironman triathlons and five marathons. Brendan resides in Long Island City, NY with his wife and two daughters.
About
Douglas Hubbard is the inventor of the Applied Information Economics (AIE) method and founder of Hubbard Decision Research (HDR). He is the author of How to Measure Anything: Finding the Value of Intangibles in Business, The Failure of Risk Management: Why It’s Broken and How to Fix It, Pulse: The New Science of Harnessing Internet Buzz to Track Threats and Opportunities, How to Measure Anything in Cybersecurity Risk, 2e, and his latest book How to Measure Anything in Project Management. He has sold over 200,000 copies of his books in eight different languages. Three of his books have been required reading for the Society of Actuaries exam prep. In addition to his books, Mr. Hubbard has been published in several periodicals including Nature, The IBM Journal of Research and Development, OR/MS Today, Analytics, CIO, Information Week, and Architecture Boston.
Mr. Hubbard’s career has focused on the application of AIE to solve current business issues facing today’s corporations. Mr. Hubbardhas completed over 200 risk/return analyses of large, critical projects, investments and other management decisions in the last 25 years. AIE is the practical application of several fields of quantitative analysis including Bayesian analysis, Monte Carlo simulations, and many others. Mr. Hubbard’s consulting experience totals over 36 years and spans many industries including insurance, financial services, pharmaceutical, healthcare, utilities, energy, federal and state government, entertainment media, military logistics, and manufacturing. His AIE methodology, has received critical praise from The Gartner Group, The Giga Information Group, and Forrester Research. He is a popular speaker at valuation, risk, metrics and decision analysis conferences all over the world.
About
Tony Martin-Vegue is a cybersecurity and technology risk expert with over 25 years of experience helping Fortune 500 companies and high-growth organizations build and scale quantitative risk programs. A hands-on practitioner as well as a leader, Tony has performed more than a thousand quantitative risk assessments across cyber, fraud, operations, and enterprise domains.
He is the author of the upcoming book From Heatmaps to Histograms: A Practical Guide to Cyber Risk Quantification (Apress, 2026) and writes the newsletter Heatmaps to Histograms: Field Notes, where he shares practical, creative approaches to risk and decision-making. Tony is a frequent speaker at FAIRcon, SIRAcon, RSA, Security BSides, and ISACA events, and has been published in outlets including the ISACA Journal and Risk.net.
Tony advises companies on starting or improving their cyber risk quantification programs, helping leaders choose the right CRQ platform, avoid common pitfalls, and translate analysis into decisions that matter. He is known for making complex concepts accessible, blending deep technical knowledge with relatable storytelling and a people-first approach.
Based on an island in the San Francisco Bay, Tony enjoys time with his family, travel, cooking (especially bread and Mexican food), and open-water swimming, including ten swims from Alcatraz to San Francisco.
About
Charity Otwell is the Director of the CIS Critical Security Controls for CIS. She has nearly 20 years of experience in the financial services industry and has built and led various programs such as Business Continuity, Disaster Recovery, Technology Governance, and Enterprise Architecture in a highly regulated environment. Before coming to CIS, Otwell was a GRC champion and practitioner with a focus on risk assessment, process optimization, process engineering, and best practice adoption for a top-50 bank within the United States. She also helped manage the relationship with federal regulators and the management of federal regulatory exams. She completed undergraduate and graduate studies in Birmingham, Alabama, and holds multiple industry certifications.
About
For many years, Jim Reavis has worked in the information security industry as an entrepreneur, writer, speaker, technologist and business strategist. Jim’s innovative thinking about emerging security trends have been published and presented widely throughout the industry and have influenced many. Jim is helping shape the future of information security and related technology industries as co-founder, CEO and driving force of the Cloud Security Alliance. Jim has been named as one of the Top 10 cloud computing leaders by SearchCloudComputing.com. Jim is the President of Reavis Consulting Group, LLC, where he advises security companies, governments, large enterprises and other organizations on the implications of new trends such as Cloud, Mobility, Internet of Things and how to take advantage of them. Jim founded SecurityPortal, the Internet’s largest website devoted to information security in 1998, and guided it until a successful exit in 2000. Jim has been an advisor on the launch of many industry ventures that have achieved a successful M&A exit or IPO. Jim is widely quoted in the press and has worked with hundreds of corporations on their information security strategy and technology roadmap. Jim has a background in networking technologies, marketing, product management and systems integration. Jim received a B.A. in Business Administration / Computer Science from Western Washington University in 1987 and formerly served on WWU’s alumni board. Jim was recognized as a WWU Distinguished Alumnus in 2015. In 2016, Jim was inducted into the Information Systems Security Association (ISSA) Hall of Fame.
About
Christy Sluder is a Manager of Vulnerability Management at HCA Healthcare with over 25 years of experience in both hospital settings and the corporate healthcare industry. She has led transformative collaboration initiatives across technical silos and divisions at a Fortune 100 company, pioneering programs that drive innovation and strengthen enterprise-wide security posture. With deep expertise in every phase of the vulnerability management lifecycle, Christy has successfully guided multiple teams through complex security challenges with precision and purpose. She earned her Bachelor of Applied Science in Computer Science from Western Governors University and remains a passionate advocate for continuous learning and cross-functional teamwork. Outside of work, Christy enjoys camping, hiking, and getting lost in a good book. She's also an avid board game enthusiast—especially when it comes to Trivial Pursuit—and loves attending concerts across all genres of music.
About
Mark Verbeck is a seasoned Chief Financial Officer and strategic advisor with over 20 years of experience scaling high-growth technology companies. He has served as CFO for Blade Network Technologies, Coupa Software, Saba, and Cyara, where he led financial strategy, operational transformation, and successful exits to both private equity and corporate acquirers.In his leadership roles, Mark has consistently emphasized the importance of robust cybersecurity practices—not only to mitigate risk, but also to enhance enterprise value and acquisition readiness. His experience spans IPO preparation, M&A execution, and building finance teams that deliver actionable insights.Mark holds a business degree from the University of St. Thomas and is a graduate of the Stanford Executive Program at the Stanford Graduate School of Business.
About
As Senior Vice President of Product Management, Shailesh leads the product management team and drives the Qualys product vision helping customers assess and improve their IT, security and compliance posture. Since joining Qualys in 2012, he has worked in various security and compliance roles driving innovative solutions, including remote endpoint protection, endpoint detection and response, and SaaS security. In addition, Shailesh headed engineering, research and product management for Qualys Policy Compliance and File Integrity Monitoring, where he helped customers go beyond compliance to drive their IT GRC objectives. Before Qualys, he focused on security research for Symantec ESM and Compliance solutions. Shailesh holds a master’s in computer applications (MCA) from the Vishwakarma Institute of Technology and has various security certifications including CISA, CRISC, CISM. He is also a regular speaker at industry conferences.
About
As the Chief Technology Officer and Senior Vice President of the Qualys Cloud Platform, Dilip is responsible for leading global product development, data and platform engineering, DevOps, site reliability engineering, cloud operations and customer support across Qualys’ broad security product portfolio. Dilip joined Qualys in 2016 to drive Qualys’ own internal digital transformation efforts and has been instrumental in helping scale the technology and organization in support of the company’s accelerated product growth and transformation into a unified security platform. Prior to joining Qualys, Dilip served in multiple engineering leadership roles at various mid-sized and large organizations to build and deliver complex, scalable, distributed enterprise SaaS products and big data cloud platforms. Dilip has a bachelor’s degree in electronics engineering from the University of Mumbai and a master’s degree in computer science from Ball State University.
About
Shrikant Dhanawade is Director of Product Management, responsible for Cloud Security products in Qualys. He has more than a decade working experience in Cloud Automation, Cloud Security, DevSecOps with a demonstrated history of working in the Cybersecurity Products and information technology industry. Previously, Shrikant worked for various Cloud Security initiatives with Xoriant and Accenture. Shrikant holds a Bachelor of Engineering Degree in Computers from Mumbai University and Executive Program in Global Business Management from IIM Calcutta.
About
Lavish Jhamb is Sr. Product Manager, Compliance solutions at Qualys, focused on building security solutions such as ‘Custom Assessment and Response’ and ‘File Integrity Monitoring’ and helping customers assess and improve their security and compliance posture. He has over 7 years of experience working on security solutions, regulatory standards, and cyber security frameworks, with thorough understanding of operating systems. Lavish holds a bachelor’s degree in computer engineering from the Kurukshetra University Institute of Engineering and Technology and a Post Graduate Diploma in IT Infrastructure, Systems and Security from CDAC Pune.
About
I am the Sr Product Manager for Compliance Solutions here at Qualys. I have been with Qualys for over 7 years working in engineering and product role. As a product manager for Qualys, my primary focus is on helping organizations meet there security and compliance needs leveraging Qualys Policy compliance and cloud platform.
About
Himanshu Kathpal is VP, Product Management, Platform and Technologies at Qualys. He has over 13 years of experience in cybersecurity and product management, with a specialization in vulnerability management, remediation, and next-generation endpoint security. Himanshu is passionate about developing security solutions that align with the company’s cybersecurity product strategy to meet customer needs, reduce the attack surface, and strengthen the organization’s security posture. He holds a master’s degree in engineering from D.Y.Patil University, Pune, as well as an MBA in International Business Management from NMIMS, Mumbai.
About
Alex Kreilein is Vice President of Product Security at Qualys. He leads efforts to deliver secure, resilient, and trustworthy products by focusing on portfolio risk management, vulnerability management, automation, and developer enablement. Previously, Alex led security, reliability, and performance programs for mission-critical workloads at Microsoft Azure. Alex has been the CISO of a cloud-native critical infrastructure company, a leader with the Department of Homeland Security, and a multi-time entrepreneur. He holds graduate degrees from CU Boulder and the U.S. Naval War College.
About
Eran Livne is Senior Director, Endpoint Remediation at Qualys, leading a team tasked with helping customers improve their security posture through cross-platform vulnerability remediation. He has more than 20-years of product management and computer science experience working in diverse IT and security markets. In 2014, Eran founded mobile security company, LetMobile, acquired by Ivanti. Following the acquisition, he drove Ivanti’s enterprise security and endpoint security and management solutions. Eran holds a bachelor’s degree in computer science from Tel Aviv University and an MBA in high-tech business administration from Technion - Israel Institute of Technology.
About
Karun leads Qualys’ worldwide strategic alliances and channel partnerships with MSSP’s, VAS partners, consultants and resellers. A computer engineer with a passion for cybersecurity, he has been at Qualys since 2013, supporting and helping grow its business with channel partners globally. Today, Qualys powers security and compliance solutions for the majority of MSSP’s in Gartner’s Magic Quadrant for Managed Security Services.
He has been a cybersecurity and cloud advocate since his early days at HCL Technologies, one of the large global systems integrators, where he ultimately led cybersecurity pre-sales and business development for North America . Karun’s experience includes advising CIO’s and CISO’s of large fortune 500 organizations on adapting cybersecurity programs for the digital and hyperconnected age. He has a bachelor’s degree in computer engineering from the University of Pune and a post-graduate Management degree in Business Administration (M.B.A.) from Amity University, India.
About
Abhinav Mishra is Product Management Director at Qualys, where he drives strategic initiatives to advance the company’s container security offerings. With a strong focus on risk-based operations and go-to-market alignment, he works across product, engineering, and field teams to deliver impactful security outcomes for global enterprises. He brings over a decade of experience spanning product leadership, software engineering, and GTM strategy. Prior to Qualys, Abhinav led container security at Uptycs, a CNAPP vendor, and spearheaded Kubernetes multi-tenancy and developer self-service initiatives at Rafay. He began his career at VMware, where he spent five years as a software engineer focused on cloud networking and security. Abhinav holds a bachelor’s degree in computer engineering from Columbia University and an MBA from the Kellogg School of Management
About
May Mitchell is the Chief Marketing Officer (CMO) at Qualys, where she spearheads global marketing strategy, drives business growth and pipeline contribution collaborating closely with Sales and Partners to implement scalable programs that accelerates customer acquisition, retention, and expansion. With a proven track record in aligning marketing initiatives to corporate objectives, May plays a pivotal role in strengthening Qualys’ market position as an industry leader in cybersecurity and risk management.
May brings over 25 years of experience in cybersecurity marketing, specializing in go-to-market strategies that deliver measurable impact. Her career includes 15 years in executive leadership, with three terms as CMO, at companies like HUMAN Security, Ontinue, iboss, Cylance, Symantec, Forcepoint, and McAfee, where she consistently drove innovation and growth.
May has been honored as one of CRN’s Power 100 Women of the Channel for 13 consecutive years, named among the Top 50 Women in Cybersecurity by CyberScoop, and received the prestigious OnCon Top 50 Marketer Award for three consecutive years.
She holds a bachelor’s degree in computer science from California State University and has completed engineering management programs at Santa Clara University.
About
Kunal is currently VP of Product Management for the CyberSecurity Asset Attack Surface Management (CAASM), Web App and API Security product line at Qualys HQ in Foster City, CA. He is Qualys boomerang. He worked at Qualys for 3 years and incubated the XDR product line from inception. Kunal has spent 15+ years working at startups, and big and mid-size companies in cybersecurity, networking, and application security in both product and engineering roles at Juniper Networks, Extreme Networks, Sun Microsystems and Infinera. Prior to re-joining Qualys, Kunal was heading products at Israeli startup in API security and bot management AppSec space.
About
Russ Sanderlin is a U.S. Marine Corps veteran and cybersecurity professional specializing in vulnerability management and risk reduction. As a Director and Subject Matter Expert for Qualys VMDR, he helps organizations strategically mature their vulnerability management programs, moving beyond traditional scanning to risk-based approaches. With a CISSP certification and consulting experience across finance, manufacturing, insurance, and travel, he brings cross-industry insights to help customers strengthen their cybersecurity programs.
About
Jonathan Trull is a longtime security practitioner and CISO & SVP Security Solution Architecture with over 18 years of experience in the cybersecurity industry and is currently the Senior Vice President of Customer Solutions Architecture and Engineering at Qualys. His career has spanned operational CISO and infosec roles with the State of Colorado, Qualys, Optiv, and Microsoft. While at Microsoft, Jonathan led the Microsoft Detection and Response Team (DART) whose mission was to respond to cyber security incidents around the globe ranging from cyber espionage initiated by nation-state actors to ransomware attacks and included the investigation of and response to the NOBELIUM threat actor campaign which leveraged the SolarWinds supply chain. Jonathan also serves as an advisor to several security startups and venture capital firms and supports the broader security community through his work with the Cloud Security Alliance, Center for Internet Security, and IANS. He is also an adjunct faculty member at Carnegie Mellon University where he mentors and coaches those attending the CISO Executive Education Program. Jonathan is a frequent speaker at industry conferences such as BlackHat, RSA, and SANS and holds several industry certifications including the CISSP, OSCP, CCSP, and GCFA. Jonathan is a veteran of the U.S. Navy finishing his career as a Lieutenant Commander supporting the Information Warfare Domain.
Agenda
Training Sessions
Conference Sessions
Training is free for all customers. Sign up today as space is limited.
7:30 AM – 5:00 PM
Registration
JW Marriott Hotel at the Galleria
7:30 AM – 8:30 AM
Attendee Breakfast
JW Marriott Hotel at the Galleria
Unlock the Power of the Qualys Enterprise TruRisk™️ Platform
Jamie Kaushik
Qualys
Scan Like a Pro: Best Practices and Troubleshooting
Jeremy Oliver
Qualys
De-Risk Web Applications and APIs with Qualys TotalAppSec
Fil Lamagna
Qualys
12:00 PM – 1:00 PM
Lunch
JW Marriott - Liberty Hall
SwagOps Store
A Deep Dive into Qualys TruRisk™️ and Exploring Enterprise TruRisk Management (ETM)
Marcus Burrows
Qualys

Chinmay Inamdar
Qualys
Strengthen Your Cloud Security Posture with Qualys TotalCloud
Prachi Jain
Qualys
Stay Continuously Audit Ready with Qualys Policy Audit
Jeremy Oliver
Qualys
Training is free for all customers. Sign up today as space is limited.
7:30 AM – 6:00 PM
Registration
JW Marriott Hotel at the Galleria
7:30 AM – 8:30 AM
Attendee Breakfast
JW Marriott Hotel at the Galleria
Patching and Beyond: Reduce Risk with Qualys TruRisk™️ Eliminate

Sharda Singh
Qualys
A Deep Dive into Qualys TruRisk™️ and Exploring Enterprise TruRisk Management (ETM)

Marcus Burrows
Qualys

Chinmay Inamdar
Qualys
Streamline Your Implementation Using Qualys APIs

Fil Lamagna
Qualys

David Gregory
Qualys
Partner Summit
12:00 PM – 1:00 PM
Lunch
JW Marriott - Liberty Hall
SwagOps Store
Unlock the Power of the Qualys Enterprise TruRisk™️ Platform

Keith Lawton
Qualys
Operate like an Expert using Qualys Query Language (QQL) and Dashboards

Jamie Kaushik
Qualys
Mastering Qualys: Advanced Use Cases & Troubleshooting Deep Dive

Kevin O'Keefe
Qualys
5:30 PM – 7:00 PM
Welcome Reception
JW Marriott - Liberty Hall
7:15 AM – 8:45 AM
Breakfast
JW Marriott - Liberty Hall
7:30 AM – 5:00 PM
Registration
JW Marriott Hotel at the Galleria
SwagOps Store
Welcome to ROCon

Shawn O'Brien
Fire Doesn’t Innovate: Thriving in the Face of Evolving Cyber Risks

Kip Boyle
Cyber Risk Opportunities
Moving From Attack Surface to Risk Surface Management

Sumedh Thakar
Qualys
10:15 AM – 10:45 AM
AM Break
JW Marriott Hotel at the Galleria
Innovations to Power Your Risk Operations Center (ROC)

Shailesh Athalye
Qualys
Panel: Cyber Risk from a Board Perspective

Jonathan Trull
Qualys

Tom Berquist
Qualys

Jim Reavis
Cloud Security Alliance

Mark Verbeck
12:00 PM – 1:30 PM
Lunch
JW Marriott - Liberty Hall
Technical Track
Transforming the Risk Operations Center with Agentic AI Workflows

Mayuresh Ektare
Qualys
As cyber threats become increasingly sophisticated and regulatory pressures intensify, security leaders face growing pressure not only to detect vulnerabilities but also to actively manage and communicate risk in real-time.The Risk Operations Center (ROC) is emerging as the strategic nerve center for proactive, data-driven risk reduction. However, operationalizing the ROC at scale means going beyond dashboards and alerts; it requires an intelligent, automated approach that unifies security signals, business context, and response workflows. In this session, we'll explore how Qualys ETM, powered by Agentic Al, enables organizations to shift from reactive security postures to continuous, measurable risk mitigation. Attendees will learn how Agentic Al autonomously correlates threat intelligence, asset criticality, and exploitability data to cut through the noise and spotlight the risks that truly matter.
Whether you're a CISO defining your strategic roadmap or a security leader optimizing existing processes, this session will deliver actionable insights on how to:
- Transform vulnerability data into prioritized, business-aligned risk signals- Automate triage and remediation at scale with context-aware playbooks- Build a unified risk narrative for executives and boards
Business Track
Panel: Speaking the Language of Business: Cyber Risk Reimagined

Richard Seiersen
Qualys

Douglas Hubbard
Hubbard Decision Research

Tony Martin-Vegue
95 Risk Advisory
Security leaders must translate cyber risk into business terms—financial impact, strategic priorities, and governance metrics. In this moderated session, Richard Seiersen, joined by cyber risk experts Tony Martin-Vegue and Doug Hubbard, will explore how to shift from attack-surface metrics to a risk-surface perspective that business leaders can act on. The discussion will highlight practical frameworks and quantification models that connect vulnerabilities and threats to measurable business outcomes. Panelists will share real-world examples of how organizations are redefining cyber risk in ways that inform decisions, strengthen governance, and elevate cybersecurity as a business enabler. Attendees will leave with actionable strategies to close the communication gap between security and leadership and ensure cyber risk is managed as a core business priority.
Technical Track
Effective Risk Reduction with Patch and Patchless Strategies

Eran Livne
Qualys

Lavish Jhamb
Qualys

Tom Scheffler
Cintas
Security finds the risks. IT gets stuck fixing them. The result? Security teams are buried in findings, IT teams are drowning in tickets, and progress on reducing exposure is too slow.Qualys Eliminate closes that gap. It connects detection to action with automated, prioritized remediation—so Security can assign the right fixes to IT, with the proper context, at the right time.
The payoff:
• Clear, streamlined handoffs from Security to IT.
• Fixing what matters first instead of chasing endless lists.
• Automated workflows that cut exposure windows and keep both teams in sync.
Because spotting risks doesn't make you safer, eliminating them does.
Business Track
Panel: Aligning Cyber Insurance to Risk Operations

Richard Seiersen
Qualys

Brendan Hall
Alliant

Scott Stransky
Marsh McLennan
Technical Track
Redefining Risk Programs: Modernizing VM into Money-Minded CTEM

Kunal Modasiya
Qualys

Christy Sluder
HCA Healthcare
Vulnerability management is evolving. It's no longer just about finding and patching flaws, but about understanding and reducing risk across your entire attack surface. With VMDR and Cyber Security Asset Management, you've already laid the groundwork, giving teams visibility, control, and scalable prioritization across complex environments. The Qualys Risk Operations Center (ROC) means moving past whack-a-mole scans and into strategic exposure management, driven by business impact and financial relevance. Leveraging prompt-driven Cyber Risk Agents, Qualys helps security teams navigate, analyze, and act on exposure data with context, speed, and accountability, transforming fragmented data into clear action.
In this session, you'll see how you can elevate your current VMDR and Cybersecurity Asset Management deployment and build an effective ROC to orchestrate unified risk insights and drive real-time, coordinated response at scale. We'll also explore how Al supercharges this journey, helping your teams work faster, smarter, and with greater impact.
Business Track
Panel: Cyber Risk from the Lens of the CIO

Brad Bell
Qualys

Tom Berquist
Qualys

Ralph Loura
SustainableIT
3:00 PM – 3:30 PM
PM Break
JW Marriott Hotel at the Galleria
Technical Track
When Cloud Risk Meets Code: Fixing Attack Paths at the Source

Kunal Modasiya
Qualys

Shrikant Dhanawade
Qualys

Terry Barber
American Express Global Business Travel
Cloud environments drive innovation, agility, and growth; however, every advance brings new security challenges, ranging from misconfigurations and API exposures to the pitfalls of the shared responsibility model. As enterprises rapidly migrate workloads and modern apps to the cloud, the complexity of managing risk and compliance increases, and traditional siloed security strategies can't keep pace. Competitors may claim CNAPP coverage, but without deep application security integration and true code-to-cloud visibility, critical risks remain hidden.
This session explores blind spots in multi-cloud and app security, exposes today's fragmented defenses, and shows how Qualys helps DevSecOps, CloudSecOps, and security leaders stop attack paths early—at the code and app layer—before they become costly incidents.
Key Takeaways — What You'll Learn:
• How the Qualys Risk Operations Center for Cloud prioritizes vulnerabilities, misconfigurations, exposures, and exploitability to surface truly critical risks across cloud and app layers.
• Why Attack Path analysis illuminates hidden lateral movement and privilege escalation routes—and how to disrupt them at the source.
• How code-to-cloud tracing and DevSecOps integrations ensure app and cloud security controls align with modern CI/CD pipelines, fixing risks in-code.
• How FlexScan and Application Security deliver continuous discovery and protection for multi-cloud, web apps, and APls with unified visibility.
• How QFlow automation streamlines remediation and compliance processes to reduce tool sprawl and operational friction.
Stop guessing. Start securing. Gain a precise roadmap to cloud and app-native maturity, built on the pillars of visibility, automation, and intelligence that protect and power your digital future.
Business Track
From Gut Feel to Good Data: How AI will Transform Risk Management

Tony Martin-Vegue
95 Risk Advisory
Artificial intelligence promises faster, richer insights for cyber risk quantification, but it also brings hallucinations, biases, and overconfidence. This talk explores where AI truly adds value in transforming gut-feel estimates into usable data, and where human judgment and validation remain essential. Attendees will leave with practical strategies to integrate AI into their risk workflows without losing rigor or credibility.
Technical Track
Containers Never Rest. Neither Should Your Strategy

Abhishek Singh
Qualys

Abhinav Mishra
Qualys

Antonio Anderson
Somos, Inc.
Containers have become the backbone of modern applications, but with them comes a new challenge: risk that never sleeps. SOCs are flooded with alerts, ROCs are overwhelmed by vulnerabilities, and security teams face a losing battle as baselines constantly regress due to new workloads and findings. Attackers are moving faster while security budgets aren't keeping pace.
In this session, we'll explore how to bring risk operations thinking to containers — shifting from endless detection and fire drills to dollar-optimized, risk-appropriate action. You'll see how Qualys TruRisk quantifies and prioritizes vulnerabilities using 25+ threat feeds, toxic combination analysis, and business criticality. We'll demonstrate how to prevent regressions with controls at build, deployment, and runtime, and how code-to-cloud remediation paths map risks back to the code and resources that introduced them—enabling teams to fix issues earlier and address them at the source.
Finally, we'll cover how container-native detection and response, full Kubernetes visibility, and Cybersecurity Asset Management-powered software catalog intelligence eliminate blind spots — even in serverless and standalone workloads.
Business Track
Transforming Compliance Fire-Drills into Confidence and Readiness

Alex Kreilein
Qualys

Charity Otwell
Center for Internet Security

Alex Reid
Coalfire

Mohammed Siraj
MUFG
Security burnout is no longer a side effect of the job – it’s a crisis. The relentless fire drills of compliance audits, urgent findings, and “check-the-box” mandates keep leaders stuck in tactical mode instead of building resilient programs. But we also know the way out: automation, continuous monitoring, and risk-based prioritization. It’s time to focus on the important enablers that bring predictability to our work, empowering us to take on priorities we never seem to prioritize.
In this candid session, Alex Kreilein, VP of Product Security & Public Sector Solutions at Qualys, will challenge the status quo of security program management. Learn how to transform compliance into confidence, audits into sustainable readiness, and security investments into measurable resilience. Walk away with a new perspective on how to protect your teams from burnout while positioning your organization to lead with trust, efficiency, and operational strength.
Technical Track
Closing Session

May Mitchell
Qualys
Business Track
Closing Session

Shawn O'Brien
Risk Busters - Live Capture the Flag

Courtney Burr
Qualys

Jatinder Pal Singh
informatica
7:15 AM – 8:45 AM
Breakfast
JW Marriott - Liberty Hall
7:30 AM – 3:00 PM
Registration
JW Marriott Hotel at the Galleria
SwagOps Store
Keynote: Risk Yoga: Stretching Strategy Into Measurable Action

Richard Seiersen
Qualys
Celebrating Innovation

Shawn O'Brien
Fireside Chat: AI Agents at Work: Balancing Innovation, Risk, and Compliance

Dilip Bachwani
Qualys

Jim Reavis
Cloud Security Alliance
Partner Panel: Managed Services Offerings for ROC

Chris Catanzaro
Qualys

Furey DiDomenico
GuidePoint Security

Neel Sata
ImagineX Digital

Lance Seelbach
DXC Technology, LLC
10:30 AM – 11:00 AM
AM Break
JW Marriott Hotel at the Galleria
Qualys Threat Research Unit (TRU): Heart of your ROC

Saeed Abbasi
Qualys
Eliminate the Risk of Audit Failure
Anu Kapil
Qualys

Joshua McDonald
Comerica
Perimeters are so 2015: Expanding Risk Operations with Identity Context

Himanshu Kathpal
Qualys

Corey Amsler
GE Vernova
12:30 PM – 1:30 PM
Lunch
JW Marriott - Liberty Hall
Technical Track
App-solutely Secure: Managing Application Security Posture in the Age of AI

Asma Zubair
Qualys

Joe Moore
Siemens
The application attack surface is rapidly expanding with the adoption of generative and agentic Al. Traditional security testing tools often miss AI-driven components, leaving blind spots that attackers can quickly exploit.
In this session, you'll learn how to assess and manage application risk holistically. We'll explore how Al and LLM usage impacts an application's risk profile, how to test modern apps holistically, prioritize risks effectively, streamline remediation across development and security teams, and continuously monitor for real-world exploitability, turning visibility into actionable security at scale.
Key Takeaways
• Discover your attack surface: Identify known, unknown, and forgotten applications and APls, their interconnections, and embedded AI/LLM usage.
• Strengthen application security posture: Manage risks across traditional and AI-powered components in one integrated program.
• Protect sensitive data: Detect data exposure risks and assess exploitability with comprehensive testing.
• Accelerate secure releases: Streamline workflows to balance security and speed to market.
• Build resilience and trust: Reduce breach risk, improve security maturity, and increase customer confidence.
Business Track
Ensure Audit Readiness for PCI 4.0 FIM Requirements

Lavish Jhamb
Qualys
PCI DSS 4.0 mandates File Integrity Monitoring (FIM) and File Access Monitoring (FAM) across all critical systems to detect unauthorized changes. This session demonstrates how Qualys FIM ensures complete coverage of PCI 4.0 requirements by closing compliance gaps. You’ll also discover what’s new in PCI 4.0 for FIM and which reports to present to auditors for a successful assessment.
Technical Track
The Benchmark Advantage: Measuring What Matters in Threat Intel

April Lenhard
Qualys
With threat intelligence, timing is everything; yet, most companies don't know how their risk identification times truly compare with those of their peers for proactive risk-related remediation. With Qualys' Enterprise TruRisk Management, organizations can finally benchmark median time to detect (MTTD) and median time to remediate (MTTR) across peer groups, segmented by industry. These insights extend beyond vanity metrics, providing critical context that reveals whether your team is lagging, leading, or in line with the competition. By transforming raw performance data into actionable intelligence, leaders can prioritize investments and drive measurable improvements. Today's session will reveal how benchmarking elevates threat intel from isolated metrics to a powerful tool for resilience and risk reduction.
Business Track
Getting the Most Value from Your Existing VMDR Subscription

Russ Sanderlin
Qualys

Jon Blevins
Syniverse
Vulnerability management is more than a compliance requirement. It is the foundation for a strategic and effective risk program. In this session, we will show you how to gain confidence in your current VMDR practices, maximize their impact, and build the foundation for the next level of risk maturity with Qualys Enterprise TruRisk Management. Learn how to strengthen your program today while preparing for proactive, continuous risk reduction in the future.
Technical Track
GenAI: Harness the Power, Eliminate the Risk

Kunal Modasiya
Qualys

Asma Zubair
Qualys
As organizations rapidly integrate generative into products and workflows, security and governance challenges are becoming critical. This session will guide you through how to identify, assess, and mitigate AI-specific risks so you can adopt these technologies with confidence. We will discuss: Key Takeaways· Discovery and inventory of your AI attack surface — including LLMs, AI workloads, MCP servers· Threats and vulnerability assessments unique to AI pipelines and agentic behaviors· AI risk assessment and monitoring to stay ahead of evolving threats· Cross-team collaboration — aligning data science, security, and application stakeholders for stronger defense Whether you’re launching your first AI initiative or scaling enterprise deployments, this session provides a clear blueprint for building trust, resilience, and security into your AI journey. Cloud Connectors bridge Qualys & multi-cloud environments, extending visibility to cloud assets while automatically tracking active VMs and removing inactive ones to maintain an accurate inventory
Business Track
One Agent to Rule Them All

Spencer Brown
Qualys

Ali Zaher
SLB
Closing Remarks

Shawn O'Brien
3:00 PM – 3:30 PM
Closing Remarks
Conference Highlights
Explore and secure the digital journey.
Dive into the profound impact of the digital journey and explore how to build in security automation from the data center to the cloud. Industry experts and Qualys leaders discuss automation strategies, preview product roadmaps, listen to your challenges, and answer your questions.
Get inspired
Engage with Qualys’ customer-facing teams and your peers around best practices and user case studies for applying security automation to real-world challenges.
Sharpen your expertise
One day of free training covers forward-looking strategies, best practices to improve effectiveness and productivity, and core and expanded product features to up-level your security program.
Who Should Attend
CIOs, CSOs and CTOs; directors and managers of network, security and cloud; developers and DevSecOps practitioners; Qualys partners and consultants; or any forward-thinking security professionals.
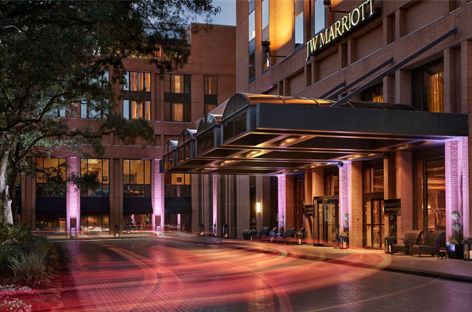
Register NowJW Marriott Houston by the Galleria
Houston, Texas, USA
The Risk Operations Conference will be held at the JW Marriott Houston by the Galleria.
5150 Westheimer Road,
Houston, TX 77056
JW Marriott - Houston, Texas | USA
Conference Pricing
Attendance at ROCon is complimentary. This includes access to all general sessions, breakfast*, lunch and breaks. Travel and hotel accommodations are not included with ROCon or pre-conference training.
*continental breakfast on Monday & Tuesday; buffet breakfast on Wednesday & Thursday
Book Your Hotel Now
FAQs
Qualys is committed to providing a safe and healthy experience for all ROCon participants
As part of our efforts to make ROCon Americas a successful and productive event, Qualys is committed to providing a safe, professional and welcoming environment for all participants. To that end, we require everyone to follow our Code of Conduct.
Code of ConductIf you have any questions, please read our FAQs.
If you still have questions, please call us at +1 (650) 801 6100 or email us at [email protected]
Frequently Asked Questions